Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
Kittysploit-framework — Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,.... | Kitploit
Tools/GitHubGitHub/sia-iotechnology/kittysploit-framework
OSINT (Open Source Intelligence)Penetration Testing FrameworksReconnaissanceExploit FrameworksWeb Proxies & InterceptionDebuggersPost-ExploitationCommand and ControlRed TeamingPayload DevelopmentAI Security
5939873vor 4 TagenVon Kitploit geprüft
Teilen
GitHub
sia-iotechnology/kittysploit-framework

Kittysploit-framework

Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
Repository anzeigenWebseite
Inhalt in der angeforderten Sprache nicht verfügbar. Englische Version wird angezeigt.
KittySploit logo

KittySploit

Exploitation and post-exploitation framework — one console.

Recon, scanning, exploits, interactive sessions, and post-exploitation across 60+ session connectors (shell, browser, databases, cloud, IoT/ICS, and more).
Python License Discord GitHub stars

Installation · Quick start · Full guide · Website

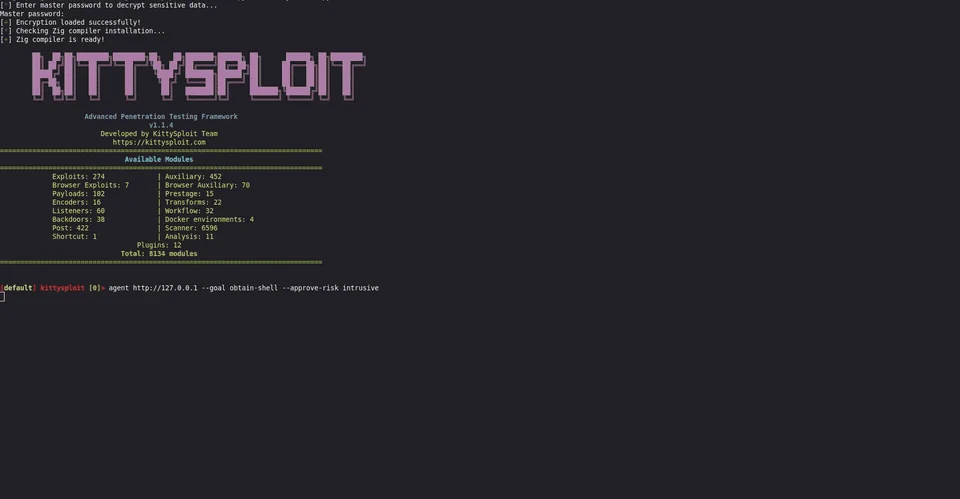
KittySploit — console, exploitation, and sessions

At a glance

StepWhat KittySploit does
1. FindWeb, network, cloud, and service scanners and recon
2. ExploitExploit modules, chains, and optional local-LLM agent
3. Post-exploit60+ session connectors — loot, pivot, persistence, enumeration

Everything stays in one console: modules, listeners, payloads, built-in C2, and reporting.

Use only on targets you own or are explicitly authorized to test.

Why KittySploit?

Typical stacks split the scanner, exploit framework, C2, and notes across different tools.

KittySploit brings them together: exploit to get a session, then run post-exploitation without switching apps.

Post-exploitation connector examples: Linux/Windows shell, browser (JS session), SSH, MySQL/PostgreSQL/Redis/MongoDB, SMB, FTP, Kubernetes, AWS/GCP/Azure, PHP webshell, WinRM, LDAP, BLE, MQTT, Modbus, BACnet, ONVIF, and more.

Module scale (approximate): thousands of scanners/auxiliary modules, 700+ exploits, 400+ post modules.

Installation

Linux and macOS

git clone https://github.com/SIA-IOTechnology/Kittysploit-framework.git
cd Kittysploit-framework
./install/install.sh
python3 kittyconsole.py

One-line install:

curl -fsSL https://raw.githubusercontent.com/SIA-IOTechnology/Kittysploit-framework/main/install/install-standalone.sh | bash

Windows

git clone https://github.com/SIA-IOTechnology/Kittysploit-framework.git
cd Kittysploit-framework
install\install.bat
python kittyconsole.py

Quick start

kittysploit> doctor
kittysploit> search cve:2024 type:exploit
kittysploit> use exploits/multi/http/...
kittysploit> run

kittysploit> sessions -l
kittysploit> sessions -i 1
kittysploit> search type:post platform:windows

Automated web mission (authorized lab):

kittysploit> agent https://lab.local

Shell goal on an internal lab:

kittysploit> agent http://192.168.56.10 \
  --profile internal-lab \
  --goal obtain-shell \
  --approve-risk intrusive \
  --shell-hunter

Use --plan-only or --dry-run to preview without intrusive actions.

Core features

  • Exploitation — search / use / run, payloads, listeners, exploit queues
  • Sessions and C2 — shells, callbacks, pivots, multi-session management
  • Post-exploitation — modules per session type (gather, manage, pivot, loot)
  • Agent (optional) — local LLM (Ollama), mission profiles, scope controls
  • Automation — CLI, API/RPC, and MCP for IDE or scripted workflows

Agent profiles, compound evidence, environment variables, and cookbooks are in USAGE.md.

Ecosystem

ProjectPurpose
KittyProxyHTTP capture and analysis
KittyCosmicGraphical interface
KittyOsintVisual OSINT
KittyProtocolProtocol analysis
KittyV8DebuggerV8 debugging

Demo video · Site and marketplace · Wiki

Community

  • Discord
  • Issues
  • Liberapay

The project is still evolving — validate in a lab before production engagements.

Acknowledgments

Thanks to Woody for their contributions.

License

Released under the MIT License.

Tool herunterladen

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Das ultimative OSINT-Toolkit: Untersuchungsgraph, Konfidenzbewertung, Alias-Familien, Karte, Zeitleiste und Berichte. 49 Module, 400+ Websites, keine API-Schlüssel erforderlich.

    717
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    504
  • 3

    ARTEX

    baarai/artex

    LLM-basierte Multi-Agenten-Plattform für autonome Penetrationstests mit Planer-/Worker-Agenten, Asset- und Explorationsgraphen, MITM-Verkehrsaufzeichnung und Schwachstellen-Retesting.

    402
  • 4

    redforge

    cybersecurity91/redforge

    Browser-seitiges Red-Team-Toolkit mit 102 Offline-Tools für Recon, Payload-Generierung, Credential-Angriffe, Krypto, Encoding und Engagement-Reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Das System der Handlung für KI-native Cybersicherheit – wo Absicht zu gesteuerter Ausführung wird, Beweise zu operativem Gedächtnis werden und jeder Einsatz den nächsten verbessert.

    260
  • 6

    antifox

    antifox-ai/antifox

    KI-Multi-Agenten-Plattform für autonome Penetrationstests, die Recon, Angriffsflächen-Erkennung, Exploit-Validierung und evidenzbasierte Berichtserstellung durchführt.

    259

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →