
 revoltsecurities/shodanx
ShodanX ist ein Tool, um Informationen über Ziele mithilfe von Shodan-Dorks zu sammeln⚡.


Funktionen | Installation | Verwendung | Post-Installation


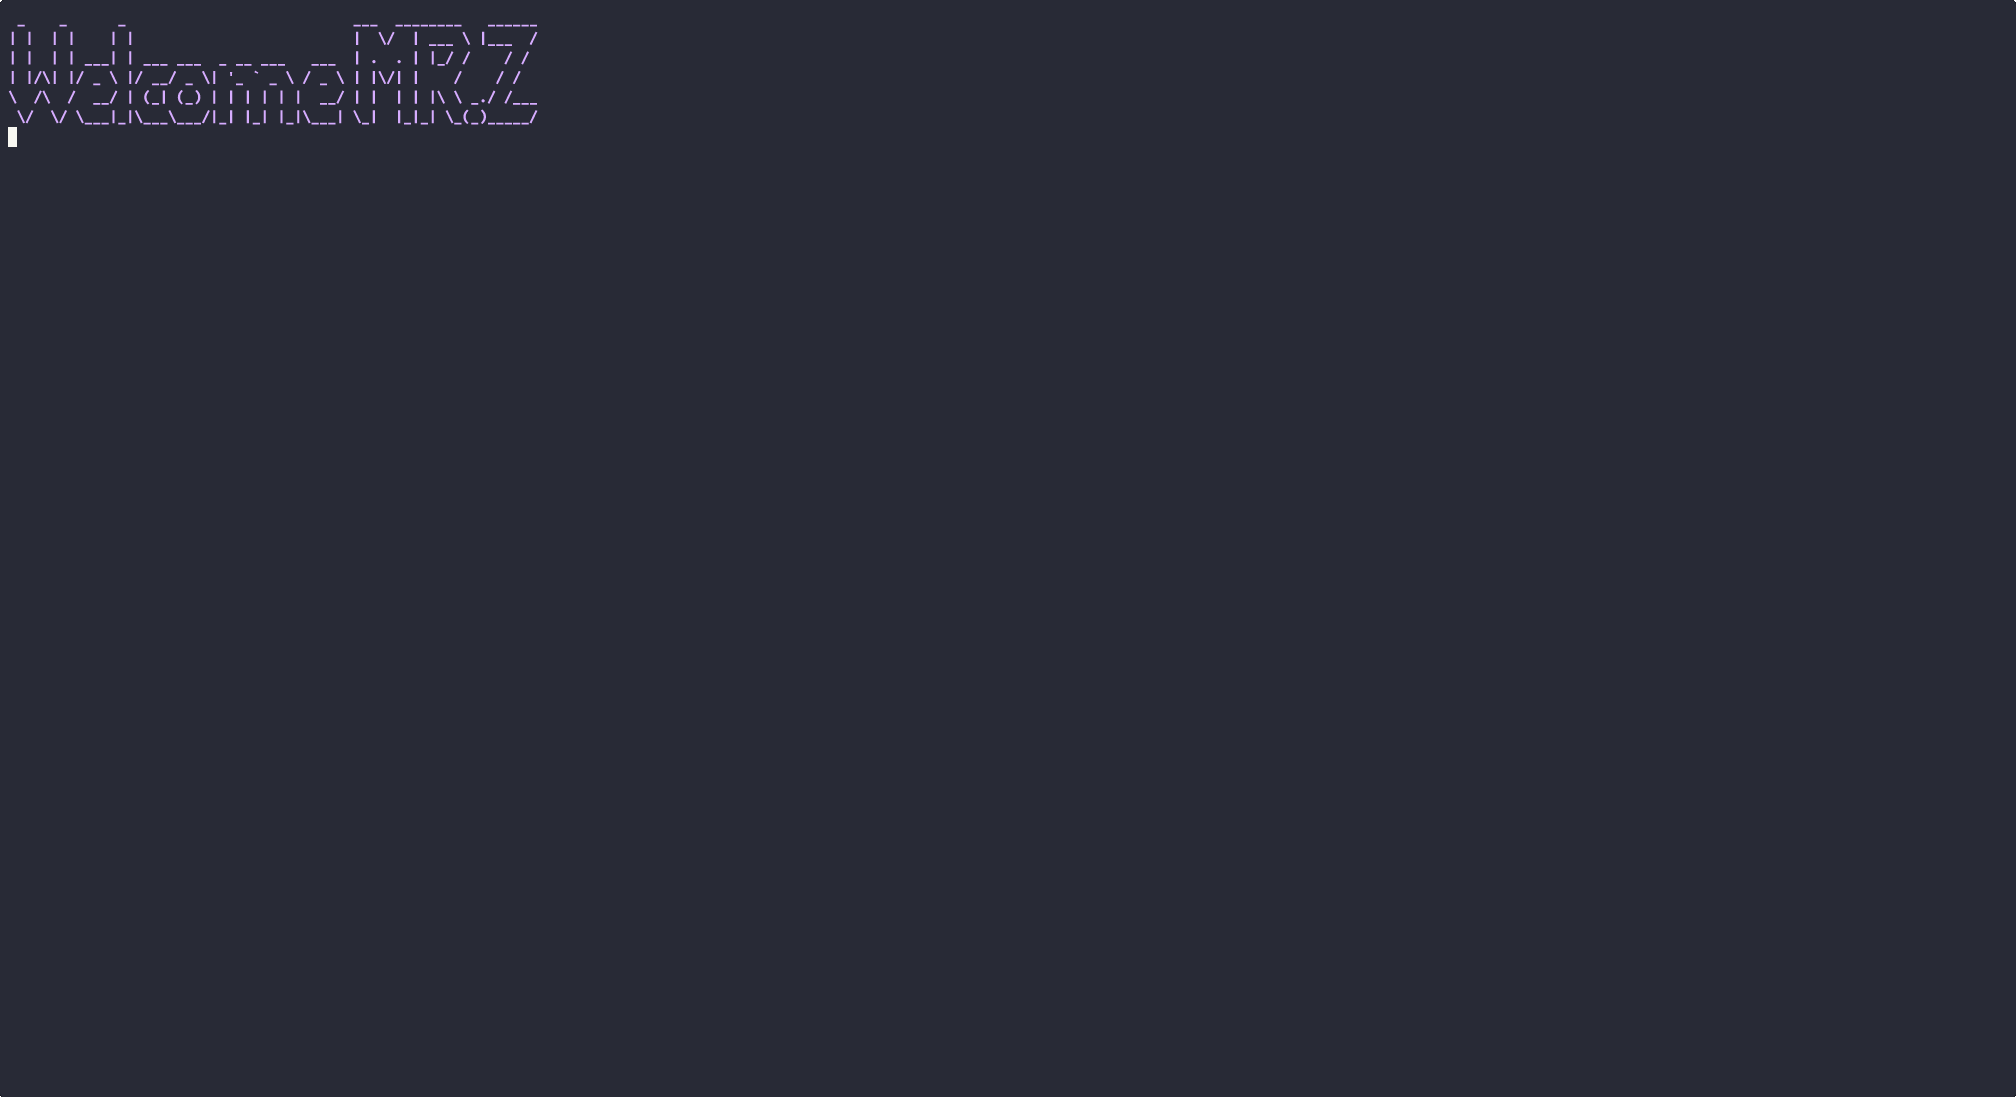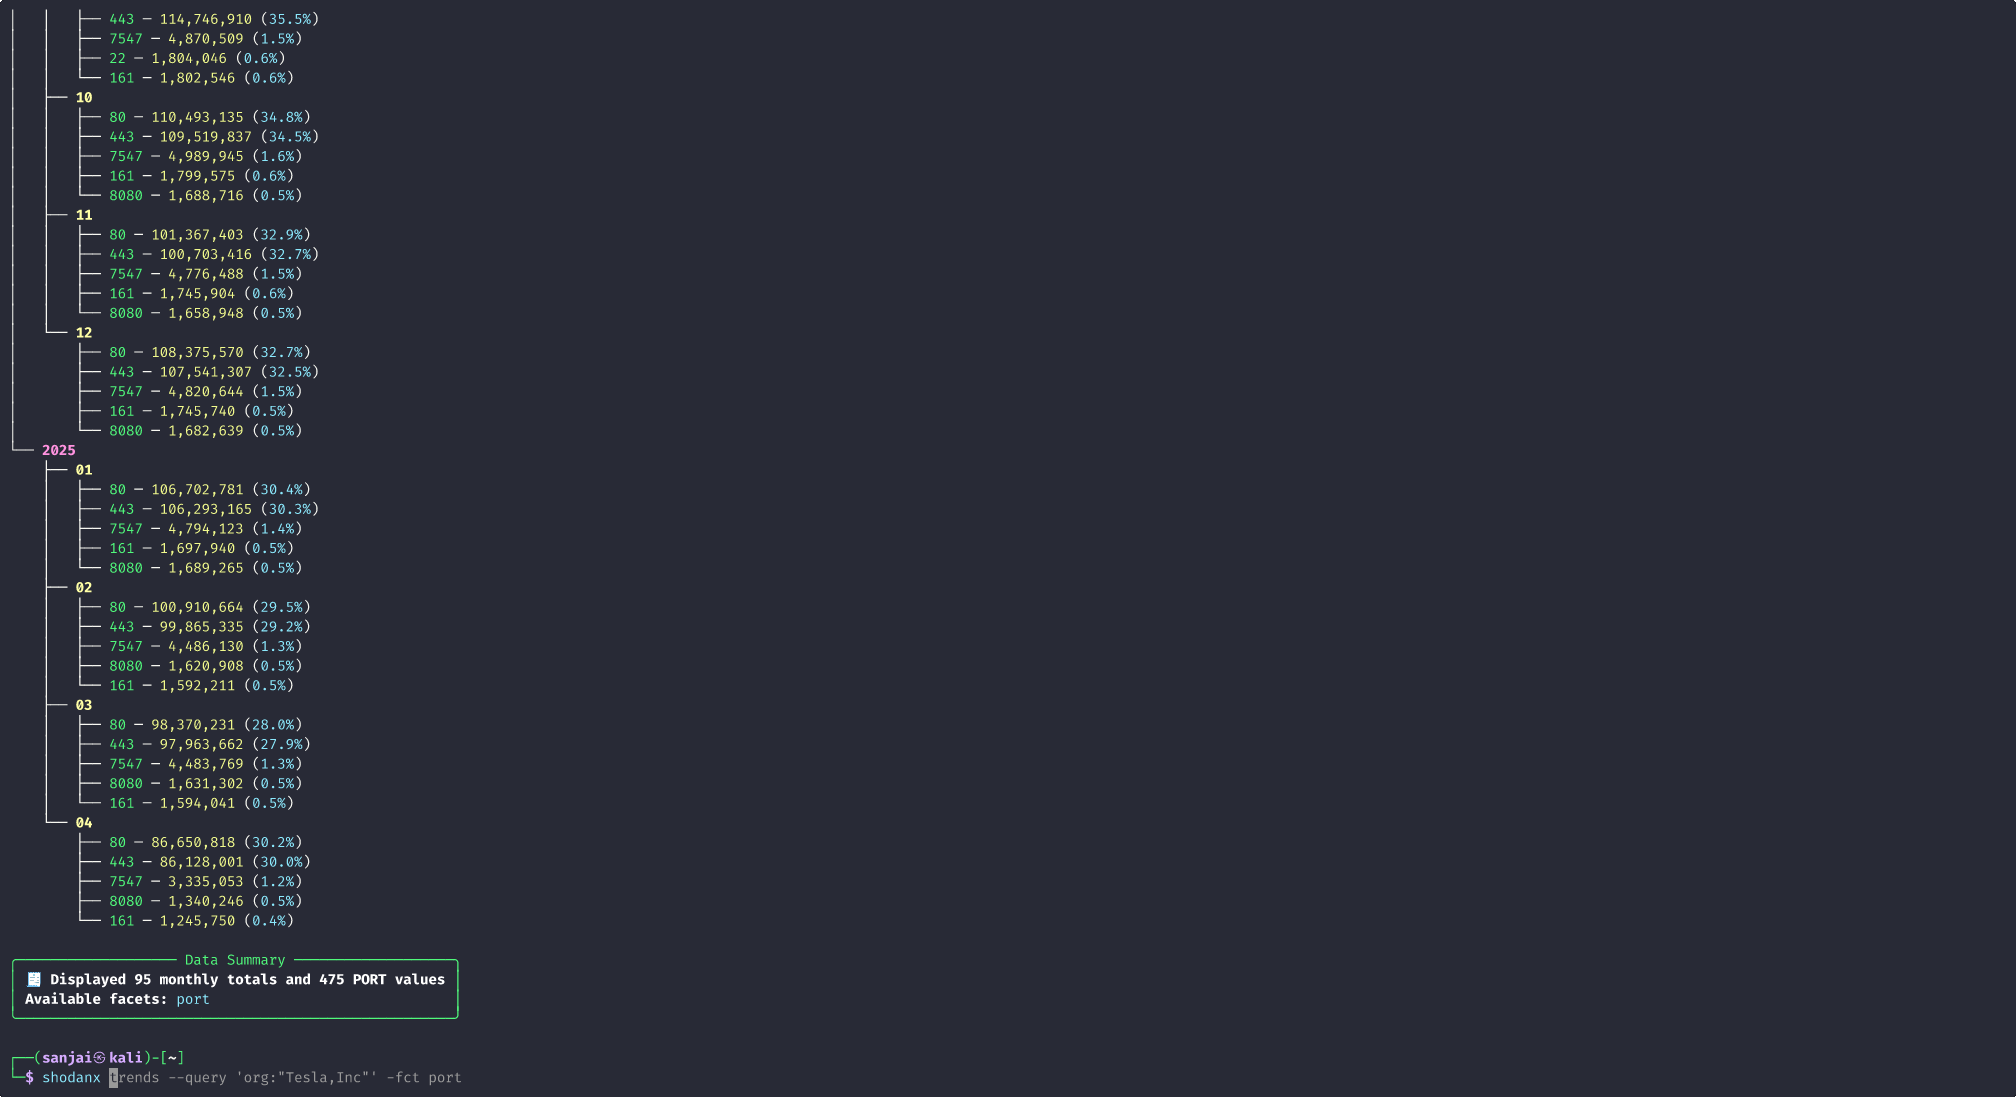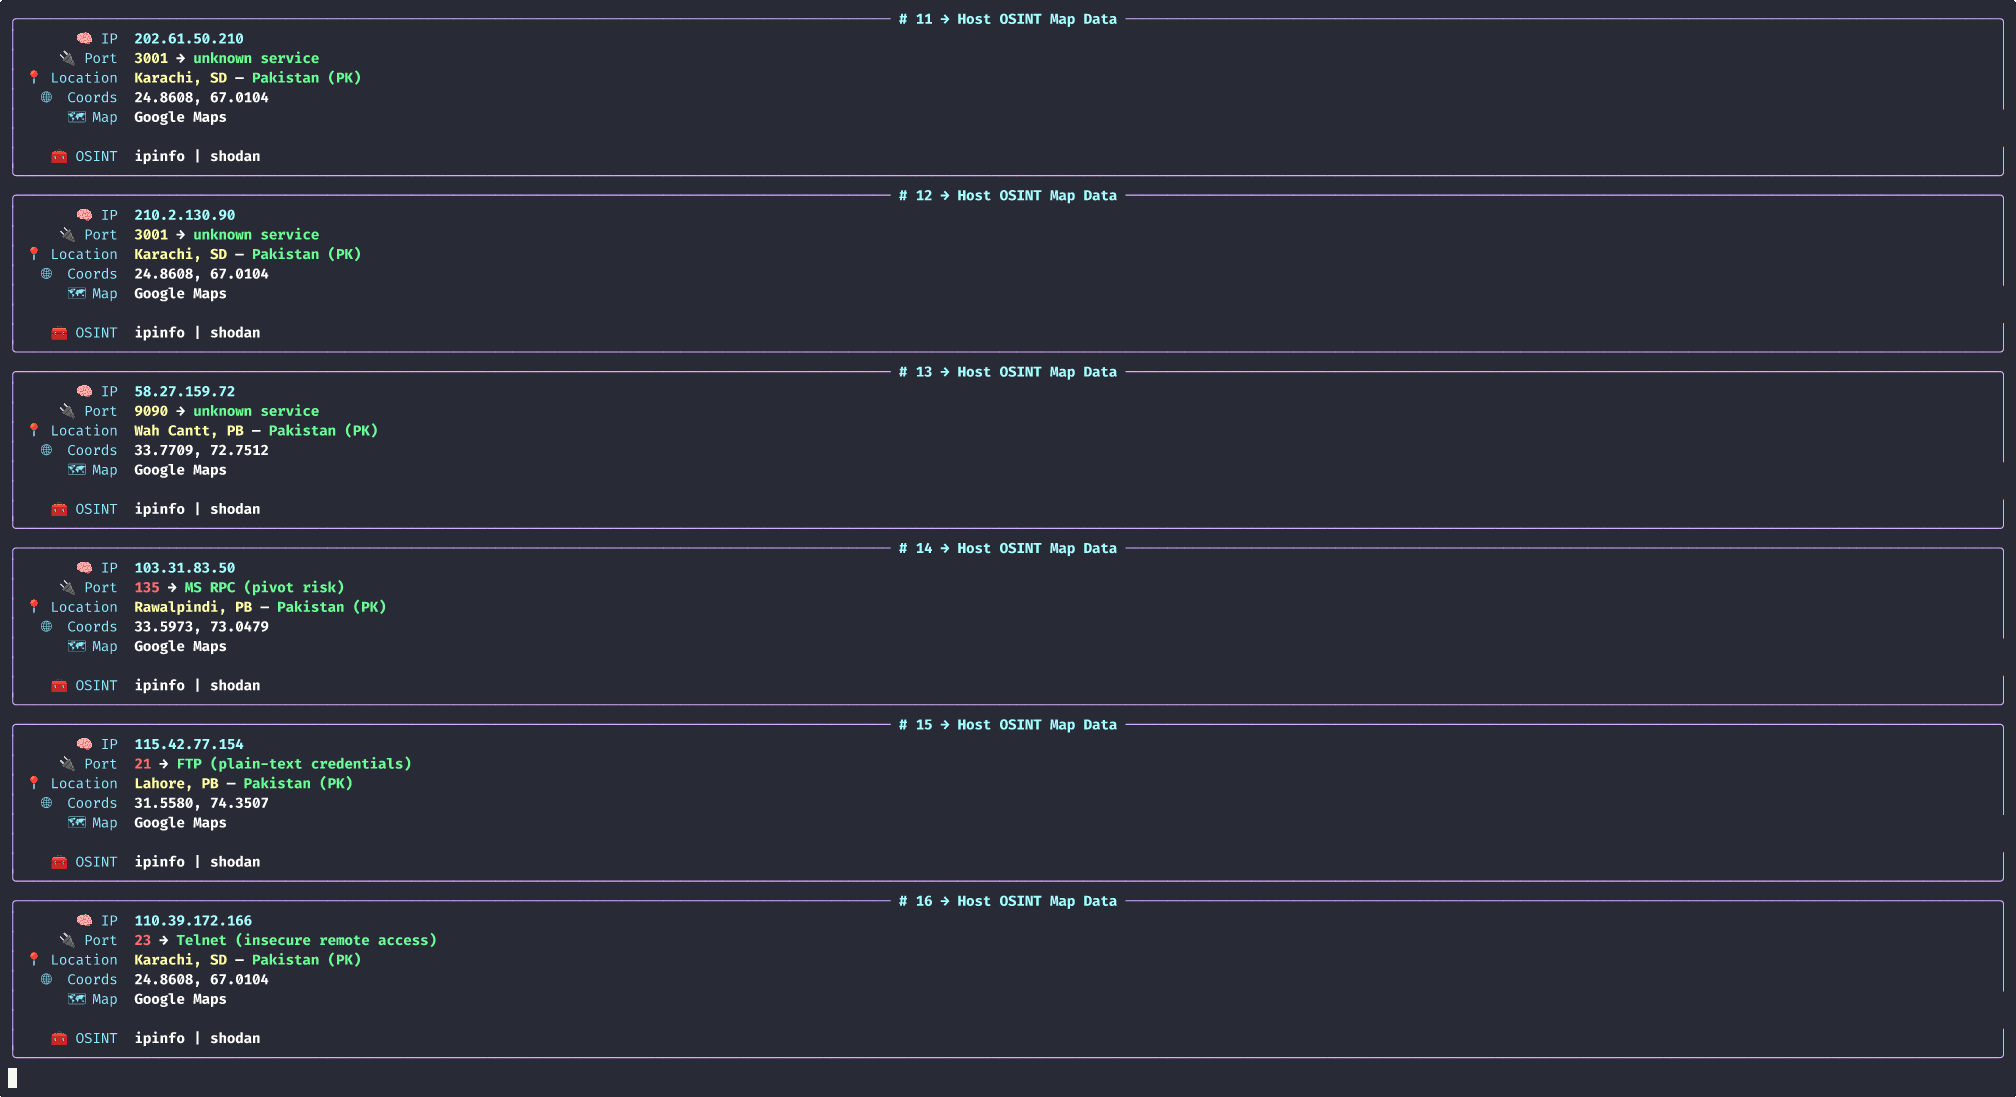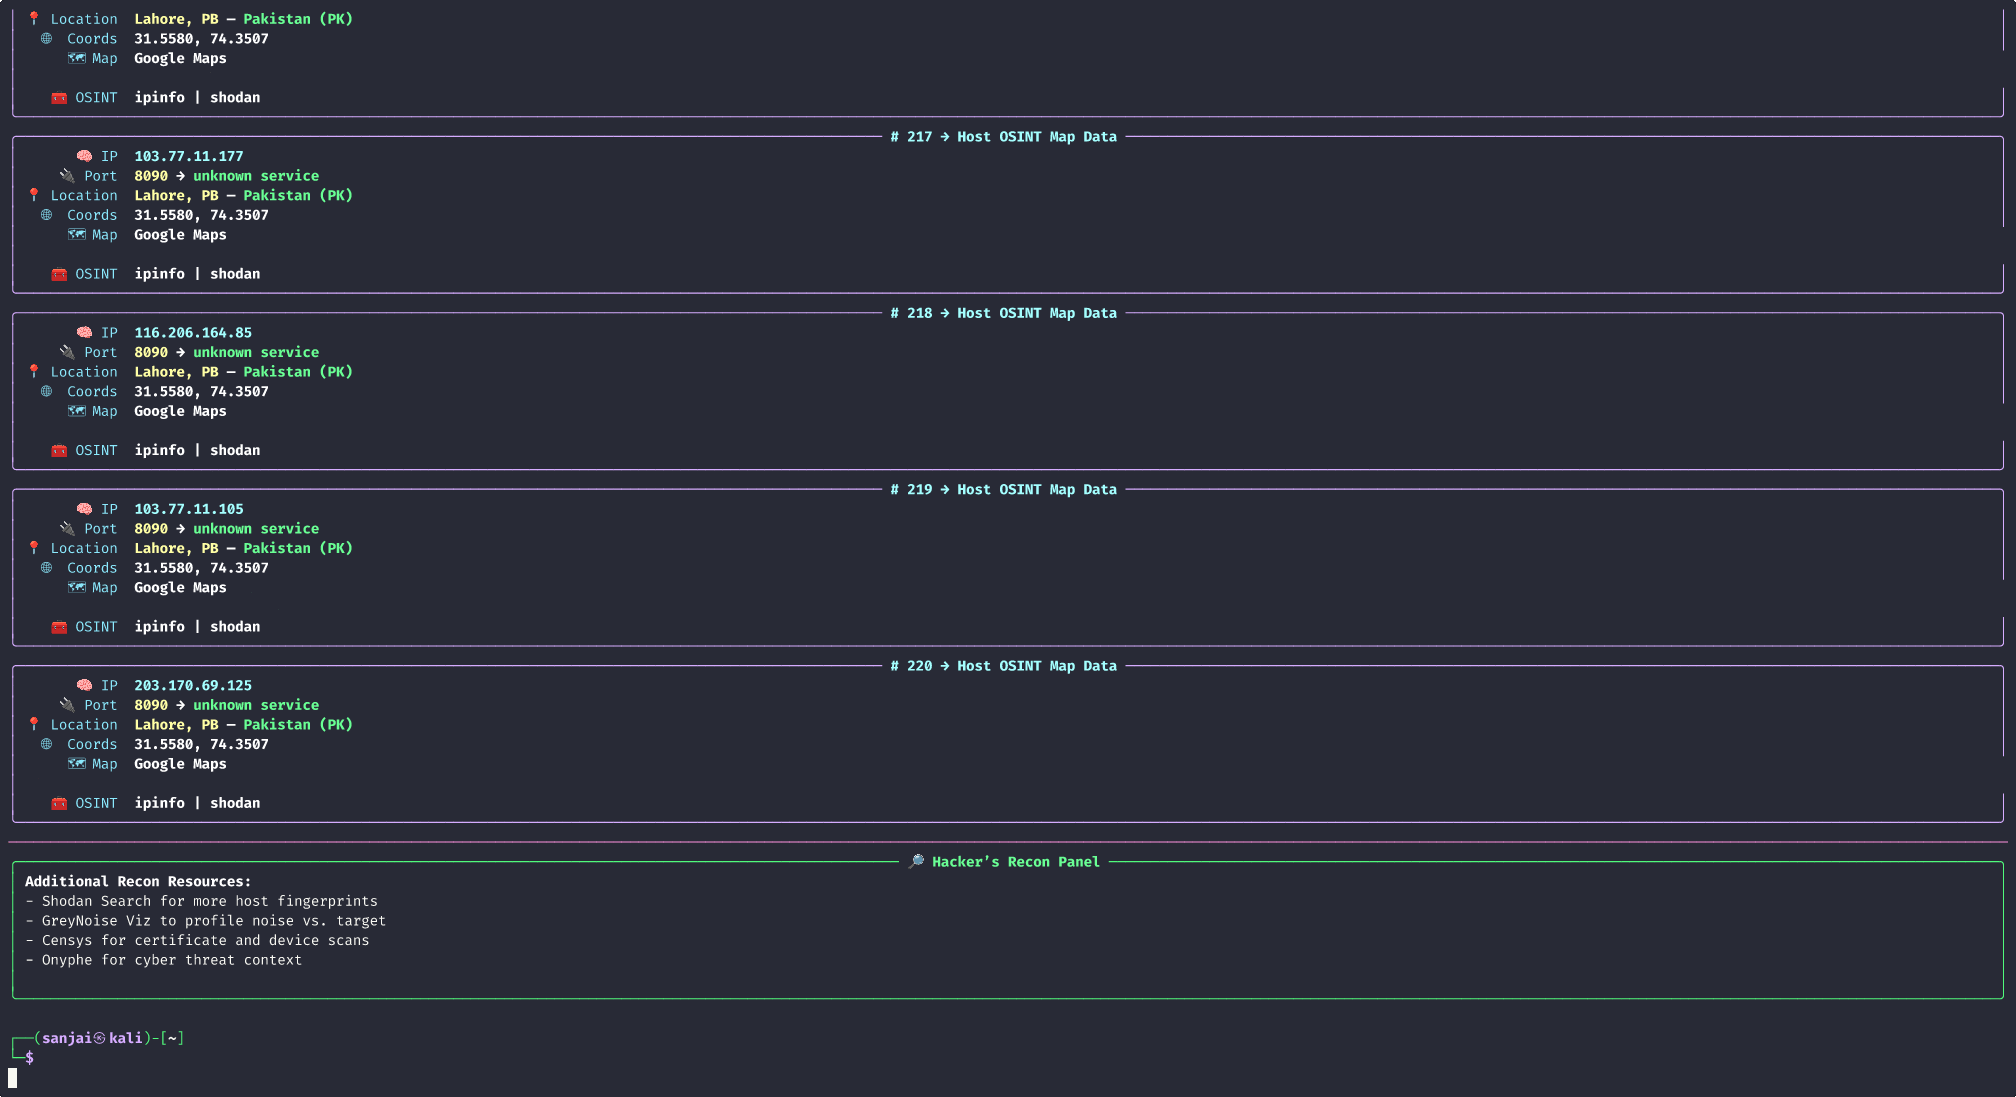
🔐 shodanx auth – Konfigurieren und sichere Speicherung Ihres Shodan-API-Keys.🔓 shodanx login – Überprüfen Sie Ihren Zugriffslevel und den Status Ihres API-Keys.🏢 shodanx org – Organisationsweite Scans mit Shodans leistungsstarken Facetten durchführen.🌐 shodanx domain – Domainbezogene Metadaten, offene Ports und Host-Expositionen erfassen.📡 shodanx subdomain – Passive Subdomains über Shodans DNS-Intel entdecken.🔒 shodanx ssl – Wiederverwendete oder abgelaufene SSL-Zertifikate per Fingerprint-Suche verfolgen.🎯 shodanx custom – Erweiterte Shodan-Dorks und benutzerdefinierte Filterabfragen ausführen.📦 shodanx internetdb – Shodans leichtgewichtige InternetDB für schnelle IP-/Domain-Analysen nutzen.🗺️ shodanx map – Geografische Verteilung exponierter Dienste und Ports visualisieren.🧬 shodanx cvedb – Hosts bekannten Schwachstellen über die CVE-Datenbank zuordnen.🏭 shodanx entitydb – Technologien, Software und Anbieter auf exponierten Systemen erkunden.🌍 shodanx exposuredb – Öffentlich exponierte Assets und Datenlecks nach Ländern identifizieren.🖼️ shodanx faviconmap – Systeme anhand einzigartiger Favicons für laterale Entdeckungen verfolgen.📈 shodanx trends – Expositionstrends im Zeitverlauf analysieren (Enterprise-Zugriff erforderlich).shodanx kann einfach mit pip installiert werden
pip install git+https://github.com/RevoltSecurities/ShodanX --break-system-packages
✅ Stellen Sie sicher, dass Python 3.13 oder neuer installiert ist.
shodanx -h
   _____    __                __                   _  __
  / ___/   / /_   ____   ____/ /  ____ _   ____   | |/ /
  \__ \   / __ \ / __ \ / __  /  / __ `/  / __ \  |   /
 ___/ /  / / / // /_/ // /_/ /  / /_/ /  / / / / /   |
/____/  /_/ /_/ \____/ \__,_/   \__,_/  /_/ /_/ /_/|_|


                     - RevoltSecurities

╭───────────────────────╮
│                       │
│    SHODANX ⚡ HELP    │
│                       │
╰───────────────────────╯
DESCRIPTION

ShodanX is a terminal-powered recon and OSINT tool built on top of the Shodan Services.
It empowers ethical hackers and red teamers to identify exposed infrastructure,
search CVEs, map attack surfaces, and run internet-wide queries in real time.

MODES (shodanx <mode>)

┏━━━━━━━━━━━━┳━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━┓
┃ Mode       ┃ Description                                                      ┃
┡━━━━━━━━━━━━╇━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━┩
│ auth       │ Configure and save your Shodan API key for authenticated access. │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ login      │ Verify your ShodanX access level and API key validity.           │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ org        │ Perform organization-wide scans using Shodan facets.             │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ domain     │ Enumerate metadata, ports, and host exposure for a domain.       │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ subdomain  │ Discover passive subdomains using Shodan’s DNS data.             │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ ssl        │ Search by SSL fingerprint to track reused/expired certs.         │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ custom     │ Execute advanced queries using Shodan filters and dorks.         │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ internetdb │ Lightweight analysis of IPs/domains via Shodan InternetDB API.   │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ map        │ Visualize geo-distribution of exposed services and ports.        │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ cvedb      │ Identify vulnerable systems via Shodan’s CVE database.           │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ entitydb   │ Explore technologies/vendors via Shodan’s EntityDB.              │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ exposuredb │ Discover globally exposed assets and leaks by country.           │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ faviconmap │ Find systems using specific favicons via Shodan FaviconMap.      │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ trends     │ View historical exposure trends (Shodan Enterprise required).    │
└────────────┴──────────────────────────────────────────────────────────────────┘
FLAGS
┏━━━━━━━━━━━━┳━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━┓
┃ Flag       ┃ Description                      ┃
┡━━━━━━━━━━━━╇━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━┩
│ -h, --help │ Show this help message and exit. │
└────────────┴──────────────────────────────────┘
USAGE
shodanx <mode>

DETAILS
 shodanx auth        → Configure and save your Shodan API key for authenticated access.
 shodanx login       → Verify your ShodanX access level and API key validity.
 shodanx org         → Perform organization-wide scans using Shodan facets.
 shodanx domain      → Enumerate metadata, ports, and host exposure for a domain.
 shodanx subdomain   → Discover passive subdomains using Shodan’s DNS data.
 shodanx ssl         → Search by SSL fingerprint to track reused/expired certs.
 shodanx custom      → Execute advanced queries using Shodan filters and dorks.
 shodanx internetdb  → Lightweight analysis of IPs/domains via Shodan InternetDB API.
 shodanx map         → Visualize geo-distribution of exposed services and ports.
 shodanx cvedb       → Identify vulnerable systems via Shodan’s CVE database.
 shodanx entitydb    → Explore technologies/vendors via Shodan’s EntityDB.
 shodanx exposuredb  → Discover globally exposed assets and leaks by country.
 shodanx faviconmap  → Find systems using specific favicons via Shodan FaviconMap.
 shodanx trends      → View historical exposure trends (Shodan Enterprise required).
Nach erfolgreicher Installation von shodanx führen Sie diese schnellen Schritte aus, um vollständig authentifiziert und scanbereit zu sein:







