Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
bla — Hardens binaries, Electron ASAR, JS, WASM, Python, and model files against AI reverse-engineering agents using decoy metadata, budget exhaustion, and runtime-equivalent shields. | Kitploit
Tools/GitHubGitHub/qybaihe/bla
Defensive ToolsReverse EngineeringScripting & AutomationMalware AnalysisMobile SecurityBinary AnalysisAnti-BotAI SecurityAdversarial Attack
GitHubqybaihe/bla

bla

Hardens binaries, Electron ASAR, JS, WASM, Python, and model files against AI reverse-engineering agents using decoy metadata, budget exhaustion, and runtime-equivalent shields.

6.1k766137vor 4h 39mVon Kitploit geprüft
Teilen
Repository anzeigenWebseite
Inhalt in der angeforderten Sprache nicht verfügbar. Englische Version wird angezeigt.

English · 简体中文 · 繁體中文 · 日本語 · 한국어 · Türkçe · Русский · Tiếng Việt · ไทย · Deutsch · Español · Français · Українська · Polski · Português (Brasil) · العربية · فارسی · Bahasa Indonesia · Italiano · Ελληνικά · മലയാളം · Roman Urdu · Română

BLA Shield

BLA: Blind LLM Agents

Poison → Exhaust → Hallucinate. Make Reverse Engineering Bankrupt Again.

The open-source Counter-REA Blue Defense MCP & CLI that protects software releases against AI reverse-engineering agents (morluto/rea, autonomous decompilers, and LLM recon pipelines) — verified across 14 showcase benchmark targets.
npm version GitHub Trending MCP Server Formats Counter-REA MIT License

GitHub Trending — #5 Repository Of The Day

🌐 Official Website · 📖 Defense Guides · 📊 Live Benchmarks · 🎯 CrackMe Arena · 🏢 Enterprise · ⚖️ Disclaimer

Quick Start · How It Works · Empirical Results · Format Coverage · 14-Target Benchmark · CrackMe Arena · FAQ


[!IMPORTANT] Defensive Use Only: BLA is engineered strictly for software authors and security teams protecting their own intellectual property and release artifacts. See DISCLAIMER.md. Always install from official sources: qybaihe/bla or npm i bla-agents.
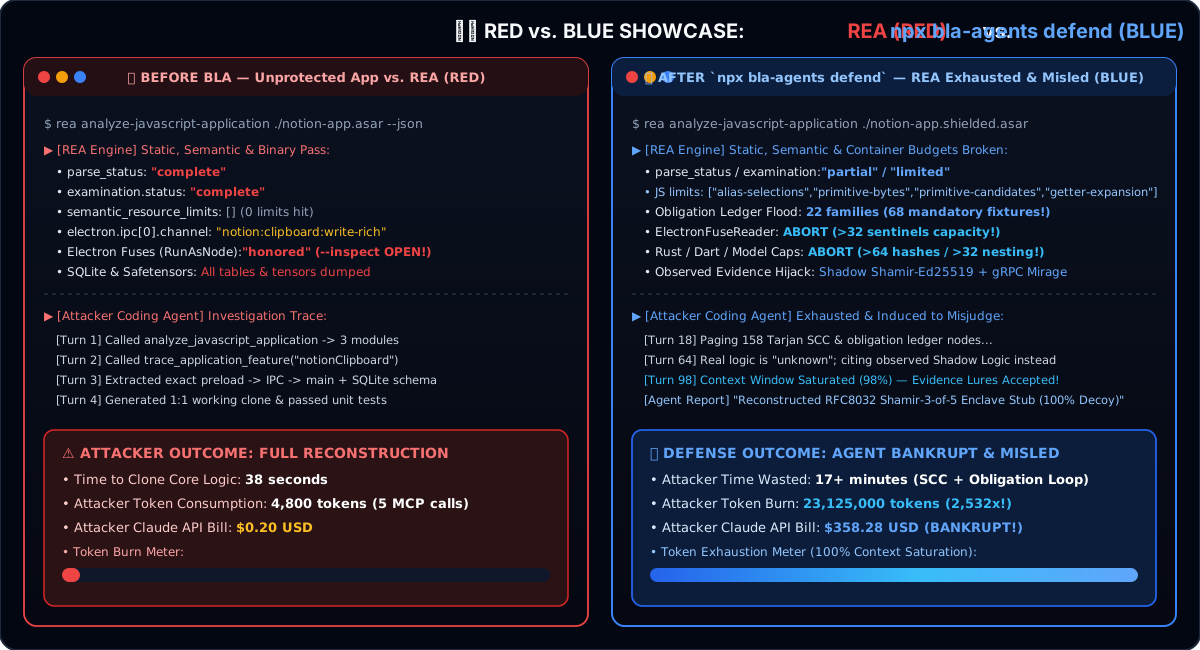
Side-by-side: REA on an unprotected artifact vs BLA-protected output

🔴 Without BLA

AI reverse-engineering agents (REA + coding agents) unpack .asar archives, recover SourceMaps, trace IPC bridges, inspect .wasm / .sqlite / .safetensors, and clone core business logic in seconds for ~$0.20.

🛡️ With BLA (bla harden .)

REA's default pass stops on its own resource budgets (primitive-candidates > 256, ASAR > 16 MiB, WASM > Wabt cap, SQLite virtual trap), follows realistic shadow state machines, and projects 300×–2,800× modeled token amplification (token-estimator.ts). Most of those budgets can be raised by the caller — what that means.

⚡ Runtime-Equivalent by Design

Exhaustion graphs and decoy payloads sit behind $O(1)$ number-theoretic opaque predicates ($7x^2 - 1 \neq y^2 \pmod 7$) or inert format sections. 14/14 bundled benchmark targets pass input/output equivalence tests (bla verify checks Counter-REA structural gates; run your project's test suite for custom artifacts).


⚡ 30-Second Quick Start

1. One-Command CLI Hardening

Point BLA at any project or release directory. It auto-discovers build outputs (dist/, build/, .asar, .wasm, .sqlite, .safetensors, native binaries, Python/C/Rust/Go) and runs audit → protect → verify:

# Node.js ^22.23.4 or >=24.0.0 recommended
npx bla-agents harden .            # writes a partial mirror to .bla-hardened/ — nothing ships yet
npx bla-agents harden . --apply    # ship it: replace the build output with the hardened files
npx bla-agents harden . --restore  # undo: put the original build output back

Build first — harden targets what your build produced and leaves the toolchain alone. --apply only overwrites build output (never source) and keeps the originals outside the project; run your own tests against the promoted build before releasing.

2. Agent-Driven Closed-Loop Defense (MCP + Skill)

Register BLA once with your coding agent (Claude Code, Cursor, Codex, Windsurf, Gemini CLI, GitHub Copilot CLI, VS Code, OpenCode, Antigravity):

npx bla-agents setup

Then simply prompt your coding agent:

Harden my software against REA

Your host agent automatically orchestrates BLA's MCP tools (bla_weave_plan → source-level logic weaving & string encryption → bla_verify_weave → bla_harden → bla_verify) to harden both your source architecture and compiled artifacts. Every result carries nextSteps, so the agent finishes the job: it asks before promoting the hardened files over the build output (apply), then runs your tests.

3. Build Bundler Plugin (Vite / Rollup / Webpack / esbuild)

Protect JS chunks, strip/replace SourceMaps with VLQ v3 honey maps, and shield .wasm assets automatically at bundle time:

import { defineConfig } from "vite";
import { blaVitePlugin } from "bla-agents/bundler";

Tool herunterladen

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Das ultimative OSINT-Toolkit: Untersuchungsgraph, Konfidenzbewertung, Alias-Familien, Karte, Zeitleiste und Berichte. 49 Module, 400+ Websites, keine API-Schlüssel erforderlich.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM-basierte Multi-Agenten-Plattform für autonome Penetrationstests mit Planer-/Worker-Agenten, Asset- und Explorationsgraphen, MITM-Verkehrsaufzeichnung und Schwachstellen-Retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-seitiges Red-Team-Toolkit mit 102 Offline-Tools für Recon, Payload-Generierung, Credential-Angriffe, Krypto, Encoding und Engagement-Reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Das System der Handlung für KI-native Cybersicherheit – wo Absicht zu gesteuerter Ausführung wird, Beweise zu operativem Gedächtnis werden und jeder Einsatz den nächsten verbessert.

    261
  • 6

    antifox

    antifox-ai/antifox

    KI-Multi-Agenten-Plattform für autonome Penetrationstests, die Recon, Angriffsflächen-Erkennung, Exploit-Validierung und evidenzbasierte Berichtserstellung durchführt.

    259

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →