Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
Tools/GitHubGitHub/msaad00/agent-bom
Vulnerability ScannersContainer SecurityCloud SecurityDevSecOpsSecret DetectionThreat IntelligenceSupply Chain SecurityMisconfigurationAI Security
GitHubmsaad00/agent-bom

agent-bom

AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code, containers, cloud and AI. Self-host free; local scans need no account.

29788vor 14h 40mVon Kitploit geprüft
Repository anzeigenWebseite
Teilen
Inhalt in der angeforderten Sprache nicht verfügbar. Englische Version wird angezeigt.

agent-bom — AI supply-chain BOM: supported agents, MCP servers and AI packages, and what each one can reach.

Build PyPI Python 3.11 through 3.14

Apache-2.0 license OpenSSF Scorecard

AI supply-chain BOM: supported agents, MCP servers and AI packages, and what each one can reach.

For AppSec teams and developers who run Claude Code, Cursor, Codex or any MCP client: see which agents, MCP servers, tools and packages are installed, which are vulnerable, and what each one can reach. Local scans need no account.

Quick start · Try in browser · Laptop → team → org · Product tour · Docs

Quick start

From the repository you want to inspect, with uv installed:

uvx agent-bom scan . -f html -o agent-bom-report.html

Open agent-bom-report.html for inventory, findings and fix guidance. Run it again later to see what changed. No MCP configuration in the project? Package findings still apply.

No project handy? uvx agent-bom scan --demo --offline scans a bundled sample. Exit 1 is expected there: the sample trips the security gate. Elsewhere, a non-zero exit can mean a security gate or incomplete assessment; inspect the report and coverage (exit codes, first-run guide).
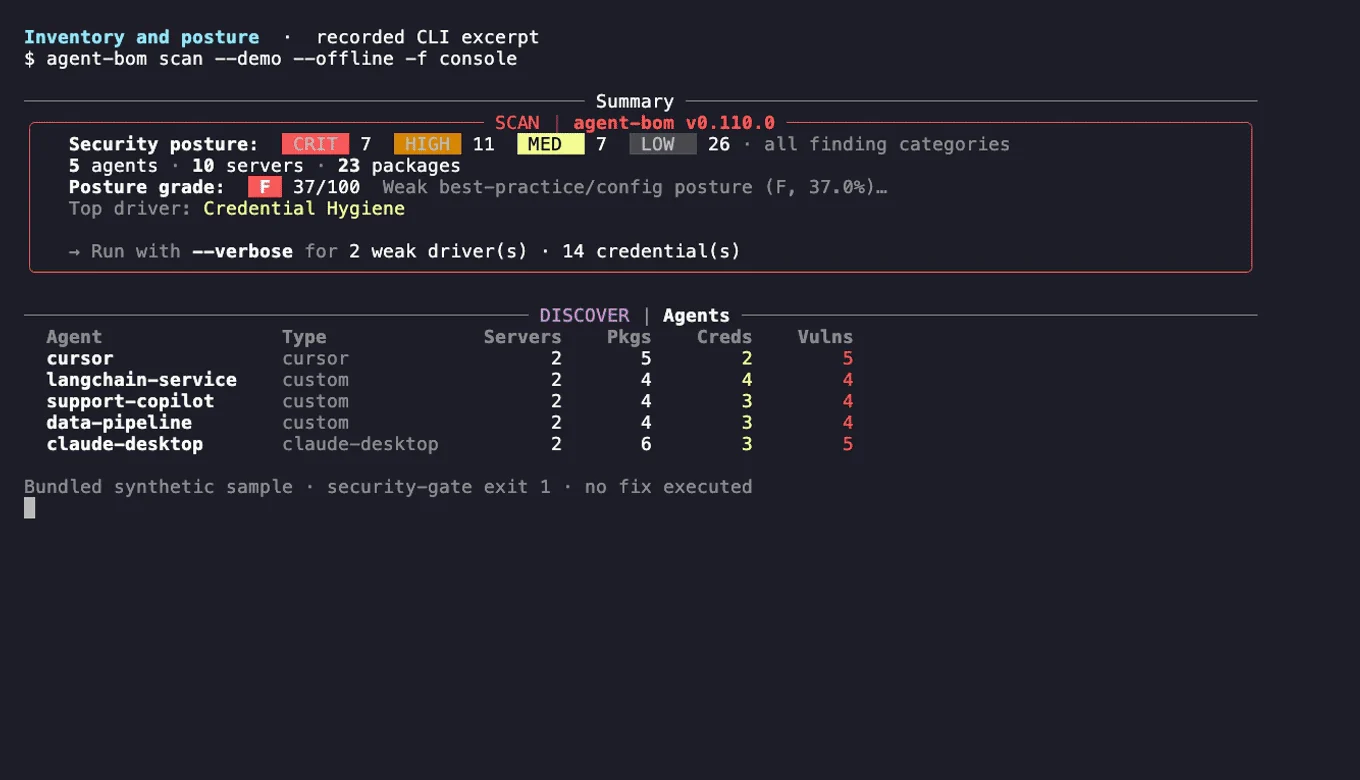
Recorded agent-bom CLI showing sample findings and remediation guidance; no fix executed

What the scan reads and what it does not establish

The scan stays inside this repository: packages, MCP configuration, secrets and personal data, skills and IaC. It does not read agent configuration elsewhere on the machine. Missing evidence is reported as partial, not clean. See what a scan does and does not establish.

From laptop to team to org

  • On your laptop: uvx agent-bom scan . for findings with fixes and a delta on every rescan; claude mcp add agent-bom -- uvx agent-bom mcp server to use agent-bom as a tool inside your coding agent (MCP server, plugins).
  • In your team: uses: koda-ai-studio/agent-bom@v0 on pull requests and a weekly schedule: for a PR gate with a findings comment, SARIF in code scanning and a weekly rescan that catches new CVEs in unchanged code (GitHub Action).
  • Across your org: agent-bom up locally, then Docker Compose or the Helm chart from oci://ghcr.io/koda-ai-studio/charts/agent-bom for retained scans, one graph of agents, MCP servers, packages and credentials, SSO and audit in your own infrastructure (self-host).

All three are free under Apache-2.0 and are adoption paths, not editions. There is no managed cloud offering today; community support runs on GitHub (deployment chooser, support model).

Why an AI supply-chain BOM

A CVE in an AI package, a poisoned tool description or an over-scoped credential matters by what the agent that loads it can reach. A package SBOM stops at packages; agent-bom records the chain, agent → MCP server → tool → package → credential → data, and keeps the evidence for every edge.

Sample production AI environment: Document Intake Agent uses a document-tools MCP server that depends on pillow 9.0.0, linked to KEV-listed CVE-2023-4863; Support Triage Agent uses a ticketing MCP server that references TICKETING_API_KEY, which can access a customer ticket archive

Sample data. What the sample shows

What it covers

Agents and MCP servers, models and AI platforms, dependencies, code, containers and IaC, cloud and data platforms, and a runtime MCP proxy and gateway. Exports are SARIF, CycloneDX, SPDX, JSON and HTML.


Coverage by area
Tool herunterladen

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Das ultimative OSINT-Toolkit: Untersuchungsgraph, Konfidenzbewertung, Alias-Familien, Karte, Zeitleiste und Berichte. 49 Module, 400+ Websites, keine API-Schlüssel erforderlich.

    790
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    508
  • 3

    ARTEX

    baarai/artex

    LLM-basierte Multi-Agenten-Plattform für autonome Penetrationstests mit Planer-/Worker-Agenten, Asset- und Explorationsgraphen, MITM-Verkehrsaufzeichnung und Schwachstellen-Retesting.

    435
  • 4

    redforge

    cybersecurity91/redforge

    Browser-seitiges Red-Team-Toolkit mit 102 Offline-Tools für Recon, Payload-Generierung, Credential-Angriffe, Krypto, Encoding und Engagement-Reporting.

    346
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Das System der Handlung für KI-native Cybersicherheit – wo Absicht zu gesteuerter Ausführung wird, Beweise zu operativem Gedächtnis werden und jeder Einsatz den nächsten verbessert.

    263
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT-Plattform, die Shadowserver-Berichte in MongoDB einliest und sie als interaktive Karten, Analysen, Findings, Advisories und Executive-Dashboards wiedergibt.

    260

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →