


Bash-Tool für wiederholte Wi-Fi-Sicherheitsprüfungen zu Fuß, mit Nachweisberichten. (neu erdachtes WLAN-WarDriving)



CyclePatrol ist ein einziges Bash-Skript, cp.sh. Es ist ein Werkzeug zur Bewertung der Wi-Fi-Sicherheit für das Terminal.
Es läuft unter Linux und Android (Kali NetHunter). Es benötigt root.
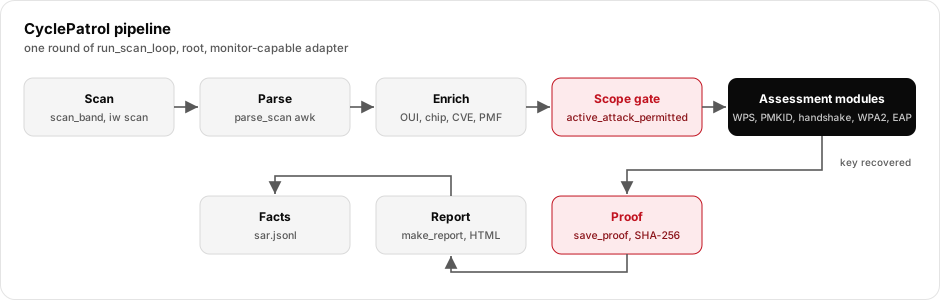
Das Werkzeug läuft in einer Schleife. In jeder Runde:
Nur zur autorisierten Nutzung. CyclePatrol führt aktive drahtlose Angriffe aus. Verwende es nur in Netzwerken, die dir gehören oder für die du eine schriftliche Genehmigung zum Testen hast.
Diese Dokumentation wurde anhand des Quellcodes verfasst. Sie lehrt nicht, wie man Netzwerke angreift. Sie erklärt, wie das Werkzeug aufgebaut ist, wie Daten fließen und wo die Sicherheitslogik liegt.
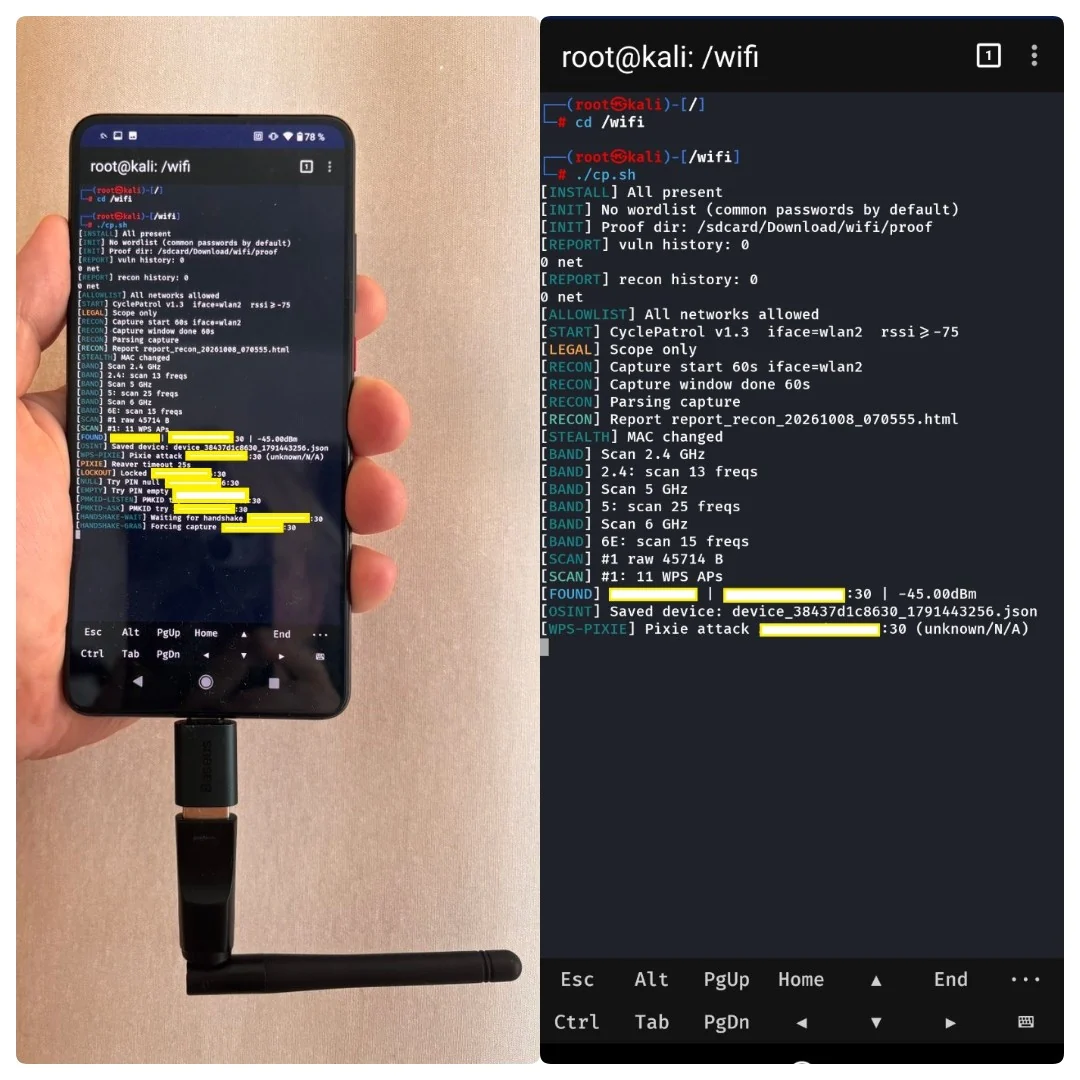
| Element | Wert | Quelle |
|---|---|---|
| Werkzeugname | CyclePatrol | TOOL_NAME |
| Version | 1.6 | VERSION |
| SAR-/Berichtsversion | 1 / 5 | SAR_VERSION / REPORT_VERSION |
| Sprache | Bash 5+ | Skriptkopf |
| Berechtigung | root erforderlich | run_precheck |
| Standard-Schnittstelle | wlan2 | DEF_IFACE |
| Standard-Logverzeichnis | /sdcard/Download/wifi | DEF_LOG_DIR |
| Verfolgte Dateien | cp.sh, vendor/oui.json, vendor/vendors.json, README.md, LICENSE, docs/ | Repo-Wurzel |
| Konfiguration | nur Umgebungsvariablen + CLI-Flags | main |
# 1. get the code
git clone https://github.com/buybitart/cyclepatrol
cd cyclepatrol

# 2. make it runnable
chmod +x cp.sh

# 3. start (root required)
sudo ./cp.sh
Hilfe und die vollständige Optionsliste:
./cp.sh --help
flowchart TD
    M[main parse CLI] --> AI[auto_install_deps apt]
    AI --> PC[run_precheck validate_env root iface tmp dirs allowlists]
    PC --> RC{recon mode?}
    RC -- "--recon" --> RE[run_recon airodump-ng] --> RPT1[report_recon_*.html] --> END1[exit]
    RC -- default --> R0[run_recon once at start]
    R0 --> LOOP[run_scan_loop]
    LOOP --> MAC[stealth MAC rotate]
    MAC --> SCAN[scan_band 2.4 / 5 / 6E via iw scan]
    SCAN --> PARSE[parse_scan awk -> targets]
    PARSE --> PT[process_target per AP, up to MAX_TARGETS]
    PT --> REP[make_report report_*.html]
    REP --> SLEEP[sleep COOLDOWN] --> LOOP
Details siehe docs/architecture.md und docs/data-flow.md.
| Komponente | Funktionen (Beispiele) | Aufgabe |
|---|---|---|
| Start / Konfiguration | main, validate_env, run_precheck, auto_install_deps | Flags parsen, Root + Interface + Tools prüfen, temporäre Verzeichnisse anlegen |
| Interface-Steuerung | ensure_mode, iface_set_type, iface_set_channel, iface_do_scan | Monitor-/Managed-Modus, Kanal, iw-Scan |
| Stealth | stealth_mac_rotate, stealth_gen_mac, stealth_wps_id_block | zufällige MAC, zufällige WPS-UUID |
| Scan + Parsen | scan_band, parse_scan | iw scan-Ausgabe sammeln, Beacons in Felder parsen |
| Anreicherung | get_chip, get_cves, detect_dpp_vulns, Vendor-KB-Lookups | OUI → Hersteller → Chipsatz, CVE-Hinweise, DPP-Prüfungen |
| Scope-Gate | active_attack_permitted, allowlist_init_active | entscheiden, ob ein aktives Modul auf einer BSSID laufen darf |
| Assessment-Module | attack_pixie, attack_vendor, attack_pmkid, attack_deauth_handshake, attack_wpa_psk_brute, attack_wpa_enterprise_eviltwin | die Funk-Tests (umschließen externe Tools) |
| Offline-Crack | offline_crack, _hashcat_22000, _aircrack_cap | erfassten PMKID / Handshake knacken |
| Nachweise + Ausgabe | sar_store_record, save_proof, make_report, recon_report | JSONL-Fakten, Proof-Dateien, HTML-Berichte |
| Standort | location_fix, location_nmea_feeder | GPS-Tagging für War-Driving (Android / gpsd) |
Vollständige Funktionsübersicht: docs/project-structure.md.
CyclePatrol ist ein Orchestrator. Es ruft Standard-Linux-Funkwerkzeuge als Subprozesse auf.
| Tool | Verwendet von | Zweck |
|---|---|---|
iw, ip, nmcli, macchanger | Interface + Stealth | Scan, Modus, Kanal, MAC |
reaver | attack_pixie, attack_vendor, attack_null, attack_empty, attack_user_pin | WPS-Registrar-Austausch |
pixiewps | attack_pixie | Offline-WPS-PIN-Wiederherstellung |
wpa_supplicant, wpa_cli, wpa_passphrase | WPS, verify_psk_live, attack_wpa_psk_brute | Assoziation, Live-Schlüsselprüfung |
hcxdumptool, hcxpcapngtool | attack_pmkid, attack_pmkid_active | PMKID-Erfassung → hashcat 22000 |
tcpdump | eapol_passive_capture | passive EAPOL-Erfassung |
airodump-ng, aireplay-ng, mdk4 | attack_deauth_handshake, run_recon | Erfassung, Deauth, Recon |
hashcat, aircrack-ng | offline_crack | Offline-Crack von Erfassungen |
eaphammer, hostapd-wpe | attack_wpa_enterprise_eviltwin | 802.1X-Evil-Twin-Anmeldedaten-Erfassung |
dragondrain, dragontime | sae_dos_dragondrain, sae_timing_dragontime | WPA3-/SAE-Prüfungen. Funktionen definiert, aber nie aufgerufen (toter Code), siehe docs/security.md |
tshark, airgraph-ng | recon_report | Uptime-Parsen, Diagramme |
gpsd, termux-location, gpspipe | Standort | GPS-Fix / Tagging |
jq | Vendor-KB | JSON-Lookup (optional) |
Moduldetails und Gating: docs/modules.md.
Alles wird unter LOG_DIR geschrieben (Standard /sdcard/Download/wifi).
Das Verzeichnis wird mit chmod 700 angelegt. Ausgabedateien verwenden chmod 600.
| Pfad | Inhalt |
|---|---|
sar.jsonl | Fakten pro AP, ein JSON-Objekt pro Zeile |
cp_audit.log | Audit-Log: AP, Methode, Ergebnis |
report_*.html | Assessment-Bericht (Befunde, Schweregrad, Nachweise) |
report_recon_*.html | Bericht zur passiven Recon-Erhebung |
proof/proof_*.conf | Nachweis eines bestätigten Befunds: PIN, PSK, SHA-256, Live-Verify |
proof/proofs.jsonl | Chain-of-Custody-Manifest: eine Zeile pro Proof-Datei, mit ihrer SHA-256 |
proof/handshake_*.cap | erfasster 4-Way-Handshake |
proof/pmkid_*.22000 | PMKID im hashcat-22000-Format |
known_bssids.txt, processed_bssids.txt | Zustand (bereits Erledigtes überspringen) |

