

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
Kategorien

Webanwendungs-Exploitation

Speziell entwickelte Tools zur Ausnutzung gängiger Webanwendungs-Schwachstellen (z. B. SQL-Injection, XSS).

Kitploit empfohlen
Top-Tools

10 ausgewählt
sqlmap preview#1

sqlmap

GitHubsqlmapproject/sqlmap
38.2kvor 21h 6m
beef preview#2

beef

GitHubbeefproject/beef
11.0kvor 2 Tagen
nuclei preview#3

nuclei

GitHubprojectdiscovery/nuclei
30.4kvor 13h 46m
zaproxy preview#4

zaproxy

GitHubzaproxy/zaproxy
15.6kvor 0 Tagen
XSStrike preview#5

XSStrike

GitHubs0md3v/xsstrike
15.1kvor 1 Jahr
ffuf preview#6

ffuf

GitHubffuf/ffuf
16.5kvor 1 Monat
dirsearch preview#7

dirsearch

GitHubmaurosoria/dirsearch
14.6kvor 16 Tagen
feroxbuster preview#8

feroxbuster

GitHubepi052/feroxbuster
8.0kvor 7 Tagen
nikto preview#9

nikto

GitHubsullo/nikto
10.6kvor 3 Monaten
wpscan preview#10

wpscan

GitHubwpscanteam/wpscan
9.7kvor 14h 17m
NeuesteRelevanzBeliebtesteKürzlich aktualisiert
14887 Ergebnisse
CVE-2025-4123-Exploit preview

CVE-2025-4123-Exploit

GitHubmorphykutay/cve-2025-4123-exploit

Proof-of-Concept-Tool, das eine manipulierte Nutzlast an ein Ziel sendet und offene Weiterleitungs-Schwachstellen erkennt, indem es 301/302-Antworten…
vulnerability-analysisexploitationweb-application-exploitation+1
vor 1 Jahr
cve-2026-5147-exp preview

cve-2026-5147-exp

GitHublan1oc/cve-2026-5147-exp

Exploit-Skript für CVE-2026-5147, das boolesche und zeitbasierte Blind-SQL-Injection gegen MySQL-Schnittstellen durchführt, um Version, Datenbank,…
vulnerability-analysisexploitationweb-application-exploitation+1
vor 7 Monaten
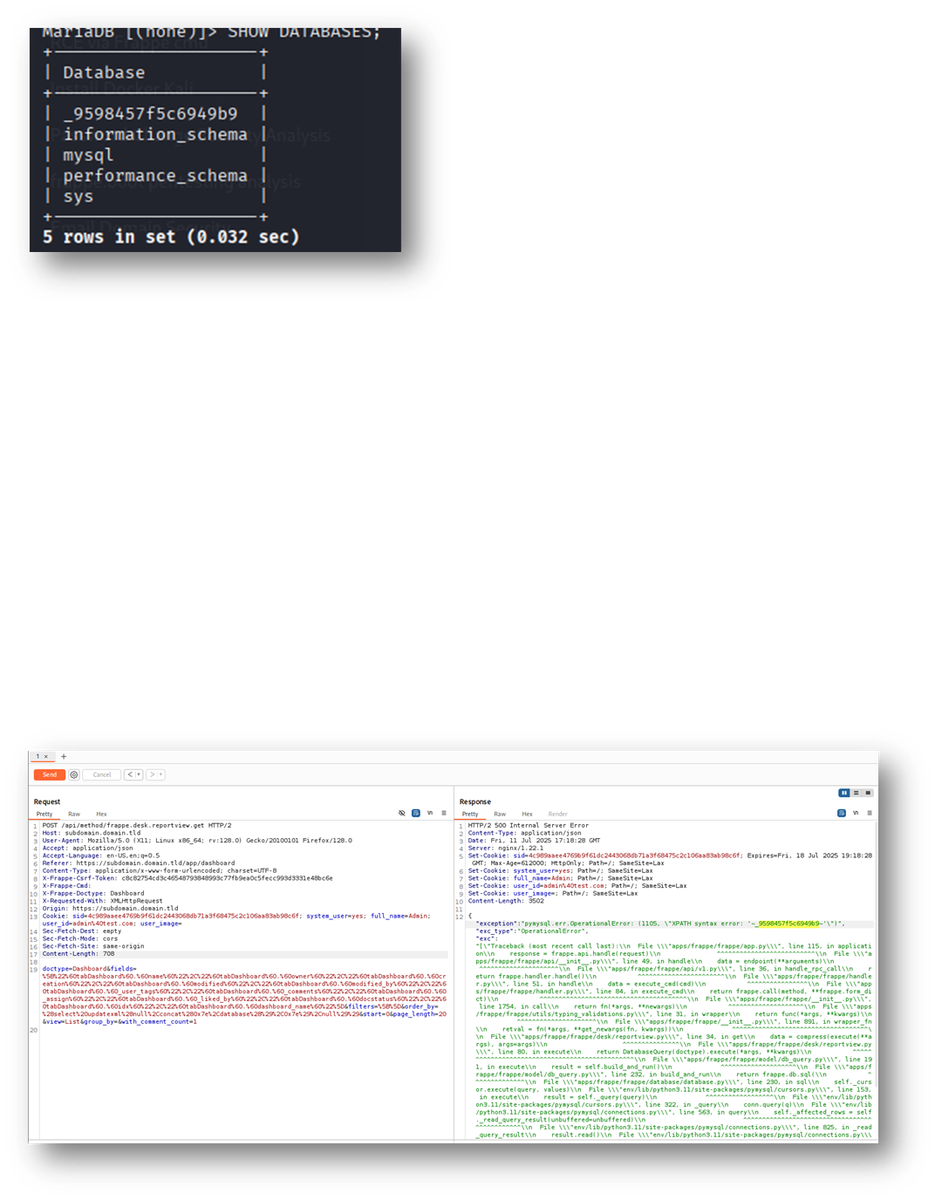
CVE-2025-56381 preview

CVE-2025-56381

GitHubmoalali/cve-2025-56381

ERPNEXT v15.67.0 wurde festgestellt, dass es mehrere SQL-Injection-Schwachstellen im Endpunkt /api/method/frappe.desk.reportview.get über die…
vulnerability-analysisexploitationweb-application-exploitation+2
1vor 1 Jahr
CVE-2021-44593 preview

CVE-2021-44593

GitHubmister-joe/cve-2021-44593

Öffentliche Offenlegung und Writeup zu CVE-2021-44593, einer nicht authentifizierten SQL-Injection in Simple College Website, die zu beliebigem…
vulnerability-analysisexploitationweb-application-exploitation+2
2vor 4 Jahren
CVE-2026-31908 preview

CVE-2026-31908

GitHubmehranturk/cve-2026-31908

Proof-of-Concept-Exploit für CVE-2026-31908, eine kritische Header-Injection-Schwachstelle in Apache APISIX, die die Umgehung der Authentifizierung…
vulnerability-analysisexploitationweb-application-exploitation+3
1vor 7 Monaten
Exploit-CVE-2026-1357 preview

Exploit-CVE-2026-1357

GitHubitsismarcos/exploit-cve-2026-1357

Exploit für CVE-2026-1357 im WordPress-WPVivid-Plugin, der Remote-Codeausführung über manipulierte AES-verschlüsselte Payloads und Directory…
vulnerability-scannersexploitationweb-application-exploitation+2
1vor 9 Monaten
cve-2026-24858 preview

cve-2026-24858

GitHubgagaltotal/cve-2026-24858

Python-Helfer zum Scannen der Fortinet-Webverwaltung auf CVE-2026-24858 SSO-Authentifizierungsumgehung und optional zum Senden expliziter Payloads…
vulnerability-scannersexploitationweb-application-exploitation+2
1vor 9 Monaten
marimo_CVE-2026-39987_RCE_PoC preview

marimo_CVE-2026-39987_RCE_PoC

GitHubfevar54/marimo_cve-2026-39987_rce_poc

PoC für CVE-2026-39987: Pre-Authentifizierungs-RCE über WebSocket in Marimo vor 0.23.0 (CVSS 9.3).
reconnaissancevulnerability-analysisexploitation+3
vor 7 Monaten
CVE-2026-3786 preview

CVE-2026-3786

GitHubmefhika120/cve-2026-3786

Proof-of-concept-Exploit für CVE-2026-3786, eine SQL-Injection-Schwachstelle in EasyTheme, die Datenbankmanipulation für Sicherheitsforschung…
vulnerability-analysisexploitationweb-application-exploitation
vor 8 Monaten
CVE-2024-33297 preview

CVE-2024-33297

GitHubmathsabo/cve-2024-33297

# XSS-Schwachstelle (gespeichert) in Microweber < 2.0.9

vulnerability-analysisexploitationweb-application-exploitation+2
vor 1 Jahr
CVE-2026-21876 preview

CVE-2026-21876

GitHubmefhika120/cve-2026-21876

Minimaler PoC und Docker-Container, der einen WAF-Bypass in OWASP ModSecurity CRS über die Verarbeitung von Multipart-Zeichensätzen demonstriert, was…
vulnerability-analysisexploitationweb-application-exploitation+2
vor 10 Monaten
cve-2025-59287-exploit-poc preview

cve-2025-59287-exploit-poc

GitHubmaxymgorn/cve-2025-59287-exploit-poc

Proof-of-Concept-Exploit für CVE-2025-59287, eine kritische, nicht authentifizierte RCE in WSUS über unsichere BinaryFormatter-Deserialisierung, die…
vulnerability-analysisexploitationweb-application-exploitation+3
vor 1 Jahr
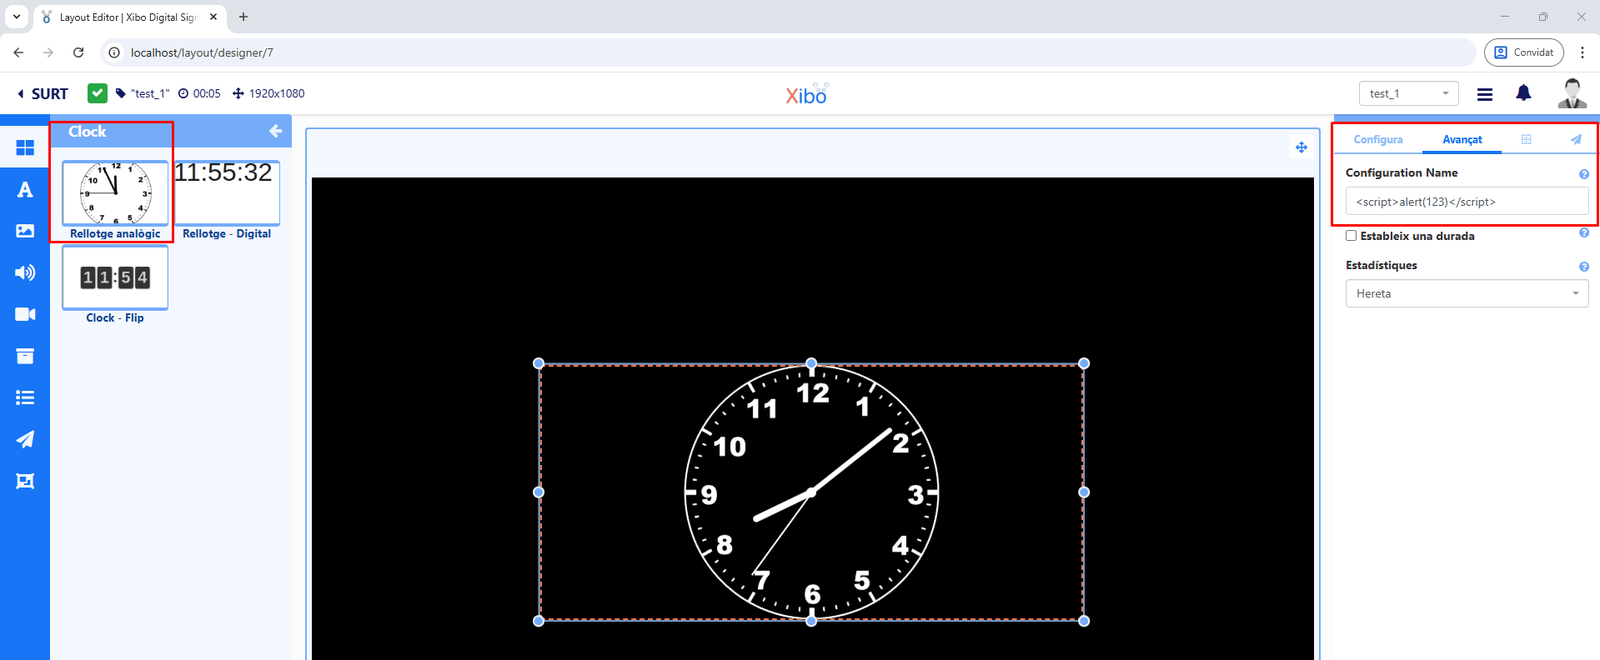
smartermail-CVE-2026-23760-poc preview

smartermail-CVE-2026-23760-poc

GitHubmaxmnml/smartermail-cve-2026-23760-poc

CVE-2026-23760 – Eine Authentifizierungsumgehung über die Passwort-Reset-API in SmarterMail.
authentication-authorizationvulnerability-analysisexploitation+3
7vor 9 Monaten
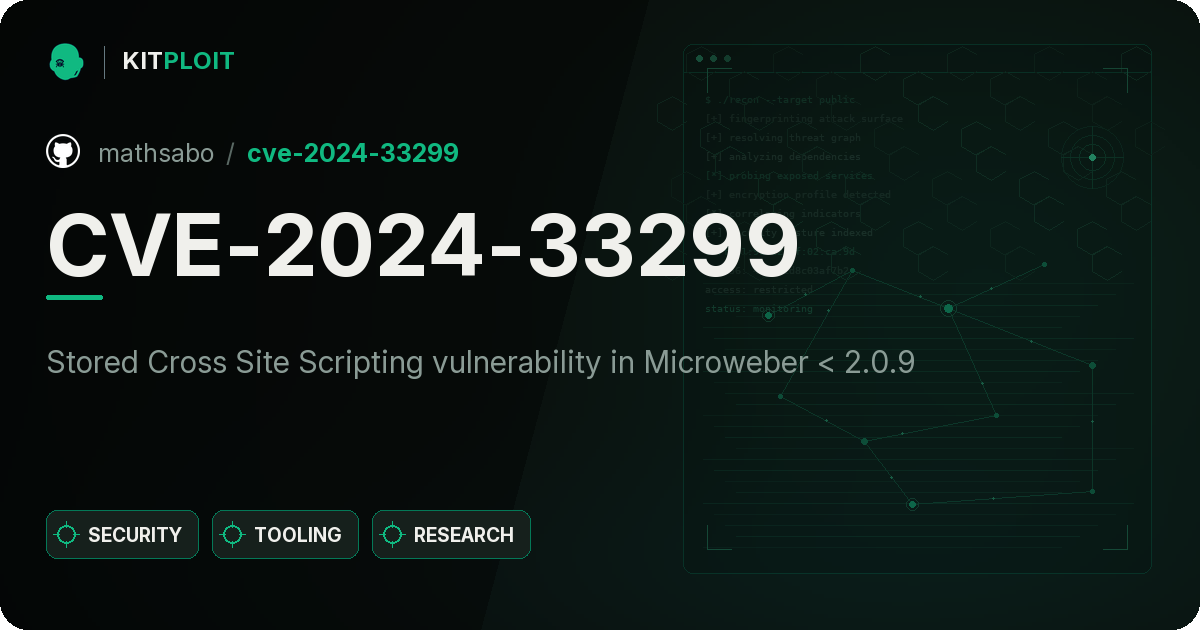
CVE-2025-41089 preview

CVE-2025-41089

GitHubmarinafabregat/cve-2025-41089

Reflektiertes Cross-Site-Scripting (XSS) in Xibo CMS v4.1.2 von Xibo Signage, verursacht durch eine fehlende ordnungsgemäße Validierung der…
vulnerability-analysisexploitationweb-application-exploitation+2
4vor 1 Jahr
CVE-2024-33299 preview

CVE-2024-33299

GitHubmathsabo/cve-2024-33299

# XSS-Schwachstelle (gespeichert) in Microweber < 2.0.9
vulnerability-analysisexploitationweb-application-exploitation+2
vor 1 Jahr
CVE-2024-33298 preview

CVE-2024-33298

GitHubmathsabo/cve-2024-33298

# XSS-Schwachstelle (gespeichert) in Microweber < 2.0.9
vulnerability-analysisexploitationweb-application-exploitation+2
vor 1 Jahr
CVE-2023-22527-POC preview

CVE-2023-22527-POC

GitHubmanh130902/cve-2023-22527-poc

Eine Schwachstelle mit kritischem Schweregrad für Remote Code Execution (RCE) (CVE-2023-22527) wurde in Confluence Server und Data Center entdeckt.
vulnerability-analysisexploitationweb-application-exploitation+2
22vor 2 Jahren
CVE-2025-8081-Elementor preview

CVE-2025-8081-Elementor

GitHublyesh4ck/cve-2025-8081-elementor

Proof-of-Concept-Exploit für CVE-2025-8081, ein beliebiges Dateilesen im Elementor-WordPress-Plugin, das authentifizierten Administratoren das Lesen…


vulnerability-analysisexploitationweb-application-exploitation+2
vor 1 Jahr
Zurück1…959697…100Weiter







