

sleuthkit
 sleuthkit/sleuthkit
用于分析磁盘和文件系统镜像、恢复已删除数据、生成时间线以及使用哈希验证证据的取证库和CLI工具包。
disk-forensicshash-analysisforensics+3
 arkime/arkime
Arkime 是一个开源的、大规模、全包捕获、索引和数据库系统。
 wiltodelta/remove-ai-watermarks
Remove visible and invisible AI watermarks from images and video, and AI provenance metadata from images, video, and audio. Python library, CLI, and…
 ericzimmerman/kapefiles
此仓库用作社区为 KAPE 创建的 Targets 和 Modules 的存放处。
 microsoft/avml
用于取证和应急响应的便携式 Linux 内存采集工具,可捕获与 LiME 兼容的内存镜像,并支持可选压缩与远程流式传输。
 magicsword-io/loldrivers
精心策划的易受攻击和恶意Windows驱动程序数据库,包含YARA、Sigma、ClamAV和Sysmon检测规则,用于主动威胁狩猎和事件响应。

 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
 circl/ail-framework
AIL框架 - 分析信息泄露框架。项目已迁移至 https://github.com/ail-project
 aipentest/cyberstrikeai
AI原生网络安全的行动系统——在这里,意图转化为受治理的执行,证据转化为运营记忆,每一次操作都让下一次更完善。
 kunai-project/kunai
基于eBPF的Linux安全监控与威胁猎手,提供按时间顺序排列、具备容器感知能力的事件,并支持基于主机的关联分析,适用于事件响应和取证分析。
 secdev/scapy
基于 Python 的交互式数据包操作库,用于在多种协议中伪造、解码、发送、捕获和分析网络数据包,支持扫描、路由追踪、攻击和网络发现。
 katrielmoses/mailaccess
Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess

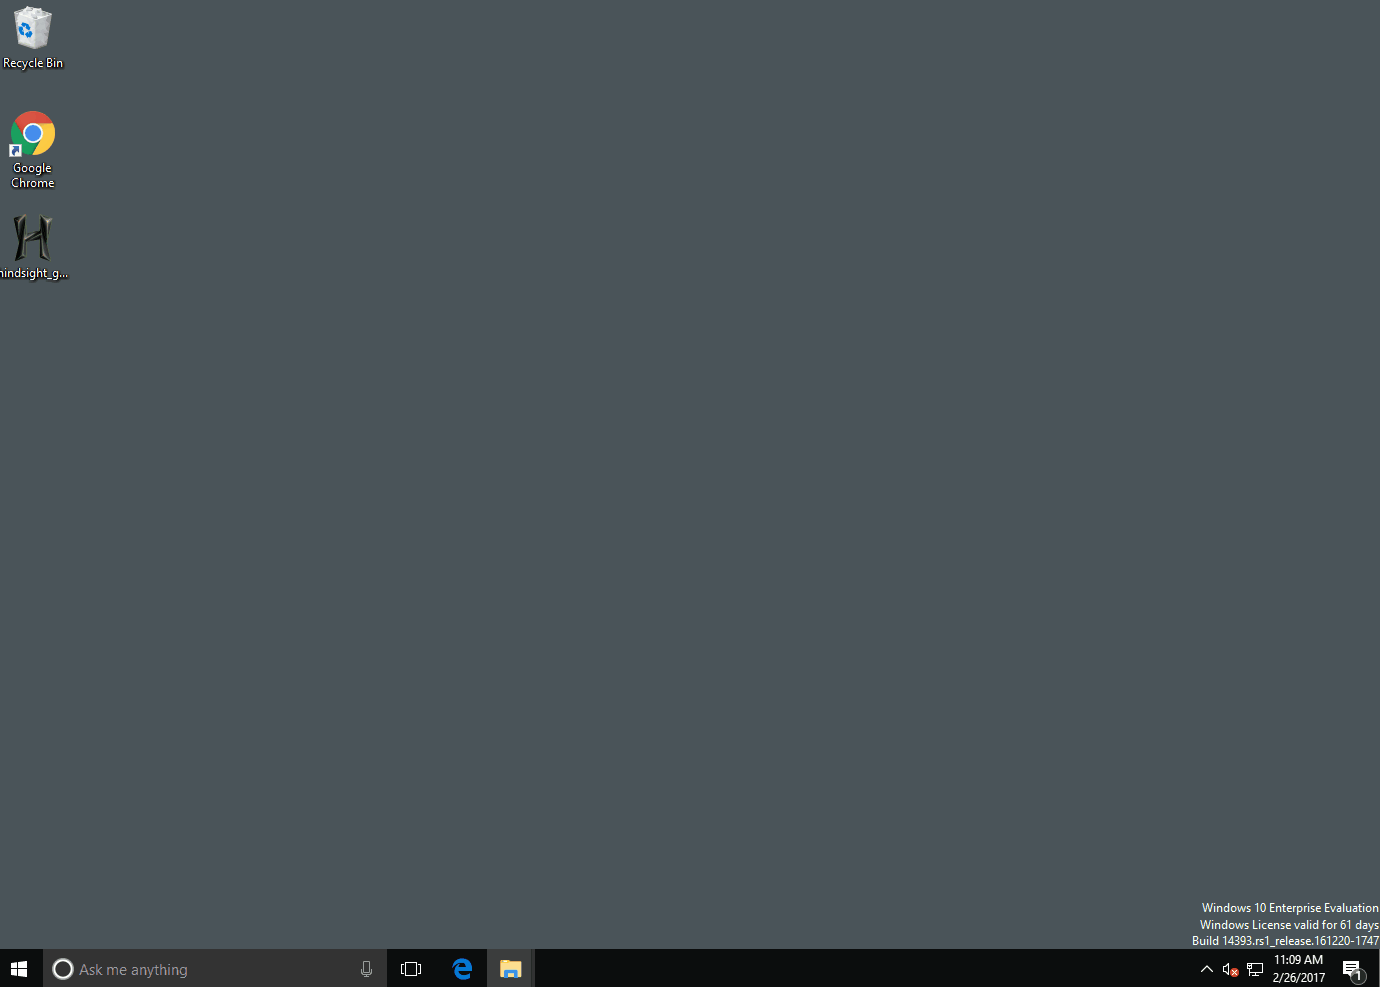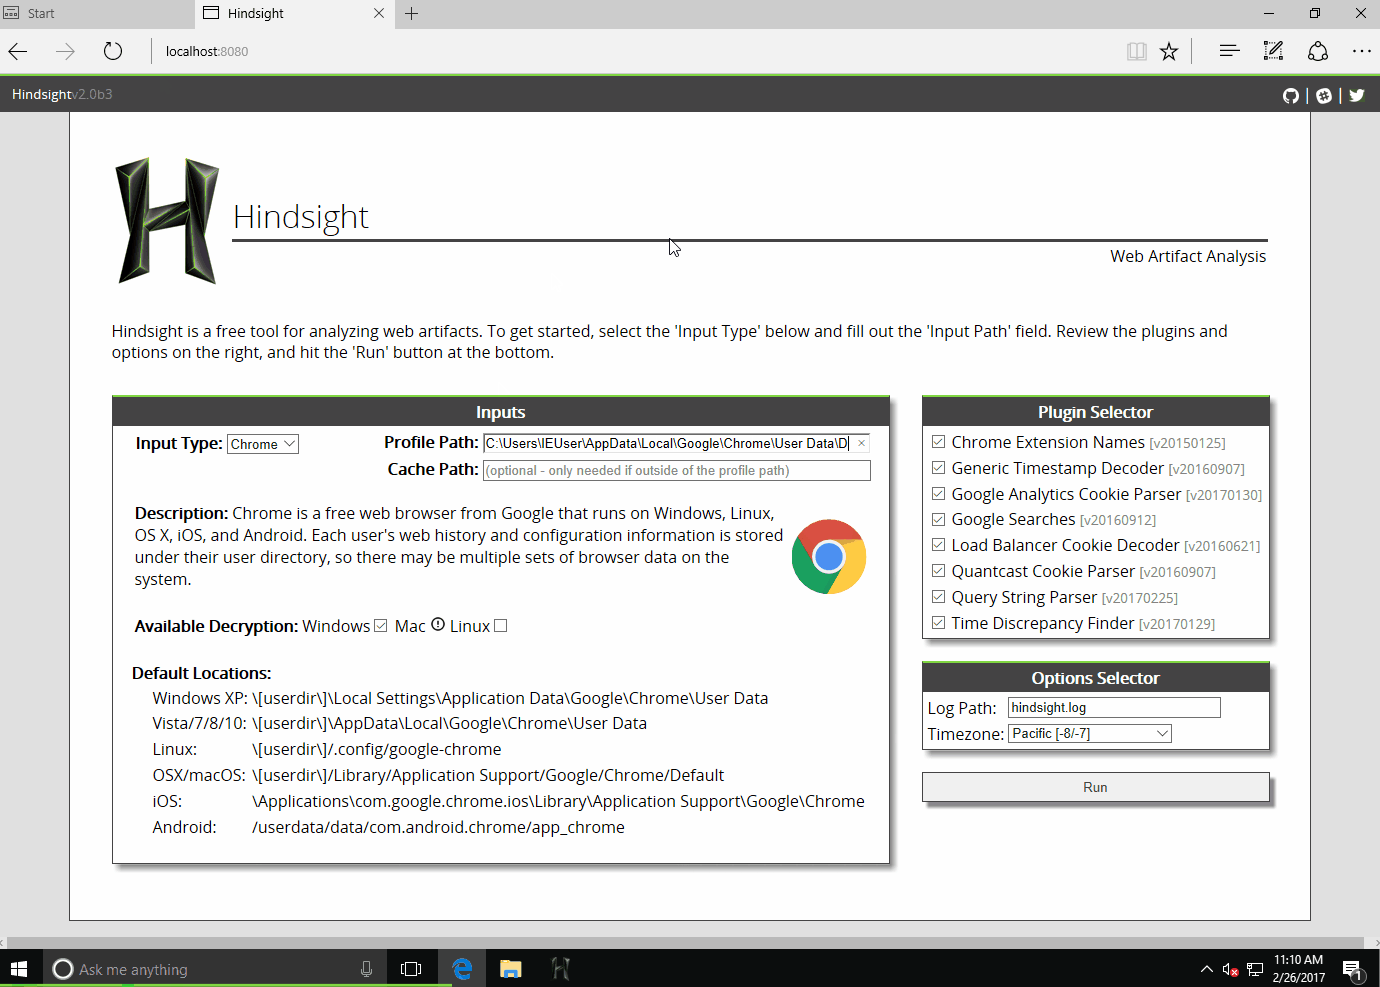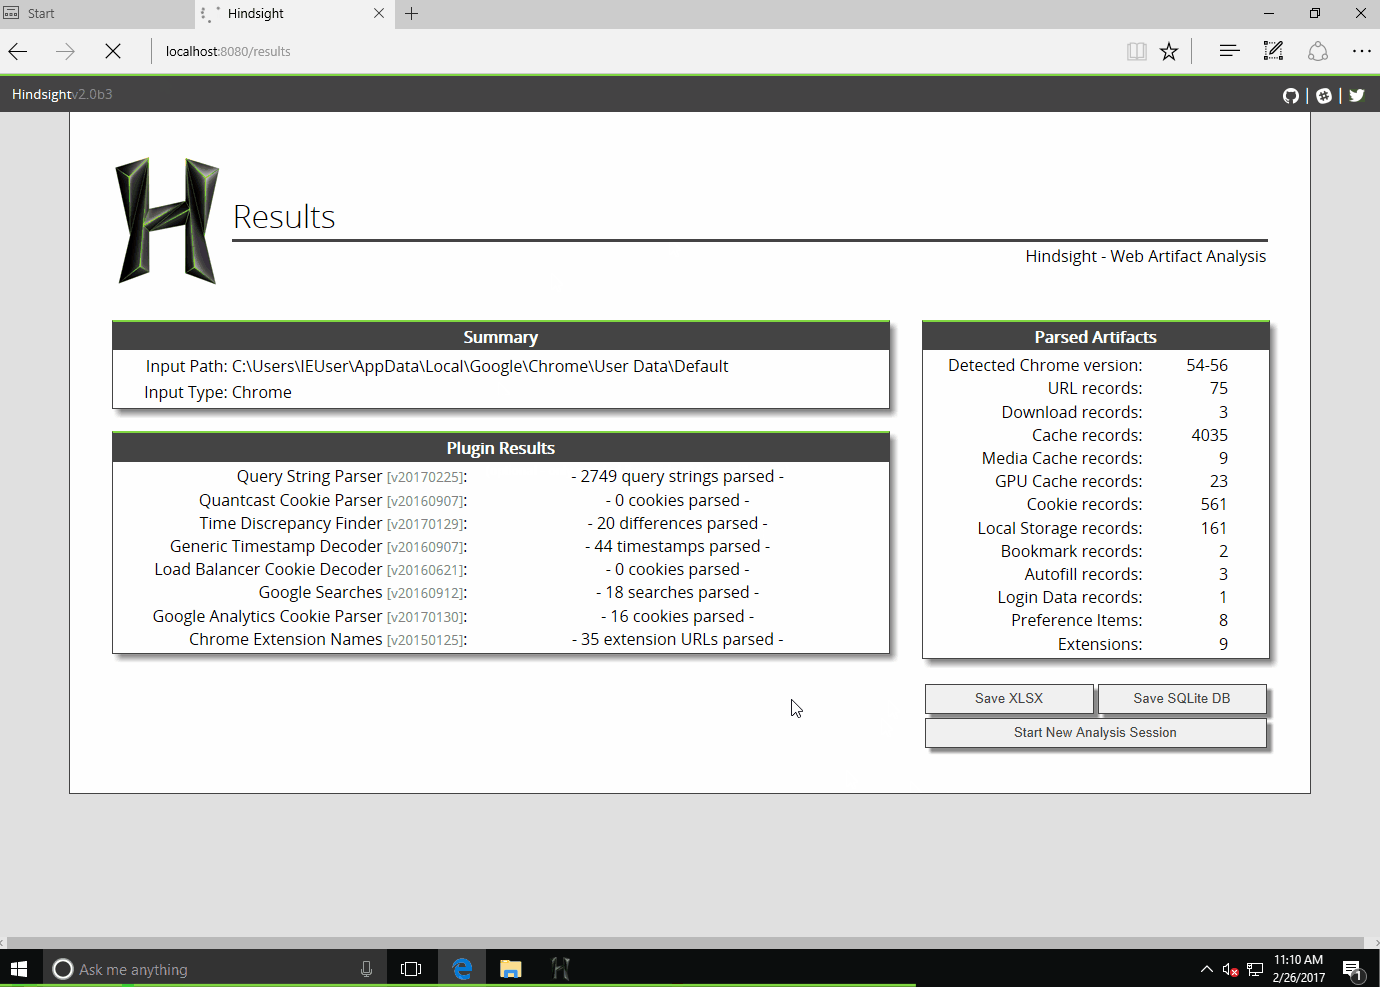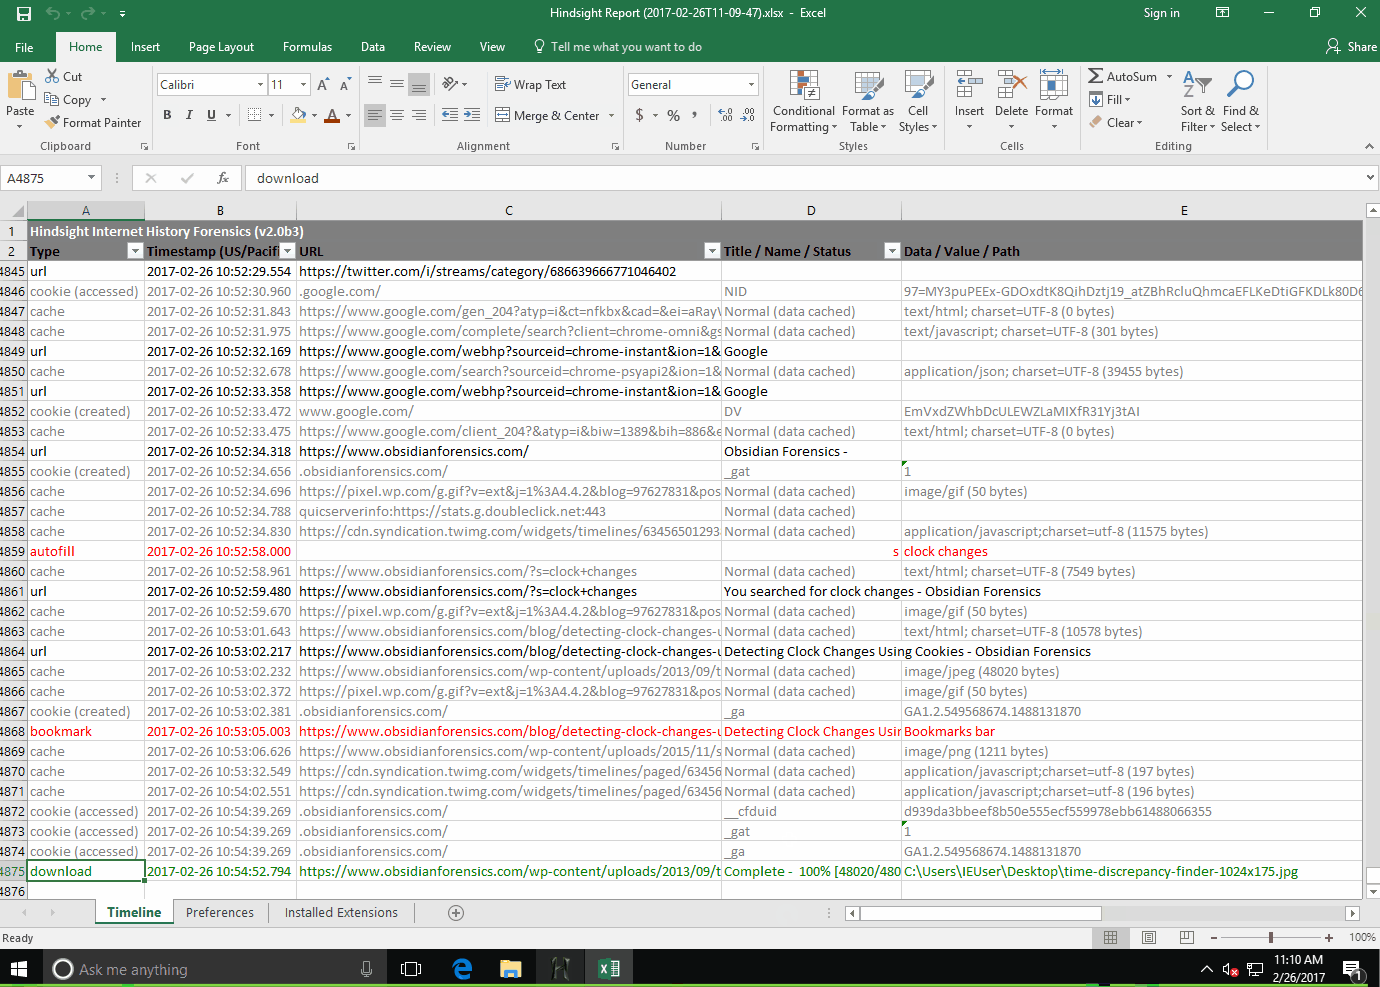 ryandfir/hindsight
用于 Google Chrome、其他基于 Chromium 的浏览器以及 Mozilla Firefox 的浏览器取证工具
 ssrajadh/sentrysearch
使用 Gemini Embedding 2 或 Qwen3-VL 对视频进行语义搜索。