
 owasp/sbom-vex-taint-analysis
Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX documents in compliance with OWASP GenAI guidelines.

Automatically generate signed CycloneDX VEX documents from SBOMs using a secure multi-agent AI pipeline built with the Microsoft Agent Framework (C# / .NET) in accordance with the OWASP GenAI Security Project guidelines.


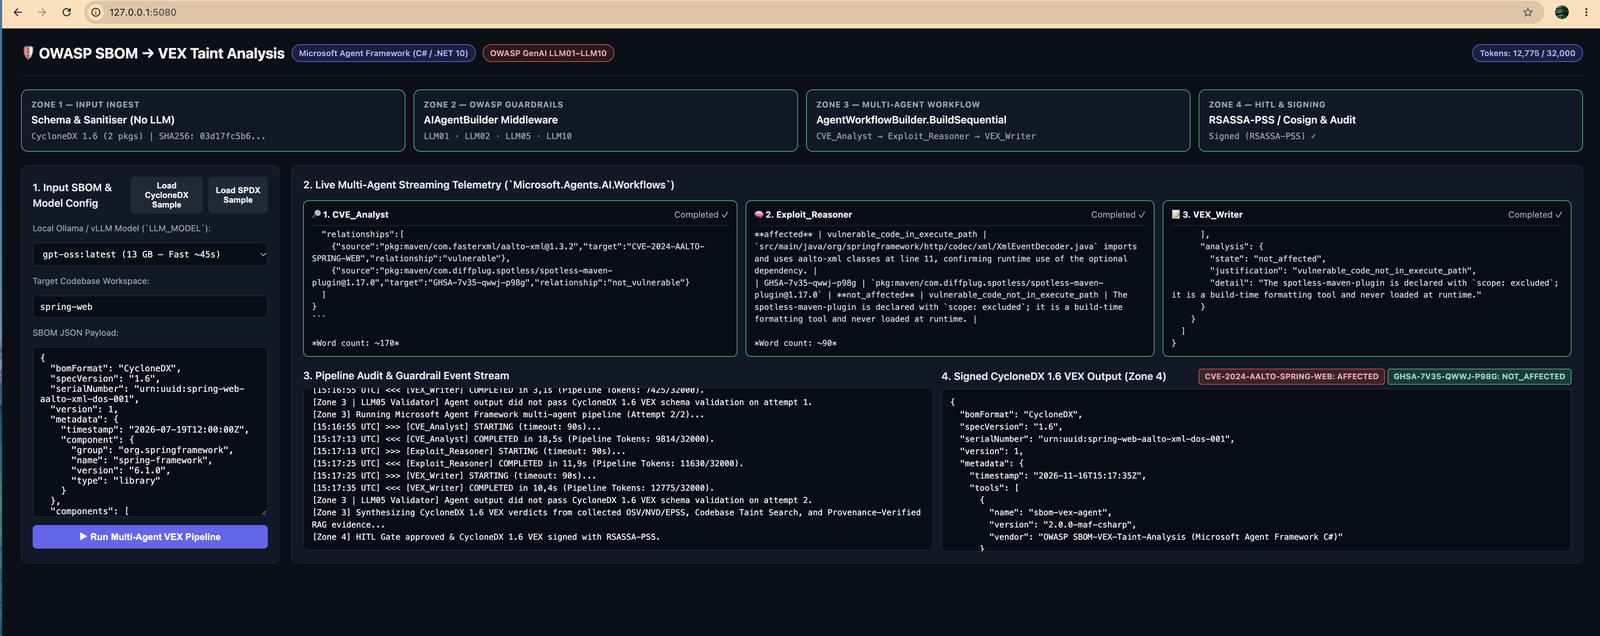
Generating an SBOM surfaces hundreds of CVEs. In practice, over 90% are not exploitable in a specific product's runtime context. Without a Vulnerability Exploitability eXchange (VEX) document, every downstream tool — Dependency-Track, release gates, procurement checklists — drowns in false positives.
Read the WIKI for more technical details and results of testing.
Manual VEX generation is time-consuming and does not scale. A skilled analyst can spend hours assessing a single component. A production SBOM may contain 500–2,000 components.
This project automates that reasoning pipeline — securely, without vendor lock-in, with all data remaining on your infrastructure.
Real-world motivation: In 2024, security researcher Johanna Curiel documented exactly this problem while analysing the Kubernetes Java Client (LinkedIn article). The OSV scanner identified a high-risk CVE in
com.diffplug.spotless:spotless-maven-plugin 1.17.0in seconds. Determining it wasnot_affected(build-time plugin, never executed at runtime) took hours of manual analysis. This project automates that reasoning step.
Four security zones. Nothing crosses a boundary without explicit validation.
┌─────────────────────────────────────────────────────────────────┐
│  ZONE 1 — Input ingestion (no LLM)                              │
│  SBOM upload → Schema validate → Sanitise → SHA-256 audit hash  │
└────────────────────────────┬────────────────────────────────────┘
                             │
┌────────────────────────────▼────────────────────────────────────┐
│  ZONE 2 — OWASP guardrail middleware (AIAgentBuilder.Use)       │
│  Prompt guard (LLM01) · Output filter (LLM02/05)                │
│  Agency limiter (LLM06) · Token budget & MaxMessages (LLM10)    │
└────────────────────────────┬────────────────────────────────────┘
                             │
┌────────────────────────────▼────────────────────────────────────┐
│  ZONE 3 — Multi-agent pipeline (Microsoft Agent Framework C#)   │
│                                                                  │
│  AgentWorkflowBuilder.BuildSequential                            │
│       ├── CVE Analyst       NVD v2 + OSV + EPSS per component   │
│       ├── Exploit Reasoner  Call graph · LLM reasoning · RAG    │
│       └── VEX Writer        CycloneDX 1.6 schema-validated      │
│                                                                  │
│  Vector store (Qdrant) — signed past VEX decisions              │
└────────────────────────────┬────────────────────────────────────┘
                             │
┌────────────────────────────▼────────────────────────────────────┐
│  ZONE 4 — Output, signing, audit                                │
│  Human-in-the-loop gate → cosign/GPG sign → audit log           │
└─────────────────────────────────────────────────────────────────┘
This project is designed against the OWASP Top 10 for LLM Applications 2025 and the OWASP Top 10 for Agentic Applications 2026.
| OWASP Risk | ID | Mitigation in this project |
|---|---|---|
| Prompt Injection | LLM01 | All SBOM fields sanitised before LLM injection; injection pattern blocklist in SbomIngestor and OwaspGuardrailMiddleware |
| Sensitive Info Disclosure | LLM02 | PII scrubber on all agent outputs; internal path filter (OwaspGuardrailMiddleware) |
| Improper Output Handling | LLM05 | CycloneDX 1.6 schema validation before signing; retry on failure |
| Excessive Agency | LLM06 | Read-only AIFunction tools during analysis; HITL gate for all CVSS ≥ 7.0 or affected rulings |
| System Prompt Leakage | LLM07 | Internal policies separated from system prompt |
| Vector / Embedding Weakness | LLM08 | Stored vectors signed with HMAC-SHA256; provenance checked before context injection |
| Unbounded Consumption | LLM10 | MaxMessageCount(20) in middleware; per-pipeline token budget; strict NVD/OSV HTTP timeouts |
Human-in-the-loop is mandatory. A VEX
not_affectedoraffectedstatement for a high-severity CVE is a legal-grade assertion. No VEX is signed without human reviewer approval. This is not configurable.
| Component | Tool | Notes |
|---|---|---|
| Agent orchestration | Microsoft Agent Framework (C# / .NET) | Microsoft.Agents.AI & Microsoft.Agents.AI.Workflows (replaces legacy AutoGen) |
| AI abstractions | Microsoft.Extensions.AI + Microsoft.Agents.AI.OpenAI | IChatClient, AIAgent, AIFunctionFactory, AIAgentBuilder middleware |
| LLM (recommended) | Qwen2.5-Coder-32B | Best structured JSON + security reasoning |
| LLM server | vLLM (prod) / Ollama (dev) | OpenAI-compatible API (VLLM_BASE_URL) |
| CVE data | NVD v2 API + OSV.dev + EPSS | All free, no API key required |
| Vector store | Qdrant | Self-hosted, provenance-signed past VEX decisions |
| SBOM formats | CycloneDX 1.4–1.7 (JSON), SPDX 2.2/2.3 (JSON) | Schema-validated and sanitised on ingest |
| VEX output | CycloneDX 1.6 VEX | Schema-validated before signing |
| Signing | cosign / RSASSA-PSS | Timestamped, SHA-256 payload signed, audit-logged |
| Audit log | Append-only JSONL / PostgreSQL | Every agent decision and signature recorded |
Everything runs on-premises. No data leaves your infrastructure.
Hardware (production):
Hardware (development / small SBOMs):
llama3.1:8b via OllamaSoftware:
dotnet)git clone https://github.com/OWASP/SBOM-VEX-Taint-Analysis
cd SBOM-VEX-Taint-Analysis
dotnet build SbomVexAgent/SbomVexAgent.csproj
# Development — Ollama (CPU/GPU, any laptop)
ollama pull llama3.1
ollama serve

# Production — vLLM (GPU required)
python -m vllm.entrypoints.openai.api_server \
  --model Qwen/Qwen2.5-Coder-32B-Instruct \
  --gpu-memory-utilization 0.90 \
  --host 0.0.0.0 --port 8000
Web Interface (Live Streaming Dashboard on http://localhost:5080):
dotnet run --project SbomVexAgent -- ui --port 5080







