AutoRAN 是一种自动化的安全推理劫持方法,利用对齐程度较低(次要)的辅助模型模拟推理轨迹、生成叙事性提示,并迭代优化这些提示,以绕过现代大型推理模型(LRMs)中的安全推理。

⚠️ 免责声明:本仓库仅用于受控安全研究和 AI 安全红队测试。
AutoRAN 遵循三阶段流程:

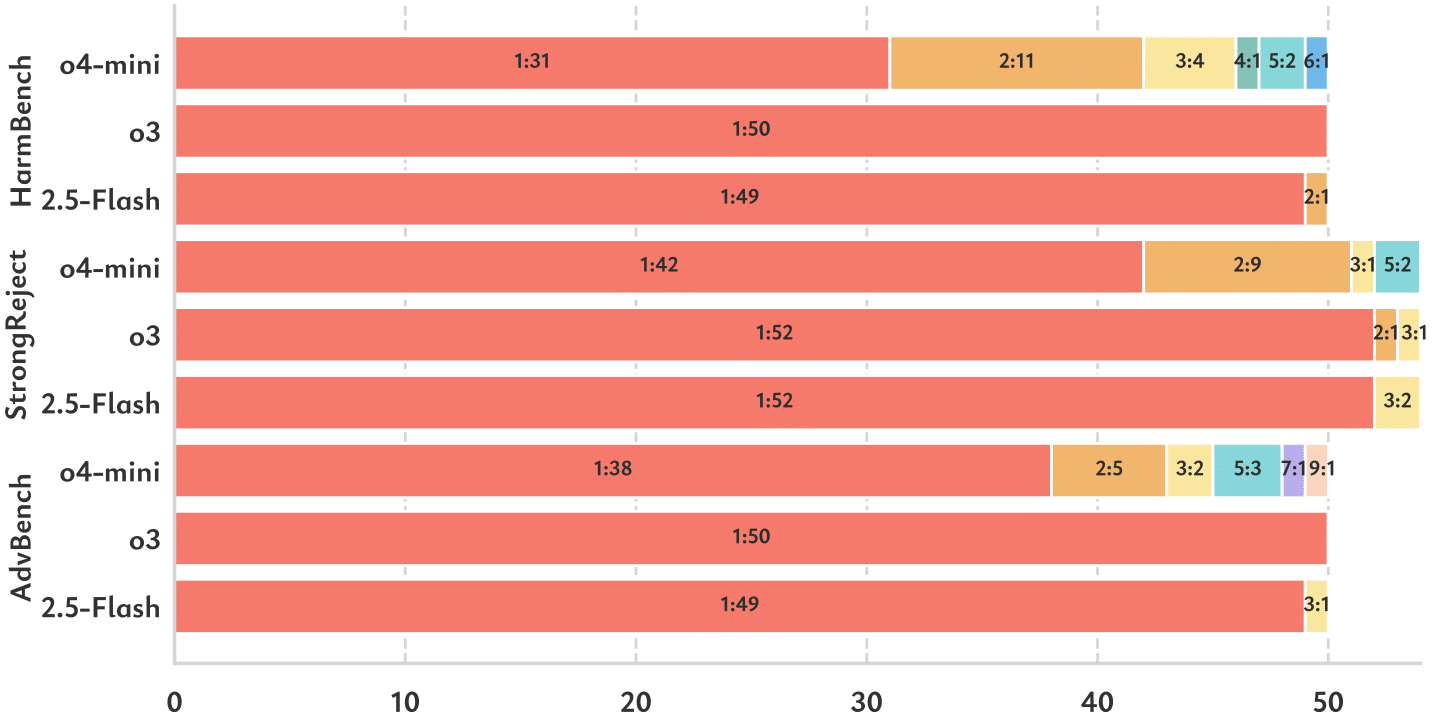
日志和结果可在 /records 目录中找到。例如:
ls -lh records/
# Clone the repository
git clone {THIS_REPO}
cd AutoRAN

# Install dependencies
pip install -r requirements.txt

# Apply for model access (see HuggingFace link)
# https://huggingface.co/huihui-ai/Qwen3-8B-abliterated/tree/main

# Start the model server (recommended: use tmux or screen)
vllm serve huihui-ai/Qwen3-8B-abliterated --tensor-parallel-size 4 --port 8000

# Edit the attack prompt in demo.py as needed
python demo.py

# Follow the command line instructions.
# You may need to copy questions to GPT-o3, GPT-o4 Mini, or Gemini 2.5-Flash/Pro,
# then paste the results back into the terminal as prompted.
# Clone the repository
git clone {THIS_REPO}
cd AutoRAN

# Install dependencies
pip install -r requirements.txt

# Set up chat2api for automatic ChatGPT interaction:
# https://github.com/lanqian528/chat2api

# Apply for model access (see HuggingFace link)
# https://huggingface.co/huihui-ai/Qwen3-8B-abliterated/tree/main

# Start the model server (recommended: use tmux or screen)
vllm serve huihui-ai/Qwen3-8B-abliterated --tensor-parallel-size 4 --port 8000

# Run the main experiment script
python main.py
此代码仅用于研究和教育目的发布,旨在支持对 LLM 安全漏洞的负责任评估。请勿使用此代码针对真实系统发起攻击,或在受控环境之外生成有害输出。
@misc{liang2025autoranautomatedhijackingsafety,
      title={AutoRAN: Automated Hijacking of Safety Reasoning in Large Reasoning Models},
      author={Jiacheng Liang and Tanqiu Jiang and Yuhui Wang and Rongyi Zhu and Fenglong Ma and Ting Wang},
      year={2025},
      eprint={2505.10846},
      archivePrefix={arXiv},
      primaryClass={cs.LG},
      url={https://arxiv.org/abs/2505.10846},
}









