内核 rootkit,驻留在 Windows 注册表值数据内部。 作者:Oleksiuk Dmytro(又名 Cr4sh)
http://twitter.com/d_olex http://blog.cr4.sh [email protected]
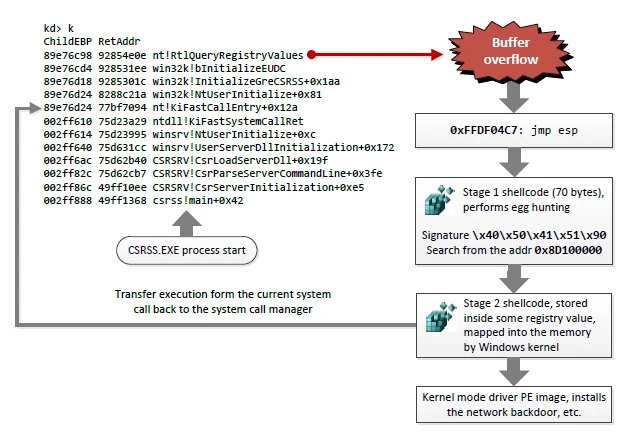
该 rootkit 利用 win32k.sys 中的零日漏洞(函数 win32k!bInitializeEUDC() 中的缓冲区溢出)在操作系统启动时获得执行权限。
特性:
基于 NDIS 的网络后门(+ meterpreter/bind_tcp)。
为避免被检测到未知的可执行代码,它会将自身在内存中移动到某些默认 Windows 驱动程序的可丢弃节之上。
公共反 rootkit 工具完全无法检测。
可在 Windows 7(SP0、SP1)x86 上运行。
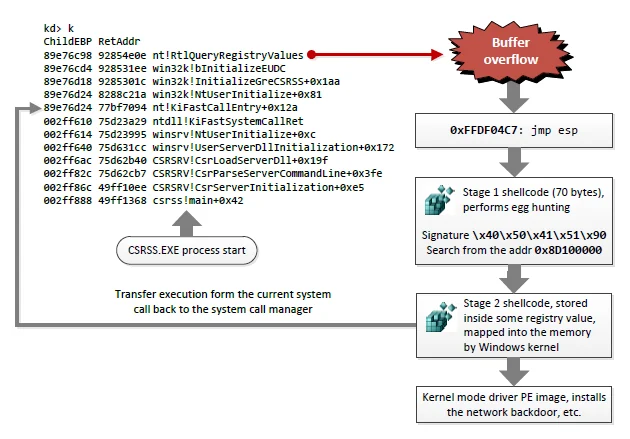
该 rootkit 最初在我的演讲中于 ZeroNights 2012 大会上展示。 更多信息请参阅幻灯片和视频:https://raw.githubusercontent.com/Cr4sh/blog/master/windows-registry-rootkit/Applied-anti-forensics.pdf