

ship-safe v9.7.5
面向 AI 编写软件的独立安全代理。发现问题,调查其是否真实存在,并向你展示证据。确定性核心,无需 API 密钥,支持 JSON 和 SARIF 输出。
面向 AI 编写软件的独立安全代理。它发现问题、调查问题是否真实存在,并向你展示证据。
网站 · 文档 · 安全与数据流 · 基准测试 · 定价 · 博客 · 参与贡献


Ship Safe CLI
Ship Safe 在你的仓库中本地运行,分为两层工作。
确定性引擎会在应用代码、AI 代理、MCP 配置、提示词、依赖项、CI/CD、密钥以及云相关配置中发现问题。快速、可重复且经过基准测试——这是传感器层。
随后,调查层会判定这些发现的价值。它追踪到达 sink 的值,在项目中搜索规则声称缺失的控制措施,跨单个文件无法容纳的配置构建攻击链,并且——在你要求时——用泄露的密钥向其提供商进行探测。每个结论都附带得出该结论的检查过程及其读取的行:
CONFIRMED — traced end to end (10)

    NoSQL Injection via $where [high]
    app/data/allocations-dao.js:78  NOSQL_INJECTION_WHERE
    why: threshold is assigned from the HTTP request and reaches the sink without validation on that path.
    decided by: dataflow
      1. value reaches NOSQL_INJECTION_WHERE here  app/data/allocations-dao.js:78
      2. getByUserIdAndThreshold is called here with threshold  app/routes/allocations.js:23
      3. threshold is assigned here  app/routes/allocations.js:20
    fix: Replace $where with standard MongoDB operators ($eq, $gt, $regex, etc.)
来自 ship-safe investigate 针对 OWASP NodeGoat 的真实输出。被污染的值在路由文件中被解构,并传入三个目录之外的 DAO。
从一条命令开始:
npx ship-safe
无需注册。扫描无需 API 密钥。核心检查可离线运行。AI 支持的 red-team 模式在可用时会使用你配置的提供商。
使用 --no-ai 可确保完全本地扫描。由提供商支持的分类、深度分析和 GPT-Red 会在尽力进行凭据掩码后,将有限上下文直接发送到你选择的提供商。有关确切边界和上下文限制,请参阅 Security & Data Flow。
快速开始
需要 22.x 系列上的 Node.js 22.13+,或 Node.js 24+。当前开发版本不再支持 Node 18 和 20。
# Interactive REPL: scan, fix, and ask questions in one session
npx ship-safe

# Full audit: secrets + 31 agents + deps + remediation plan
npx ship-safe audit .

# Investigate: confirmed / likely / unresolved / refuted, with the evidence
npx ship-safe investigate .
npx ship-safe investigate . --all       # also detail unresolved and refuted
npx ship-safe investigate . --verify    # probe leaked keys against their providers

# Before you open an unfamiliar folder with an agent: what runs on open?
npx ship-safe trust ~/Downloads/take-home
npx ship-safe trust . --json

# What can an AI agent working in this repo actually reach?
npx ship-safe capabilities .

# AI agent red-team scenarios for agent-readable content
npx ship-safe red-team . --gpt-red

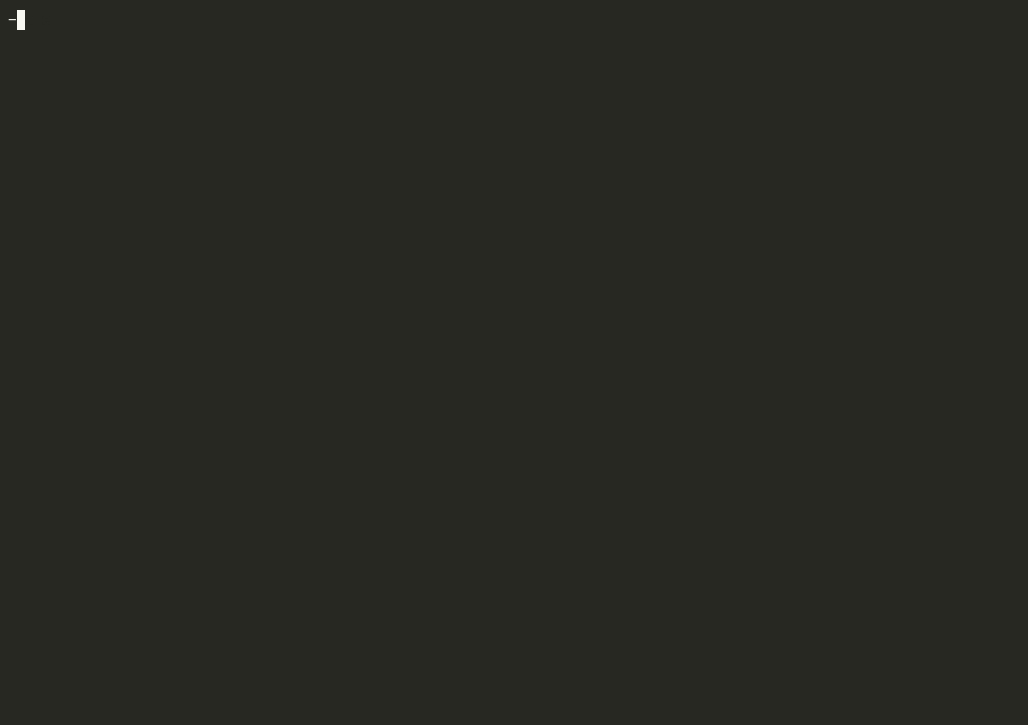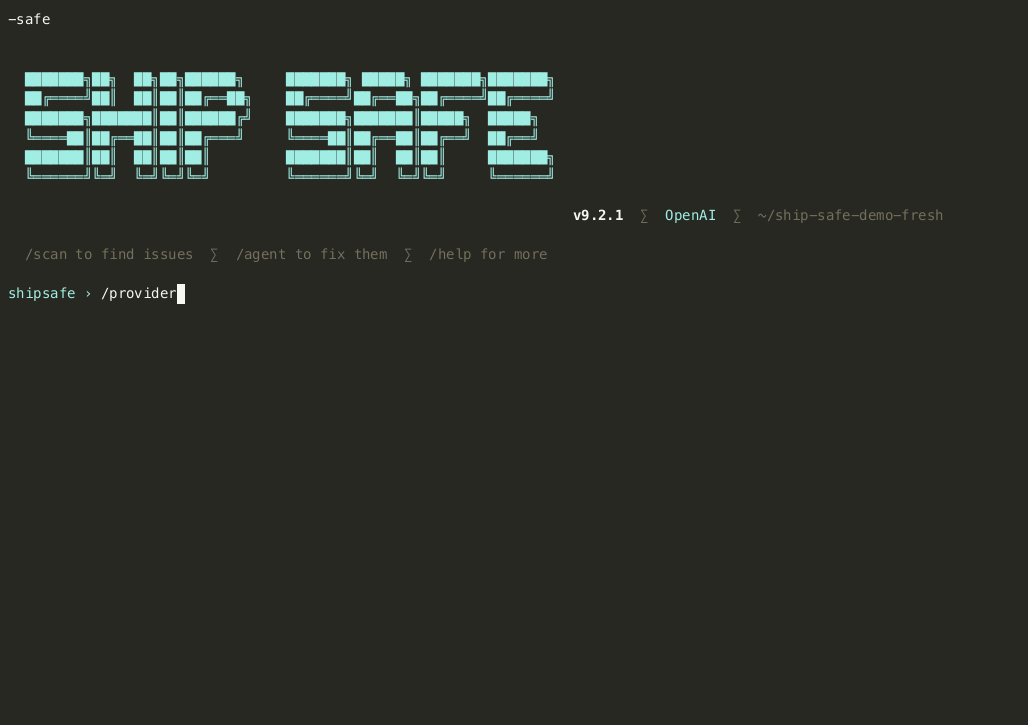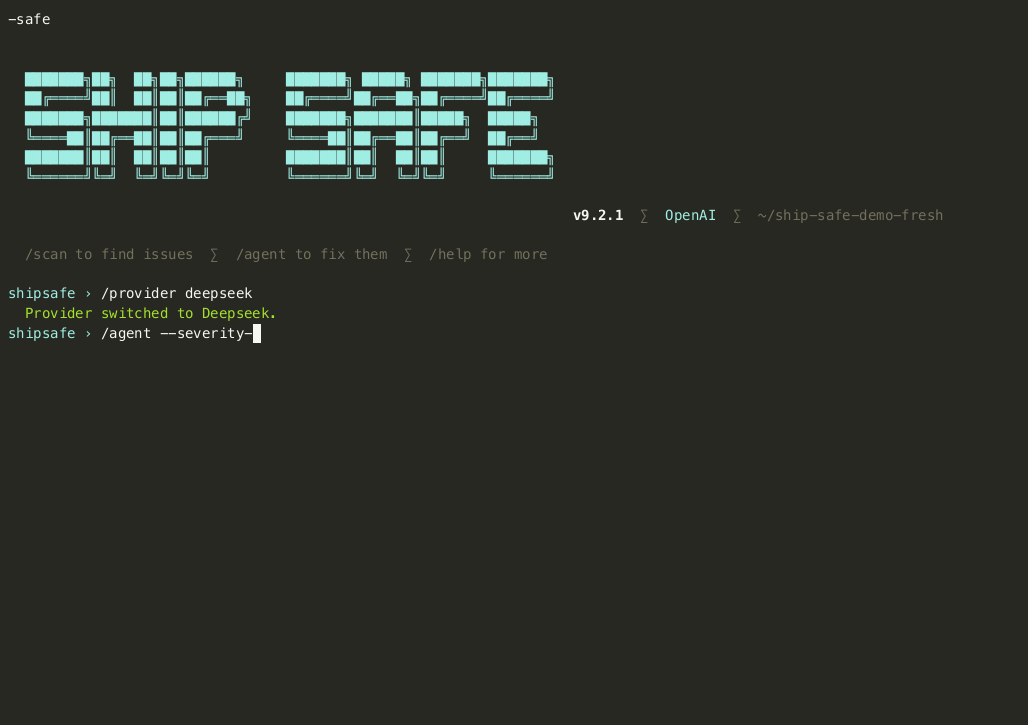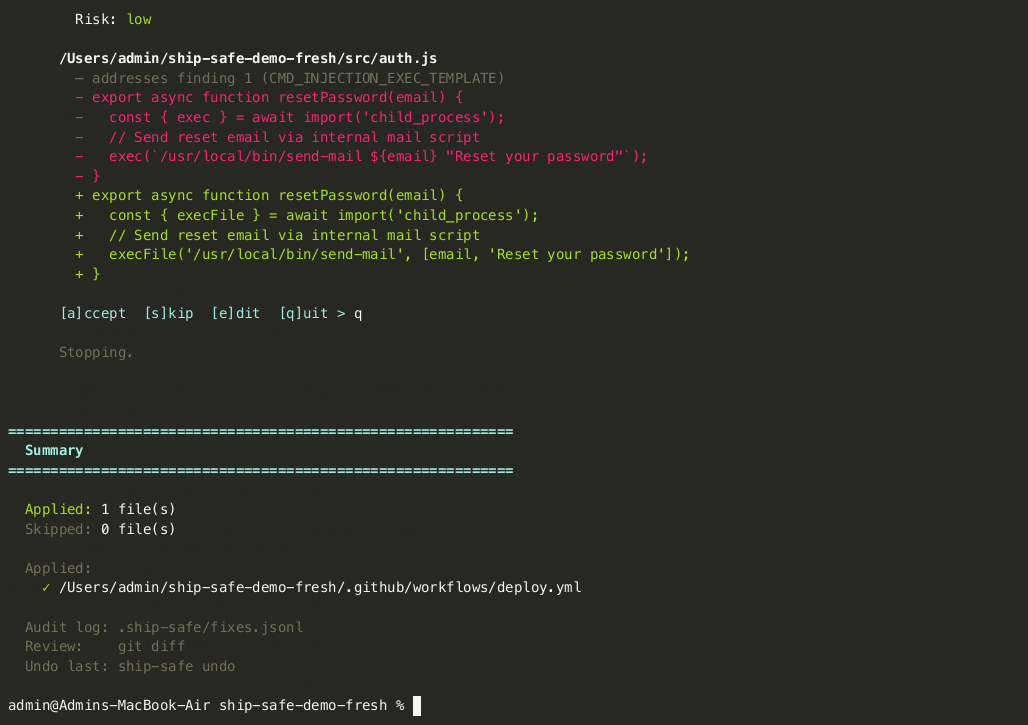
# Interactive fix agent: plan, diff, approve, inspect the static rescan
npx ship-safe agent .
npx ship-safe agent . --severity critical   # critical findings only
npx ship-safe agent . --branch --pr         # fix on a branch + open a PR

# Undo the last fix
npx ship-safe undo

# CI/CD mode — fails on any critical finding
npx ship-safe ci . --sarif results.sarif
npx ship-safe ci . --fail-on high              # stricter: critical or high

# Gate on evidence instead of severity: block only what was established
npx ship-safe ci . --fail-on-verdict confirmed
npx ship-safe ci . --ignore-refuted            # do not block on what was argued away
对于拉取请求,将可信基线扫描与头部扫描进行对比,以便现有仓库债务保持可见,同时不会阻塞无关变更:
# On the trusted base revision
npx ship-safe ci . --fail-on none --no-deps \
  --write-baseline-report /tmp/ship-safe-base.json

# On the pull request head
npx ship-safe ci . --base-report /tmp/ship-safe-base.json --fail-on high
基础产物包含哈希化后的发现标识、相对路径和规则元数据。它不存储原始匹配到的密钥。PR 结果将发现分类为已引入、已解决、未变更或不确定;模糊匹配会被显示,但不会阻止拉取请求。
机器可读报告契约
scan --json、audit --json 和 ci --json 包含 schemaVersion: 1、Ship Safe 版本以及 UTC generatedAt 时间戳。发现路径默认相对于项目,因此报告可以在工作站和 CI 之间移动,而不会泄露本地目录名称。仅当消费者明确需要主机路径时才使用 --absolute-paths。SARIF 报告在其工具元数据中携带相同的包版本。
Ship Safe 能发现什么
| 领域 | 示例 |
|---|---|
| AI 与 LLM 安全 | 提示注入、智能体劫持、过度代理、内存投毒、RAG 投毒、不安全的工具调用 |
| MCP 与智能体配置 | 过宽的工具权限、被投毒的注册表、不受信任的传输、危险的允许列表 |
| 应用安全 | SQL/NoSQL 注入、XSS、SSRF、认证绕过、路径遍历、不安全的 API 路由 |
| 密钥与合规 | API 密钥、令牌、凭据、PII、git 历史中泄露的密钥 |
| 供应链 | 域名抢注、依赖混淆、有风险的安装脚本、未固定版本的 AI 操作 |
| CI/CD | 流水线投毒、未固定版本的 GitHub Actions、密钥日志记录、不安全的工作流触发器 |
工作原理
- 本地扫描 - Ship Safe 使用针对性智能体检查你的仓库,并跳过不适用的检查。
- 调查每个发现 - 独立的检查轮次决定它是否真实,并按优先级排序,使成本较低的轮次永远不会推翻成本较高的轮次:追踪到的数据路径优先于模型对同一文件的解读,而经过认证的探测优先于两者。
- 阅读证据 - 发现会归结为已确认、可能、未解决或已反驳,每一项都会引用得出结论所依据的行,因此你可以对某个步骤提出异议,而不是对严重性标签提出异议。
- 可控地修复 - 智能体提出计划和差异,在写入前询问,报告静态重新扫描证据,并保持更改可逆。检测器消失并非独立的重新测试;参见修复结果。
- 在 CI 中设卡 - 使用
ship-safe ci使有风险的构建失败,并将 SARIF 上传到 GitHub 代码扫描。
“为什么不直接让我的编码智能体审查仓库?”
你可以这样做,而且应该这样做。它会发现真实的问题。但关于它自身的工作,有三个问题它在结构上无法回答。
编写这段代码的智能体是不是在给自己的作业打分? 问作者作者是否犯了错误,这不是审查。Ship Safe 是一个独立的审查者,采用独立的方法,并且它会公开地自我矛盾——数据流追踪会推翻启发式检查轮次,而实时探测会推翻两者。
它能看见自己能触及的范围吗? 审查你仓库的编码智能体无法读取你的 MCP 服务器配置,无法枚举它启动时被授予的权限,而且它正是其触及范围受到质疑的行为者。ship-safe capabilities 从外部读取所有这些信息,并报告那些单独看平平无奇、组合起来却危险的组合:
  CRITICAL  Repository-controlled instructions reach an unattended write capability
    1. CLAUDE.md is read as instructions and can be changed by anyone who lands a commit
       CLAUDE.md:1
    2. Claude Code runs without per-action approval
       .claude/settings.json:2
    3. shell execute granted: Bash(git push:*)
       .claude/settings.json:3
    4. filesystem write granted: Write
       .claude/settings.json:3
    5. mcp-tool write granted: mcp__github__create_pull_request
       .claude/settings.json:3
    Impact: Text committed to this repository can direct the agent to write files
            or run commands with no human in the loop.
    Boundary: Require approval for write and execute tools during sessions on
              untrusted branches, or remove the pre-granted entries.
其中每一行单独来看都平平无奇。但合在一起,它们构成了一条从拉取请求到特权写入的路径,而任何单文件审查都无法发现它,因为没有任何单个文件包含这条路径。
它是否一致,你能否证明它变得更好了? 问两次,得到两个答案。Ship Safe 的引擎是确定性的,其结论在 CI 中由一项基准测试把关,该基准测试评分的是结论质量,而非模式覆盖率:它能确定多少已知真实发现、能驳斥多少已知噪声,以及它是否会驳斥真实发现。最后一项的预算为零——它是唯一会静默丢失漏洞的错误类别。参见 benchmarks/。
开发者为何使用它
- 为 AI 原生应用而构建:捕获智能体、MCP 服务器、提示词、RAG 流程、托管智能体配置和 AI 驱动的 CI 中的风险。
- 与 AI 客户端配合使用:通过本地 stdio 服务器将 Ship Safe 暴露给 Codex、Claude Desktop、Cursor、Windsurf 及其他 MCP 客户端。
- 快速的本地反馈:在 PR 之前、审查期间或 CI 内部运行它,无需将代码发送到托管扫描器。
- 修复可审查:每个建议的更改在触及你的文件之前都会以 diff 形式展示。
- 适配你的技术栈:JavaScript、TypeScript、Python、配置文件、基础设施文件、GitHub Actions 等。
- 开源核心:MIT 许可的 CLI,附带文档、示例和不断发展的智能体系统。