<p align="center">
<img src="https://assets.kitploit.com/production/public/readmes/49363/b1f8834990a38d393bed6703c926c2f633c9d6afc19261eb02c67e9d45b7f350.png" alt="Ship Safe 标志" width="180" />
</p>
<p align="center"><strong>面向 AI 编写软件的独立安全代理。它发现问题、调查问题是否真实存在,并向你展示证据。</strong></p>
<p align="center"><a href="https://shipsafe.sh">网站</a> · <a href="https://shipsafe.sh/docs">文档</a> · <a href="https://shipsafe.sh/security">安全与数据流</a> · <a href="https://shipsafe.sh/benchmarks">基准测试</a> · <a href="https://shipsafe.sh/pricing">定价</a> · <a href="https://shipsafe.sh/blog">博客</a> · <a href="https://github.com/asamassekou10/ship-safe/contribute">参与贡献</a></p>
<p align="center">
<a href="https://www.npmjs.com/package/ship-safe"><img src="https://badge.fury.io/js/ship-safe.svg" alt="npm version" /></a>
<a href="https://www.npmjs.com/package/ship-safe"><img src="https://img.shields.io/npm/dm/ship-safe.svg" alt="npm downloads" /></a>
<a href="https://github.com/asamassekou10/ship-safe/actions/workflows/ci.yml"><img src="https://github.com/asamassekou10/ship-safe/actions/workflows/ci.yml/badge.svg" alt="CI" /></a>
<a href="https://opensource.org/licenses/MIT"><img src="https://img.shields.io/badge/License-MIT-yellow.svg" alt="License: MIT" /></a>
<a href="https://github.com/asamassekou10/ship-safe/stargazers"><img src="https://img.shields.io/github/stars/asamassekou10/ship-safe?style=social" alt="GitHub stars" /></a>
<a href="https://github.com/sponsors/asamassekou10"><img src="https://img.shields.io/badge/Sponsor-%E2%9D%A4-ea4aaa?logo=github" alt="Sponsor" /></a>
</p>
## Ship Safe CLI
Ship Safe 在你的仓库中本地运行,分为两层工作。
**确定性引擎**会在应用代码、AI 代理、MCP 配置、提示词、依赖项、CI/CD、密钥以及云相关配置中发现问题。快速、可重复且经过基准测试——这是传感器层。
随后,**调查层**会判定这些发现的价值。它追踪到达 sink 的值,在项目中搜索规则声称缺失的控制措施,跨单个文件无法容纳的配置构建攻击链,并且——在你要求时——用泄露的密钥向其提供商进行探测。每个结论都附带得出该结论的检查过程及其读取的行:
```
CONFIRMED — traced end to end (10)
NoSQL Injection via $where [high]
app/data/allocations-dao.js:78 NOSQL_INJECTION_WHERE
why: threshold is assigned from the HTTP request and reaches the sink without validation on that path.
decided by: dataflow
1. value reaches NOSQL_INJECTION_WHERE here app/data/allocations-dao.js:78
2. getByUserIdAndThreshold is called here with threshold app/routes/allocations.js:23
3. threshold is assigned here app/routes/allocations.js:20
fix: Replace $where with standard MongoDB operators ($eq, $gt, $regex, etc.)
```
<sub>来自 <code>ship-safe investigate</code> 针对 OWASP NodeGoat 的真实输出。被污染的值在路由文件中被解构,并传入三个目录之外的 DAO。</sub>
从一条命令开始:
```bash
npx ship-safe
```
无需注册。扫描无需 API 密钥。核心检查可离线运行。AI 支持的 red-team 模式在可用时会使用你配置的提供商。
使用 `--no-ai` 可确保完全本地扫描。由提供商支持的分类、深度分析和 GPT-Red 会在尽力进行凭据掩码后,将有限上下文直接发送到你选择的提供商。有关确切边界和上下文限制,请参阅 [Security & Data Flow](https://shipsafe.sh/security)。
<p align="center">
<img src="https://assets.kitploit.com/production/public/readmes/49363/75988a5baca705edcd06c5d39049d35be36f660fad2362de6700cf40eb72d2dd.gif" alt="Ship Safe REPL 演示" width="800" />
</p>
---
## 快速开始
需要 22.x 系列上的 Node.js 22.13+,或 Node.js 24+。当前开发版本不再支持 Node 18 和 20。
```bash
# Interactive REPL: scan, fix, and ask questions in one session
npx ship-safe
# Full audit: secrets + 31 agents + deps + remediation plan
npx ship-safe audit .
# Investigate: confirmed / likely / unresolved / refuted, with the evidence
npx ship-safe investigate .
npx ship-safe investigate . --all # also detail unresolved and refuted
npx ship-safe investigate . --verify # probe leaked keys against their providers
# Before you open an unfamiliar folder with an agent: what runs on open?
npx ship-safe trust ~/Downloads/take-home
npx ship-safe trust . --json
# What can an AI agent working in this repo actually reach?
npx ship-safe capabilities .
# AI agent red-team scenarios for agent-readable content
npx ship-safe red-team . --gpt-red
# Interactive fix agent: plan, diff, approve, inspect the static rescan
npx ship-safe agent .
npx ship-safe agent . --severity critical # critical findings only
npx ship-safe agent . --branch --pr # fix on a branch + open a PR
# Undo the last fix
npx ship-safe undo
# CI/CD mode — fails on any critical finding
npx ship-safe ci . --sarif results.sarif
npx ship-safe ci . --fail-on high # stricter: critical or high
# Gate on evidence instead of severity: block only what was established
npx ship-safe ci . --fail-on-verdict confirmed
npx ship-safe ci . --ignore-refuted # do not block on what was argued away
```
对于拉取请求,将可信基线扫描与头部扫描进行对比,以便现有仓库债务保持可见,同时不会阻塞无关变更:
```bash
# On the trusted base revision
npx ship-safe ci . --fail-on none --no-deps \
--write-baseline-report /tmp/ship-safe-base.json
# On the pull request head
npx ship-safe ci . --base-report /tmp/ship-safe-base.json --fail-on high
```
基础产物包含哈希化后的发现标识、相对路径和规则元数据。它不存储原始匹配到的密钥。PR 结果将发现分类为已引入、已解决、未变更或不确定;模糊匹配会被显示,但不会阻止拉取请求。
### 机器可读报告契约
`scan --json`、`audit --json` 和 `ci --json` 包含 `schemaVersion: 1`、Ship Safe 版本以及 UTC `generatedAt` 时间戳。发现路径默认相对于项目,因此报告可以在工作站和 CI 之间移动,而不会泄露本地目录名称。仅当消费者明确需要主机路径时才使用 `--absolute-paths`。SARIF 报告在其工具元数据中携带相同的包版本。
## Ship Safe 能发现什么
| 领域 | 示例 |
|------|----------|
| AI 与 LLM 安全 | 提示注入、智能体劫持、过度代理、内存投毒、RAG 投毒、不安全的工具调用 |
| MCP 与智能体配置 | 过宽的工具权限、被投毒的注册表、不受信任的传输、危险的允许列表 |
| 应用安全 | SQL/NoSQL 注入、XSS、SSRF、认证绕过、路径遍历、不安全的 API 路由 |
| 密钥与合规 | API 密钥、令牌、凭据、PII、git 历史中泄露的密钥 |
| 供应链 | 域名抢注、依赖混淆、有风险的安装脚本、未固定版本的 AI 操作 |
| CI/CD | 流水线投毒、未固定版本的 GitHub Actions、密钥日志记录、不安全的工作流触发器 |
## 工作原理
1. **本地扫描** - Ship Safe 使用针对性智能体检查你的仓库,并跳过不适用的检查。
2. **调查每个发现** - 独立的检查轮次决定它是否真实,并按优先级排序,使成本较低的轮次永远不会推翻成本较高的轮次:追踪到的数据路径优先于模型对同一文件的解读,而经过认证的探测优先于两者。
3. **阅读证据** - 发现会归结为已确认、可能、未解决或已反驳,每一项都会引用得出结论所依据的行,因此你可以对某个步骤提出异议,而不是对严重性标签提出异议。
4. **可控地修复** - 智能体提出计划和差异,在写入前询问,报告静态重新扫描证据,并保持更改可逆。检测器消失并非独立的重新测试;参见[修复结果](https://github.com/asamassekou10/ship-safe/blob/main/docs/fix-verification.md)。
5. **在 CI 中设卡** - 使用 `ship-safe ci` 使有风险的构建失败,并将 SARIF 上传到 GitHub 代码扫描。
<p align="center">
<img src="https://assets.kitploit.com/production/public/readmes/49363/31125a0161ee16c772304e3097cdea464c8988cdc8e818ebf8356506fa1f1314.gif" alt="Ship Safe 智能体演示" width="800" />
</p>
---
## “为什么不直接让我的编码智能体审查仓库?”
你可以这样做,而且应该这样做。它会发现真实的问题。但关于它自身的工作,有三个问题它在结构上无法回答。
**编写这段代码的智能体是不是在给自己的作业打分?** 问作者作者是否犯了错误,这不是审查。Ship Safe 是一个独立的审查者,采用独立的方法,并且它会公开地自我矛盾——数据流追踪会推翻启发式检查轮次,而实时探测会推翻两者。
**它能看见自己能触及的范围吗?** 审查你仓库的编码智能体无法读取你的 MCP 服务器配置,无法枚举它启动时被授予的权限,而且它正是其触及范围受到质疑的行为者。`ship-safe capabilities` 从外部读取所有这些信息,并报告那些单独看平平无奇、组合起来却危险的组合:
```
CRITICAL Repository-controlled instructions reach an unattended write capability
1. CLAUDE.md is read as instructions and can be changed by anyone who lands a commit
CLAUDE.md:1
2. Claude Code runs without per-action approval
.claude/settings.json:2
3. shell execute granted: Bash(git push:*)
.claude/settings.json:3
4. filesystem write granted: Write
.claude/settings.json:3
5. mcp-tool write granted: mcp__github__create_pull_request
.claude/settings.json:3
Impact: Text committed to this repository can direct the agent to write files
or run commands with no human in the loop.
Boundary: Require approval for write and execute tools during sessions on
untrusted branches, or remove the pre-granted entries.
```
其中每一行单独来看都平平无奇。但合在一起,它们构成了一条从拉取请求到特权写入的路径,而任何单文件审查都无法发现它,因为没有任何单个文件包含这条路径。
**它是否一致,你能否证明它变得更好了?** 问两次,得到两个答案。Ship Safe 的引擎是确定性的,其结论在 CI 中由一项基准测试把关,该基准测试评分的是*结论质量*,而非模式覆盖率:它能确定多少已知真实发现、能驳斥多少已知噪声,以及它是否会驳斥真实发现。最后一项的预算为零——它是唯一会静默丢失漏洞的错误类别。参见 [benchmarks/](https://github.com/asamassekou10/ship-safe/blob/main/benchmarks)。
## 开发者为何使用它
- **为 AI 原生应用而构建**:捕获智能体、MCP 服务器、提示词、RAG 流程、托管智能体配置和 AI 驱动的 CI 中的风险。
- **与 AI 客户端配合使用**:通过本地 stdio 服务器将 Ship Safe 暴露给 Codex、Claude Desktop、Cursor、Windsurf 及其他 MCP 客户端。
- **快速的本地反馈**:在 PR 之前、审查期间或 CI 内部运行它,无需将代码发送到托管扫描器。
- **修复可审查**:每个建议的更改在触及你的文件之前都会以 diff 形式展示。
- **适配你的技术栈**:JavaScript、TypeScript、Python、配置文件、基础设施文件、GitHub Actions 等。
- **开源核心**:MIT 许可的 CLI,附带文档、示例和不断发展的智能体系统。
## 免费 CLI,付费团队工作流
开源 CLI 是在本地扫描任何仓库的最快方式。当你需要围绕同一扫描器的托管工作流时,再升级:
| 需求 | 使用 |
|------|-----|
| 本地扫描、审计和智能体辅助修复 | 免费 CLI |
| 扫描历史、云仪表板和 PDF 报告 | Pro |
| 共享工作区、PR Guardian、团队报告和协作 | Team |
在 [shipsafe.sh/pricing](https://shipsafe.sh/pricing) 比较各方案。
Ship Safe Cloud 是用于扫描历史、PR Guardian、计费和团队工作流的托管仪表板,由于包含商业产品代码和托管基础设施工作流,它在私有仓库中开发。公开的 `ship-safe` 仓库仍专注于 MIT 许可的 CLI、安全智能体、规则、测试夹具、CI 集成和文档。有关仓库边界,参见 [Ship Safe Cloud](https://github.com/asamassekou10/ship-safe/blob/main/docs/cloud.md)。
---
## 安全智能体
所有智能体并行运行。每个智能体都会自动跳过不相关的项目。
| Agent | 类别 | 检测内容 |
|-------|----------|-----------------|
| **InjectionTester** | 代码漏洞 | SQL/NoSQL 注入、命令注入、XSS、路径遍历、XXE、ReDoS、原型污染 |
| **AuthBypassAgent** | 认证 | JWT 缺陷(alg:none、弱密钥)、CSRF、OAuth 配置错误、BOLA/IDOR、TLS 绕过 |
| **SSRFProber** | SSRF | fetch/axios 中的用户输入、云元数据端点、内部 IP |
| **SupplyChainAudit** | 供应链 | 域名抢注(typosquatting)、通配符版本、可疑安装脚本、依赖混淆 |
| **ConfigAuditor** | 配置 | Docker(root 用户、:latest)、Terraform、Kubernetes、CORS、CSP、Firebase、Nginx |
| **SupabaseRLSAgent** | 认证 | 客户端代码中的 service_role 密钥、未启用 RLS 的表、anon 密钥插入 |
| **LLMRedTeam** | AI/LLM | OWASP LLM Top 10:提示注入、过度代理权限、系统提示泄露 |
| **MCPSecurityAgent** | AI/LLM | MCP 服务器滥用、工具投毒、域名抢注、未验证输入 |
| **A2ASecurityAgent** | AI/LLM | A2A agent card 投毒、缺少认证、明文端点、不安全的推送回调、未固定版本的远程卡片([覆盖范围](https://github.com/asamassekou10/ship-safe/blob/main/docs/a2a-security.md)) |
| **AgenticSecurityAgent** | AI/LLM | OWASP Agentic AI Top 10:agent 劫持、权限提升、Kimi K3/OpenAI 兼容工具调用滥用 |
| **RAGSecurityAgent** | AI/LLM | 上下文注入、文档投毒、向量数据库访问控制 |
| **MemoryPoisoningAgent** | AI/LLM | agent 记忆文件中的指令注入、隐藏的 Unicode 载荷(ASI-01、ASI-05) |
| **PIIComplianceAgent** | 合规 | 源代码中的 SSN、信用卡号、电子邮件、电话号码 |
| **VibeCodingAgent** | 代码漏洞 | AI 生成代码的反模式:无验证、空 catch、TODO 认证 |
| **ExceptionHandlerAgent** | 代码漏洞 | 空 catch、未处理的 rejection、泄露的堆栈跟踪(OWASP A10:2025) |
| **AgentConfigScanner** | AI/LLM | .cursorrules、CLAUDE.md 中的提示注入、恶意 Claude Code hooks |
| **MobileScanner** | 移动端 | OWASP Mobile Top 10 2024:不安全存储、WebView 注入、调试模式 |
| **GitHistoryScanner** | 密钥 | git 提交历史中泄露的密钥 |
| **CICDScanner** | CI/CD | 流水线投毒、未固定版本的 action、密钥日志记录(OWASP CI/CD Top 10) |
| **APIFuzzer** | API | 无认证路由、批量赋值、GraphQL 内省、调试端点 |
| **ManagedAgentScanner** | AI/LLM | Claude Managed Agent 配置错误:always_allow 策略、无限制网络访问(ASI-03–ASI-07) |
| **HermesSecurityAgent** | AI/LLM | 工具注册表投毒、函数调用注入、技能权限漂移(ASI-01–ASI-10) |
| **AgentAttestationAgent** | 供应链 | 未固定版本的 agent、缺少完整性哈希、未签名清单(ASI-10、SLSA L0) |
| **AgenticSupplyChainAgent** | 供应链 | 权限过高的 AI CI action、OAuth 权限蔓延、未签名的 AI webhook 接收器(ASI-02、ASI-06) |
| **RobloxSecurityAgent** | 供应链 | 恶意 Roblox/Luau Toolbox 资源(运行时资源注入、`rbxassetid://` 加载器、`HttpEnabled`、隐藏在实例属性中的载荷) |
| **ModelScanAgent** | 供应链 | ML 模型权重中的代码执行载荷(`.pt`/`.pkl`/`.ckpt` 中的 pickle 操作码)、未使用 `weights_only` 的 `torch.load`、规避扫描器的归档文件(CWE-502、CWE-506) |
| **TrustBoundaryAgent** | Agentic | GhostApproval 符号链接攻击(以配置命名的链接指向 `~/.ssh`/`~/.aws`/`.env`)、逃逸出目录树的仓库符号链接、agent 可读文档中的 Friendly Fire 审查时运行指令(CWE-59、CWE-61) |
| **SlopSquatAgent** | 供应链 | 幻觉/幽灵包导入(slopsquatting)——未声明、未安装或非内置的裸导入,以及已知的 AI 幻觉名称(CWE-1357) |
| **ClickFixAgent** | 供应链 | ClickFix / 伪造 CAPTCHA 粘贴即运行诱饵(伪造错误 + Win+R/Ctrl+V/命令栏按键、PowerShell cradle)以及伪造安装程序的 npm 生命周期脚本(CWE-1357、CWE-506) |
| **InstallGuardAgent** | 供应链 | 生命周期脚本中的 npm 蠕虫行为(凭据窃取、环境变量外泄、破坏性 `rm -rf`、混淆的 `node -e`)以及被武器化的 `binding.gyp` node-gyp 操作(CWE-506、CWE-829) |
**调查流程**,按各自证据的优先级从高到低排列:
| 流程 | 等级 | 它确立的内容 |
|------|------|---------------------|
| **VerifierAgent** | 启发式 | 对发现项周围进行模式检查。从不多于“可能”的表述 |
| **DeepAnalyzer** | 分析 | 对发现项及其文件进行 LLM 污点读取,并验证引用 |
| **DataflowInvestigator** | 数据流 | 将值追溯回其来源,跨越一个函数边界并进入其他文件。支持 JavaScript、TypeScript 和 Python |
| **AbsenceInvestigator** | 存在性 | 在项目或处理程序中搜索规则声称缺失的控制措施 |
| **LiteralContextInvestigator** | 存在性 | 根据写入值周围的内容——散文、帮助字符串或保留地址——来判定关于该值的发现项 |
| **CapabilityGraph** | 链 | 从任何单个文件都不包含的配置中构建攻击链 |
| **RedosReproducer** | 复现 | 在带有截止时间的工作进程中,针对生成的输入运行被标记的模式 |
| **SecretsVerifier** | 复现 | 将泄露的密钥呈现给其提供商。需主动选择启用:此操作会披露该密钥 |
如果某项主张所引用的文件或行无法解析,该主张会被记录,但绝不会决定裁决。两个等级相同但意见不一致的流程会解析为未解决,而不是解析为更令人担忧的那个裁决。
**另外:** ScoringEngine
---
## REPL
```
$ ship-safe
███████╗██╗ ██╗██╗██████╗ ███████╗ █████╗ ███████╗███████╗
...
v9.4.1 · DeepSeek · ~/my-project
/scan to find issues · /agent to fix them · /help for more
shipsafe ›
```
| 命令 | 作用 |
|---------|-------------|
| `/scan` | 重新扫描项目 |
| `/agent` | 运行交互式修复循环 |
| `/findings` | 列出上次扫描的发现项 |
| `/show <n>` | 查看发现项 n 的完整详情 |
| `/plan <n>` | 预览发现项 n 的修复计划(不写入) |
| `/undo [--all]` | 撤销上次修复(或所有修复) |
| `/share` | 将扫描报告发布为公开 URL(7 天) |
| `/diff` | 显示 git 工作区差异 |
| `/provider <name>` | 在会话中切换 LLM 提供商 |
| `/quit` | 退出(也可用 `Ctrl-D` 或 `Ctrl-C`) |
任何不以 `/` 开头的内容都会作为自由形式的问题发送给 LLM,并以你最新的扫描结果作为上下文。
---
## CI/CD
```yaml
# .github/workflows/security.yml
name: Security Audit
on: [push, pull_request]
jobs:
security:
runs-on: ubuntu-latest
steps:
- uses: actions/checkout@v4
- name: Security gate
run: npx ship-safe ci . --sarif results.sarif
- uses: github/codeql-action/upload-sarif@v3
if: always()
with:
sarif_file: results.sarif
```
GitLab CI 版本位于 [docs/examples/gitlab-security-workflow.yml](https://github.com/asamassekou10/ship-safe/blob/main/docs/examples/gitlab-security-workflow.yml)。
### 带内联 PR 发现的 GitHub Action
当你希望将严重和高危发现附加到更改的行时,可在 `pull_request` 工作流中使用该 Action。对于来自 fork 的贡献,请勿在此路径中使用 `pull_request_target`:Ship Safe 会拒绝这种特权组合,因为检出内容可能包含不受信任的代码。
```yaml
name: Ship Safe
on:
pull_request:
permissions:
contents: read
pull-requests: write
security-events: write
jobs:
scan:
runs-on: ubuntu-latest
steps:
- uses: actions/checkout@v4
- uses: asamassekou10/[email protected]
with:
fail-on: high
inline: true
```
内联评论为可选功能,仅发布严重/高危发现。重新运行该任务会更新摘要,而不会创建重复的内联评论。
---
## LLM 支持
可与任何提供商配合使用——从环境变量自动检测。使用 `--provider <name>` 进行覆盖。
Anthropic · OpenAI · Google · DeepSeek · Kimi K3 / Moonshot · Groq · Together · Mistral · xAI · Perplexity · Ollama · LM Studio · 任何兼容 OpenAI 的端点
Kimi 通过 `MOONSHOT_API_KEY` 或 `KIMI_API_KEY` 默认使用 `kimi-k3`。使用 `--provider kimi --model kimi-k3` 进行长上下文 GPT-Red 和深度分析运行。
针对 Kimi K3 特定的长上下文红队测试:
```bash
npx ship-safe red-team . --gpt-red --provider kimi --model kimi-k3 --k3-long-context
```
Ship Safe 还会检查 Kimi K3 / OpenAI 兼容的工具调用实现,针对以下问题:从提示上下文中动态加载工具、缺少工具允许列表、对不可信输入强制进行工具调用,以及在没有原始助手工具调用消息的情况下重放工具结果。
核心扫描不需要 API 密钥。AI 分类和 `red-team --gpt-red` 在可用时会使用你配置的提供程序,并为 GPT-Red 检查提供确定性的离线回退。
---
## 抑制误报
```python
password = get_password() # ship-safe-ignore
```
`critical` 级别的发现始终会被报告。内联注释无法隐藏其中任何一个,任何试图抑制它的尝试都会被记录在扫描结果中。该注释是供人工排除误报使用的,而任何能够写入你源代码一行的东西——包括 AI 代理——同样能够写入该注释,因此最高严重级别不会遵从它。每一次抑制都会被计数,因此一个压制了发现的扫描结果绝不会看起来像是一个没有任何发现的扫描结果。
普通代码规则不会将 Markdown 散文或围栏代码示例视为已部署的源代码进行评级。机密信息仍会在所有位置被扫描,而诸如 `AGENTS.md` 和 `CLAUDE.md` 这类代理可读文件会保留其专用的提示注入和信任边界检查。若要刻意审查围栏示例,请在 `scan`、`audit` 或 `ci` 中使用 `--include-doc-examples`。
```gitignore
# .ship-safeignore
tests/fixtures/
docs/
```
### 它的噪声有多大?
召回率只是扫描器的一半。一个把所有东西都标记出来的工具能捕获一切,却毫无用处,因此我们还会跟踪 Ship Safe 在无已知活跃漏洞的成熟项目上报告的内容。这些是原始发现,而非已确认的缺陷。
| 项目 | 原始发现 | 严重 | 评分 | 等级 |
|---|---:|---:|---:|:---:|
| [express](https://github.com/expressjs/express) | 10 | 0 | 88.2 | B |
| [requests](https://github.com/psf/requests) | 7 | 0 | 95.5 | A |
| [flask](https://github.com/pallets/flask) | 17 | 0 | 81.4 | B |
| [chalk](https://github.com/chalk/chalk) | 4 | 0 | 89.4 | B |
最初的四个项目合计有 38 条原始发现,相比 v9.6.3 之前的 1,031 条有所下降。当前包含五个项目的干净语料库还包括 Hermes Agent,它报告了 662 条发现,其中 66 条为严重级别。这两个数字都不是误报率,也不是对准确性的声明;自动化调查标签和剩余工作量记录在基准测试中。对 NodeGoat 和 DVWA 的检测下限检查仍然通过。
语料库按提交固定,可通过一条命令复现,限制条件已记录:
**[benchmarks/false-positives/](https://github.com/asamassekou10/ship-safe/blob/main/benchmarks/false-positives)**
### 它与 Semgrep、Gitleaks、Trivy、CodeQL 相比如何?
将 Ship Safe 与它们一起运行,而不是替代它们。CodeQL 执行 Ship Safe 并不尝试的过程间污点分析,Gitleaks 是密钥领域的专家,而 Trivy 背后有真实的 CVE 数据库。
Ship Safe 覆盖的是一个更窄的问题:AI 编码代理刚刚对你的仓库、你的 CI 以及你的本地工具配置做了什么。MCP 客户端配置、代理记忆投毒、幻觉包导入和 AIBOM 是我们在其他四个工具中未找到等效公开规则的领域。
完整覆盖矩阵,已对照它们的公开注册表验证,包括它们胜过我们的地方:**[docs/comparison.md](https://github.com/asamassekou10/ship-safe/blob/main/docs/comparison.md)**
---
## 添加徽章
```markdown
[](https://shipsafe.sh)
```
## 后续计划
**10.1 是一个精确性发布版本。** 它保留经过验证的 Hermes Agent 10.0 基线,并收紧证明机制,以免 Ship Safe 自身的公告引用被误认为未签名的 agent 资源。现有的插件和适配器检查是部分覆盖;终端态势、ACP/TUI、当前 cron 生命周期以及凭据可达性仍是明确待完成的工作,而非隐含的覆盖范围。参见[覆盖矩阵](https://github.com/asamassekou10/ship-safe/blob/main/docs/hermes-coverage-matrix.md)。
参见[路线图](https://github.com/asamassekou10/ship-safe/blob/main/ROADMAP.md)了解已计划的内容以及有意不做的内容。欢迎聚焦的贡献和基于基准测试的修复。
## 贡献
Ship Safe 是开源的,最好的贡献是那些让 AI 辅助开发更安全的小而聚焦的改进。
适合入门的领域:
- 为 AI、MCP、CI、云或供应链风险添加一个聚焦的安全 agent
- 为现有 agent 添加一条精确的安全规则
- 添加易受攻击的测试夹具和回归测试
- 为本地扫描、CI 门禁、红队工作流以及 MCP/agent 配置编写示例
从这里开始:
- [适合新手的问题](https://github.com/asamassekou10/ship-safe/contribute)
- [贡献者指南](https://github.com/asamassekou10/ship-safe/blob/main/CONTRIBUTING.md)
- [添加一个 agent](https://github.com/asamassekou10/ship-safe/blob/main/docs/adding-an-agent.md)
- [添加一条安全规则](https://github.com/asamassekou10/ship-safe/blob/main/docs/adding-a-security-rule.md)
- [编写自定义 agent 插件](https://github.com/asamassekou10/ship-safe/blob/main/docs/custom-agent-plugins.md)
- [安全地处理 MCP 环境变量](https://github.com/asamassekou10/ship-safe/blob/main/docs/mcp-env-safety.md)
- [在 Codex 中使用 Ship Safe](https://github.com/asamassekou10/ship-safe/blob/main/docs/integrations/codex.md)
- [在 Claude Code 中使用 Ship Safe](https://github.com/asamassekou10/ship-safe/blob/main/docs/integrations/claude-code.md)
- [在 Cursor 中使用 Ship Safe](https://github.com/asamassekou10/ship-safe/blob/main/docs/integrations/cursor.md)
- [了解修复结果与静态验证的局限](https://github.com/asamassekou10/ship-safe/blob/main/docs/fix-verification.md)
- [发布流程](https://github.com/asamassekou10/ship-safe/blob/main/docs/releasing.md)
---
## 赞助者
Ship Safe 采用 MIT 许可证,永久免费。
<p align="center">
<a href="https://github.com/sponsors/asamassekou10">
<img src="https://img.shields.io/badge/Sponsor%20Ship%20Safe-%E2%9D%A4-ea4aaa?style=for-the-badge&logo=github" alt="Sponsor Ship Safe" />
</a>
</p>
---
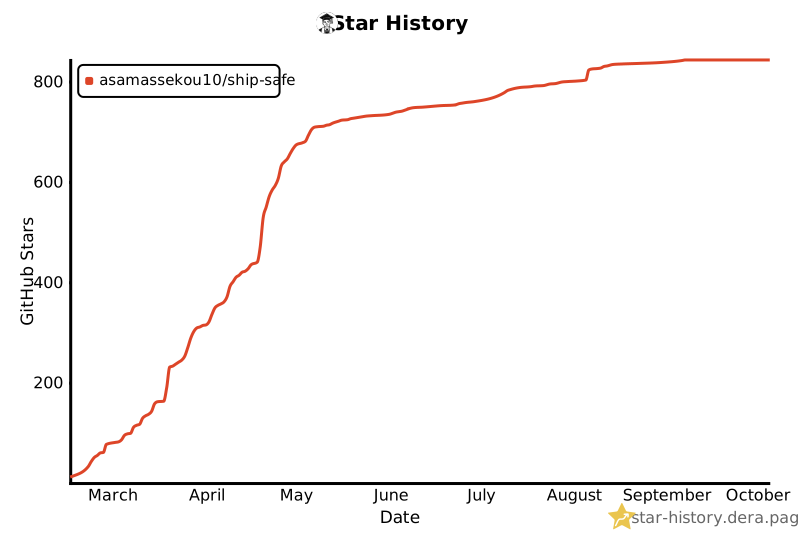
## Star 历史
[](https://star-history.dera.page/#asamassekou10/ship-safe&type=date)
---
**快速交付。安全交付。** — [shipsafe.sh](https://shipsafe.sh)


