
 #1
用于收集、分析和操作威胁源、危害指标(IOC)和攻击趋势的工具。
Kitploit 推荐

 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 0xmarcio/pocindex
Search public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 garrytan/gstack
使用 Garry Tan 的精确 Claude Code 设置:23 个有主见的工具,充当 CEO、设计师、工程经理、发布经理、文档工程师和 QA。
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
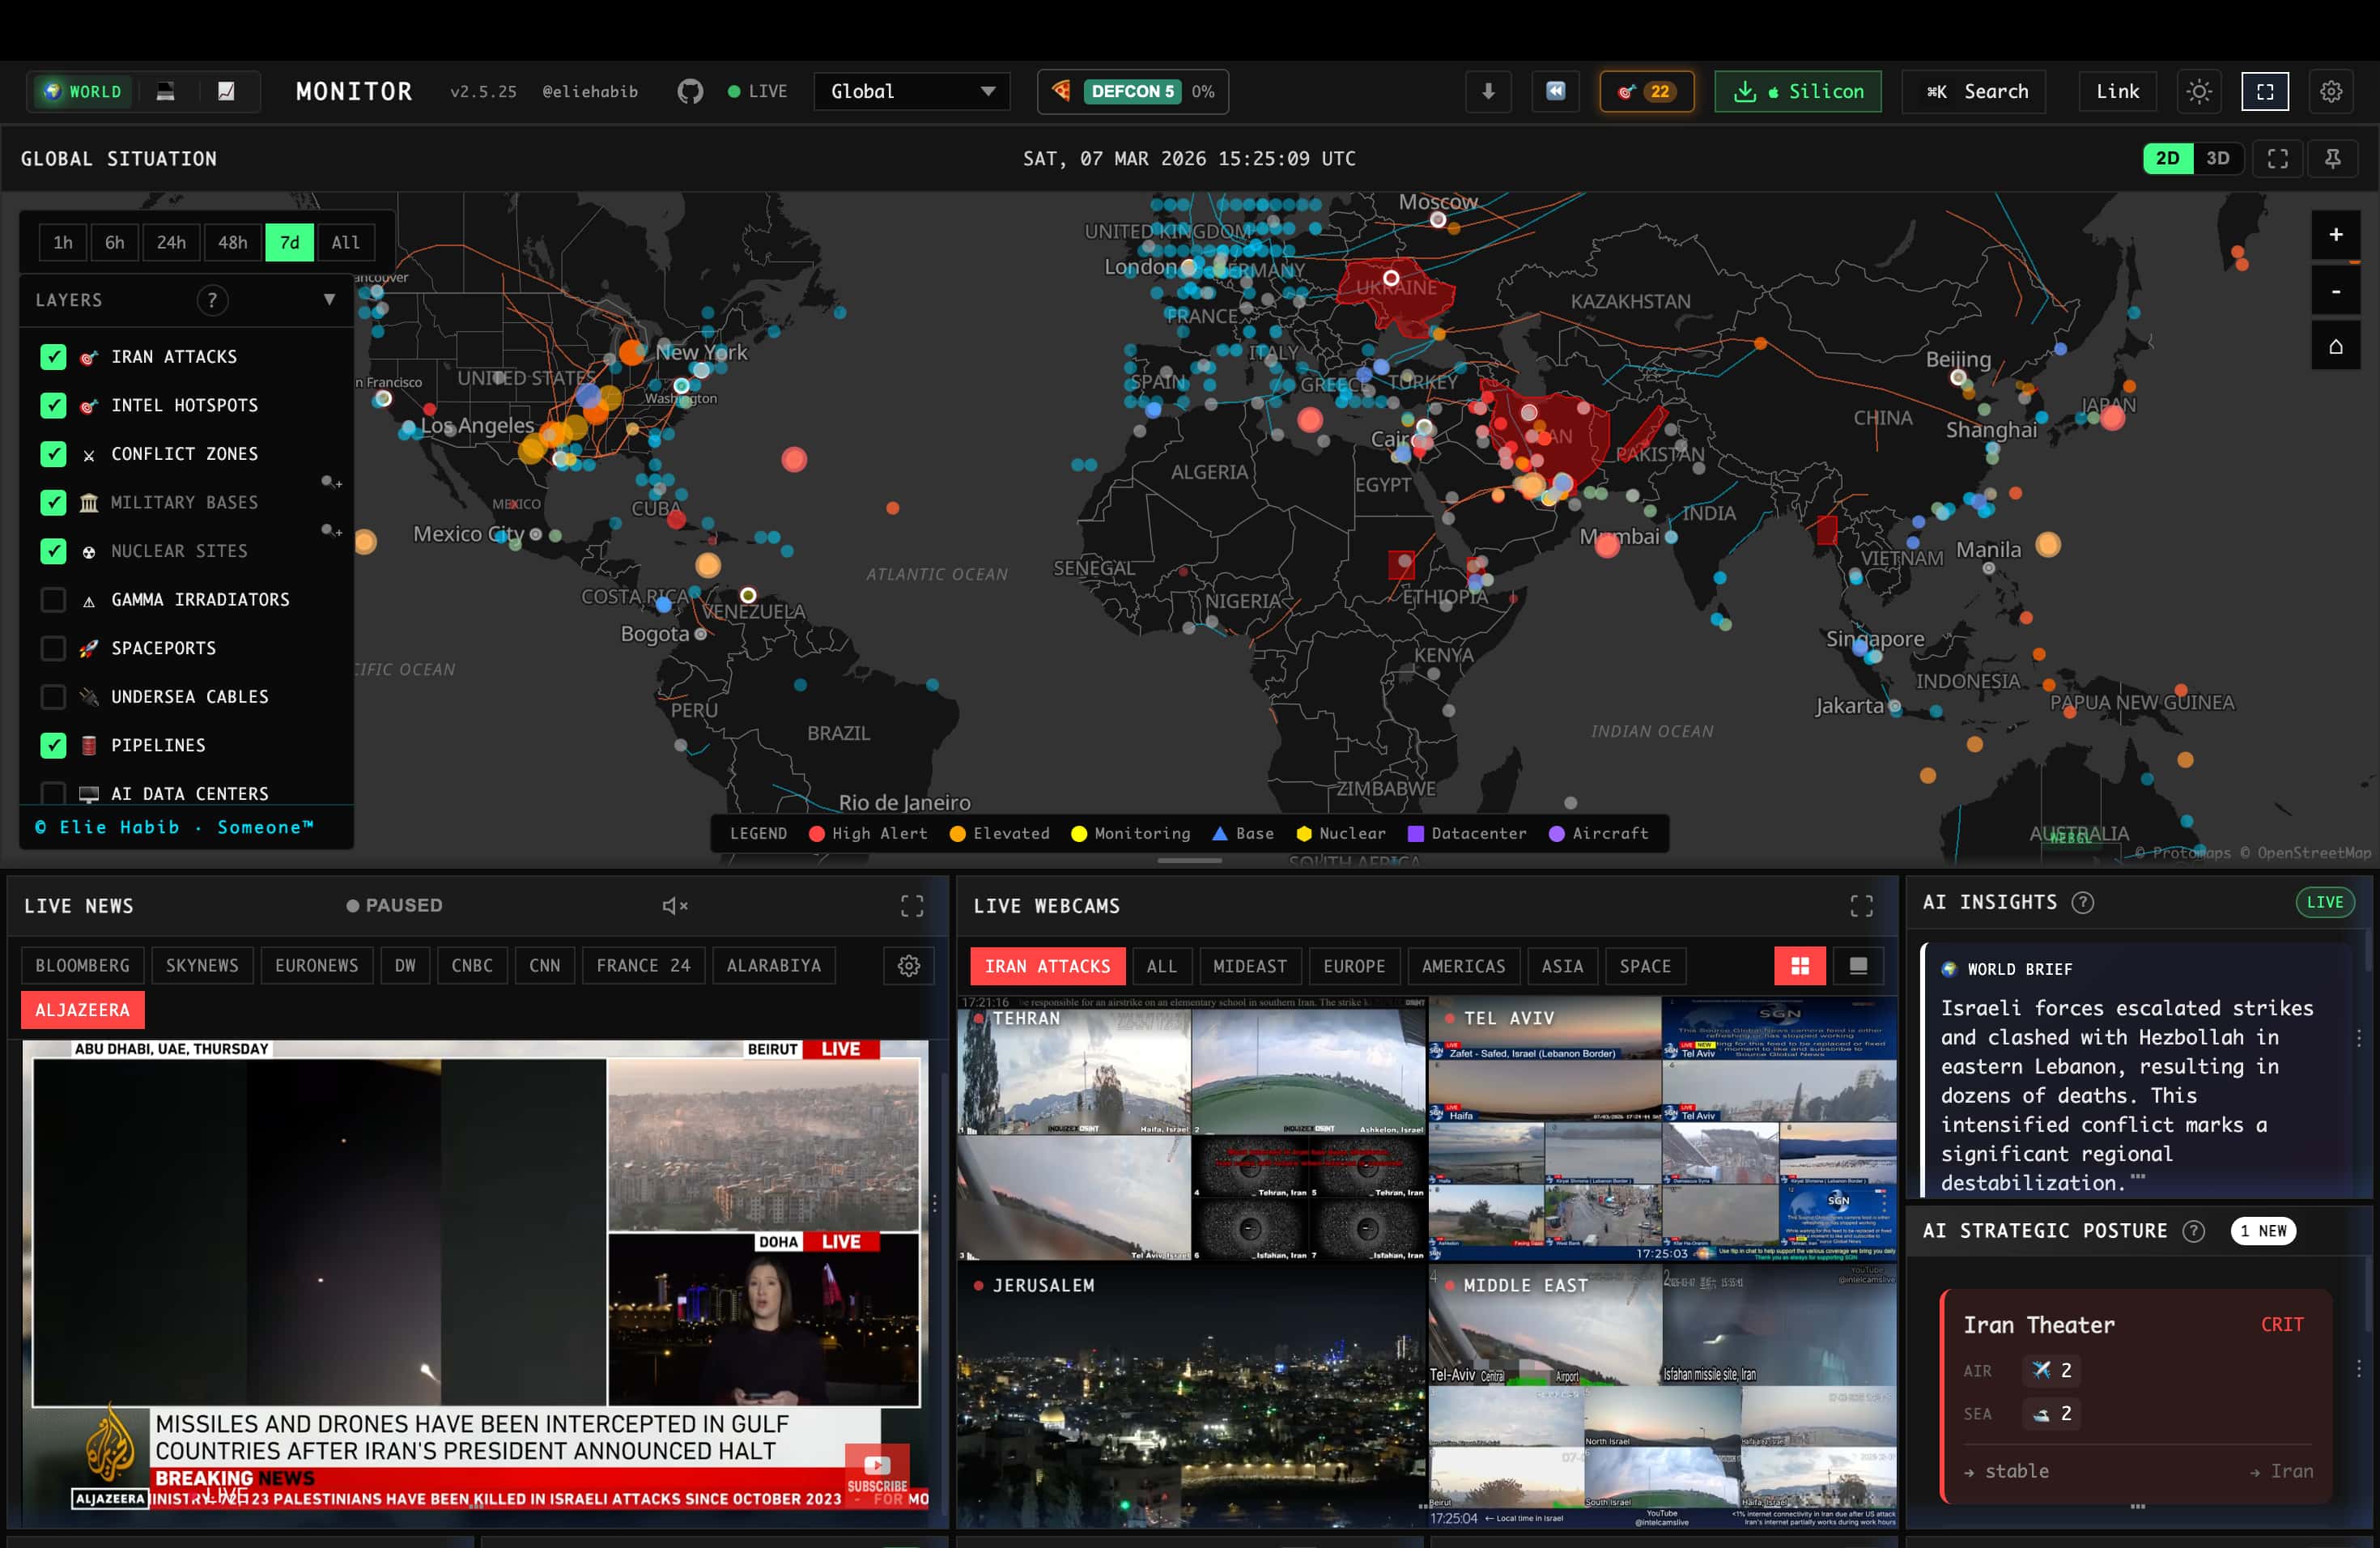 koala73/worldmonitor
实时全球情报仪表盘。AI驱动的新闻聚合、地缘政治监控和基础设施跟踪,集成在统一的情境感知界面中。
 cyberactivity/tyr
Tools collection to explore CVE and theirs associated data.

 prowler-cloud/prowler
Prowler 是全球使用最广泛的开源云安全平台,可在任何云环境中自动化安全与合规。立即连接你的代理,并基于 Agentic Cloud Defender 进行构建。
 misp/misp-objects
Curated JSON object templates that define MISP attributes and relationship types for structured threat intelligence sharing and interoperable IOC…
 crowdsecurity/crowdsec
开源IDS/IPS和WAF引擎,通过分析日志和HTTP请求来检测和阻止恶意IP,利用众包社区黑名单实现实时威胁情报。
 aquasecurity/vuln-list
NVD, Ubuntu, Alpine
 themittenmac/truetree
一个用于在 macOS 上生成类似 pstree 输出的命令行工具,具有额外的 PID 捕获功能。
 tenzir/tenzir
使用基于管道的数据流,大规模收集、解析、规范化、聚合、存储、查询和路由安全遥测数据,用于威胁检测和事件响应。
 domcyrus/rustnet
针对终端进行按进程的网络监控,具备深度包检测功能。跨平台,沙箱化。
 projectdiscovery/nuclei-templates
社区策划的用于 nuclei 引擎寻找安全漏洞的模板列表。
 vpierre/ndaal_public_sbom_auditor
Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…
 elastic/detection-rules
开发、验证并发布适用于 Elastic Security 的 SIEM 检测规则,提供 Python CLI 工具、KQL 解析、Kibana 集成以及打包好的威胁狩猎查询。






