
 #1

 cisagov/vulnrichment
一个用于进行漏洞信息增强的仓库。
 mthcht/awesome-lists
面向 SOC/CERT/CTI 检测与应急响应的精选威胁情报源、IoC 列表、YARA 规则及 DFIR 工具参考库。
 jivoi/awesome-osint
😱 一份精心整理的超棒 OSINT 资源列表
 functori/argos/argos
可疑操作图的分析与表示(Analyse et Représentation des Graphes des Opérations Suspectes)
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
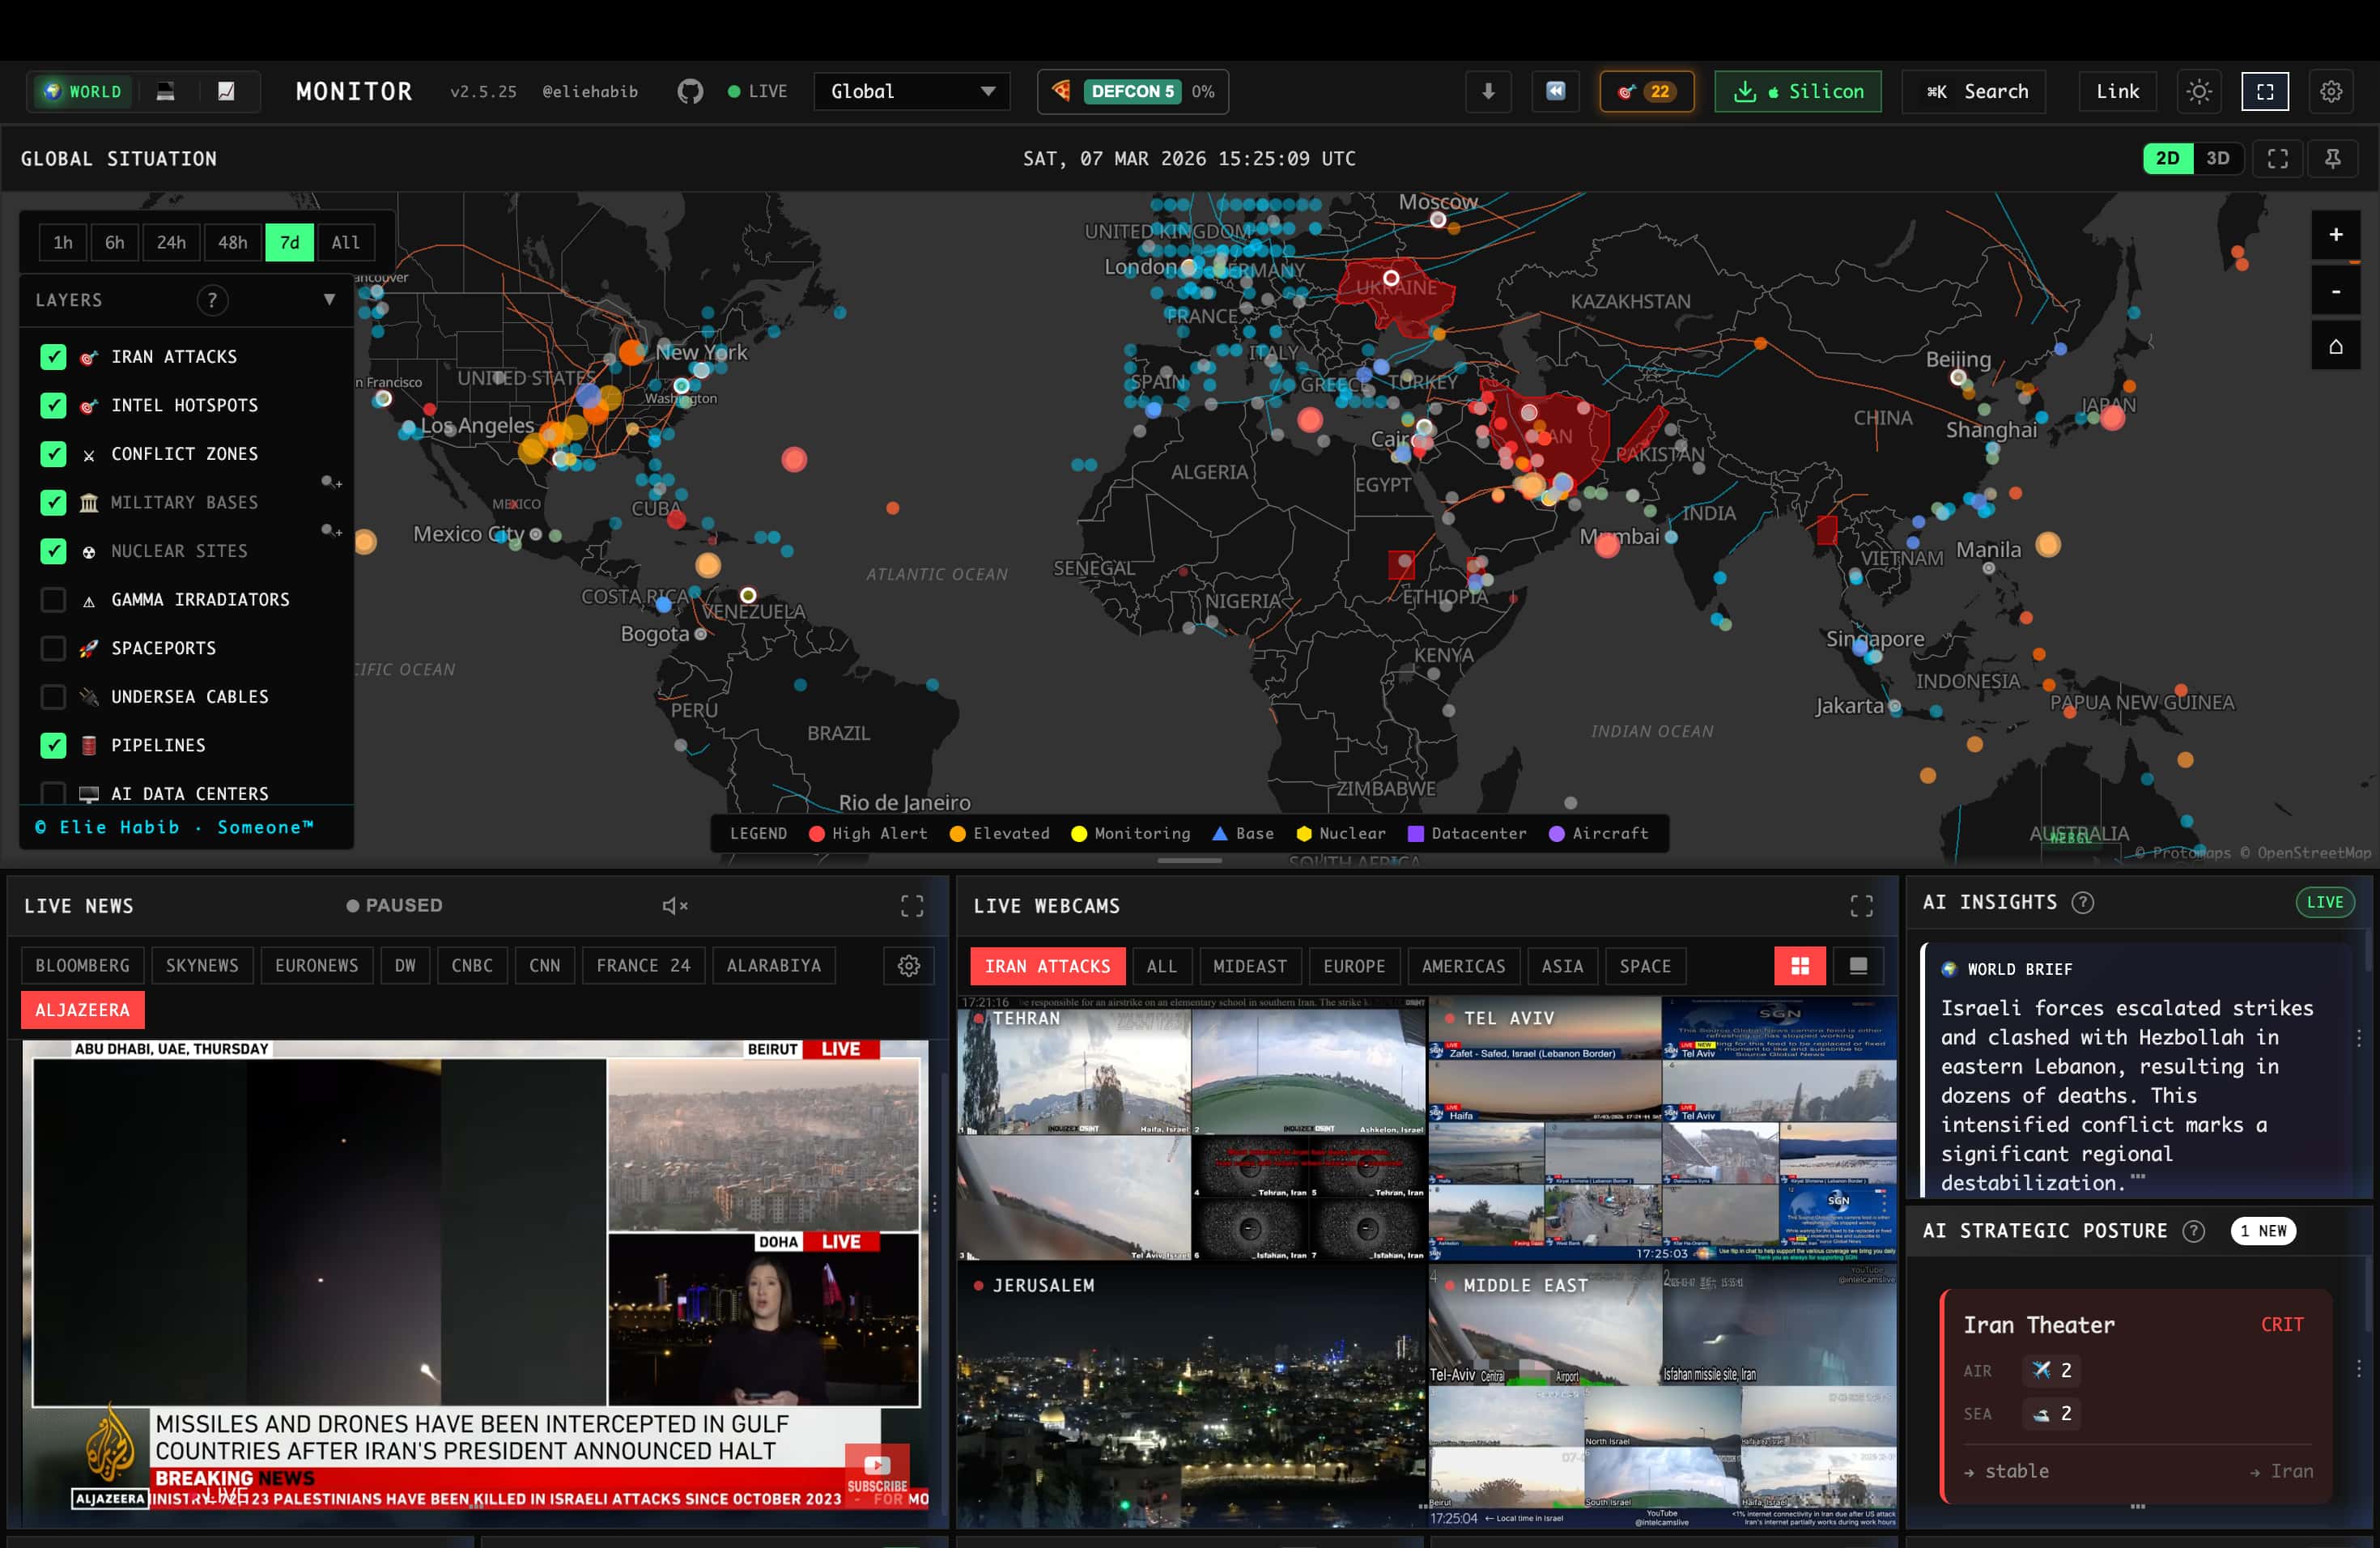 koala73/worldmonitor
实时全球情报仪表盘。AI驱动的新闻聚合、地缘政治监控和基础设施跟踪,集成在统一的情境感知界面中。
 bert-janp/open-source-threat-intel-feeds
该仓库包含可免费使用的开源威胁情报源,无需额外要求即可使用。涵盖多种类型,如IP、URL、CVE和哈希。
 facebook/threatexchange
用于携手对抗数字危害的信任与安全工具。
 simplifaisoul/osiris
Open Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
 paloaltonetworks/unit42-timely-threat-intel
一个包含威胁指标的文件集合,用于支持 Palo Alto Networks Unit 42 团队发布的社交媒体帖子,以传播及时的威胁情报。
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 opencti-platform/connectors
用于将来自 MISP 和 MITRE ATT&CK 等外部源的威胁情报、IOC 和 CTI 数据摄取并同步到平台中的 OpenCTI 连接器集合。
 misp/misp-objects
Curated JSON object templates that define MISP attributes and relationship types for structured threat intelligence sharing and interoperable IOC…
 crowdsecurity/crowdsec
开源IDS/IPS和WAF引擎,通过分析日志和HTTP请求来检测和阻止恶意IP,利用众包社区黑名单实现实时威胁情报。

 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
 mandiant/capa
基于规则的静态和动态分析工具,可识别PE、ELF、.NET和shellcode文件中的功能,并将其映射到MITRE ATT&CK技术,用于恶意软件分类。







