#1

 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 arxhr007/aliens_eye
AI powered OSINT engine to discover and map 7,700+ social media identities across the web
 zeroecco/holos
使用YAML compose文件的声明式KVM/QEMU VM编排工具。无需libvirt或XML即可管理包含cloud-init、SSH、PCI直通和镜像验证的多VM堆栈。
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 berylliumsec/nebula
AI-powered penetration testing assistant that automates reconnaissance, vulnerability analysis, and note-taking via integrated LLMs and CLI tool…
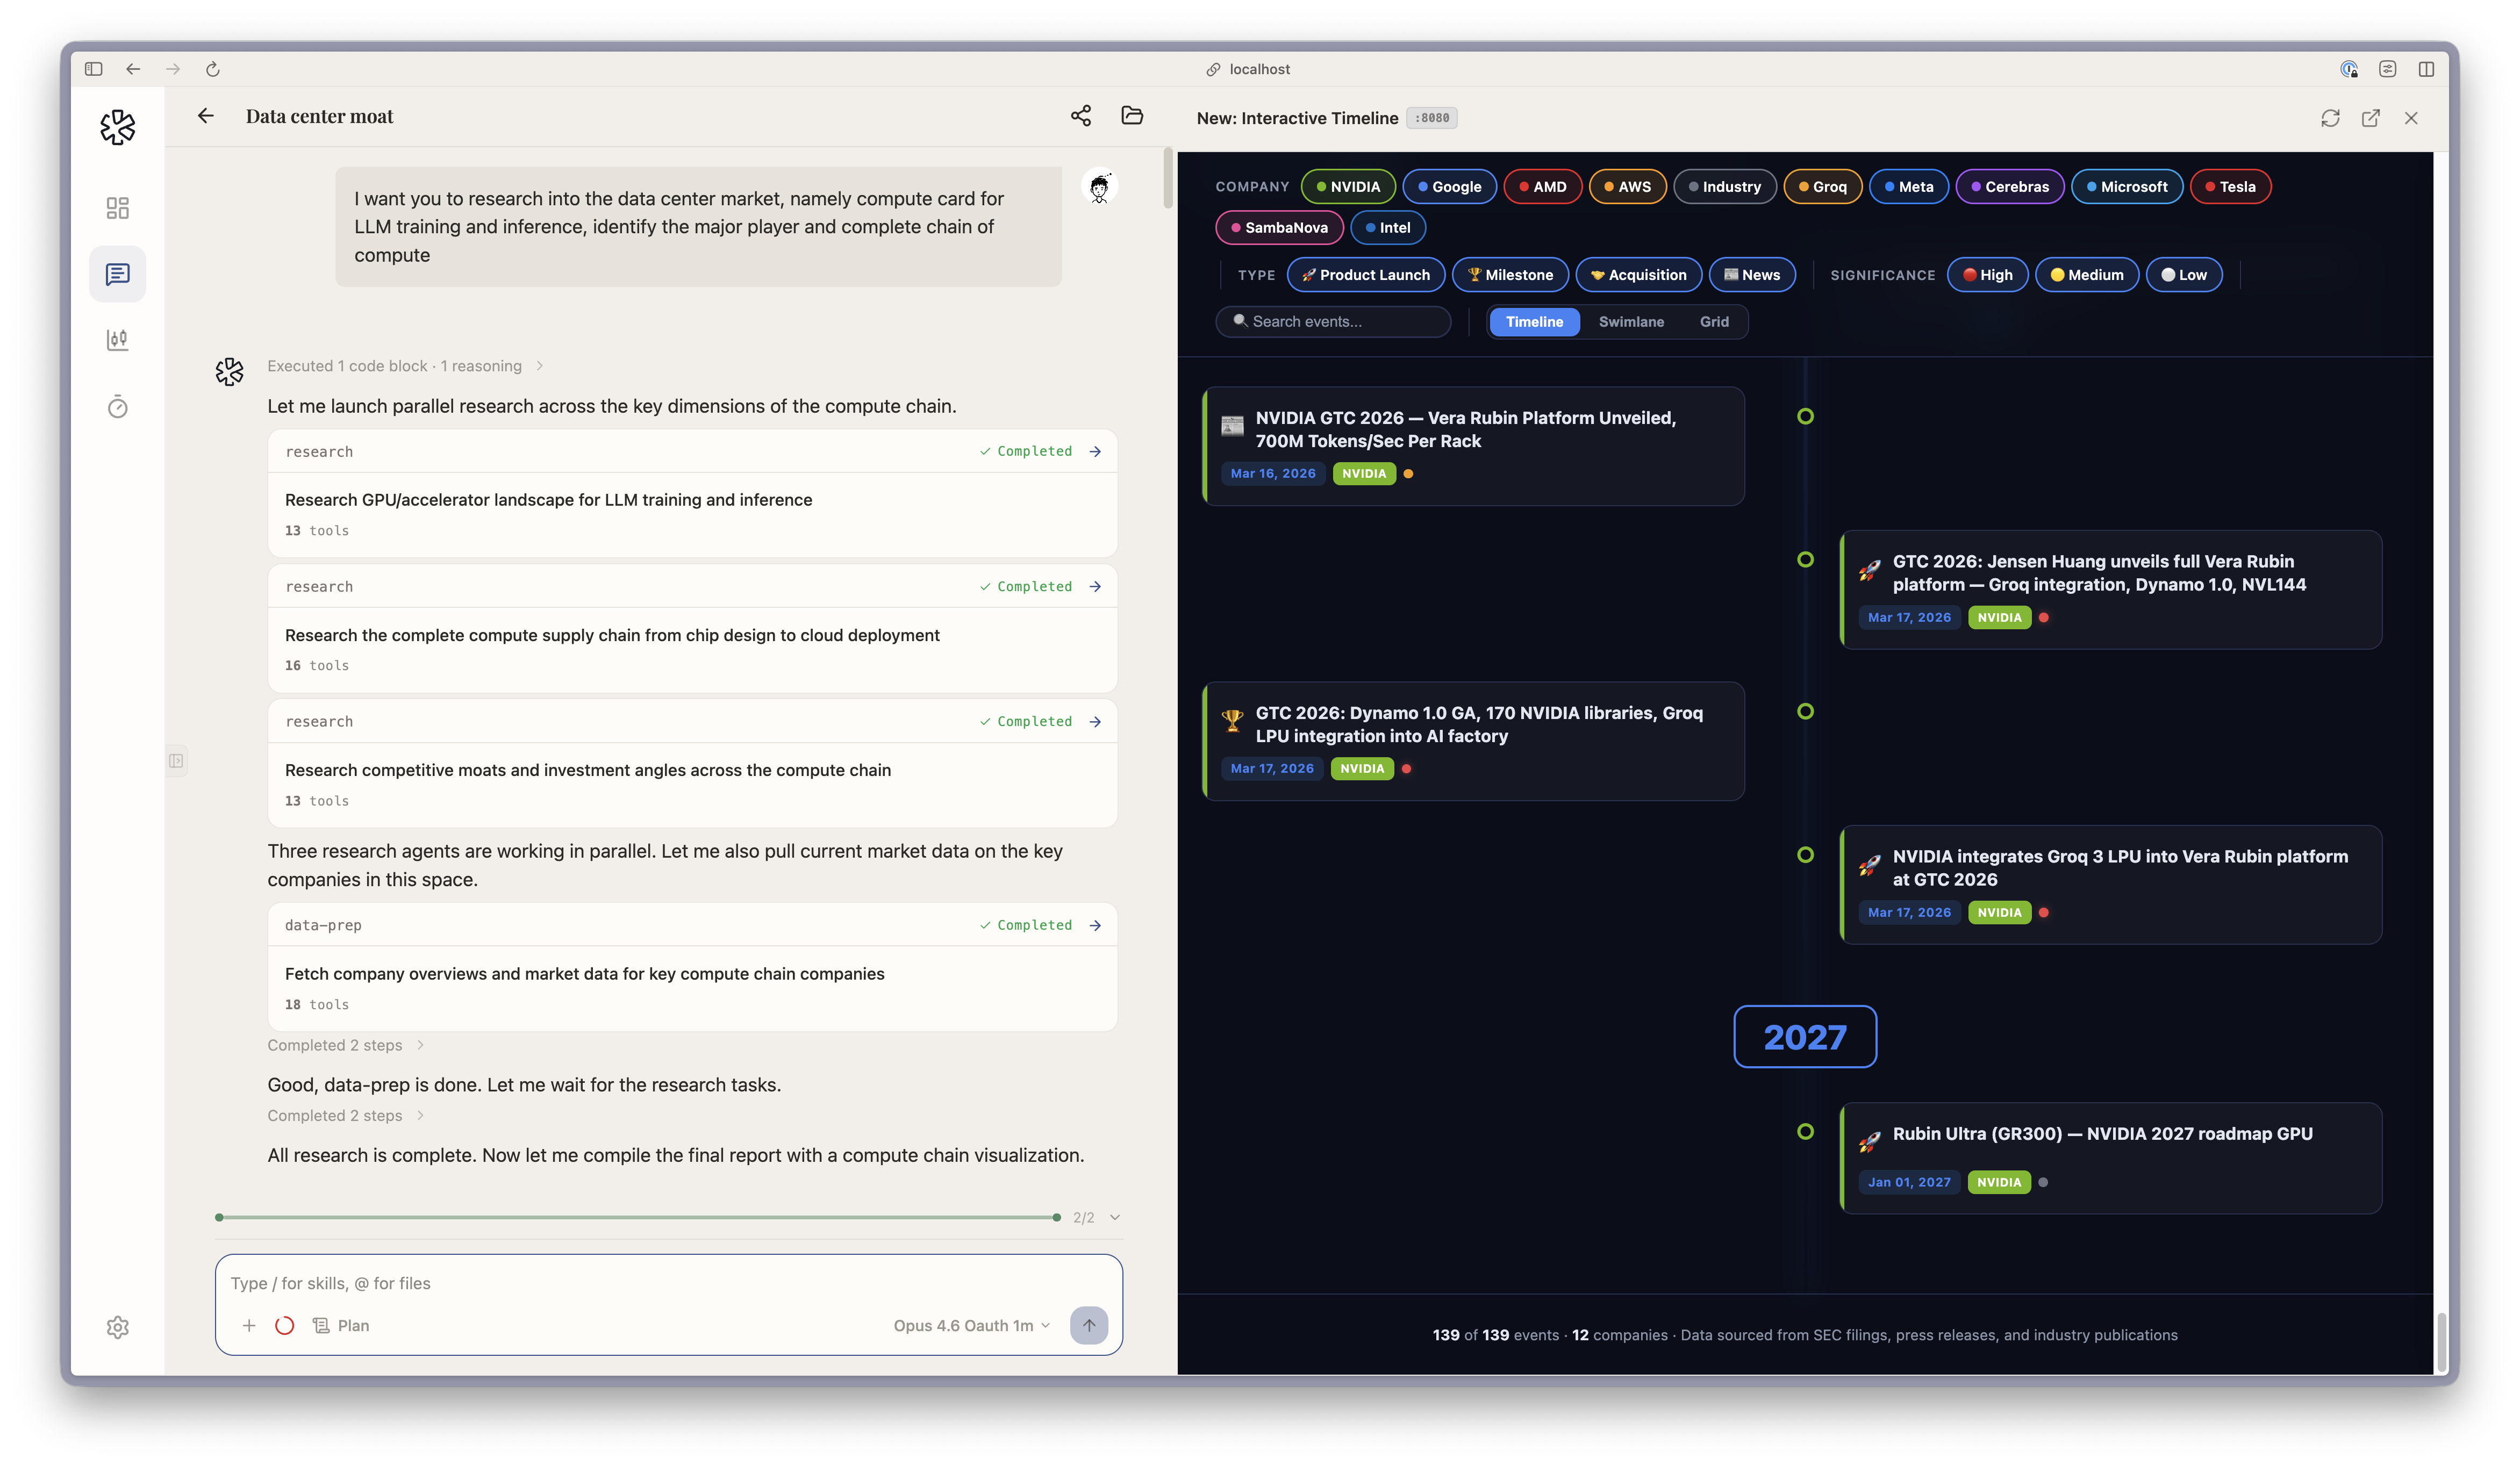 ginlix-ai/langalpha
自动化OSINT框架,用于侦察、数据收集和威胁情报聚合,配备模块化爬虫、扫描器和提取管道。
 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
 nousresearch/hermes-agent
与你共同成长的智能体

 projectdiscovery/nuclei
基于 YAML 的快速漏洞扫描器,采用模板驱动的检测引擎,可对 Web 应用、API、网络、DNS 和云基础设施进行自动化安全测试。
 pydantic/monty
A secure Python sandbox, written in Rust, for code written by AI.
 quaerendir/cve-2026-123633-123007-nginx-audit
针对五个 NGINX2Root nginx CVE(HTTP/2、HTTP/3、resolver、mail proxy)的只读 POSIX sh 审计,按 CVE 逐一判定
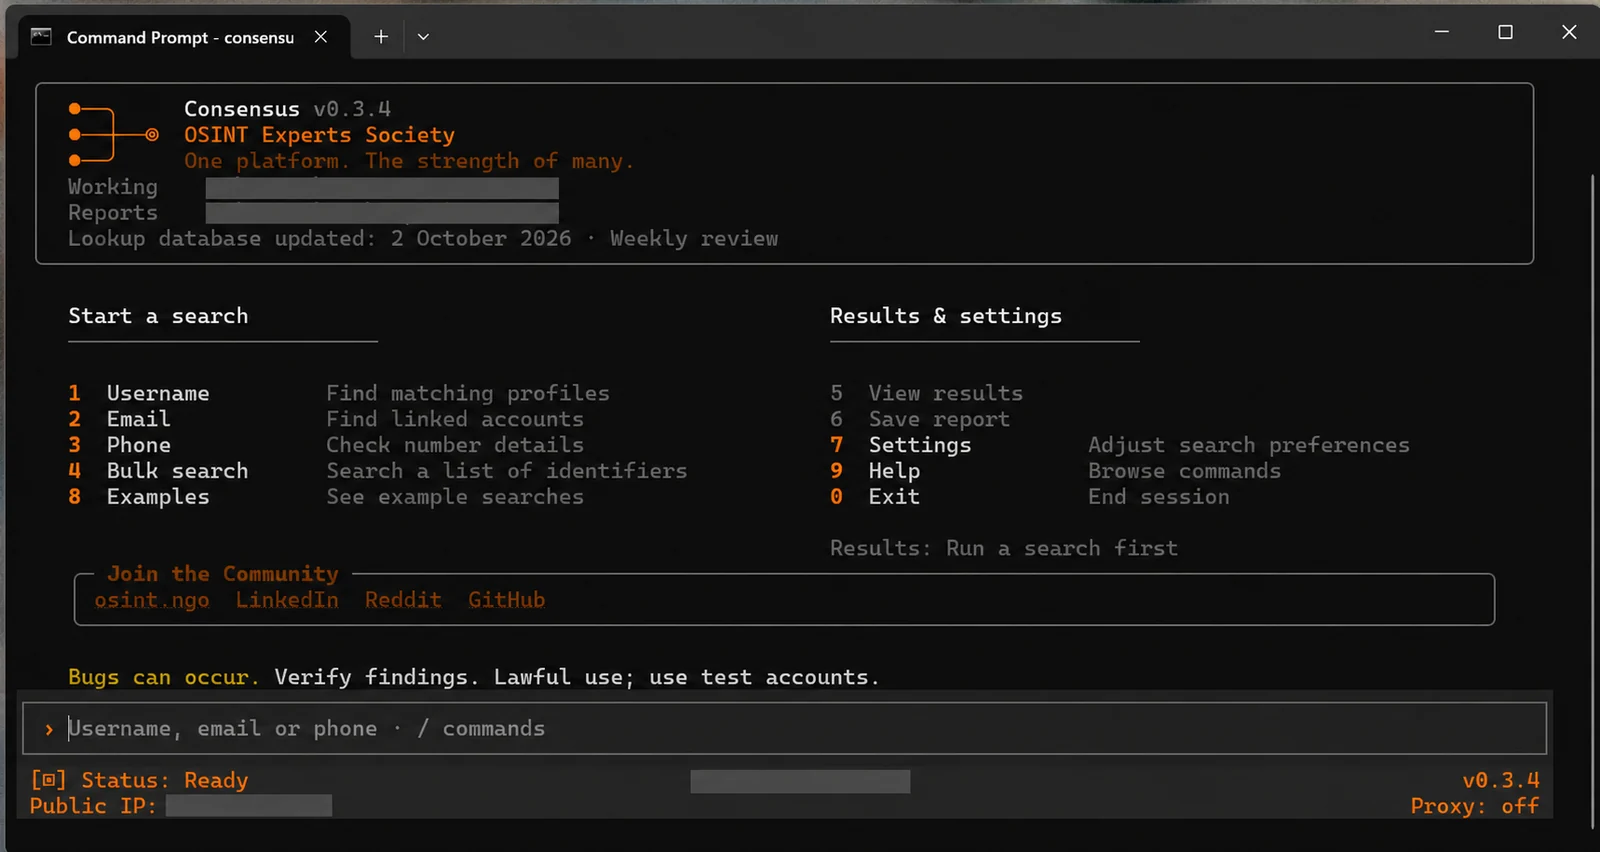 osint-experts-society/consensus-osint
🔎 用户名、邮箱和电话 OSINT — 来自 19 个项目的 9,700 多项查询检查,具备个人资料丰富、批量搜索、证据图谱和专家审核更新。
 nationalsecurityagency/ghidra
Ghidra 是一个软件逆向工程(SRE)框架
 altumptic/paranoia
Open reverse engineering — PE/ELF/Mach-O, x86/x64/AArch64, graphs, pseudocode. Rust engine, no network. Desktop · CLI · browser.
 devcop95/bugbounty-lab101
面向HackerOne研究人员的完整漏洞赏金工作区。包含范围强制执行、自动化侦察/漏洞流水线(400+工具)、报告模板、CVE/CWE监视列表,以及本地VM练习实验室。专为有纪律、合乎道德的狩猎而构建。
 apache/brpc
工业级 C++ RPC 框架,用于构建高性能分布式系统,支持多种协议(HTTP、gRPC、Redis、Thrift),内置负载均衡、命名服务和 RAFT 共识。