Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
论文与研究 — 第 70 页 | Kitploit
分类

论文与研究

用于防御或授权分析的安全论文、研究项目、技术参考和可复现资料。

Kitploit 推荐

精选工具

10 已选择
security-research preview#1

security-research

GitHubgoogle/security-research
4.6k13小时22分前
0days-in-the-wild preview#2

0days-in-the-wild

GitHubgoogleprojectzero/0days-in-the-wild
1.0k3个月前
MSRC-Security-Research preview#3

MSRC-Security-Research

GitHubmicrosoft/msrc-security-research
1.4k2年前
publications preview#4

publications

GitHubtrailofbits/publications
1.9k4天前
papers-we-love preview#5

papers-we-love

GitHubpapers-we-love/papers-we-love
111.6k20天前
criticality_score preview#6

criticality_score

GitHubossf/criticality_score
1.5k2个月前
attack-stix-data preview#7

attack-stix-data

GitHubmitre-attack/attack-stix-data
72512天前
Security-101 preview#8

Security-101

GitHubmicrosoft/security-101
6.8k2个月前
h4cker preview#9

h4cker

GitHubthe-art-of-hacking/h4cker
28.9k11小时44分前
offensive-ai-compilation preview#10

offensive-ai-compilation

GitHubjiep/offensive-ai-compilation
1.4k16天前
最新相关性最受欢迎最近更新
2266 结果
Copy-Fail-CVE-2026-31431-modernized preview

Copy-Fail-CVE-2026-31431-modernized

GitHubeynaexp/copy-fail-cve-2026-31431-modernized

CVE-2026-31431 的概念验证漏洞利用程序,由原始的 Copy Fail PE 漏洞利用程序现代化改造而来。用于教育目的演示该漏洞。

vulnerability-analysisexploitationweb-application-exploitation+2
36个月前
linux-entra-sso-PoC preview

linux-entra-sso-PoC

GitHubsqueeze440/linux-entra-sso-poc

PoC — 在 linux-entra-sso 中导致 Entra ID PRT SSO cookie 泄露的源验证错误(GHSA-g9vc-5j77-f2cm,CVE-2026-87005,CVSS 5.3)。

vulnerability-analysisexploitationweb-application-exploitation+5
2个月前
code-graph-rag-PoC preview

code-graph-rag-PoC

GitHubsqueeze440/code-graph-rag-poc

PoC — 在 code-graph-rag 中通过符号链接跟随实现项目根目录外的任意文件读写(GHSA-85gg-2gfq-q95m,CVE-2026-87008,CVSS 7.1)。
vulnerability-analysisexploitationweb-application-exploitation+3
2个月前
CVE-2026-63621 preview

CVE-2026-63621

GitHuboscerd/cve-2026-63621

Apache Camel camel-knative 结构化 CloudEvent 头注入(CVE-2026-63621)的概念验证复现器,演示了在 Spring Boot 和 Quarkus 运行时中通过恶意扩展字段进行的头注入。
vulnerability-analysisexploitationweb-security+2
2个月前
DirtyPipe-CVE-2022-0847 preview

DirtyPipe-CVE-2022-0847

GitHubvinukalana/dirtypipe-cve-2022-0847

此仓库用于分析和理解DirtyPipe漏洞利用CVE-2022-0847
privilege-escalationvulnerability-analysisexploitation+3
24年前
Breaking-the-Update-Chain-Inside-CVE-2025-59287-and-the-WSUS-RCE-Threat preview

Breaking-the-Update-Chain-Inside-CVE-2025-59287-and-the-WSUS-RCE-Threat

GitHubmrk336/breaking-the-update-chain-inside-cve-2025-59287-and-the-wsus-rce-threat

CVE-2025-59287的技术分析与概念验证漏洞利用,这是Windows Server Update Services中通过不安全反序列化导致的严重远程代码执行漏洞,包括受影响版本和缓解步骤。

vulnerability-analysisexploitationweb-application-exploitation+2
41年前
CVE-2026-99999-exploit preview

CVE-2026-99999-exploit

GitHub01luyicheng/cve-2026-99999-exploit

CVE-2026-99999 可用 PoC — 针对 Linux 内核 csum_start 漏洞的真实虚拟机逃逸(CVSS 9.3)。客户机到主机的堆内存泄漏。另见:CVE-2026-99999-analysis(教育用途)。

vulnerability-analysisexploitationinformation-gathering+3
11天前
CVE-2026-73312 preview

CVE-2026-73312

GitHubbombobombone/cve-2026-73312

# CVE-2026-73312 的概念验证与技术报告 针对 XenForo 2.3.13 之前版本中 OAuth2 刷新令牌重放漏洞的概念验证与技术报告。包含一个用于测试该问题的 Python 脚本。

vulnerability-analysisexploitationweb-security+2
2个月前
CVE-2026-71300 preview

CVE-2026-71300

GitHuboscerd/cve-2026-71300

针对 Apache Camel camel-atmosphere-websocket 调度头注入(CVE-2026-71300)的概念验证复现器,演示注入的头如何将 WebSocket 消息重定向到攻击者选择的接收者。

vulnerability-analysisexploitationweb-application-exploitation+2
2个月前
CVE-2026-46590 preview

CVE-2026-46590

GitHuboscerd/cve-2026-46590

CVE-2026-46590 的复现工具:Apache Camel camel-pqc 密钥生命周期不安全反序列化(FileBasedKeyLifecycleManager 通过 ObjectInputStream 进行旧版 .key 迁移),对 CVE-2026-40048 的修复不完整(已在…

vulnerability-analysiscode-analysisexploitation+3
3个月前
CVE-2026-34975 preview

CVE-2026-34975

GitHubromain-deperne/cve-2026-34975

针对 Plunk 原始 MIME 构造中 CRLF 电子邮件头注入的概念验证与技术分析,通过 Python PoC 演示 Bcc 注入及其他攻击向量。

vulnerability-analysisexploitationweb-application-exploitation+2
2个月前
litellm-command-injection-security-assessment preview

litellm-command-injection-security-assessment

GitHubamnsecurity/litellm-command-injection-security-assessment

针对LiteLLM命令注入风险的专业漏洞评估报告,包括执行摘要、技术影响、修复和缓解策略。

reconnaissancevulnerability-analysisweb-application-exploitation+3
34个月前
CVE-2023-42222 preview

CVE-2023-42222

GitHubitssixtyn3in/cve-2023-42222

CVE-2023-42222在WebCatalog中的概念验证利用,演示了通过Electron的shell.openExternal实现任意URL执行,以绕过安全保护并执行代码。

vulnerability-analysisexploitationweb-application-exploitation+2
33年前
CVE-2022-0847 preview

CVE-2022-0847

GitHubvudangducminh/cve-2022-0847

CVE-2022-0847(Dirty Pipe)的概念验证漏洞利用,这是一个 Linux 内核竞态条件漏洞,允许非特权用户写入只读文件并实现权限提升。

privilege-escalationvulnerability-analysisexploitation+3
2个月前
terrapod-PoC preview

terrapod-PoC

GitHubsqueeze440/terrapod-poc

PoC — Terrapod 中平台级 GPG 信任锚存储缺少授权(GHSA-6qrc-597p-mrp9,CVE-2026-87006,CVSS 6.5)。
authentication-authorizationvulnerability-analysisexploitation+4
2个月前
CVE-2026-76565 preview

CVE-2026-76565

GitHubtoanln-cov/cve-2026-76565

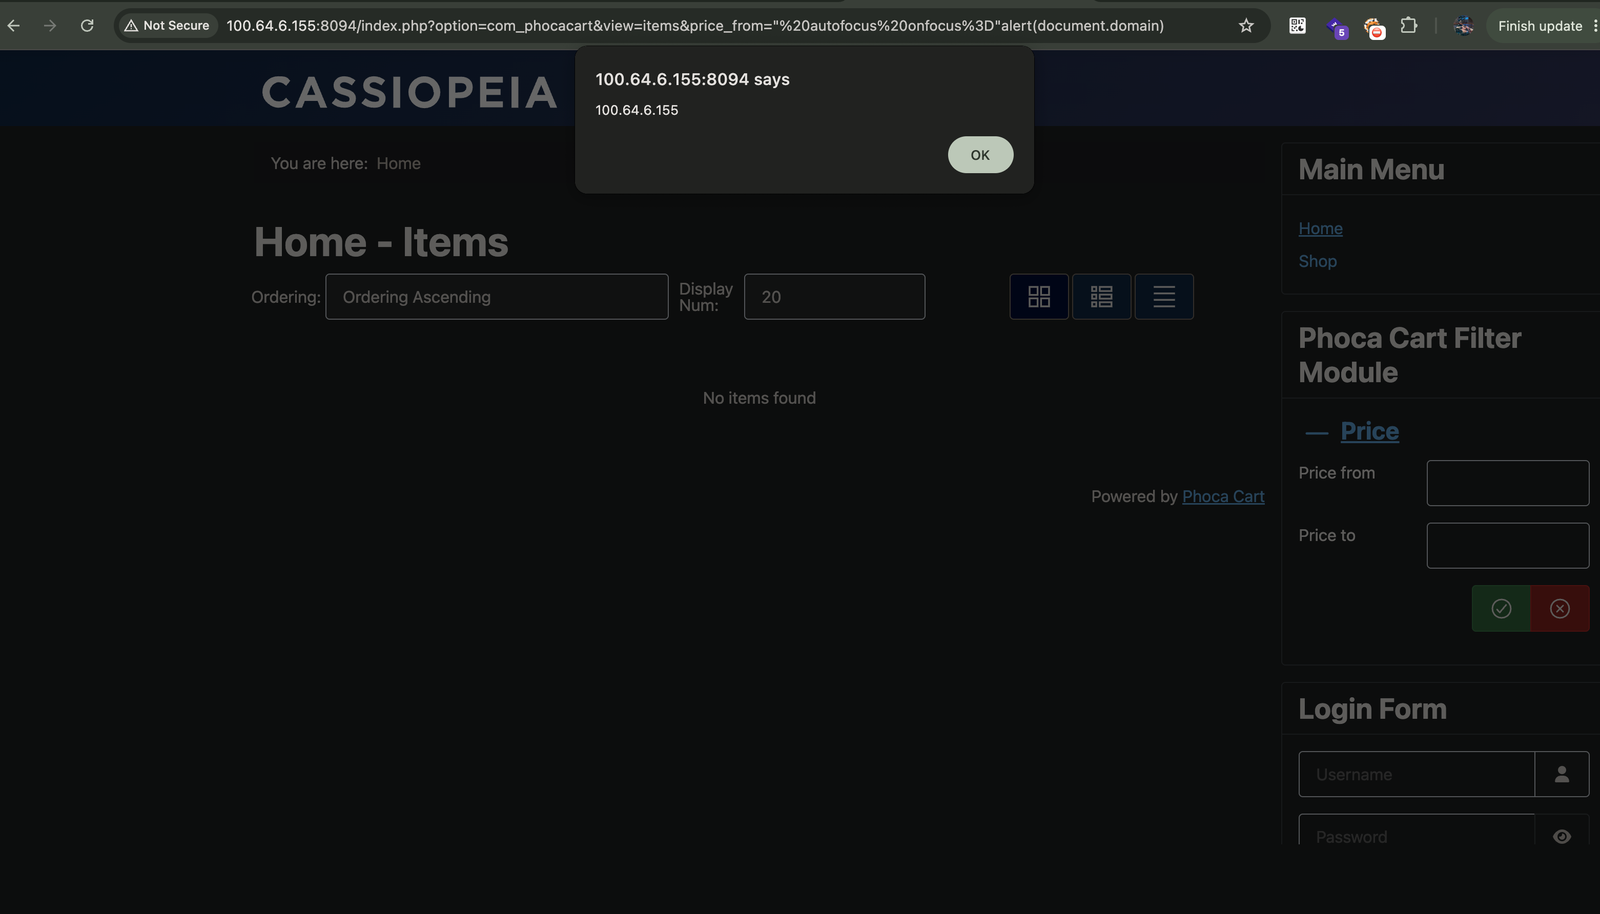
PhocaCart 中通过 price_from 与 price_to 过滤参数导致的反射型 XSS

vulnerability-analysisexploitationweb-application-exploitation+2
2个月前
CVE-2026-46584 preview

CVE-2026-46584

GitHuboscerd/cve-2026-46584

CVE-2026-46584 的复现工具:Apache Camel camel-mail 中 mail.smtp.* 标头注入,可通过路径上的 SOCKS 拦截实现凭据窃取(已在 4.14.8/4.18.3/4.21.0 中修复)

vulnerability-analysisexploitationweb-application-exploitation+3
3个月前
pgm-attack preview

pgm-attack

GitHubatsukisato/pgm-attack

针对PGM索引的投毒攻击研究代码,演示如何构造对抗性数据以降低学习型索引的性能。

machine-learningpapers-researchai-security+1
114天前
上一页1…697071…100下一页