#1

 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 yasindce1998/barzakh
Ring -4 到 Ring 0:攻防固件研究平台。我们先构建 bootkit,然后再捕获它们。闭环。对硅片零信任。
 cplusplus17/deco-filepush-disclosure
TP-Link Deco XE75 Pro V3 调试通道(tmpsvr 操作码 0xC456/0xF0)中 root 文件读写漏洞的披露与 PoC,包含 CVSS 分析和处理程序反编译。
 c8dhjp4tyv-bit/jbl-wave-buds2-firmware-research
Reverse-engineering notes and Python tooling for JBL Wave Buds 2 (BES1306) firmware: OTA container format, flash layout, BLE/GATT protocol, and…
 newbe3e/pwn2own-automotive-2026-alpine-ilx-f511-0-click-rce-exploit-writeup
Writeup of a 0-click remote code execution exploit chain developed for the Alpine iLX-F511 automotive head unit at Pwn2Own Automotive 2026.
 abraxas/sonic-gnmi-noauth
Documents and reproduces a fail-open authentication flaw in SONiC gNMI where an empty UserAuth map allows unauthenticated gNMI Set and gNOI writes,…
 greatscottgadgets/facedancer
在Python中实现你自己的USB设备,由Cynthion或GreatFET等硬件外设提供支持
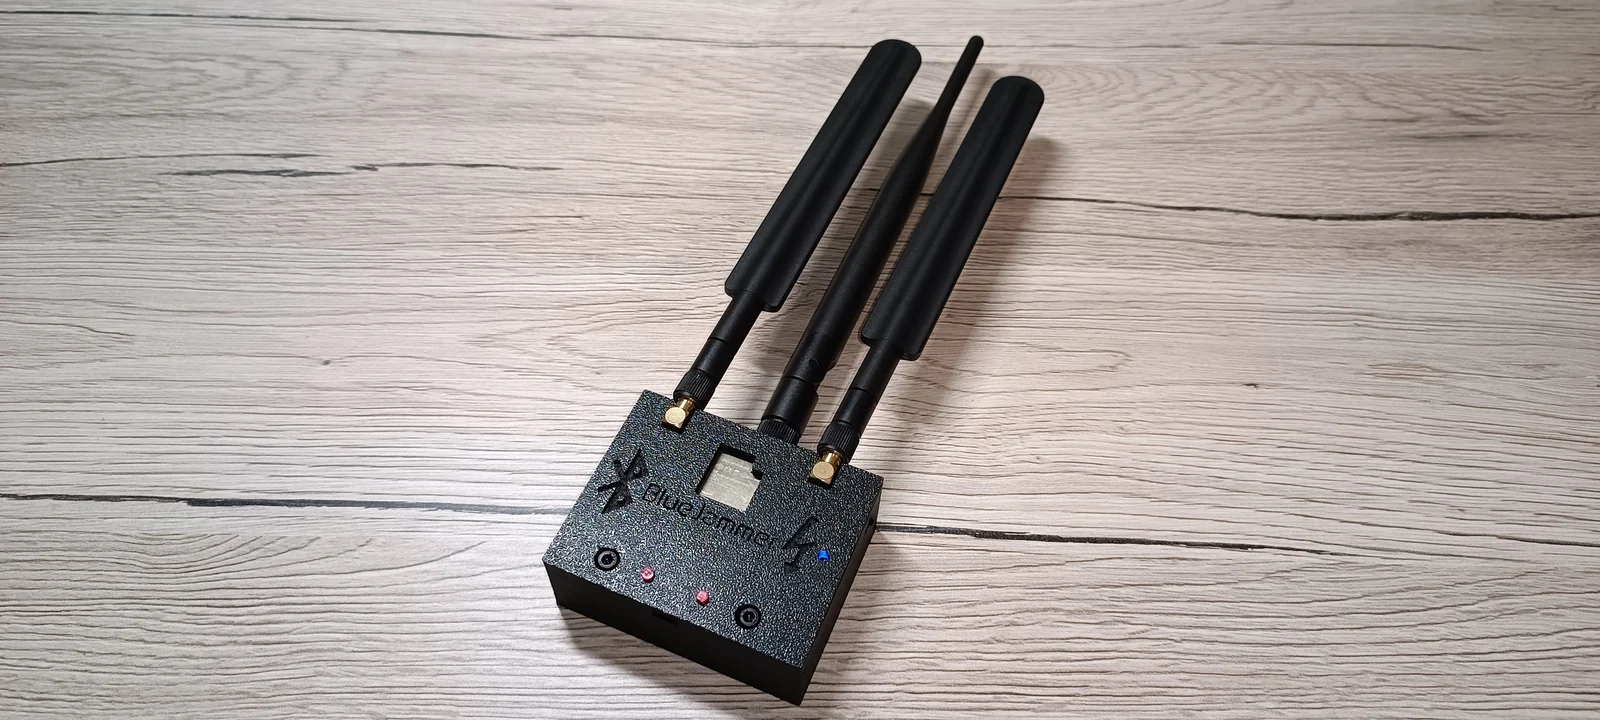 emenstanougat/esp32-bluejammer
基于ESP32和nRF24的2.4GHz干扰器,通过噪声和数据包洪泛干扰蓝牙、BLE、WiFi和RC信道,用于受控安全测试。
 jihoonjang98/hqc-x86-simd
面向AVX2和AVX-512(含GFNI)的优化HQC后量子KEM实现,以及面向x86物联网网关的统一基准测试与NIST KAT套件。
 wolfssl/wolfssh
小型、可移植、可嵌入的 C 语言 SSHv2 客户端与服务器库,支持 SCP、SFTP、端口转发以及面向嵌入式和 IoT 系统的后量子密钥交换。
 bignerd95/chimay-red
Vault 7 CIA 泄露中 Mikrotik 漏洞利用的工作 POC
 qmonnet/rbpf
用于eBPF程序的Rust虚拟机和JIT编译器
 vulncheck-oss/cisco-ios-xe-implant-scanner
基于Go的扫描器,通过发送精心构造的HTTP请求来检测被植入后门的Cisco IOS XE系统,以识别受感染的设备和存在漏洞的版本。
 j-baines/even-you-brutus
Mikrotik RouterOS 6.x Web 界面的字典暴力破解
 microsoft/routeros-scanner
用于扫描 RouterOS(Mikrotik)取证痕迹和漏洞的工具。
 therealsaumil/static-arm-bins
用于调试和运行时分析的静态编译 ARM 二进制文件
 superkhung/luadec-tplink
修改版 luadec,用于反编译 TP-Link Archer C7 的 LUA 固件。