#1


 structio-labs/n0xis
Reverse-engineering toolkit: disassembler, SSA decompiler, C++ class recovery and live-process analysis for PE and ELF. Scriptable CLI, every answer…
 lief-project/lief
跨平台库,用于解析、修改和抽象ELF、PE和MachO可执行格式。支持C++、Python和Rust API,并具备反汇编器、汇编器和调试信息功能。
 werwolv/imhex
🔍 一款为逆向工程师、程序员以及那些珍视凌晨3点工作时视网膜的人而设计的十六进制编辑器。
 morluto/awesome-reverse-engineering
Curated reverse-engineering tools and learning resources for binaries, apps, firmware, formats, and protocols.
 bunnybuzz/enigma
原生 C++ 逆向工程引擎,具备针对 PE/ELF 二进制的反汇编、反编译与分析流水线,提供交互式 GUI 并兼容 Ghidra 的反编译器。
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset

 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 ibotpeaches/apktool
一个用于逆向工程安卓apk文件的工具
 neurosaki987/tvm-recover
反虚拟化腾讯 VM 的 .tvm0 节区:将 VM 处理程序提升为 guest 级清单和 LLVM IR,恢复 CFG 与分发逻辑,并将恢复的代码修补回 PE。
 rizinorg/cutter
免费开源逆向工程平台由 rizin 驱动
 ph4ntom-rev/ph4ntom-ida-bridge
Secure local REST, CLI, MCP, and agent bridge for IDA Pro 9.x
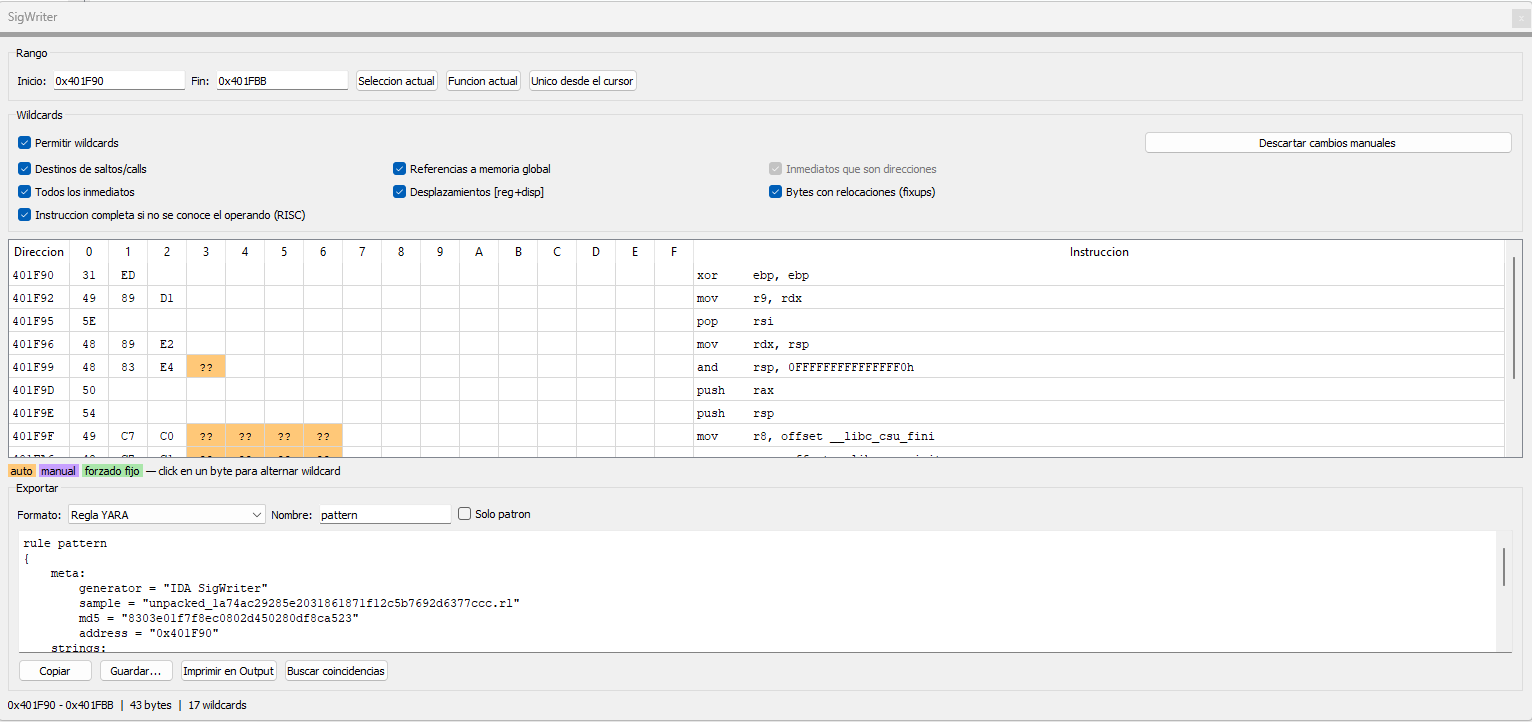 crackinglandia/idasignwriter
IDA Pro 插件,可从反汇编选择中生成字节签名,支持自动和手动通配符、匹配搜索,并可导出为 YARA、x64dbg、C 数组和二进制块。
 pdb333/cortex
Analyze software: memory scanner, debugger and static analysis of executables, .NET and Electron apps, from the desktop, the command line, or an AI…
 jp/hermes-proxy
Hermes Proxy - HTTP流量分析器