
 #1

 x64dbg/x64dbg
一个开源的Windows用户模式调试器。针对逆向工程和恶意软件分析进行了优化。
 z3prover/z3
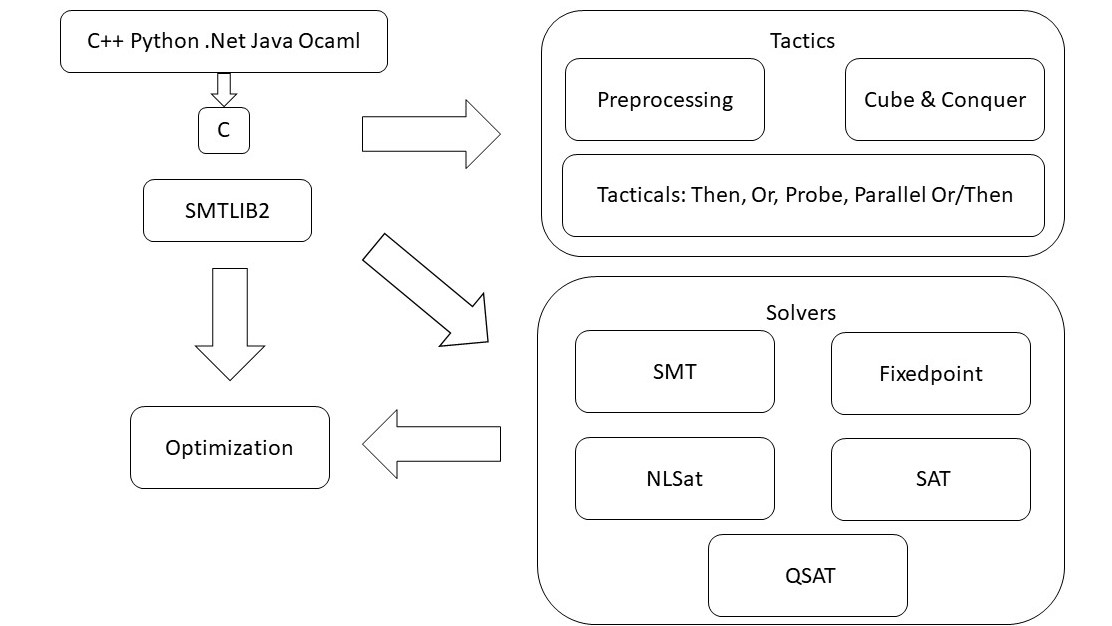
High-performance SMT solver for automated theorem proving, constraint solving, and program verification. Supports multiple theories and language…
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…

 momo5502/sogen
🪅 Windows & Linux userspace emulator
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 horsicq/xpeviewer
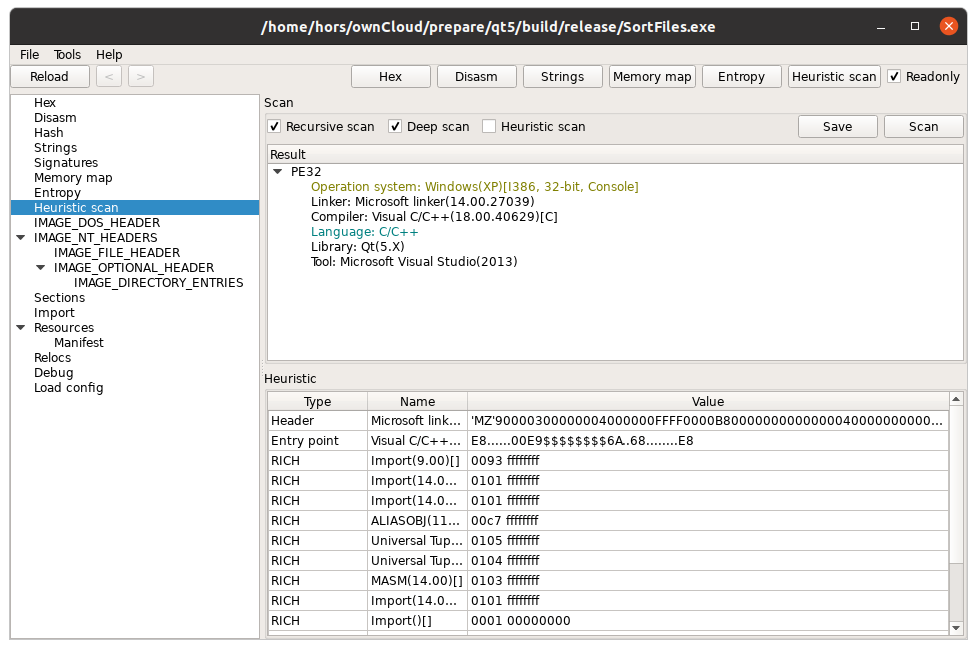
适用于 Windows、Linux 和 MacOS 的 PE 文件查看器/编辑器。
 horsicq/xmachoviewer
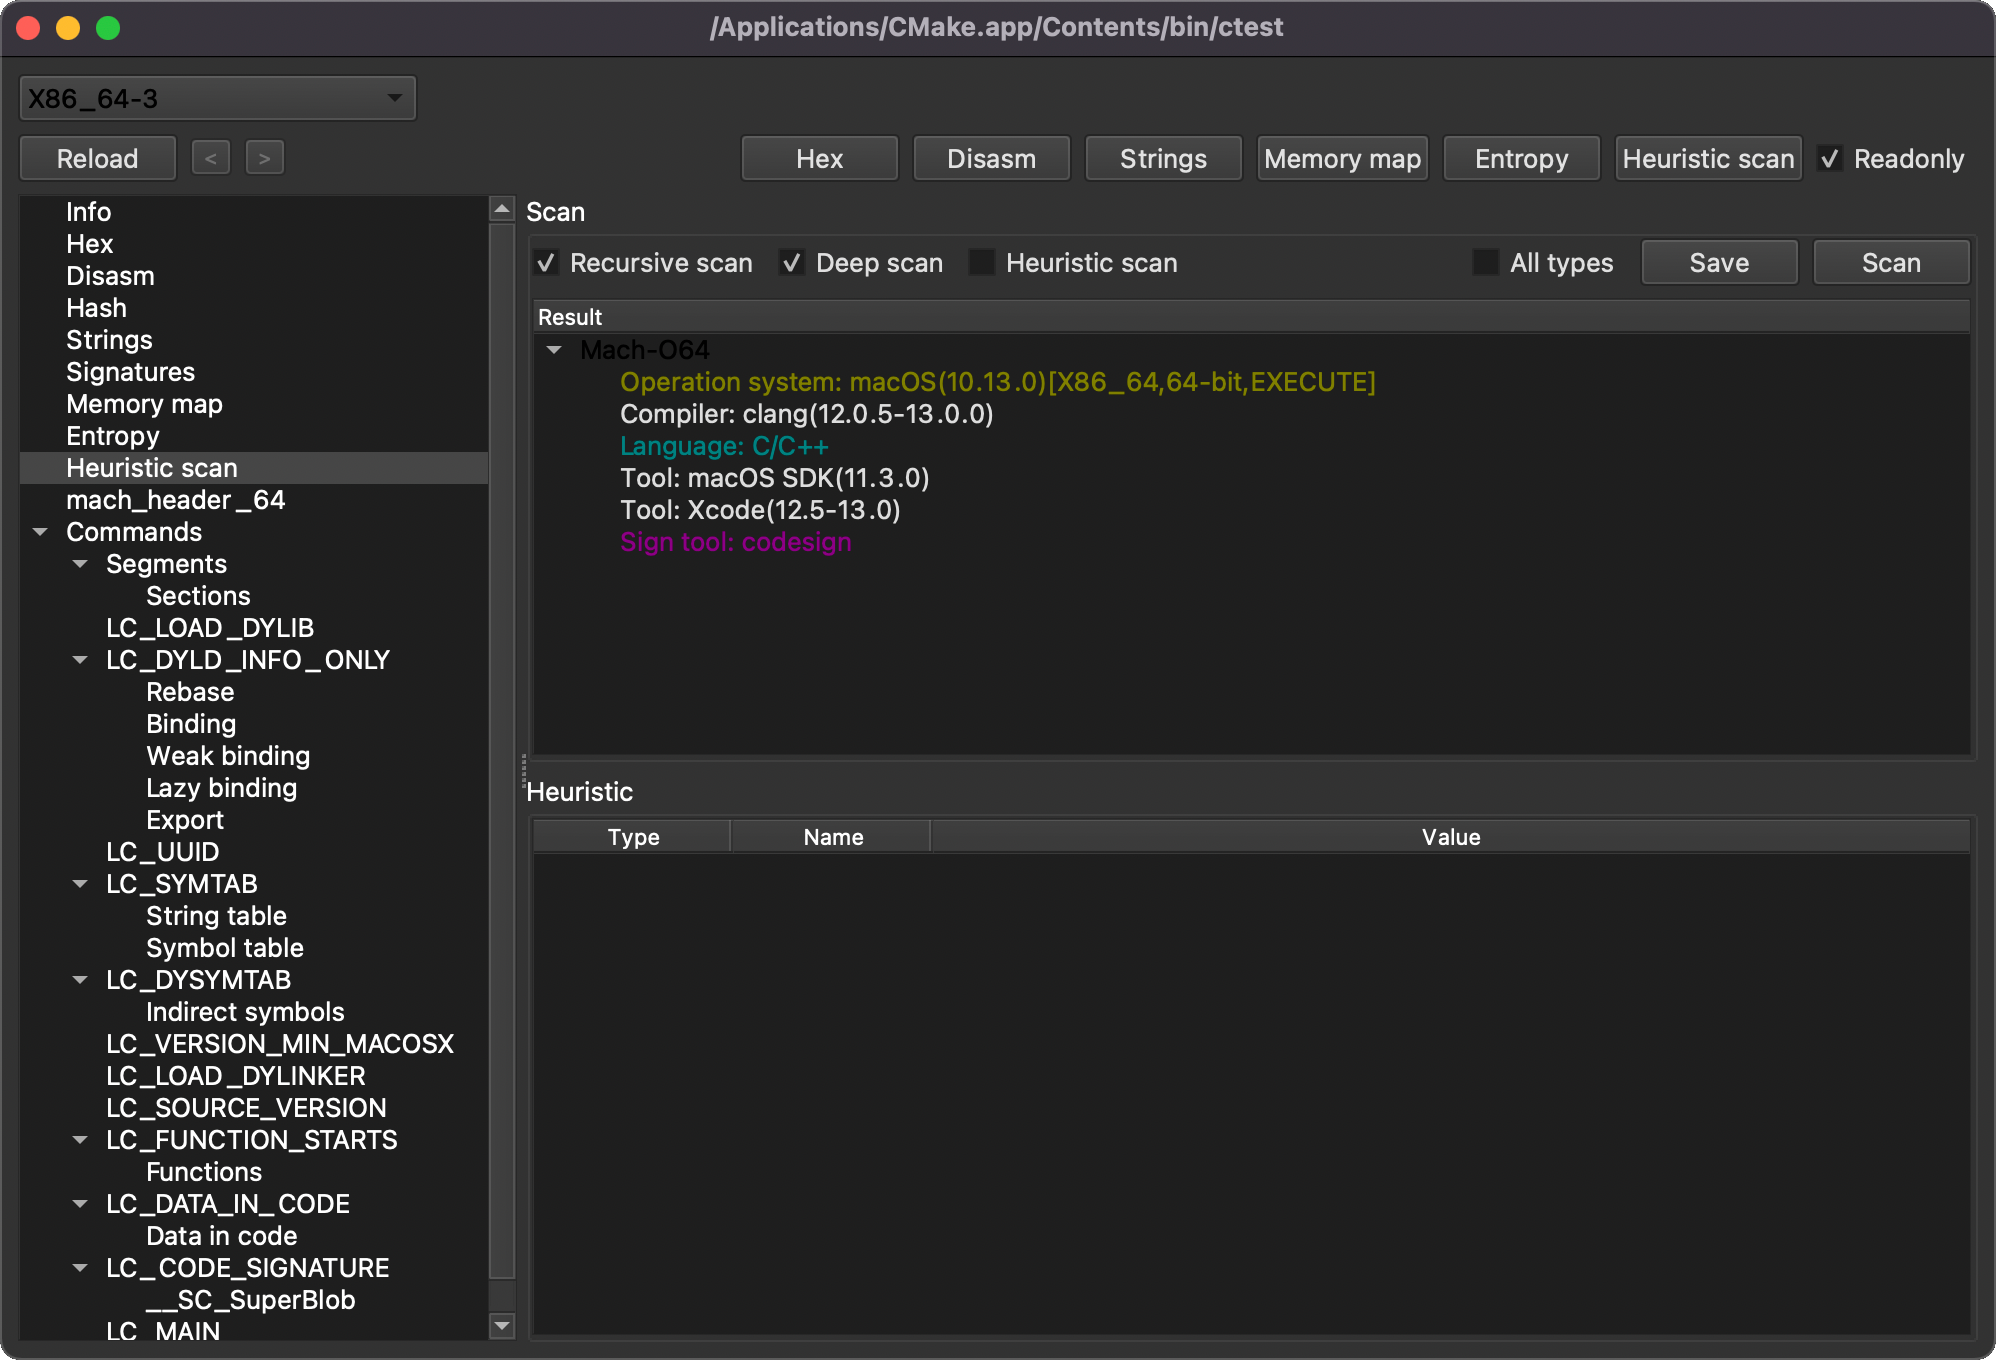
XMachOViewer 是一款适用于 Windows、Linux 和 MacOS 的 Mach-O 查看器。
 vu-ls/crassus
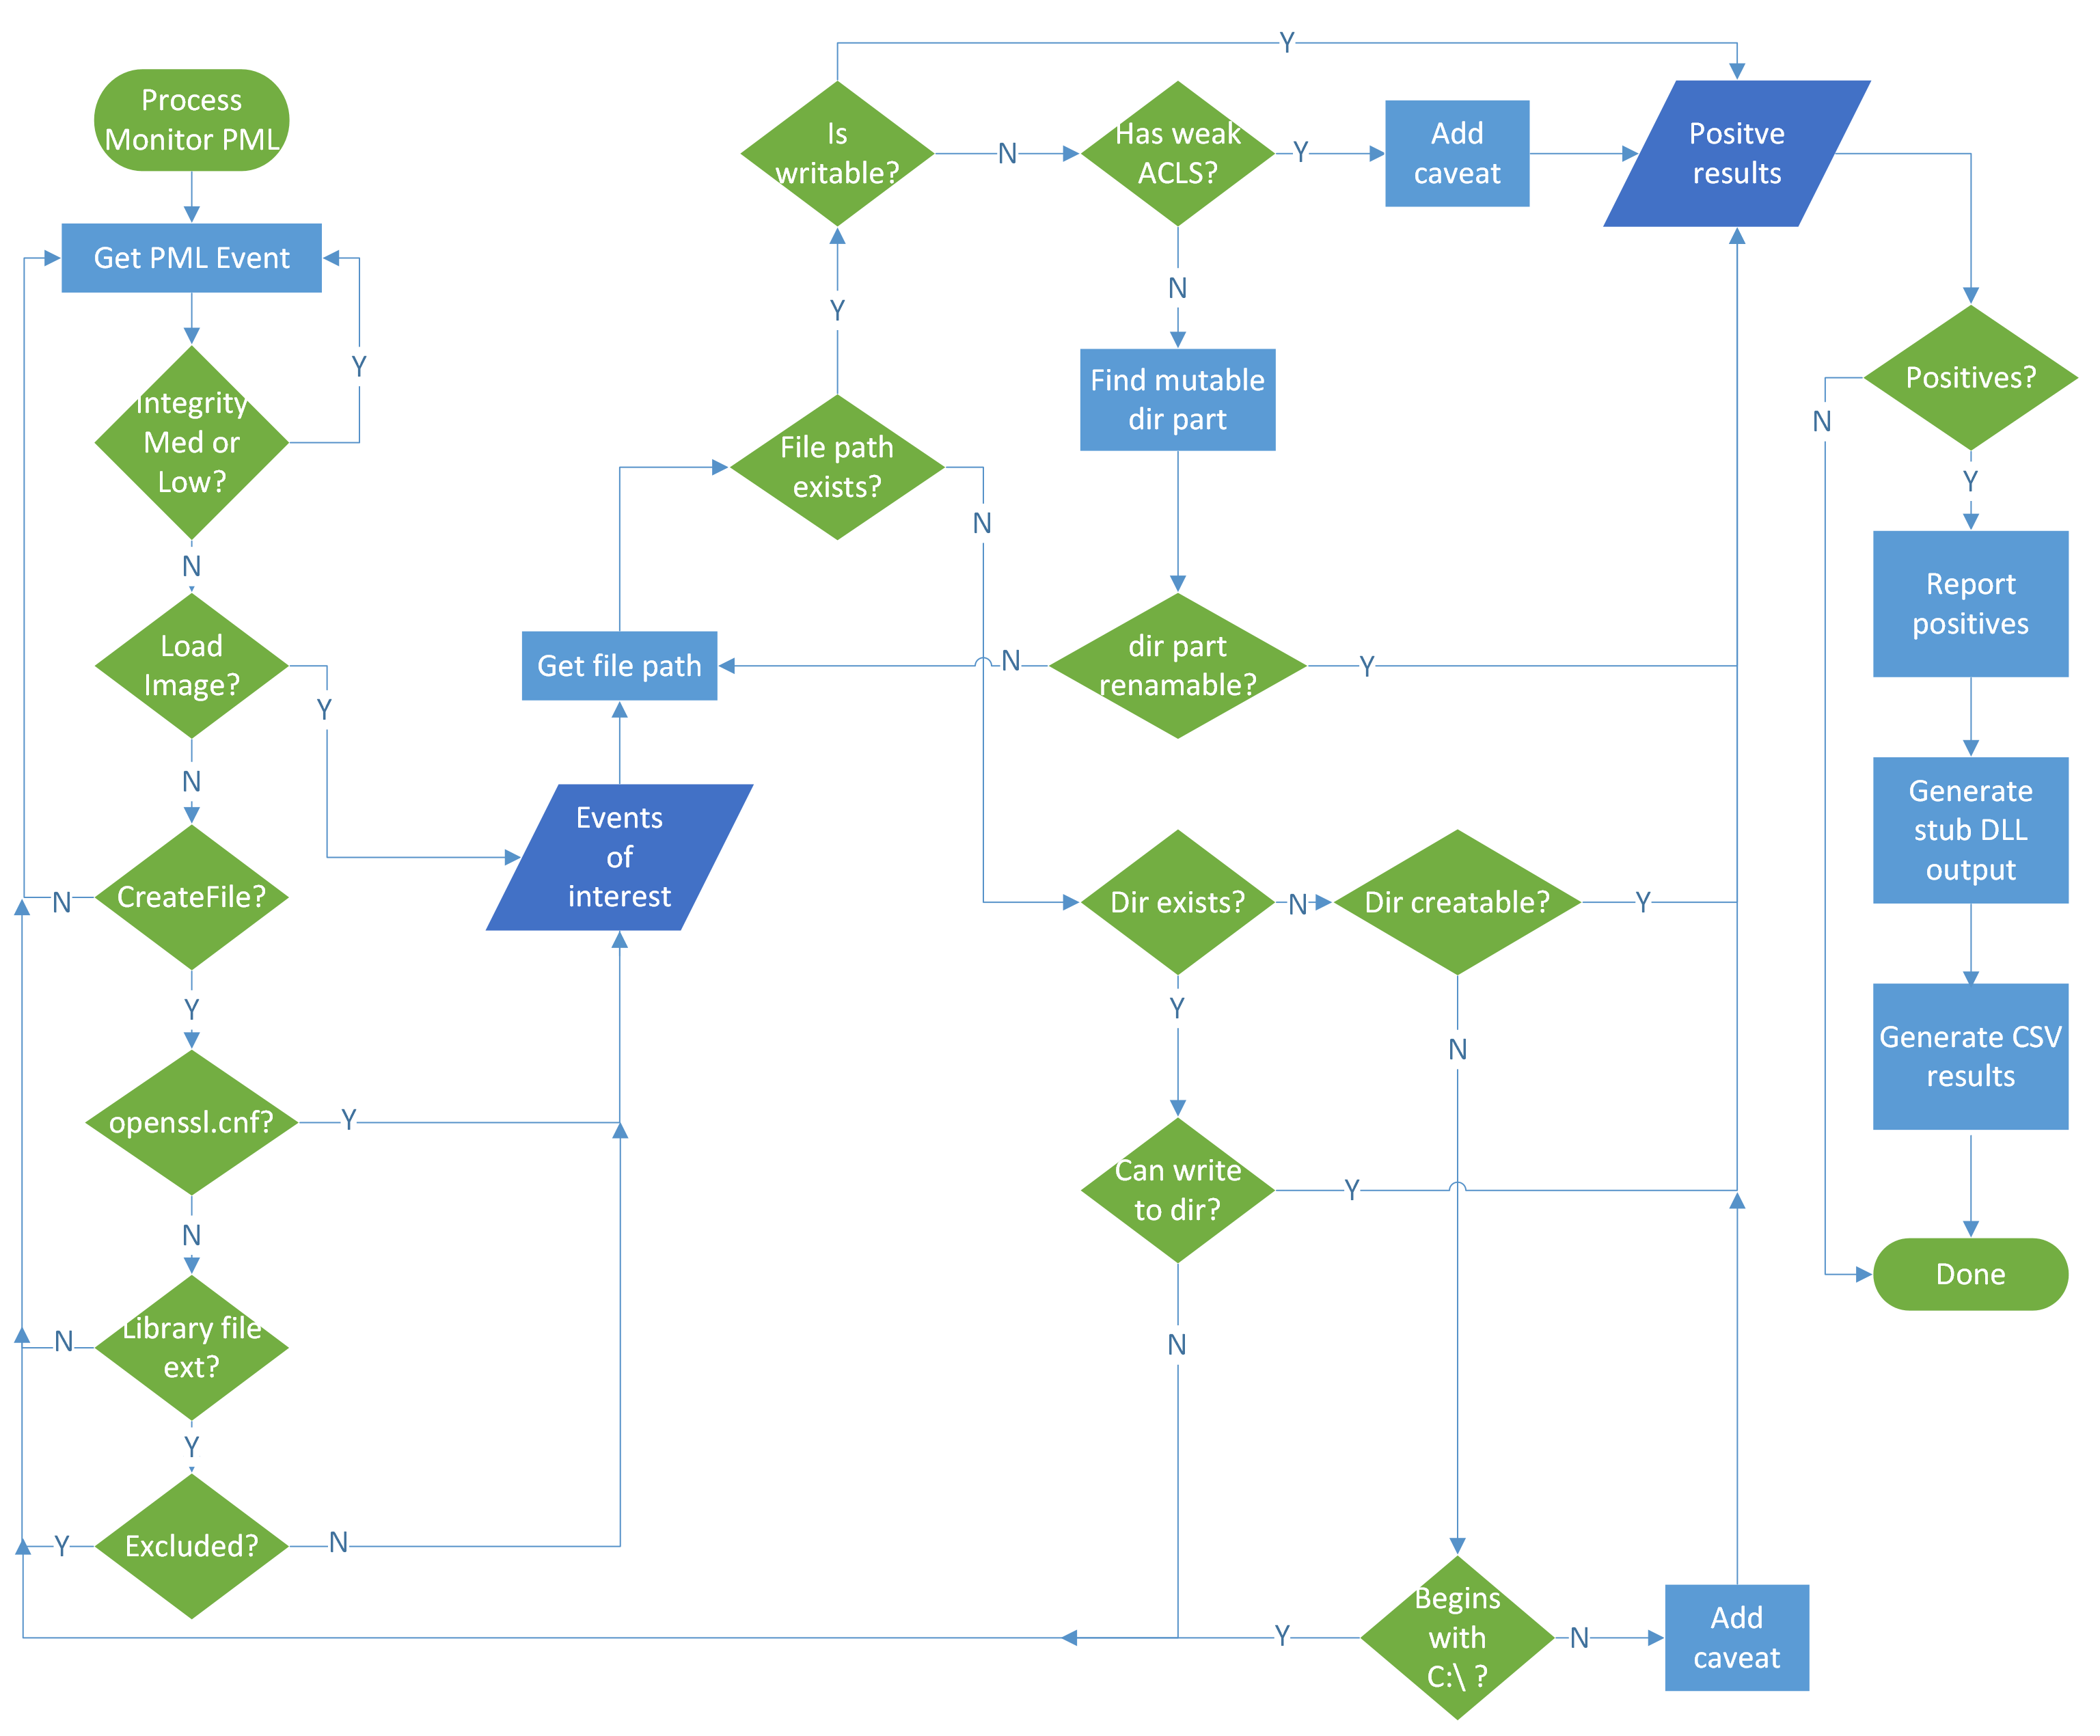
Windows权限提升发现工具,解析进程监视器启动日志以识别DLL劫持、弱ACL及其他提权路径,并自动生成代理DLL源代码。
 revng/revng
基于 LLVM 和 QEMU 构建的开源二进制分析框架与反编译器,可将二进制文件提升为可读的中间表示,用于逆向工程。
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 radareorg/radare2
类 UNIX 逆向工程框架与命令行工具集
 horsicq/detect-it-easy
用于确定文件类型的程序,适用于 Windows、Linux 和 MacOS。
 erocarrera/pefile
pefile 是一个用于读取和处理 PE(可移植可执行文件)文件的 Python 模块。

 ch0pin/rdx
A native APK and DEX decompiler written in Rust





