#1

 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 yeasen-z/leakgauge
通过训练基于对数概率的轻量级行为探针来检测 LLM 上下文泄露攻击,并提供 vLLM 离线/服务器检测管线。
 mthamil107/db_audit_research
Self-Defeating Audits:可复现的实验室环境,展示低权限 PostgreSQL 角色如何可逆地致盲基于触发器的审计器并污染归因(PG14/16),附带防御对策。使用合成数据;引用了 CVE-2018-1058 原语。
 cenobyte-vincit/xspawn
通过 launchd 的私有 XPC 接口生成 macOS 程序,而无需 exec 它们,使 EDR 将 launchd 记录为父进程。支持一次性 (one-shot)、KeepAlive 和基于 plist 的任务。
 imabee101/cve-2023-44487
用于 HTTP/2 Rapid Reset (CVE-2023-44487) 的 PoC 脚本,该脚本发送精心构造的 HTTP/2 数据流,以在易受攻击的服务器、反向代理和负载均衡器上触发拒绝服务条件。
 camillegr/cve-2026-73292
针对 CVE-2026-73292 的概念验证漏洞利用程序:对 Semaphore UI 密码更改端点发起 CSRF 攻击,提供一个恶意页面,可静默重置已认证用户的密码。
 lxxexxbxx/cve-2026-44578
Proof-of-concept exploit for CVE-2026-44578 that reproduces the vulnerable condition, enabling security researchers to validate affected systems and…
 gmh5225/awesome-ai-security
A curated list of AI Security materials and resources for Pentesters, Bug Hunters, and Security Researchers.
 loosehose/dutchoven
Application-scoped Windows network brownouts in native C and BOF form
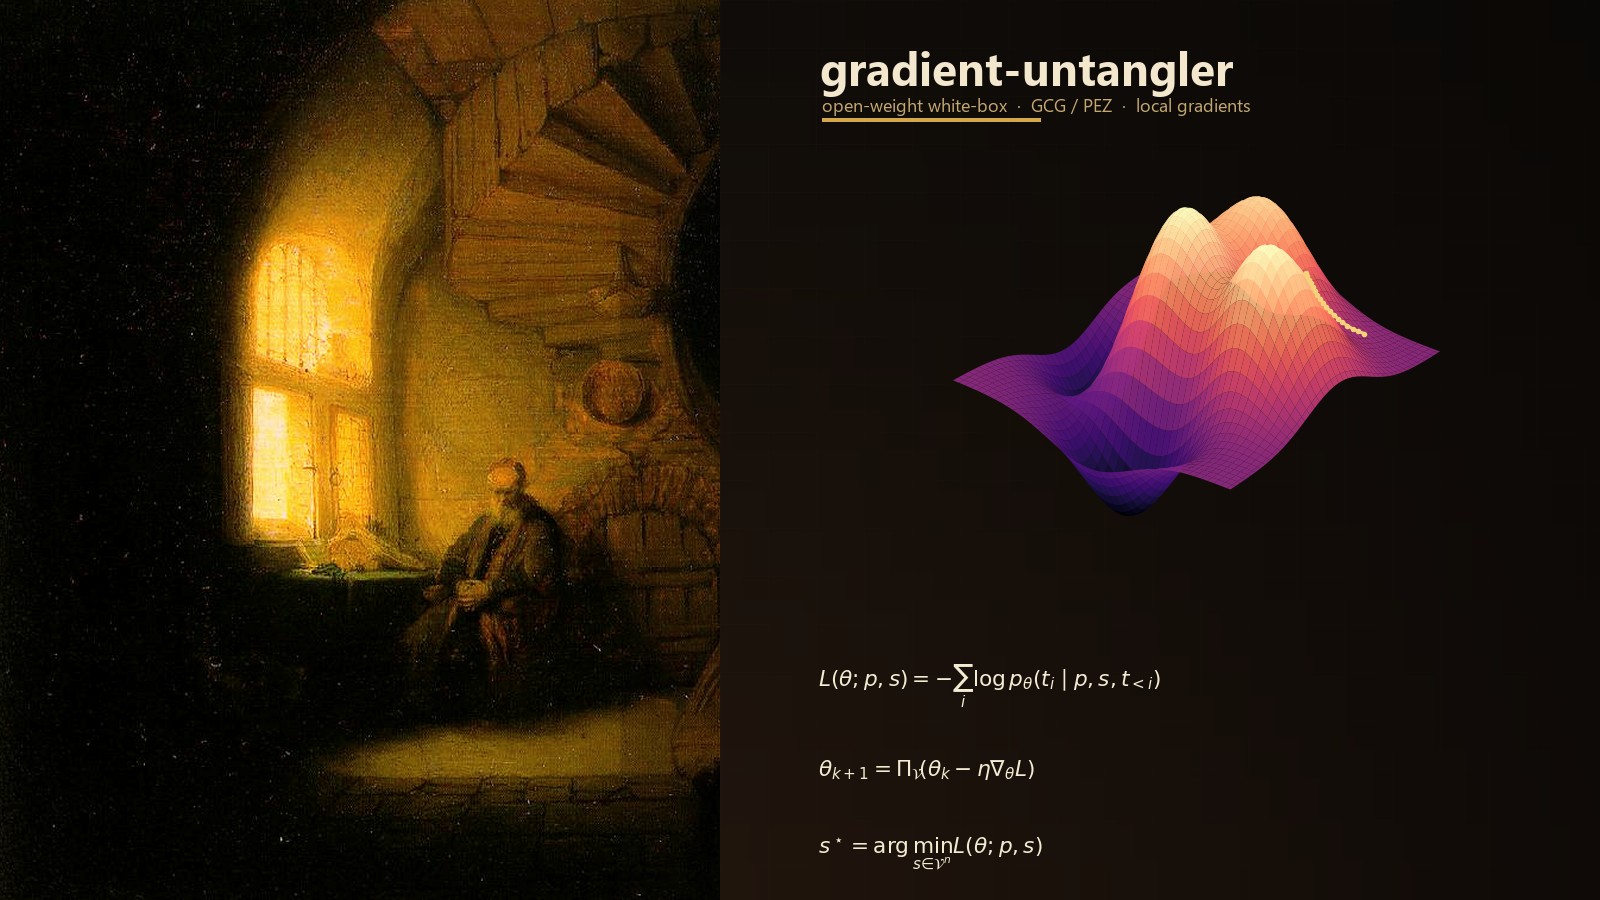
 wattocyber/gradient-untangler
Local white-box gradient attacks for open-weight LLMs: GCG/PEZ suffix search, layer saliency, weight snapshots, and rank-1 suffix-to-delta fitting…
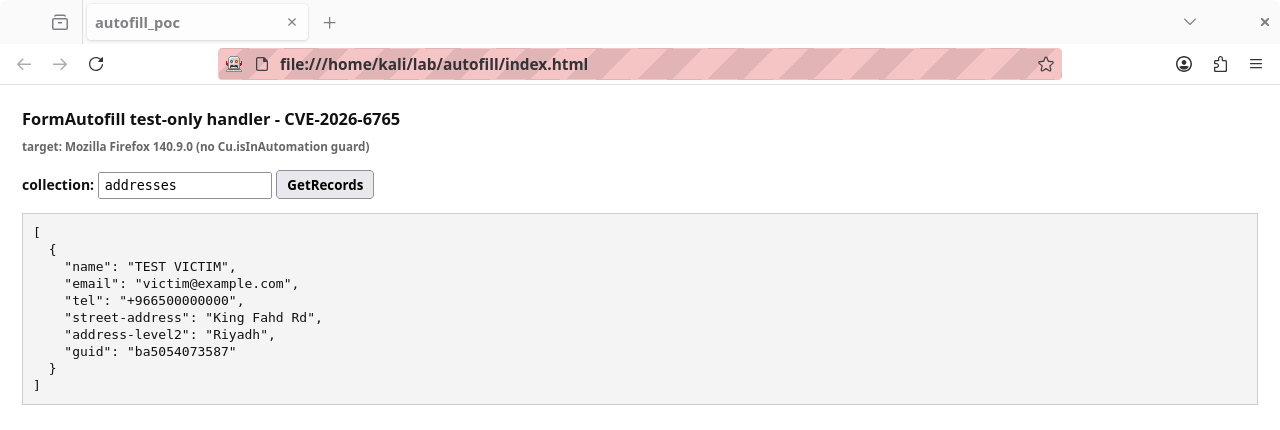 defineid/skeletonkey
CVE-2026-6765, Test only FormAutofill handlers exposed in Firefox
 aloshdenny/claude-awm
Evades LLM text watermarks by injecting Unicode variation selectors; includes the SynthID generator, mean-g detector, normalization defenses, and…
 rakib-nyc/nullorigin
仅用于研究的AI水印鲁棒性工具包:本地反向代理剥离C2PA/EXIF/XMP、Unicode、图像/音频隐写及OOXML/PDF元数据,并扫描Trojan Source。
 gmh5225/antidebug-antivm
用于检测虚拟化环境或潜在调试的不同方法
 xrazymee/ragsieve
Self-referenced local contrast for knowledge-poison detection in retrieval-augmented generation
 guillaumemeyer/watermarks-remover
一个隐私优先的应用,可从您拥有的内容中去除AI水印。
 hunt-benito/the-sanitizer-is-the-weapon-cve-2026-68749-cve-2026-68750-quadratic-dos-in-elixir-html-sanitize-ex
PoC,演示通过精心构造的 HTML 对 Elixir html_sanitize_ex 造成二次方 DoS;包含计时基准、远程利用 curl,以及针对已修补版本的验证。