Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
Log Analysis — 도구 — 3페이지 | Kitploit

도구

전체Android SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
최신관련성인기최근 업데이트
602 결과
Malcolm preview

Malcolm

GitHubcisagov/malcolm

Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…

packet-sniffing-analysisids-ips-evasionnetwork-forensics+9
2.5k

9일 전
Blue-Team-Notes preview

Blue-Team-Notes

GitHubpurp1ew0lf/blue-team-notes

블루 팀을 빼놓고 갈 거라고 생각하지 않았겠죠?

memory-forensicsnetwork-forensicsmalware-analysis+5
1.8k28일 전
Dshell preview

Dshell

GitHubusarmyresearchlab/dshell

Dshell은 네트워크 포렌식 분석 프레임워크입니다.

packet-sniffing-analysisnetwork-forensicsforensics+3
5.5k2년 전
plaso preview

plaso

GitHublog2timeline/plaso

디지털 포렌식 엔진으로, 로그, 파일 및 시스템 아티팩트를 파싱하여 슈퍼 타임라인을 구축하고, 조사 시 시간순 이벤트 상관관계를 지원합니다.

disk-forensicsioc-managementforensics+5
2.2k1일 전
LogonTracer preview

LogonTracer

GitHubjpcertcc/logontracer

Windows 이벤트 로그를 시각화하고 분석하여 악성 Windows 로그온을 조사합니다.
digital-forensicsthreat-intelligenceincident-response+2
3.2k2개월 전
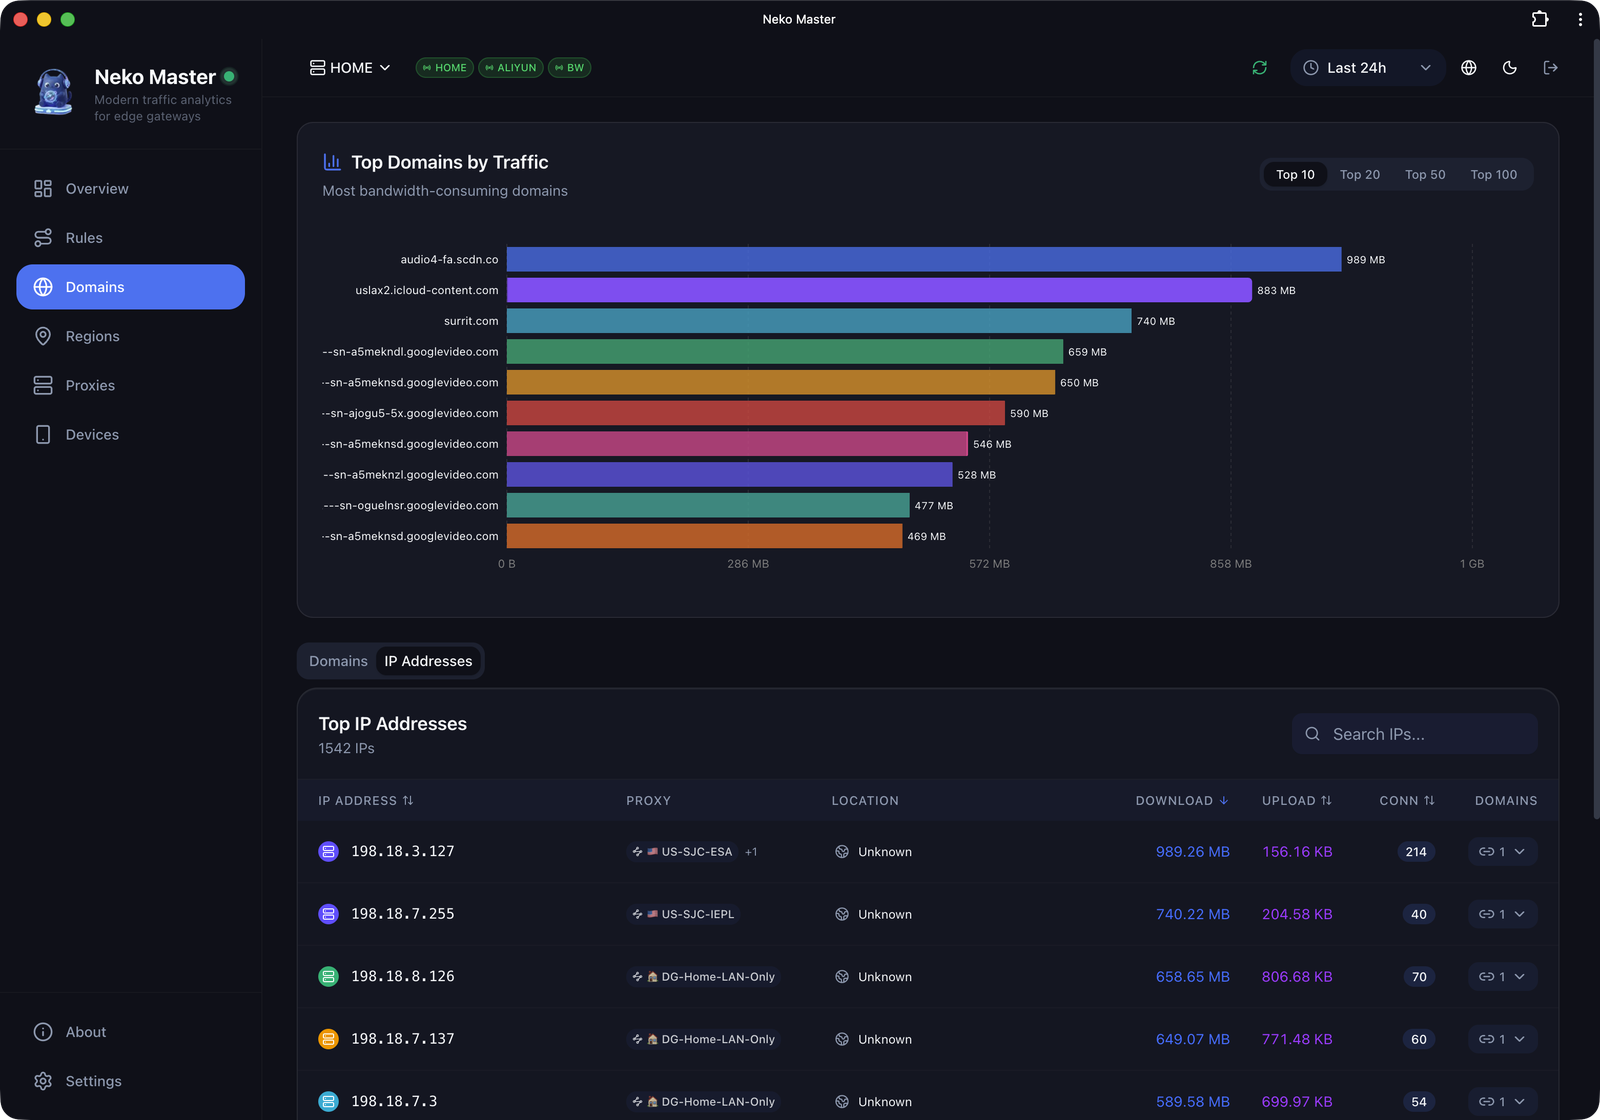
neko-master preview

neko-master

GitHubforu17/neko-master

네트워크 트래픽 시각화 및 분석을 위한 현대적이고 세련된 대시보드입니다.

network-mappinginformation-gatheringnetwork-security+3
4.2k11일 전
DeTTECT preview

DeTTECT

GitHubrabobank-cdc/dettect

전술, 기법 및 전투 위협 탐지

defensive-toolsscada-ics-securitymobile-security+4
2.3k2일 전
OSXAuditor preview

OSXAuditor

GitHubjipegit/osxauditor

OS X Auditor는 무료 Mac OS X 컴퓨터 포렌식 도구입니다.

disk-forensicsmemory-forensicsforensics+4
3.1k6년 전
AiSOC preview

AiSOC

GitHubbeenuar/aisoc

Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…

defensive-toolsthreat-intelligencemachine-learning+5
1.8k4시간 30분 전
EVTX-ATTACK-SAMPLES preview

EVTX-ATTACK-SAMPLES

GitHubsbousseaden/evtx-attack-samples

Windows EVTX 공격 샘플의 선별된 컬렉션으로, MITRE ATT&CK 기법에 매핑되어 있으며 탐지 스크립트 테스트, DFIR 교육, 위협 헌팅을 위해 설계되었습니다.

digital-forensicsthreat-intelligenceeducation+2
2.6k3년 전
opencanary preview

opencanary

GitHubthinkst/opencanary

일반적인 네트워크 서비스를 에뮬레이션하여 침해 이후의 공격자 활동을 탐지하는 경량 허니팟으로, 확장 가능한 프로토콜 모듈과 구성 가능한 알림 기능을 제공합니다.

defensive-toolsnetwork-securitythreat-intelligence+3
3.1k1개월 전
netwatch preview

netwatch

GitHubmatthart1983/netwatch

Real-time network diagnostics in your terminal. One command, zero config, instant visibility.

defensive-toolspacket-sniffing-analysisencryption-decryption-tools+8
2.3k6시간 47분 전
msticpy preview

msticpy

GitHubmicrosoft/msticpy

Microsoft 위협 인텔리전스 보안 도구

ioc-managementosintinformation-gathering+6
2.0k6일 전
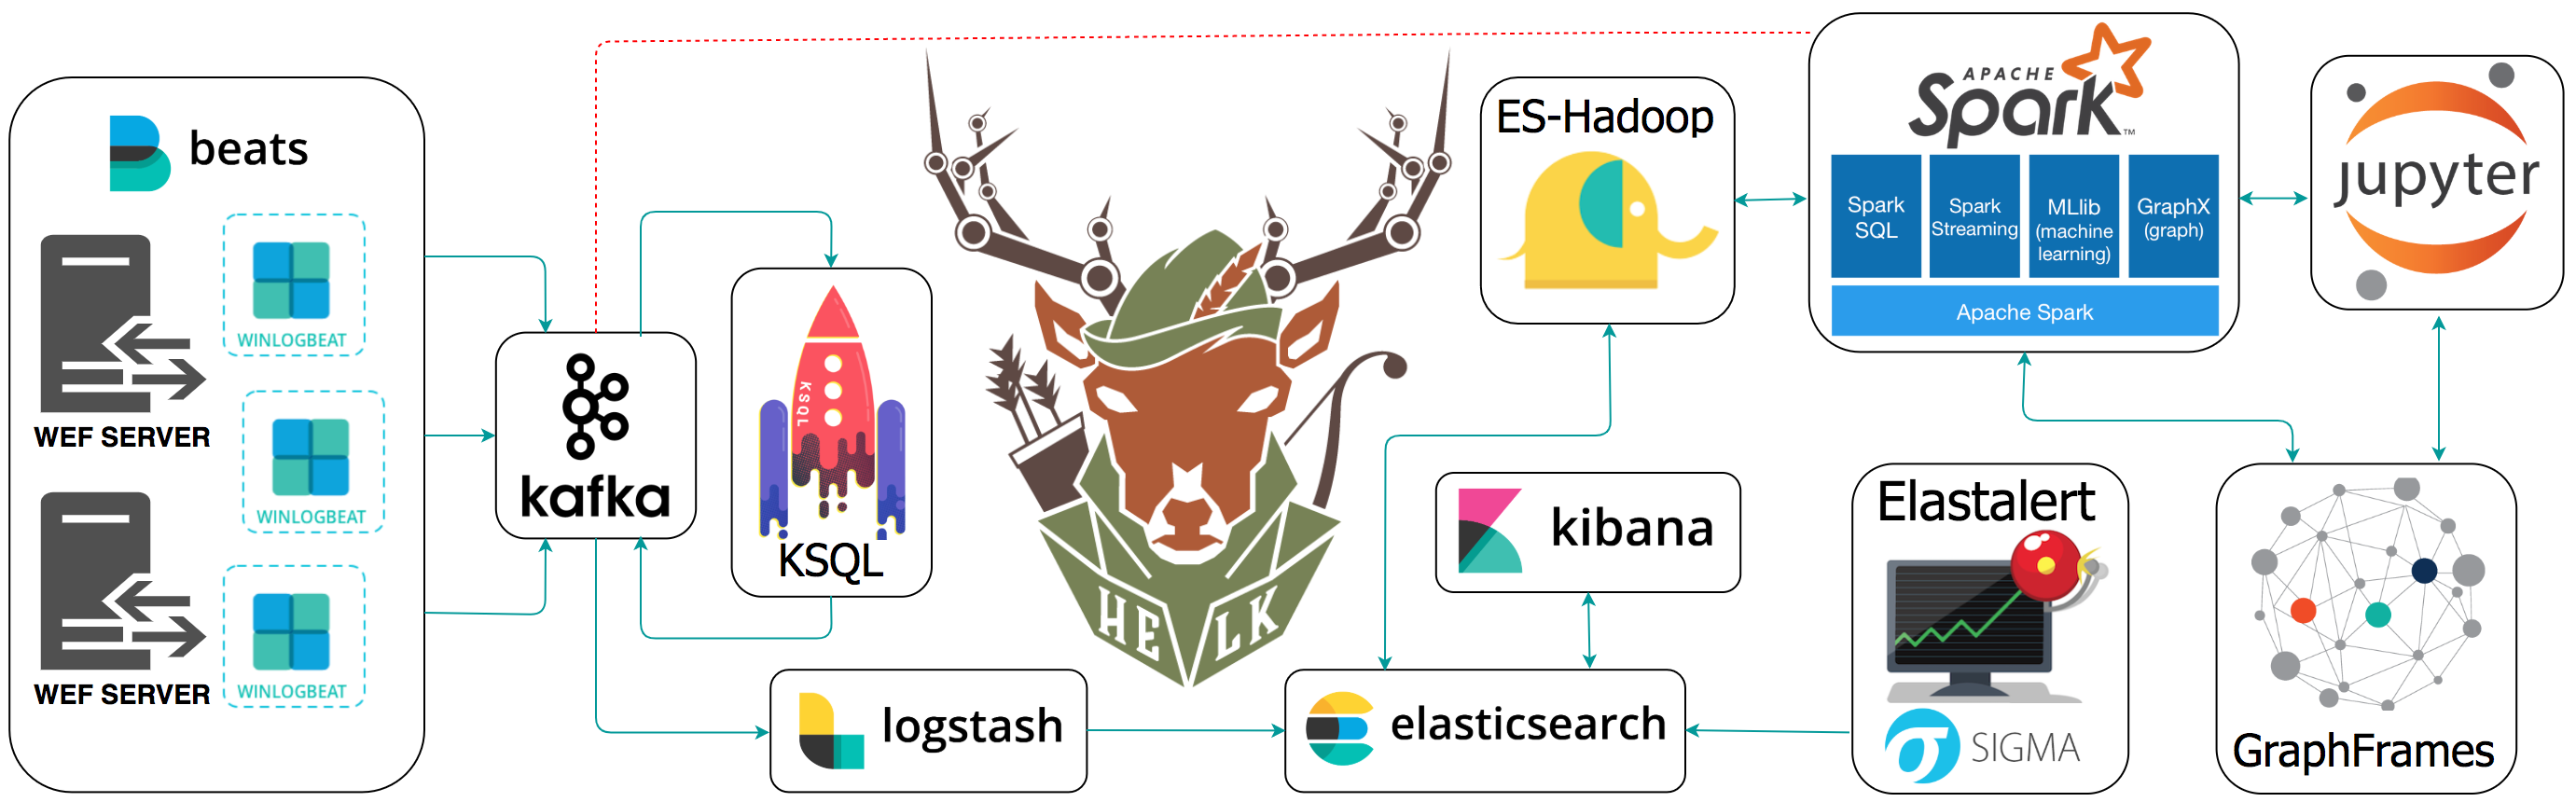
HELK preview

HELK

GitHubcyb3rward0g/helk

헌팅 ELK

threat-feeds-aggregatorsthreat-intelligencemachine-learning+3
3.9k5년 전
DeepBlueCLI preview

DeepBlueCLI

GitHubsans-blue-team/deepbluecli

PowerShell 기반 위협 헌팅 도구로, Windows 이벤트 로그를 분석하여 자격 증명 공격, 난독화된 명령, 서비스 조작, Mimikatz 사용 등 악성 활동을 탐지합니다.

malware-analysisdigital-forensicsintrusion-detection+2
2.4k3년 전
KapeFiles preview

KapeFiles

GitHubericzimmerman/kapefiles

이 저장소는 KAPE에서 사용할 수 있도록 커뮤니티에서 제작한 Targets 및 Modules를 모아두는 공간입니다.
disk-forensicsforensicsdigital-forensics+2
8642일 전
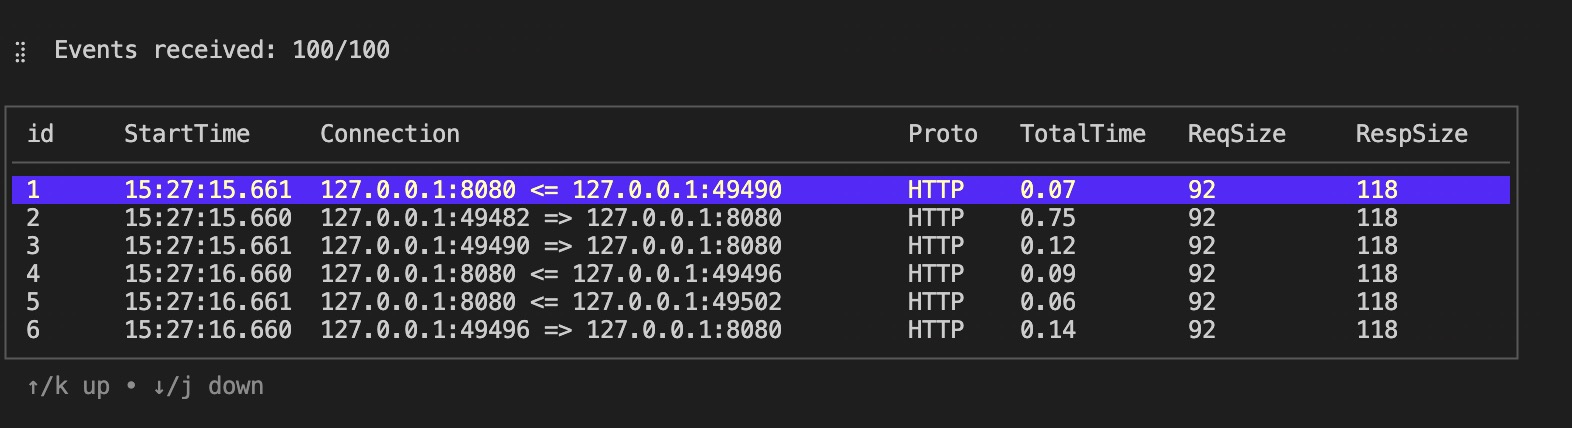
kyanos preview

kyanos

GitHubhengyoush/kyanos

Kyanos는 eBPF를 사용하는 네트워크 분석 도구입니다. 패킷이 커널에서 보내는 시간을 시각화하고 요청/응답을 캡처하여 문제 해결을 더 효율적으로 만듭니다.
packet-sniffing-analysisdynamic-analysis-sandboxingnetwork-mapping+3
5.1k4개월 전
EDR-Telemetry preview

EDR-Telemetry

GitHubtsale/edr-telemetry

이 프로젝트는 다양한 EDR 제품의 텔레메트리를 비교하고 평가하는 것을 목표로 합니다.

defensive-toolseducationcurated-resources+1
2.0k23일 전
이전1234…34다음