Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
Forensics — 16페이지 | Kitploit
카테고리

Forensics

Digital forensics, evidence collection, timeline analysis, and incident investigation tools.

Kitploit 추천

추천 도구

10 선택됨
autopsy preview#1

autopsy

GitHubsleuthkit/autopsy
3.3k5개월 전
sleuthkit preview#2

sleuthkit

GitHubsleuthkit/sleuthkit
3.2k4일 전
volatility3 preview#3

volatility3

GitHubvolatilityfoundation/volatility3
4.3k12일 전
plaso preview#4

plaso

GitHublog2timeline/plaso
2.2k7시간 20분 전
bulk_extractor preview#5

bulk_extractor

GitHubsimsong/bulk_extractor
1.4k12일 전
velociraptor preview#6

velociraptor

GitHubvelocidex/velociraptor
4.2k22시간 54분 전
timesketch preview#7

timesketch

GitHubgoogle/timesketch
3.4k1일 전
mvt preview#8

mvt

GitHubmvt-project/mvt
15.5k4일 전
androidqf preview#9

androidqf

GitHubmvt-project/androidqf
2304일 전
avml preview#10

avml

GitHubmicrosoft/avml
1.1k21시간 52분 전
최신관련성인기최근 업데이트
932 결과
MESH preview

MESH

GitHubbarghest-ngo/mesh

암호화된 P2P 메시 VPN으로 원격 모바일 포렌식을 지원하며, 무선 ADB 및 libimobiledevice 수집, 네트워크 모니터링, NAT 및 방화벽을 통한 침입 탐지를 가능하게 합니다.
android-securitypacket-sniffing-analysisencryption-decryption-tools+8
1921일 전
WDExtract preview

WDExtract

GitHubhfiref0x/wdextract

vdm 파일에서 Windows Defender 데이터베이스를 추출하고 압축을 해제합니다
encryption-decryption-toolsreverse-engineeringforensics+2
4906개월 전
dismember preview

dismember

GitHubliamg/dismember

:knife: 메모리에서 비밀 등을 스캔합니다. 아마도 언젠가는 완전한 /proc 툴킷이 될 것입니다.
memory-forensicsforensicsinformation-gathering+2
6744년 전
creddump7 preview

creddump7

GitHubciscocxsecurity/creddump7

오프라인 Windows 자격 증명 추출기로, 시스템 상호 작용 없이 레지스트리 하이브에서 LM/NT 해시, 캐시된 도메인 암호 및 LSA 비밀을 덤프합니다.
password-crackingforensics
4106년 전
lmg preview

lmg

GitHubhalpomeranz/lmg

Linux 메모리 캡처 및 분석을 자동화하는 스크립트

memory-forensicsforensicsdigital-forensics+1
2756년 전
ALFA preview

ALFA

GitHubinvictus-ir/alfa

Google Workspace 감사 로그를 위한 자동 포렌식 분석 도구입니다. 모든 로그 유형을 수집하고 이벤트를 MITRE ATT&CK Cloud Framework에 매핑하며 통계적 점수화를 통해 킬 체인을 식별합니다.
forensicsdigital-forensicscloud-security+3
1831개월 전
OpenPetya preview

OpenPetya

GitHubiss4cf0ng/openpetya

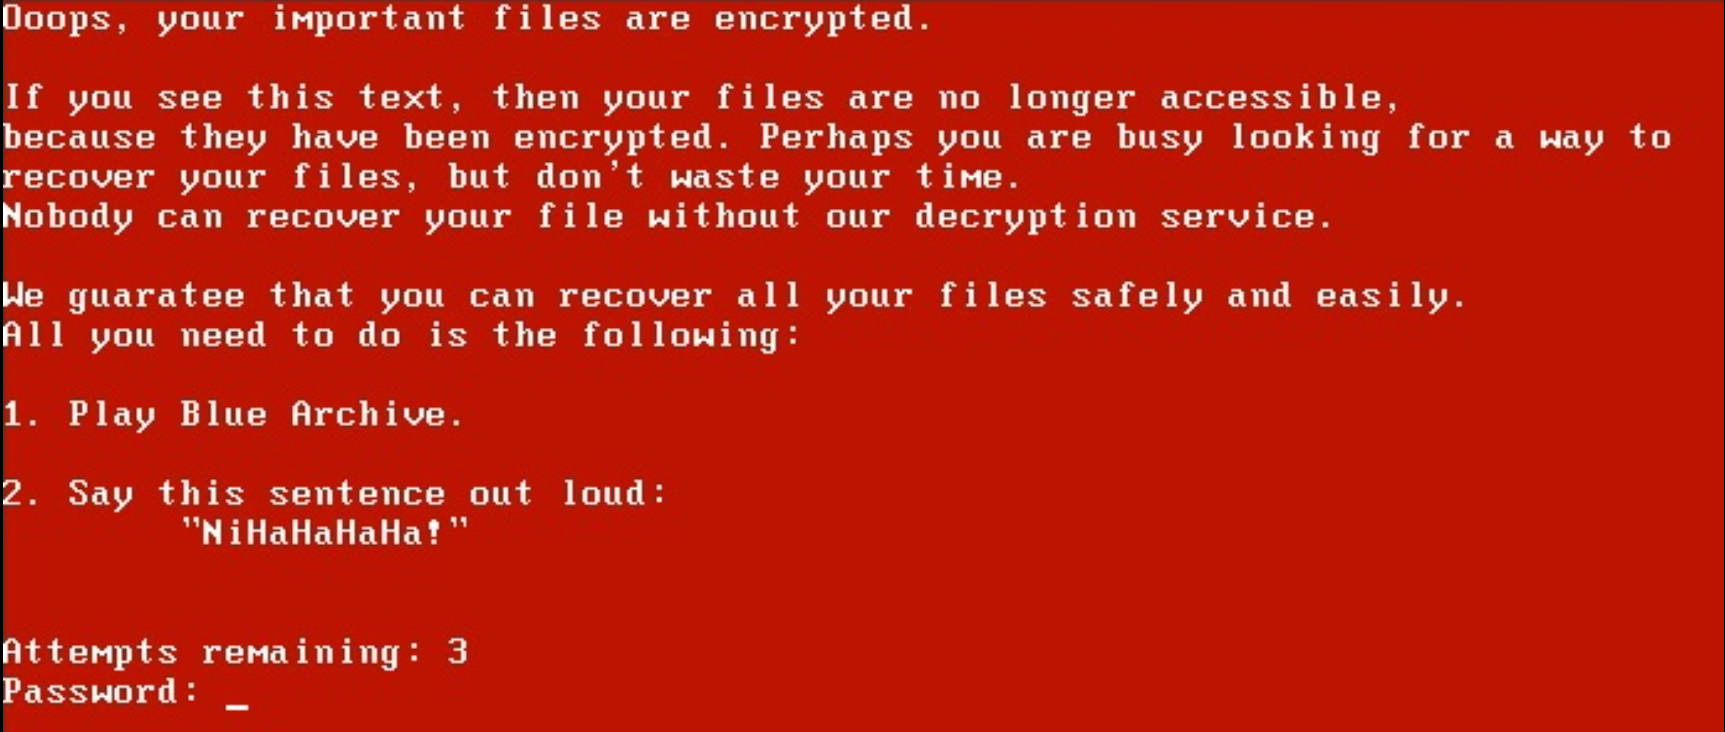
부트킷 및 UEFI 부트 애플리케이션의 개념 증명(PoC)으로, Petya 랜섬웨어에서 영감을 받았으며 Assembly, C, C++로 작성되었습니다.
encryption-decryption-toolsreverse-engineeringforensics+4
2601개월 전
rastrea2r preview

rastrea2r

GitHubrastrea2r/rastrea2r

열정과 스타일로 IOCs를 수집 및 사냥하기

ioc-managementreconnaissancememory-forensics+6
23812일 전
SuperMem preview

SuperMem

GitHubcrowdstrike/supermem

트라이지 유형에 따라 Windows 메모리 이미지를 처리하도록 개발된 Python 스크립트입니다.

memory-forensicsforensicsmalware-analysis+2
2674년 전
libvhdi preview

libvhdi

GitHublibyal/libvhdi

Library and tools to access the Virtual Hard Disk (VHD) image format 가상 하드 디스크(VHD) 이미지 형식에 접근하기 위한 라이브러리 및 도구
disk-forensicsforensicsdata-recovery+1
1491개월 전
cosa-nostra preview

cosa-nostra

GitHubjoxeankoret/cosa-nostra

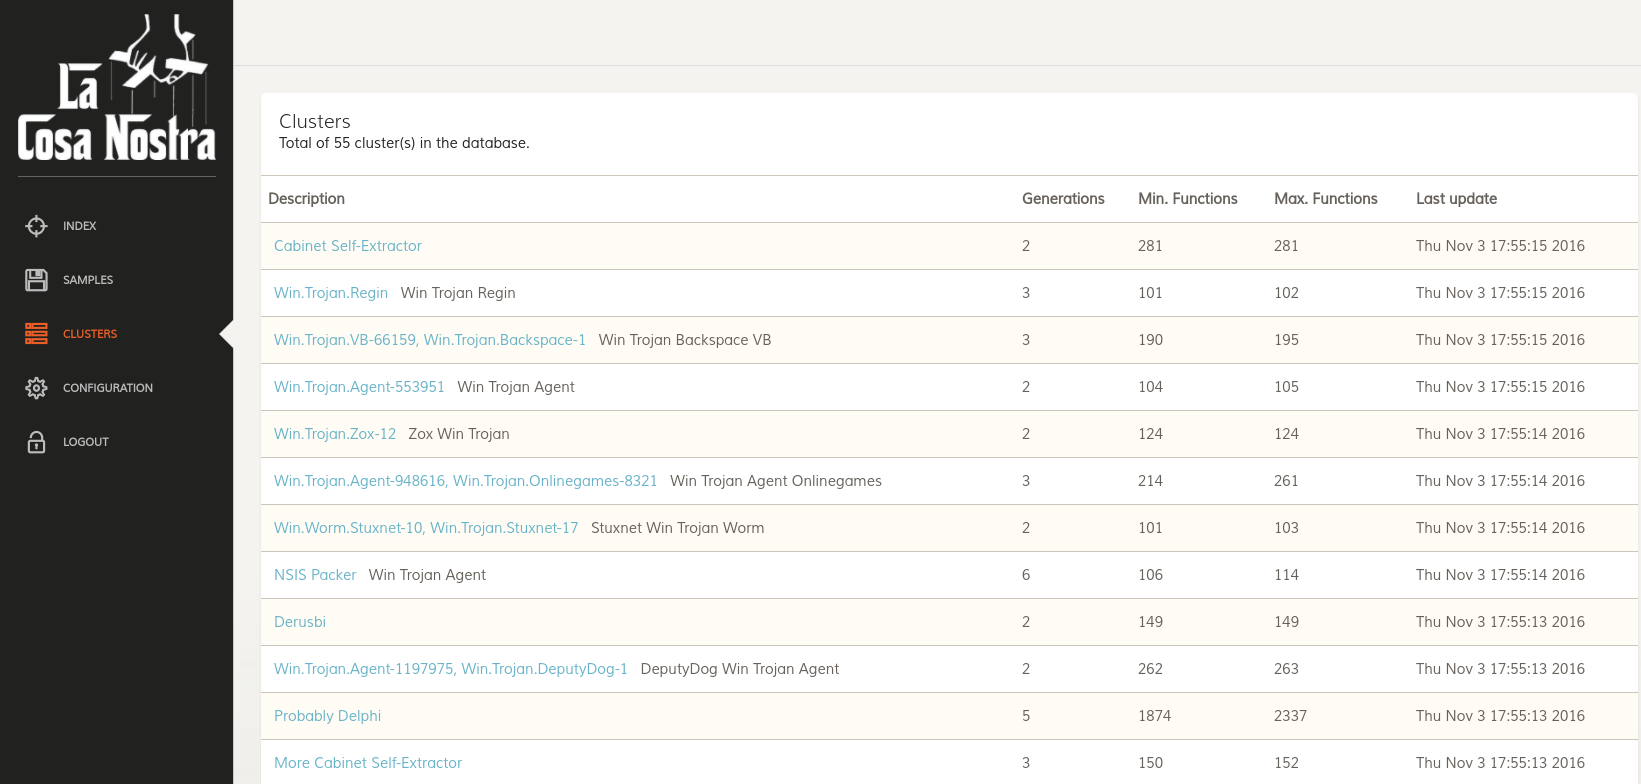
Cosa Nostra, 그래프 기반 악성코드 클러스터링을 위한 FOSS 툴킷.

static-analysisreverse-engineeringforensics+3
2312년 전
ADEL preview

ADEL

GitHubmspreitz/adel

안드로이드 데이터 추출기 라이트

android-securityforensicsmobile-forensics+4
13011년 전
iOSRestrictionBruteForce preview

iOSRestrictionBruteForce

GitHubthehappydinoa/iosrestrictionbruteforce

Python으로 iOS 제한 비밀번호 크랙하기
ios-securitypassword-attacksforensics+1
3772년 전
TEx preview

TEx

GitHubguibacellar/tex

연구자 및 조사관을 위한 텔레그램 인텔리전스 수집 도구입니다. OCR, Elasticsearch 통합, 위협 모니터링을 위한 자동 알림 기능을 갖추고 그룹, 메시지, 미디어 및 사용자 데이터를 스크래핑합니다.

osintforensicsinformation-gathering+2
3752년 전
distro preview

distro

GitHubremnux/distro

악성코드 분석, 리버스 엔지니어링 및 디지털 포렌식에 특화된 Linux 배포판을 위한 보조 파일과 Debian 패키지 소스를 제공합니다.
dynamic-analysis-sandboxingreverse-engineeringforensics+5
11910일 전
DFIR-O365RC preview

DFIR-O365RC

GitHubanssi-fr/dfir-o365rc

Office 365 및 Azure 로그 수집을 위한 PowerShell 모듈
forensicsdigital-forensicscloud-security+2
2821년 전
iMonitorSDK preview

iMonitorSDK

GitHubwecooperate/imonitorsdk

세계에서 가장 강력한 시스템 활동 모니터 엔진 · 강력한 기능의 터미널 동작 수집 방어 개발 키트 ~ EDR, 제로 트러스트, 데이터 보안, 감사 통제 등 터미널 보안 소프트웨어가 제품 기능을 신속하게 구현할 수 있도록 지원하며, 하위 드라이버의…
defensive-toolsprivilege-escalationids-ips-evasion+5
3791년 전
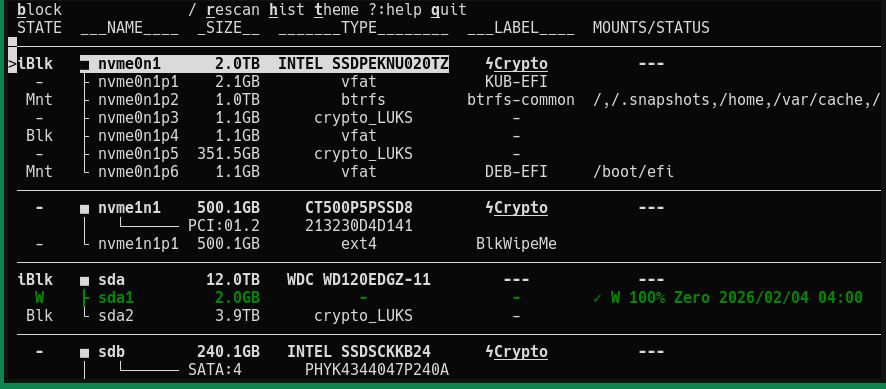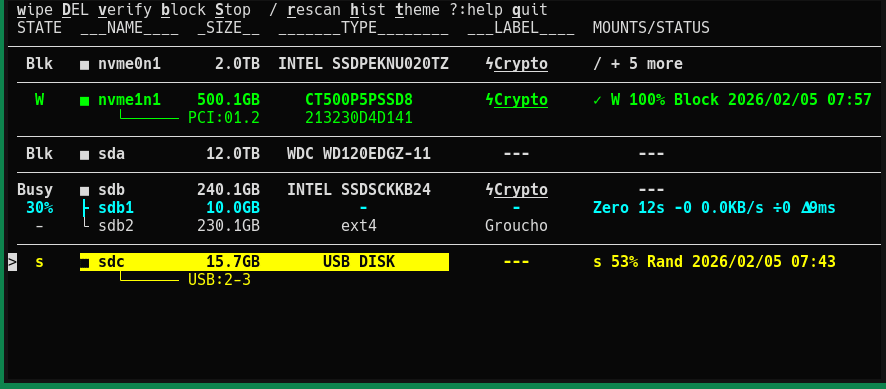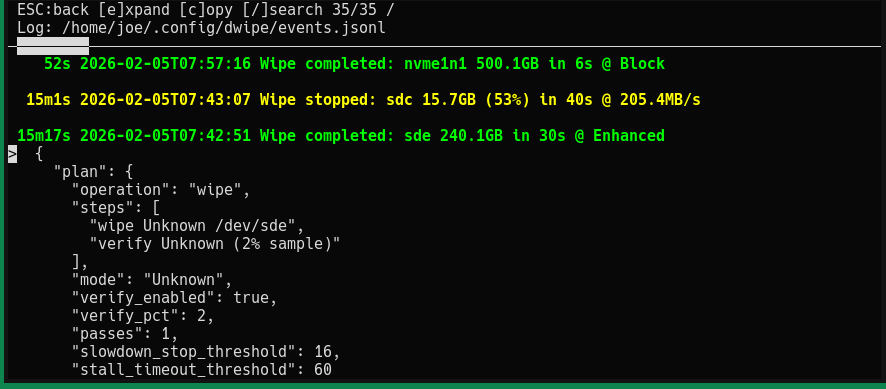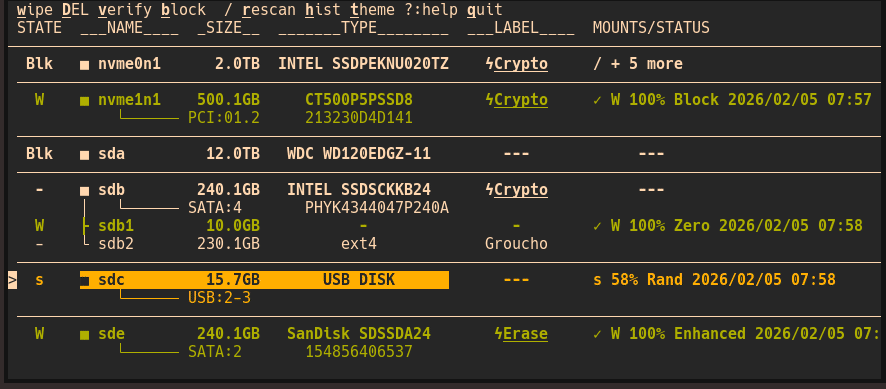
dwipe preview

dwipe

GitHubjoedefen/dwipe

Linux 기기와 파티션을 안전하고 효율적으로 삭제하는 도구

general-purpose-utilitiesencryption-decryption-toolsforensics+3
1649일 전
이전1…151617…52다음