
 #1
LLM security, prompt injection, model extraction, adversarial AI, and AI red teaming tools.
Kitploit 추천

 provos/ironcurtain
자율 AI 에이전트를 위한 보안* 런타임. 일반 영어로 작성된 헌법에서 정책을 수립합니다. (*https://ironcurtain.dev)
 meridianlabs-ai/inspect_petri
정렬 가설을 신속하게 탐색할 수 있는 정렬 감사 에이전트
 microsoft/pyrit
생성형 AI 시스템 레드팀을 위한 오픈소스 프레임워크: 공격 프롬프트 자동화, 모델 응답 점수화, 보안 및 안전 위험을 식별하기 위한 동작 감사.
 goochbeater/spiritual-spell-red-teaming
다양한 LLM, 주로 Claude를 탈옥(jailbreak)하기 위한 저장소
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
 nousresearch/hermes-agent
The agent that grows with you
 garrytan/gstack
Use Garry Tan's exact Claude Code setup: 23 opinionated tools that serve as CEO, Designer, Eng Manager, Release Manager, Doc Engineer, and QA
 google-github-actions/run-gemini-cli
GitHub Action에서 Gemini CLI를 호출합니다.
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 gautamvarmadatla/mcpsafetywarden
MCP 서버를 감싸는 프록시 서버로, 행동 프로파일링, 보안 스캐닝, 위험 게이팅, 안전한 실행을 제공합니다. 프롬프트 인젝션, 악성 툴 메타데이터, 인수 인젝션, 소스 코드 위험, 자격 증명 노출을 탐지합니다.
 kubeshop/testkube
☸️ 에이전틱 SDLC를 위한 테스트 플랫폼
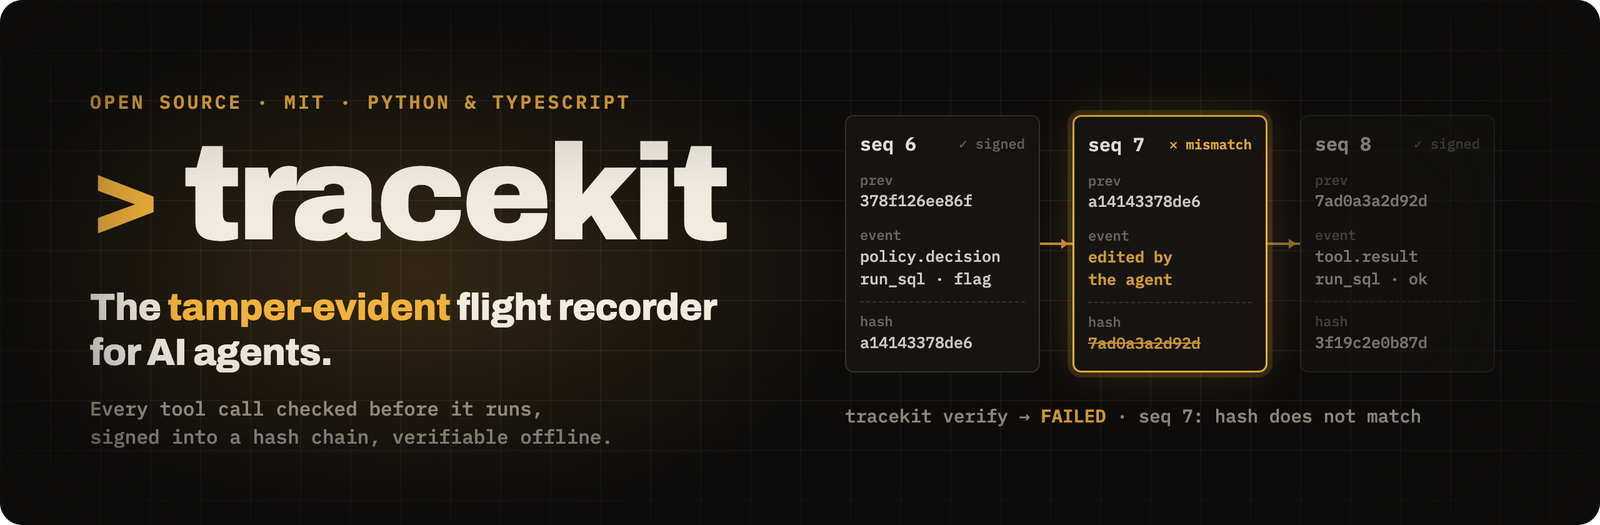 cygnux-labs/tracekit
Tamper-evident tracing, policy gates and cross-checks for AI agents: see what the agent did, and why.
 openclaw/openclaw
정말로 일을 해내는 AI. 모든 OS. 모든 플랫폼. 랍스터 방식. 🦞
 hashgraph-online/hol-guard
Open-source antivirus and firewall for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and…
 rderaison/bromure
에이전트 코딩 및 웹 브라우징을 위한 적절한 샌드박싱
 nvidia/openshell
자율 AI 에이전트를 위한 샌드박스 런타임으로, 파일시스템, 네트워크, 프로세스 제약을 강제하는 선언적 YAML 정책과 엔드포인트에 바인딩된 자격 증명 주입을 제공합니다.
 nanocoai/nanoclaw
나만의 상시 작동 AI 어시스턴트: 자체 호스팅, 오픈 소스, 경량. 각 에이전트는 선택한 하네스(Claude Code, Codex, Cursor, OpenCode)에서 내 머신의 자체 컨테이너에서 실행됩니다. Slack, WhatsApp, Telegram,…
 owasp/aisvs
AI Security Verification Standard (AISVS)는 개발자, 아키텍트, 보안 전문가가 AI 기반 애플리케이션의 보안을 검증할 수 있도록 구조화된 체크리스트를 제공하는 데 중점을 둡니다.







