Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
도구/GitHubGitHub/nvidia-nemo/guardrails
Defensive ToolsVulnerability AnalysisPrivacyMachine LearningAI SecurityAnomaly DetectionAI Security #10위
GitHubnvidia-nemo/guardrails

Guardrails

Programmable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask sensitive data.

7.5k9031726시간 19분 전Kitploit 검토 완료
공유
저장소 보기
웹사이트
요청한 언어로 콘텐츠를 사용할 수 없습니다. 영어 버전을 표시합니다.

NVIDIA NeMo Guardrails Library

License PyPI Python Tests/Linux Tests/Windows Tests/macOS Lint Documentation Total downloads Monthly downloads

Documentation · Quickstart · Use cases · Integrations · Guardrail catalog · Examples · Community · Security · Releases · Changelog

NeMo Guardrails is an open-source library for applying programmable safety and security controls to LLM and agentic applications. Agents run commands, call APIs, query your data, and read the web. Conversational applications apply input and output checks; retrieval-augmented generation (RAG) systems filter retrieved content and check answers against evidence.

You use the NeMo Guardrails library to declare what each agent may do in a policy, combining low-latency local rules with model-backed checks for jailbreaks, injected instructions, and unsafe tool calls. Your application or agent harness runs these checks and uses their results to decide whether to continue.

pip install nemoguardrails

Requires Python 3.11–3.13. Refer to the installation guide for optional packages and setup.

[!NOTE] Version 0.25.0 deprecates LLMRails, with removal planned no earlier than 0.27.0. Use Guardrails for new integrations and follow the migration guide.
What You Can Build

  • AI agents and coding assistants: Check proposed tool calls and returned results with tool rails, or connect an agent through the hooks server.
  • Conversational applications: Apply input and output checks.
  • Retrieval-augmented generation (RAG): Detect or mask sensitive data in retrieved content and check whether answers are grounded in evidence.

How It Works

  • Define your policy. Configure rails, models, and prompts in YAML. Use Python actions for custom logic.
  • Run the checks. Invoke rails at the points where your application needs a policy decision.
  • Read the result. Handle blocked or modified content before executing a tool or returning a response. You can also route generation through Guardrails.

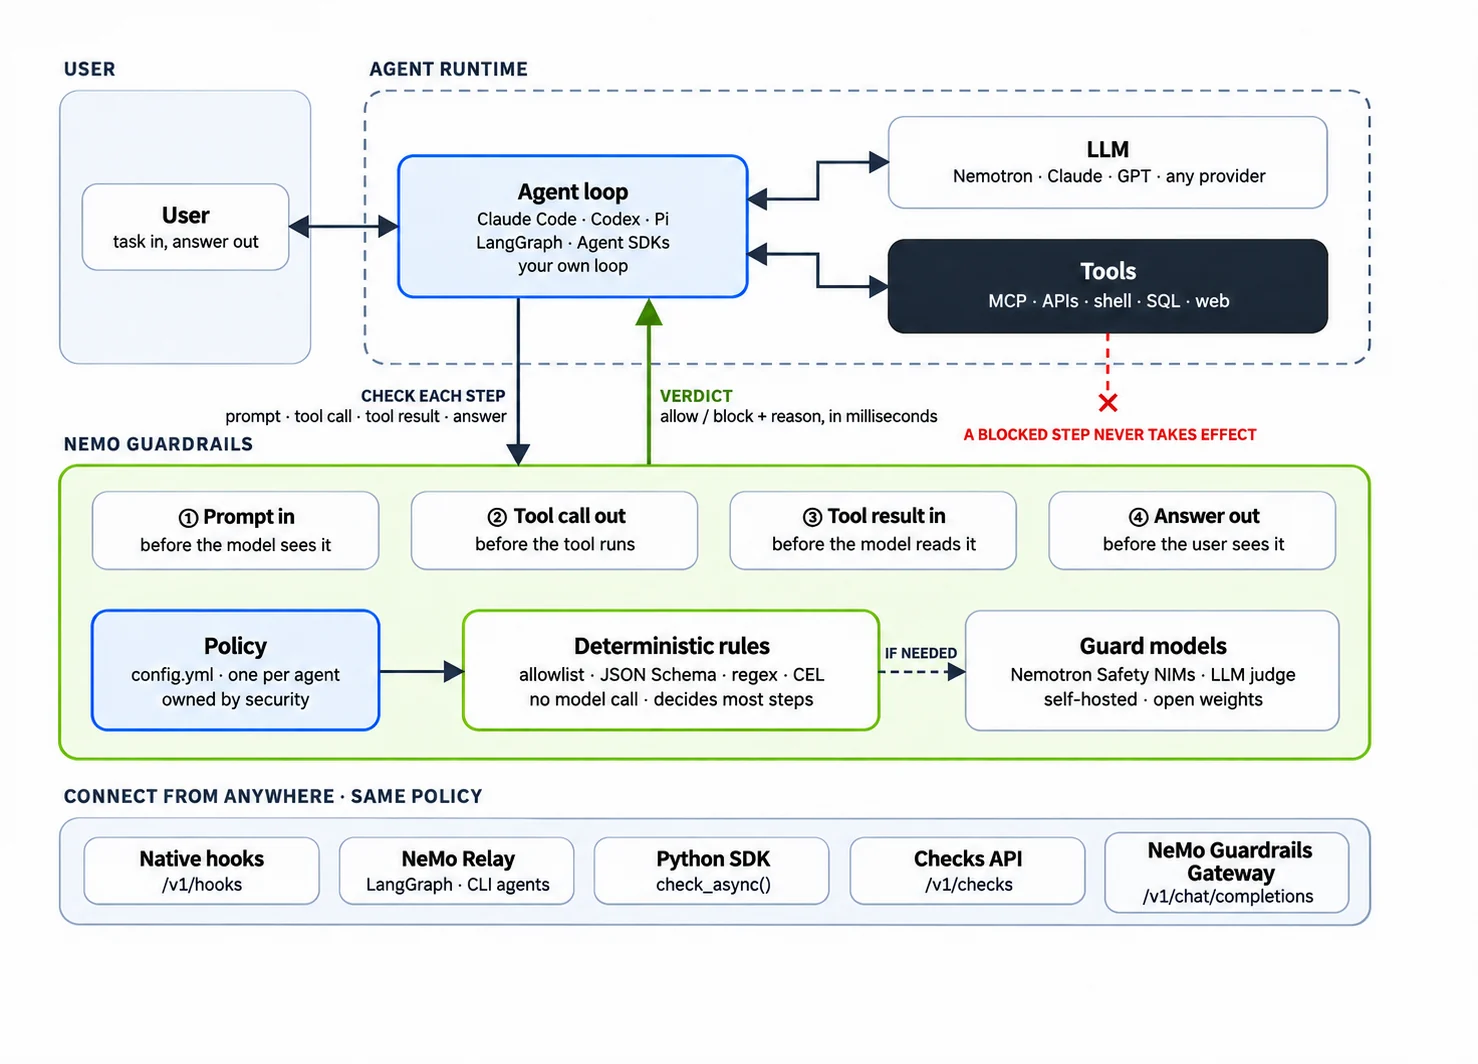
Agent runtime connected to NeMo Guardrails: configurable checks for prompts, tool calls, tool results, and answers, with policy rules, optional guard models, and integration options.

Tool-call checks run before execution, while tool-result checks run after the tool has executed. Latency depends on the configured rules, models, and services.

Integrations support different checks. Rail support varies by engine; refer to rail engine support and configuration.

Why NeMo Guardrails

  • Govern what agents do. Validate tool names and argument schemas before execution. Check tool results and apply per-tool policies before returning them to the model.
  • Keep your model and agent loop. Use checks without main-model generation to add guardrails to an existing application. Model-backed checks still call their configured model or service.
  • Compose the policy you need. Combine local regex and CEL rules with safety models and third-party checks.
  • Connect your runtime. Choose an integration for your application, shared service, or coding agent.
  • Open and yours to run. The library is Apache 2.0 licensed. Choose supported model providers and run checks with local detectors or hosted inference endpoints.

Quickstart

Check a support agent's proposed refund against a $500 limit, without a model or API key. Install the optional CEL extra for this example:

pip install "nemoguardrails[cel]"

The example validates the tool's argument schema and blocks calls over the limit. Expand it and save it as check_refund.py:

Complete Python example
import asyncio
import json

from nemoguardrails import Guardrails, RailsConfig
from nemoguardrails.rails.llm.options import RailStatus, RailType

config = RailsConfig.from_content(yaml_content="""
models: []
rails:
  tool_call:
    flows: [tool call validation]
    per_tool:
      issue_refund: [cel check tool call]
  config:
    cel:
      tool_call:
        issue_refund:
          expressions: ["args.amount > 500"]
""")

TOOLS = [{
    "type": "function",
    "function": {
        "name": "issue_refund",
        "parameters": {
            "type": "object",
            "properties": {"amount": {"type": "number", "minimum": 0}},
            "required": ["amount"],
            "additionalProperties": False,
        },
    },
}]

도구 다운로드

인기

모두 보기 →

커뮤니티에서 가장 많이 사용되는 도구를 찾아보세요.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 궁극의 OSINT 툴킷: 조사 그래프, 신뢰도 점수 산정, 별칭 패밀리, 지도, 타임라인 및 보고서. 49개 모듈, 400개 이상 사이트, API 키 불필요.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # GhostLock 원탭 실행 앱 (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM 멀티 에이전트 자율 침투 테스트 플랫폼으로, 플래너/워커 에이전트, 자산 및 탐색 그래프, MITM 트래픽 기록, 취약점 재테스트 기능을 제공합니다.

    415
  • 4

    redforge

    cybersecurity91/redforge

    브라우저 측 레드 팀 툴킷으로, 정찰, 페이로드 생성, 자격 증명 공격, 암호화, 인코딩 및 참여 보고를 위한 102개의 오프라인 도구를 제공합니다.

    343
  • 5

    antifox

    antifox-ai/antifox

    정찰, 공격 표면 탐색, 익스플로잇 검증, 증거 기반 보고서 전달을 수행하는 AI 멀티 에이전트 자율 침투 테스트 플랫폼입니다.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AI 네이티브 사이버보안을 위한 행동 체계—의도가 통제된 실행이 되고, 증거가 운영 메모리가 되며, 모든 운영이 다음 운영을 개선하는 곳.

    258

모든 도구 탐색

도구 컬렉션을 둘러보세요

모든 도구 보기 →