
 #1
脅威フィード、侵害指標(IOC)、および攻撃トレンドを収集、分析、および運用するためのツール。
Kitploit おすすめ
 kaifcodec/user-scanner
Multi-platform OSINT scanner for email and username reconnaissance across 295+ vectors. Extracts profile metadata, checks account registrations, and…
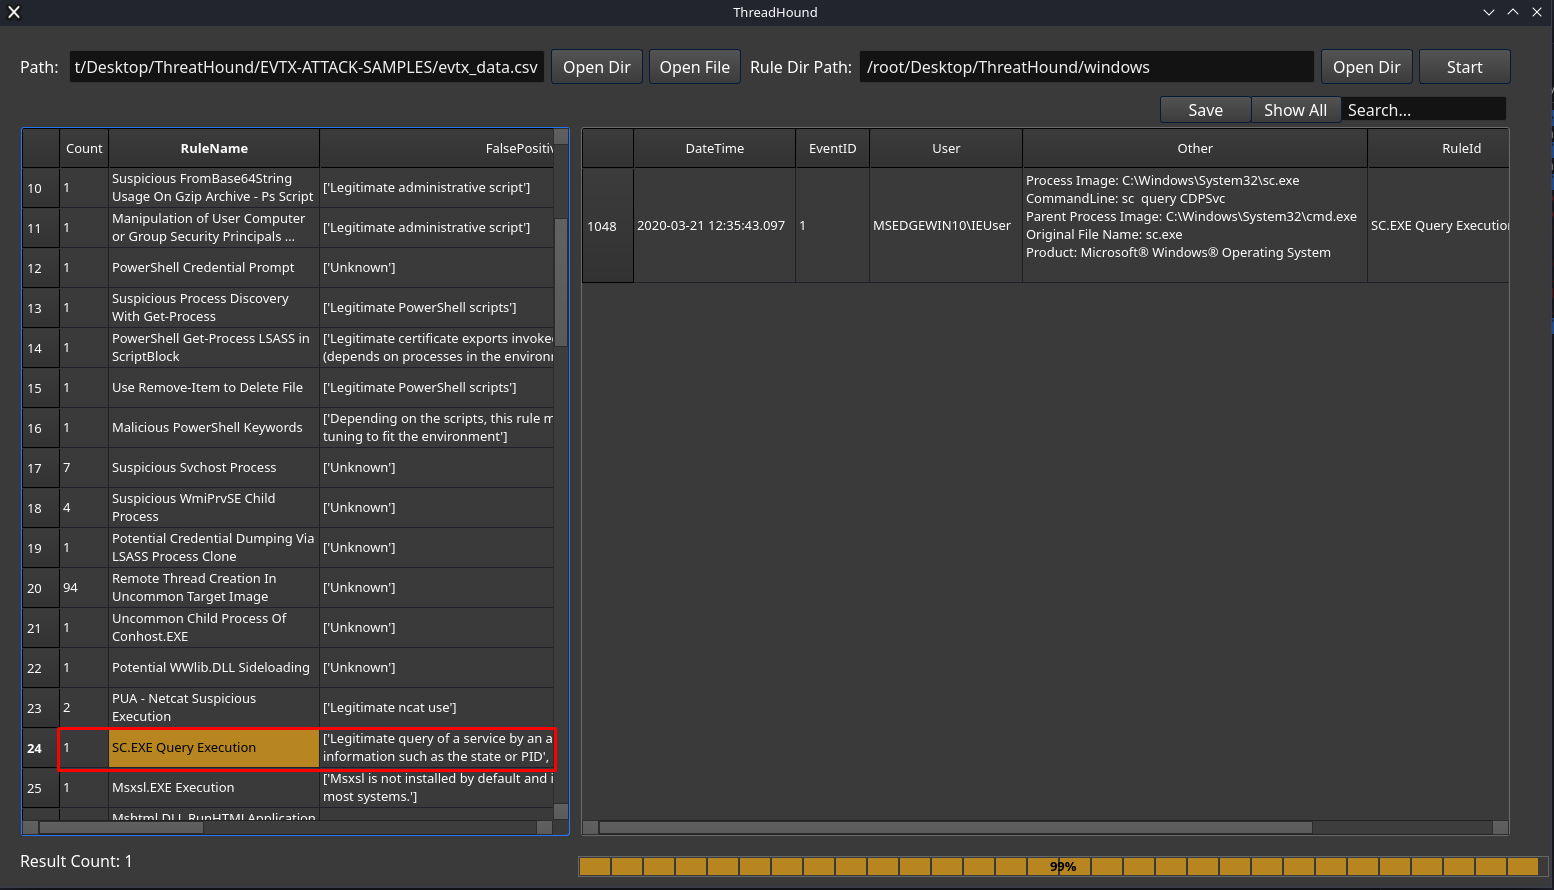 mazx0p/threathound
Windowsイベントログ向けの自動脅威ハンティングおよびインシデント対応ツール。Sigmaルール統合、リアルタイム検出、フォレンジックアーティファクト分析を備えています。
 0xmarcio/pocindex
Search public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.
 monad-developers/ultrafuzz
エンドツーエンドのエージェント型スマートコントラクトファジングと脅威ハンティング
 zeek/zeek
Zeekは、あなたが知っている典型的なIDSとは大きく異なる、強力なネットワーク分析フレームワークです。
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 astrosp/awesome-osint-list
📡 サイバーセキュリティ専門家、研究者、バグバウンティハンターのためのOSINTツールの包括的なコレクション。トピック:情報収集、リバース検索、レッドチーム、トラスト&セーフティ、AI
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 cognis-digital/c2detect
C2サーバーフィンガープリンター — Cobalt Strike、Sliver、Mythic、Havoc、Brute Ratel
 sheeki03/tirith
開発者とAIエージェント向けのターミナルセキュリティ。ホモグラフURL、パイプ→シェル、ANSIインジェクション、難読化されたペイロード、データの外部流出、悪意あるAIスキル/設定を実行前にインターセプトします。
 oyesanyf/oshoosiclaw
Ring-0 WindowsドライバーとLinux eBPFの実行前ブロックを組み合わせ、YARA検出、MITRE ATT&CKマッピング、P2Pメッシュによる脅威共有を備えた自律型Rustエンドポイントセキュリティエージェント。
 emrekybs/socmintelligence
ソーシャルメディアインテリジェンス、調査、および公開データ分析のためのモジュール式OSINT & SOCMINTフレームワーク。
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
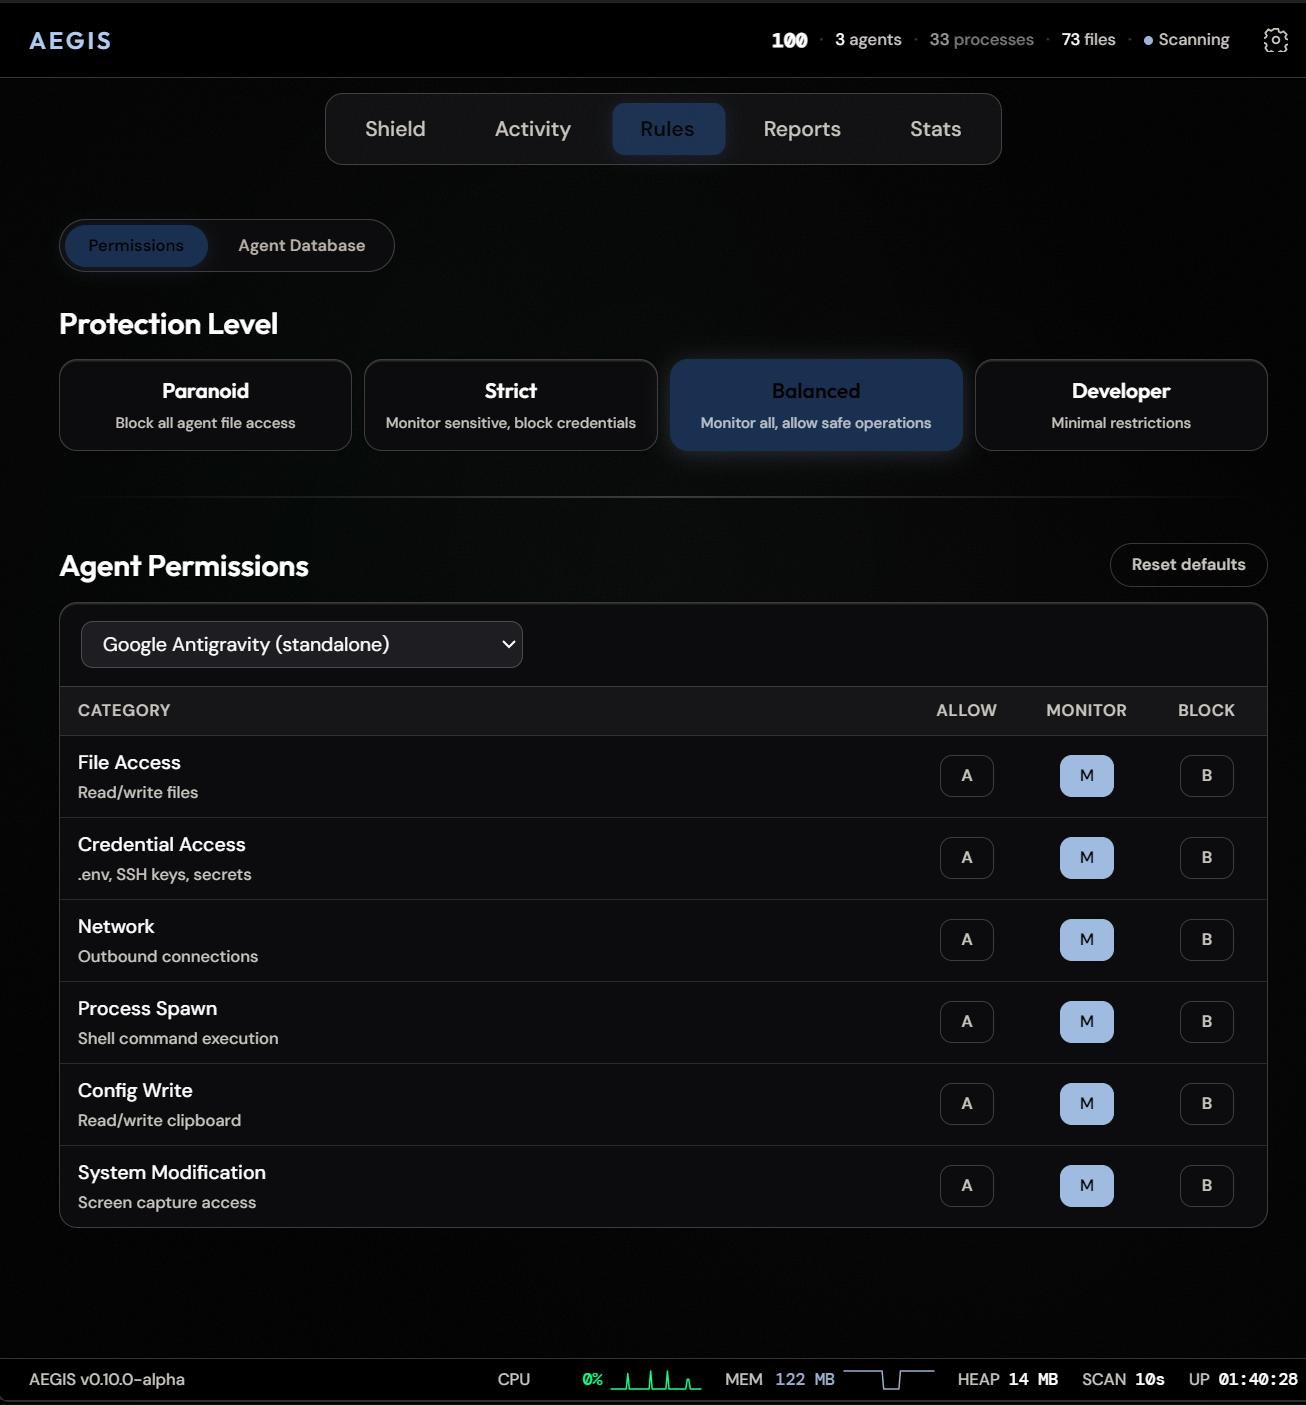 antropos17/aegis
Windows-first desktop oversight for AI agents: live monitoring, local security reviews, token usage, audit reports and opt-in action policies/MCP…
 soxoj/maigret
🕵️♂️ Collect a dossier on a person by username from 6K websites
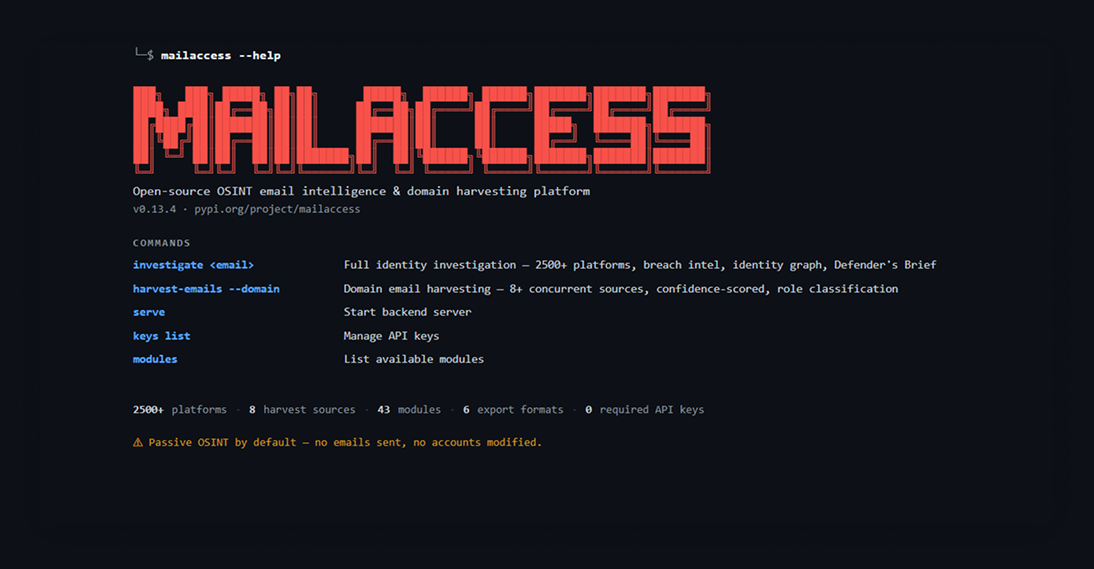 katrielmoses/mailaccess
Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess







