
 #1

 nomi-sec/poc-in-github
📡 PoC auto collect from GitHub. ⚠️ Be careful Malware.
 azure/azure-sentinel
企業全体のインテリジェントなセキュリティ分析のためのクラウドネイティブSIEM。
 antropos17/aegis
Windows-first desktop oversight for AI agents: live monitoring, local security reviews, token usage, audit reports and opt-in action policies/MCP…
 mthcht/awesome-lists
SOC/CERT/CTIの検知とインシデントレスポンス向けに、脅威インテリジェンスフィード、IoCリスト、YARAルール、DFIRツールリファレンスを厳選してまとめたリポジトリです。
 projectdiscovery/awesome-search-queries
複数の検索エンジンにわたる各種製品の検索クエリをコミュニティが厳選したリスト。
 msaad00/agent-bom
Open-source cloud and AI security platform: scan code, dependencies, containers, cloud and AI agents/MCP into one security graph. Self-host free in…
 cveproject/cvelistv5
公式CVEリストのCVE JSON 5形式のCVEキャッシュ
 pypa/advisory-database
PyPI上のPythonパッケージ向けのセキュリティアドバイザリをコミュニティで管理するデータベースであり、pip-auditやOSVなどのツールと統合するためのOSV形式の構造化された脆弱性データを提供します。
 oyesanyf/oshoosiclaw
Ring-0 WindowsドライバーとLinux eBPFの実行前ブロックを組み合わせ、YARA検出、MITRE ATT&CKマッピング、P2Pメッシュによる脅威共有を備えた自律型Rustエンドポイントセキュリティエージェント。
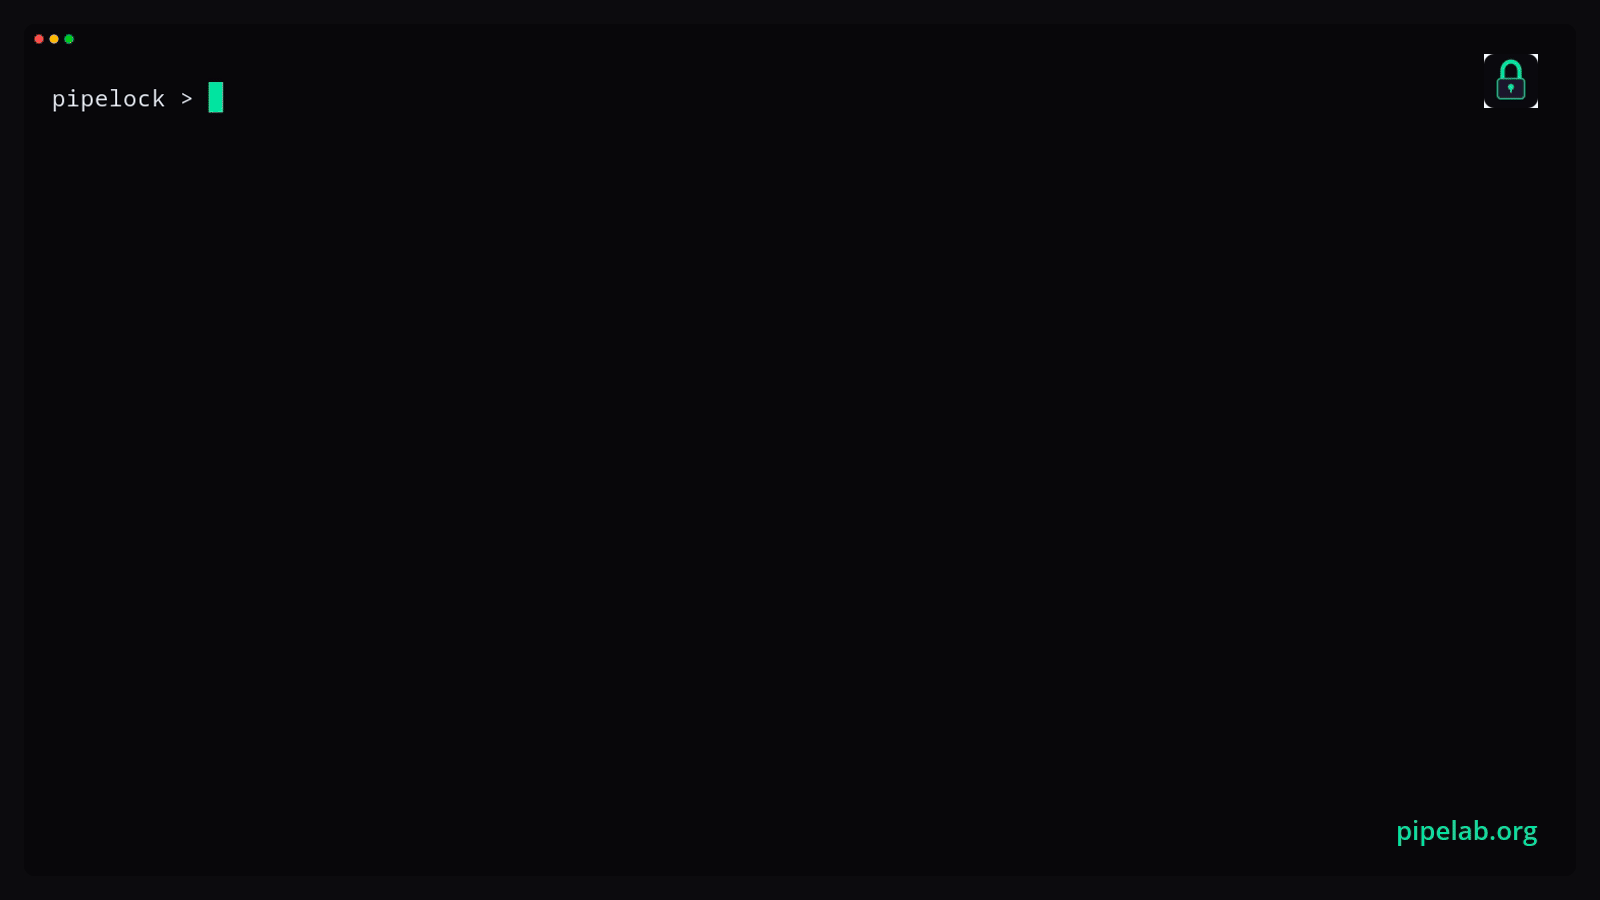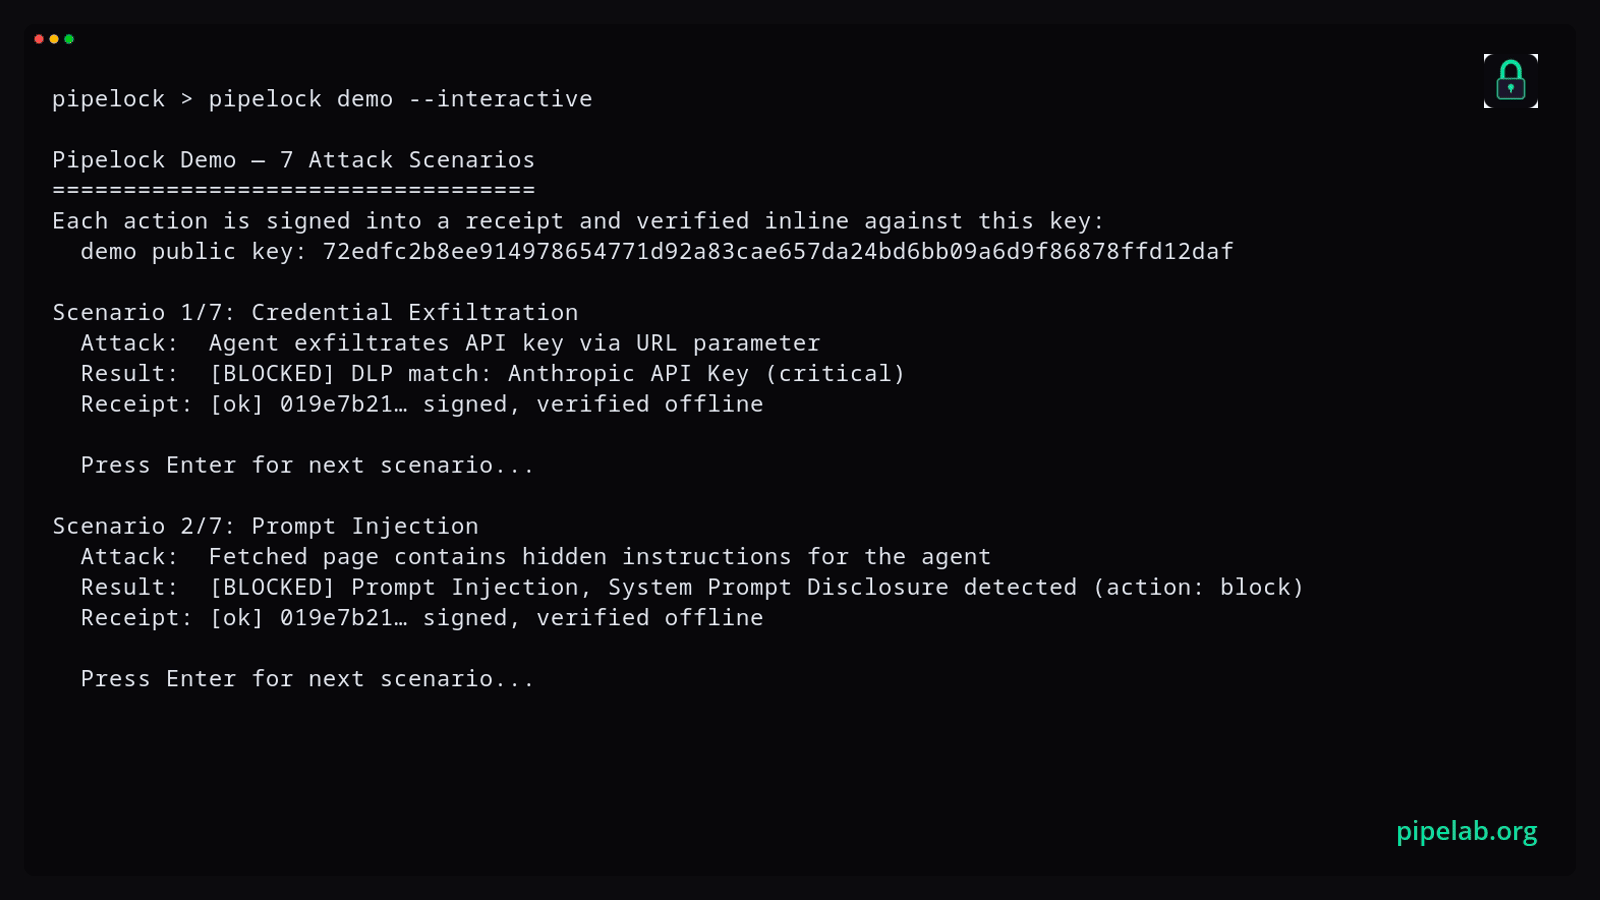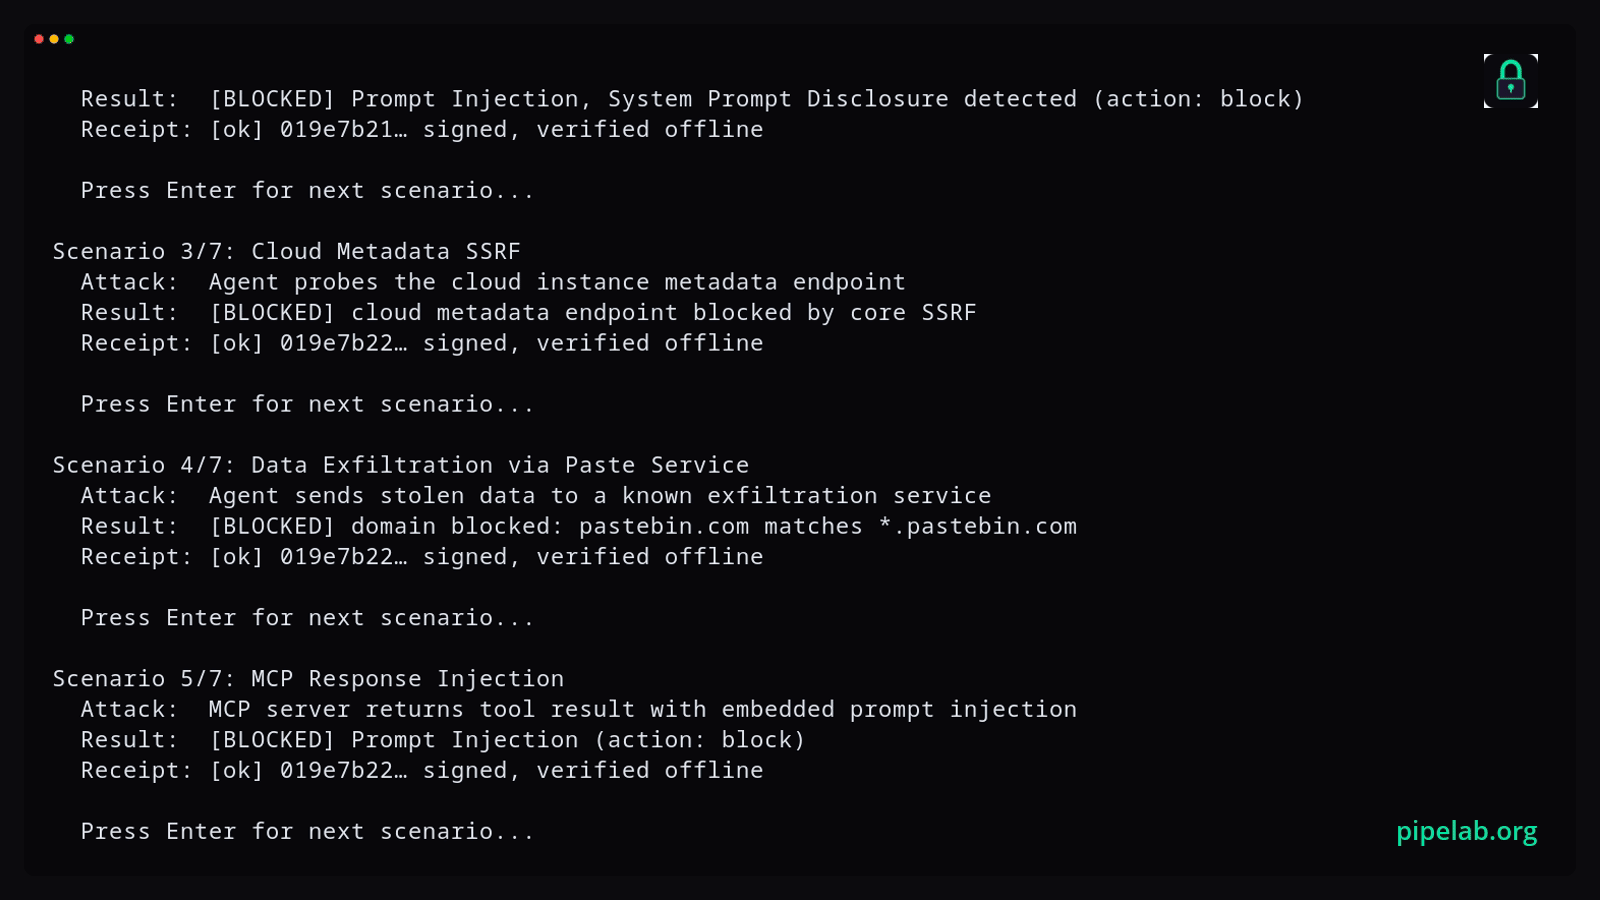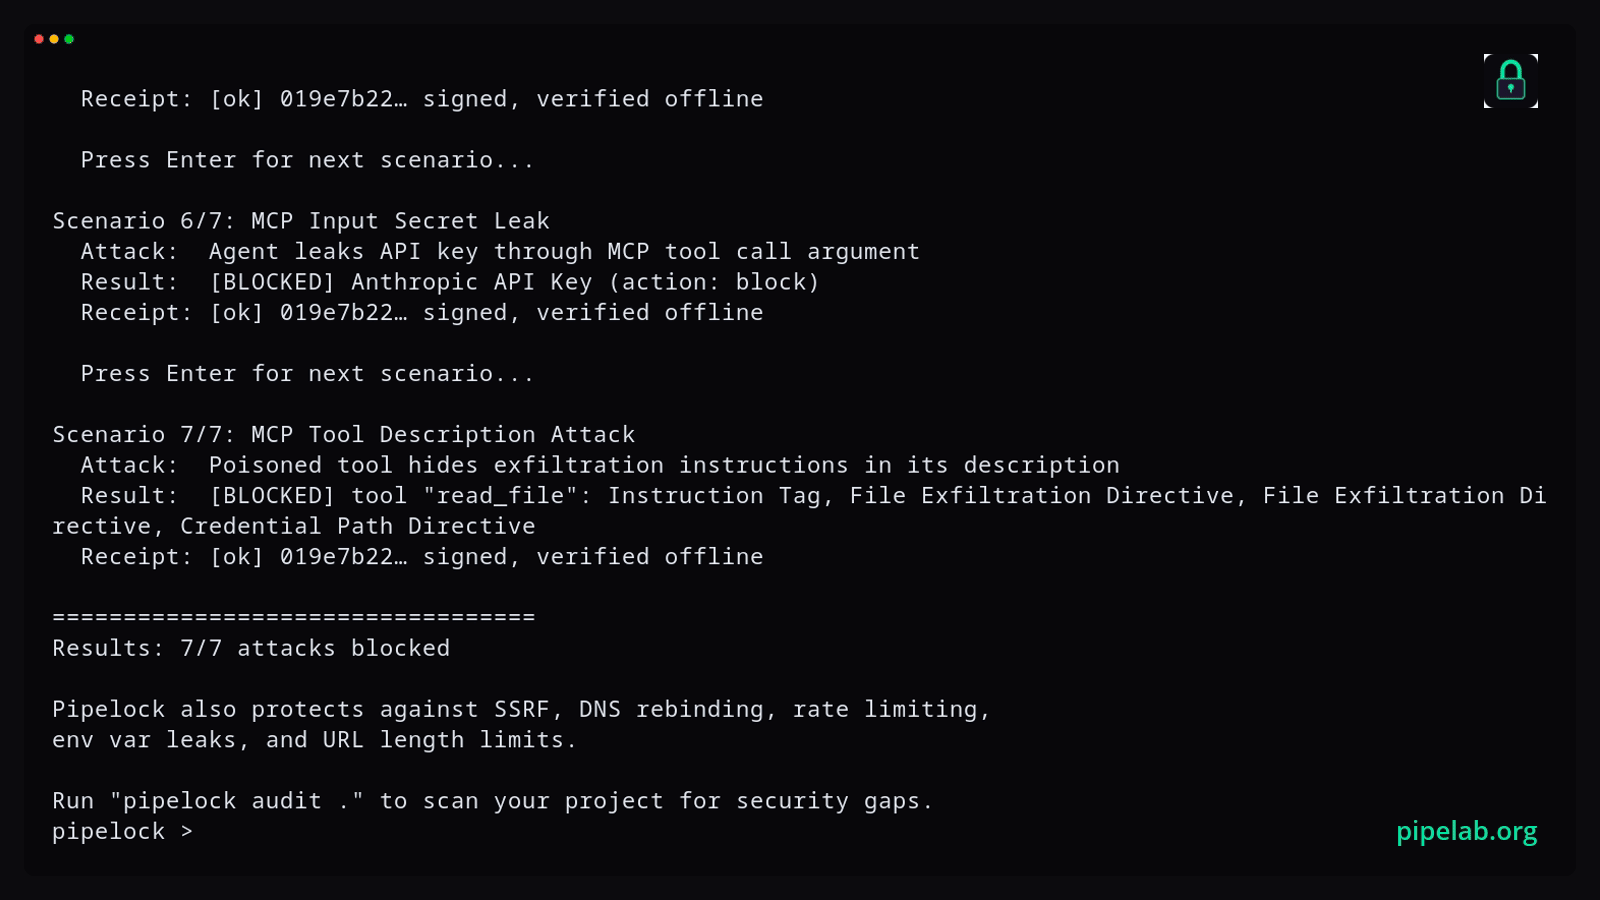 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 garrytan/gstack
Use Garry Tan's exact Claude Code setup: 23 opinionated tools that serve as CEO, Designer, Eng Manager, Release Manager, Doc Engineer, and QA
 osintbrazuca/osint-brazuca
リポジトリは、ブラジルの文脈におけるOSINTの情報、ソース(ウェブサイト/ポータル)、トリックを集める目的で作成されました。
 aquasecurity/vuln-list-redhat
Red Hat セキュリティアドバイザリ
 rubysec/ruby-advisory-db
Ruby gemおよびランタイム向けのセキュリティアドバイザリをコミュニティで維持管理するデータベースであり、構造化されたCVE/GHSAデータとパッチ適用済みバージョンを提供して、脆弱性の追跡と監査統合を支援します。
 toborrm9/malicious_extension_sentry
Malicious Extension Database
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…









