Skip to content
KitploitKITPLOIT
StrumentiExploitsBlog
Log in
Invia
StrumentiExploitsBlog
Invia

Strumenti di Hacking, PenTest e Cybersecurity per il tuo Arsenale di Sicurezza!

Kitploit è una directory di strumenti di hacking, cybersecurity e pentesting. Scopri gli ultimi aggiornamenti dei progetti per trovare vulnerabilità, analizzare sistemi, automatizzare i test e rafforzare la tua sicurezza.

FeedContattoPrivacy© 2026 Kitploit

Directory degli strumenti

Categorie

Vedi tutte le categorie
Loading categories
Kittysploit-framework — Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,.... | Kitploit
Strumenti/GitHubGitHub/sia-iotechnology/kittysploit-framework
OSINT (Open Source Intelligence)Penetration Testing FrameworksReconnaissanceExploit FrameworksWeb Proxies & InterceptionDebuggersPost-ExploitationCommand and ControlRed TeamingPayload DevelopmentAI Security
59398734 giorni faRevisionato da Kitploit
Condividi
GitHub
sia-iotechnology/kittysploit-framework

Kittysploit-framework

Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
Vedi RepositorySito web
Contenuto non disponibile nella lingua richiesta. Visualizzazione della versione inglese.
KittySploit logo

KittySploit

Exploitation and post-exploitation framework — one console.

Recon, scanning, exploits, interactive sessions, and post-exploitation across 60+ session connectors (shell, browser, databases, cloud, IoT/ICS, and more).
Python License Discord GitHub stars

Installation · Quick start · Full guide · Website

KittySploit — console, exploitation, and sessions

At a glance

StepWhat KittySploit does
1. FindWeb, network, cloud, and service scanners and recon
2. ExploitExploit modules, chains, and optional local-LLM agent
3. Post-exploit60+ session connectors — loot, pivot, persistence, enumeration

Everything stays in one console: modules, listeners, payloads, built-in C2, and reporting.

Use only on targets you own or are explicitly authorized to test.

Why KittySploit?

Typical stacks split the scanner, exploit framework, C2, and notes across different tools.

KittySploit brings them together: exploit to get a session, then run post-exploitation without switching apps.

Post-exploitation connector examples: Linux/Windows shell, browser (JS session), SSH, MySQL/PostgreSQL/Redis/MongoDB, SMB, FTP, Kubernetes, AWS/GCP/Azure, PHP webshell, WinRM, LDAP, BLE, MQTT, Modbus, BACnet, ONVIF, and more.

Module scale (approximate): thousands of scanners/auxiliary modules, 700+ exploits, 400+ post modules.

Installation

Linux and macOS

git clone https://github.com/SIA-IOTechnology/Kittysploit-framework.git
cd Kittysploit-framework
./install/install.sh
python3 kittyconsole.py

One-line install:

curl -fsSL https://raw.githubusercontent.com/SIA-IOTechnology/Kittysploit-framework/main/install/install-standalone.sh | bash

Windows

git clone https://github.com/SIA-IOTechnology/Kittysploit-framework.git
cd Kittysploit-framework
install\install.bat
python kittyconsole.py

Quick start

kittysploit> doctor
kittysploit> search cve:2024 type:exploit
kittysploit> use exploits/multi/http/...
kittysploit> run

kittysploit> sessions -l
kittysploit> sessions -i 1
kittysploit> search type:post platform:windows

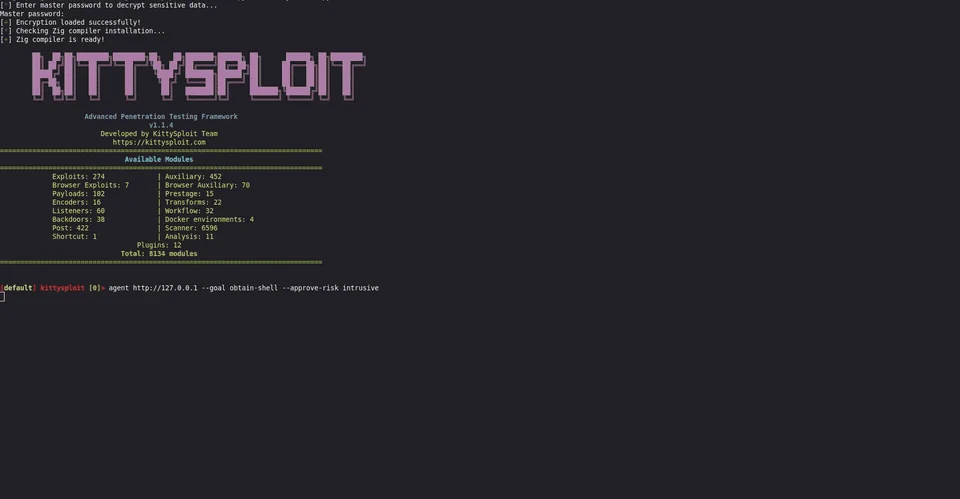
Automated web mission (authorized lab):

kittysploit> agent https://lab.local

Shell goal on an internal lab:

kittysploit> agent http://192.168.56.10 \
  --profile internal-lab \
  --goal obtain-shell \
  --approve-risk intrusive \
  --shell-hunter

Use --plan-only or --dry-run to preview without intrusive actions.

Core features

  • Exploitation — search / use / run, payloads, listeners, exploit queues
  • Sessions and C2 — shells, callbacks, pivots, multi-session management
  • Post-exploitation — modules per session type (gather, manage, pivot, loot)
  • Agent (optional) — local LLM (Ollama), mission profiles, scope controls
  • Automation — CLI, API/RPC, and MCP for IDE or scripted workflows

Agent profiles, compound evidence, environment variables, and cookbooks are in USAGE.md.

Ecosystem

ProjectPurpose
KittyProxyHTTP capture and analysis
KittyCosmicGraphical interface
KittyOsintVisual OSINT
KittyProtocolProtocol analysis
KittyV8DebuggerV8 debugging

Demo video · Site and marketplace · Wiki

Community

  • Discord
  • Issues
  • Liberapay

The project is still evolving — validate in a lab before production engagements.

Acknowledgments

Thanks to Woody for their contributions.

License

Released under the MIT License.

Scarica lo strumento

Più Popolari

Vedi tutti →

Scopri gli strumenti più utilizzati dalla nostra community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Il toolkit OSINT definitivo: grafo di indagine, punteggio di affidabilità, famiglie di alias, mappa, timeline e report. 49 moduli, oltre 400 siti, nessuna chiave API richiesta.

    708
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # App di esecuzione con un tocco GhostLock (CVE-2026-43499)

    500
  • 3

    ARTEX

    baarai/artex

    Piattaforma di penetration testing autonoma multi-agente basata su LLM con agenti planner/worker, grafi di asset e di esplorazione, registrazione del traffico MITM e retesting delle vulnerabilità.

    398
  • 4

    redforge

    cybersecurity91/redforge

    Toolkit red team lato browser con 102 strumenti offline per ricognizione, generazione di payload, attacchi alle credenziali, crittografia, codifica e reportistica dell'engagement.

    341
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Il sistema d'azione per la cybersecurity nativa AI—dove l'intento diventa esecuzione governata, le evidenze diventano memoria operativa, e ogni operazione migliora la successiva.

    259
  • 6

    antifox

    antifox-ai/antifox

    Piattaforma multi-agente di penetration testing autonoma basata sull'IA che esegue ricognizione, scoperta della superficie d'attacco, validazione dello sfruttamento e consegna di report supportati da evidenze.

    257

Esplora tutti gli strumenti

Sfoglia la nostra collezione di strumenti

Vedi tutti gli strumenti →