
Skip to content
KitploitKITPLOIT
StrumentiExploitsBlog
Log in
Invia
StrumentiExploitsBlog
Invia

Strumenti di Hacking, PenTest e Cybersecurity per il tuo Arsenale di Sicurezza!

Kitploit è una directory di strumenti di hacking, cybersecurity e pentesting. Scopri gli ultimi aggiornamenti dei progetti per trovare vulnerabilità, analizzare sistemi, automatizzare i test e rafforzare la tua sicurezza.

FeedContattoPrivacy© 2026 Kitploit

Directory degli strumenti

Categorie

Vedi tutte le categorie
Loading categories
SafeGuard — CLI Encryption tool written in Go only for learning purposes and demonstration of encryption (not secure) | Kitploit
Strumenti/GitHubGitHub/pingpongplus/safeguard
General Purpose UtilitiesEncryption/Decryption ToolsCryptographyLearning & Education
GitHubpingpongplus/safeguard

SafeGuard

CLI Encryption tool written in Go only for learning purposes and demonstration of encryption (not secure)

Vedi Repository
811036 giorni faNon ancora revisionato
Condividi
Contenuto non disponibile nella lingua richiesta. Visualizzazione della versione inglese.

Safeguard-Terminal


Safeguard is a fast, lightweight, cross-platform command-line file encryption tool written in Go.

Security Notice

This project is a learning-oriented file encryption tool.

While it uses standard cryptographic primitives from Go’s standard library (e.g. AES-GCM for authenticated encryption), it does not use a modern, memory-hard password key derivation function such as Argon2 or scrypt.

Instead, keys are derived using a lightweight, standard-library-only method. This means:

  • The encryption is secure against casual inspection
  • Integrity and tampering are detected
  • Passwords are not strongly protected against determined brute-force or GPU-based attacks

Do NOT use this tool fr your key is in plaintext and is getting saved in your terminal history

Intended use:

  • Learning and experimentation
  • Personal or low-risk file protection
  • Open-source collaboration and improvement

Installation

Build (req. Go)

git clone https://github.com/pingplus/SafeGuard.git
cd SafeGuard
go build

Usage

General syntax:

./safeguard <file> <action> <cipher> [options]

Actions:

  • --encrypt or e Encrypt a file
  • --decrypt or d Decrypt a file
  • --decrypt-directory or de Decrypt a whole directory (decrypting directory not available yet sorry :( )

Options:

  • --inplace decrypt/encrypt a file in place (experimental)
  • --key add key
  • --output specify the output name

Supported ciphers:

./safeguard --list-ciphers
[i] Available ciphers:
  xor
  caesar
  aes

AES

Encrypt a file:

./safeguard secret.txt e aes --key "your-strong-password"
# or
./safeguard secret.txt --encrypt aes --key "your-strong-password" --output secret.txt.aes

Decrypt a file:

./safeguard secret.txt d aes --key "your-strong-password"
# or
./safeguard secret.txt --decrypt aes --key "your-strong-password" --output secret.txt.dec

More

  • Encrypt with AES and write in place:
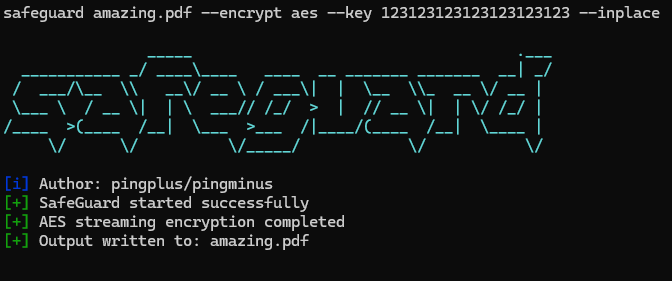
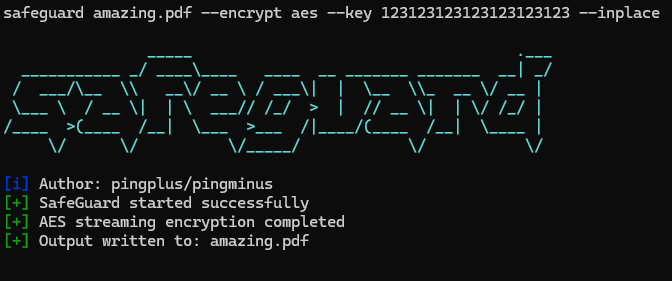
./safeguard secrets.txt e aes --key "123123123123123123123123" --inplace
# -> creates secrets.txt but encrypted
  • Decrypt with AES and specify output file :
./safeguard secrets.txt.aes d aes --key "123123123123123123123123" --output secrets_decrypted.txt

Scarica lo strumento

Più Popolari

Vedi tutti →

Scopri gli strumenti più utilizzati dalla nostra community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Il toolkit OSINT definitivo: grafo di indagine, punteggio di affidabilità, famiglie di alias, mappa, timeline e report. 49 moduli, oltre 400 siti, nessuna chiave API richiesta.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # App di esecuzione con un tocco GhostLock (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    Piattaforma di penetration testing autonoma multi-agente basata su LLM con agenti planner/worker, grafi di asset e di esplorazione, registrazione del traffico MITM e retesting delle vulnerabilità.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Toolkit red team lato browser con 102 strumenti offline per ricognizione, generazione di payload, attacchi alle credenziali, crittografia, codifica e reportistica dell'engagement.

    343
  • 5

    antifox

    antifox-ai/antifox

    Piattaforma multi-agente di penetration testing autonoma basata sull'IA che esegue ricognizione, scoperta della superficie d'attacco, validazione dello sfruttamento e consegna di report supportati da evidenze.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Il sistema d'azione per la cybersecurity nativa AI—dove l'intento diventa esecuzione governata, le evidenze diventano memoria operativa, e ogni operazione migliora la successiva.

    258

Esplora tutti gli strumenti

Sfoglia la nostra collezione di strumenti

Vedi tutti gli strumenti →





