Skip to content
KitploitKITPLOIT
StrumentiExploitsBlog
Log in
Invia
StrumentiExploitsBlog
Invia

Strumenti di Hacking, PenTest e Cybersecurity per il tuo Arsenale di Sicurezza!

Kitploit è una directory di strumenti di hacking, cybersecurity e pentesting. Scopri gli ultimi aggiornamenti dei progetti per trovare vulnerabilità, analizzare sistemi, automatizzare i test e rafforzare la tua sicurezza.

FeedContattoPrivacy© 2026 Kitploit

Directory degli strumenti

Categorie

Vedi tutte le categorie
Loading categories
wrongsecrets — Vulnerable app with examples showing how to not use secrets | Kitploit
Strumenti/GitHubGitHub/owasp/wrongsecrets
Container SecurityVulnerability AnalysisCTFCloud SecurityDevSecOpsSecret DetectionLearning & EducationLabs & PracticeTop in Labs & Practice n.8Top in Secret Detection n.19
1.5k59911712h 15m faRevisionato da Kitploit
Condividi
GitHubowasp/wrongsecrets

wrongsecrets

Vulnerable app with examples showing how to not use secrets
Vedi RepositorySito web
Contenuto non disponibile nella lingua richiesta. Visualizzazione della versione inglese.

OWASP WrongSecrets

Tweet

Java checkstyle and testing Pre-commit Terraform FMT CodeQL Dead Link Checker Javadoc and Swaggerdoc generator Test Heroku with cypress Build Dev Container

Test minikube script (k8s) Test minikube script (k8s&vault) Docker container test Test container on podman DAST with ZAP PR Preview and Visual Diff Build Preview Visual Diff

OWASP Production Project OpenSSF Best Practices Discussions Docker pulls

Welcome to the OWASP WrongSecrets game! The game is packed with real life examples of how to not store secrets in your software. Each of these examples is captured in a challenge, which you need to solve using various tools and techniques. Solving these challenges will help you recognize common mistakes & can help you to reflect on your own secrets management strategy.

Can you solve all the challenges?

Try some of them on our Heroku demo environment.

Want to play the other challenges? Read the instructions on how to set them up below.

🚀 Quick Start

New to WrongSecrets? Start here:

  1. Try Online First: Visit our Heroku demo to get familiar with the challenges
  2. Run Locally: Use Docker for the full experience with all challenges:
    docker run -p 8080:8080 -p 8090:8090 jeroenwillemsen/wrongsecrets:latest-no-vault
    
    Then open http://localhost:8080
  3. Want to see what's ahead? Try our bleeding-edge master container with the latest features:
    docker run -p 8080:8080 -p 8090:8090 ghcr.io/owasp/wrongsecrets/wrongsecrets-master:latest-master
    
    ⚠️ Note: This is a development version and may be unstable
  4. Advanced Setup: For cloud challenges and Kubernetes exercises, see the detailed instructions below

What you'll learn:

  • Common secrets management mistakes
  • How to identify exposed credentials
  • Best practices for securing secrets
  • Tools and techniques for secret detection

How it works: This repository contains intentionally vulnerable code and configuration files with real and fake secrets hidden throughout the codebase. You'll examine source code, configuration files, Docker containers, and cloud deployments to discover these secrets. Each challenge teaches you different ways secrets can be accidentally exposed in real-world applications.
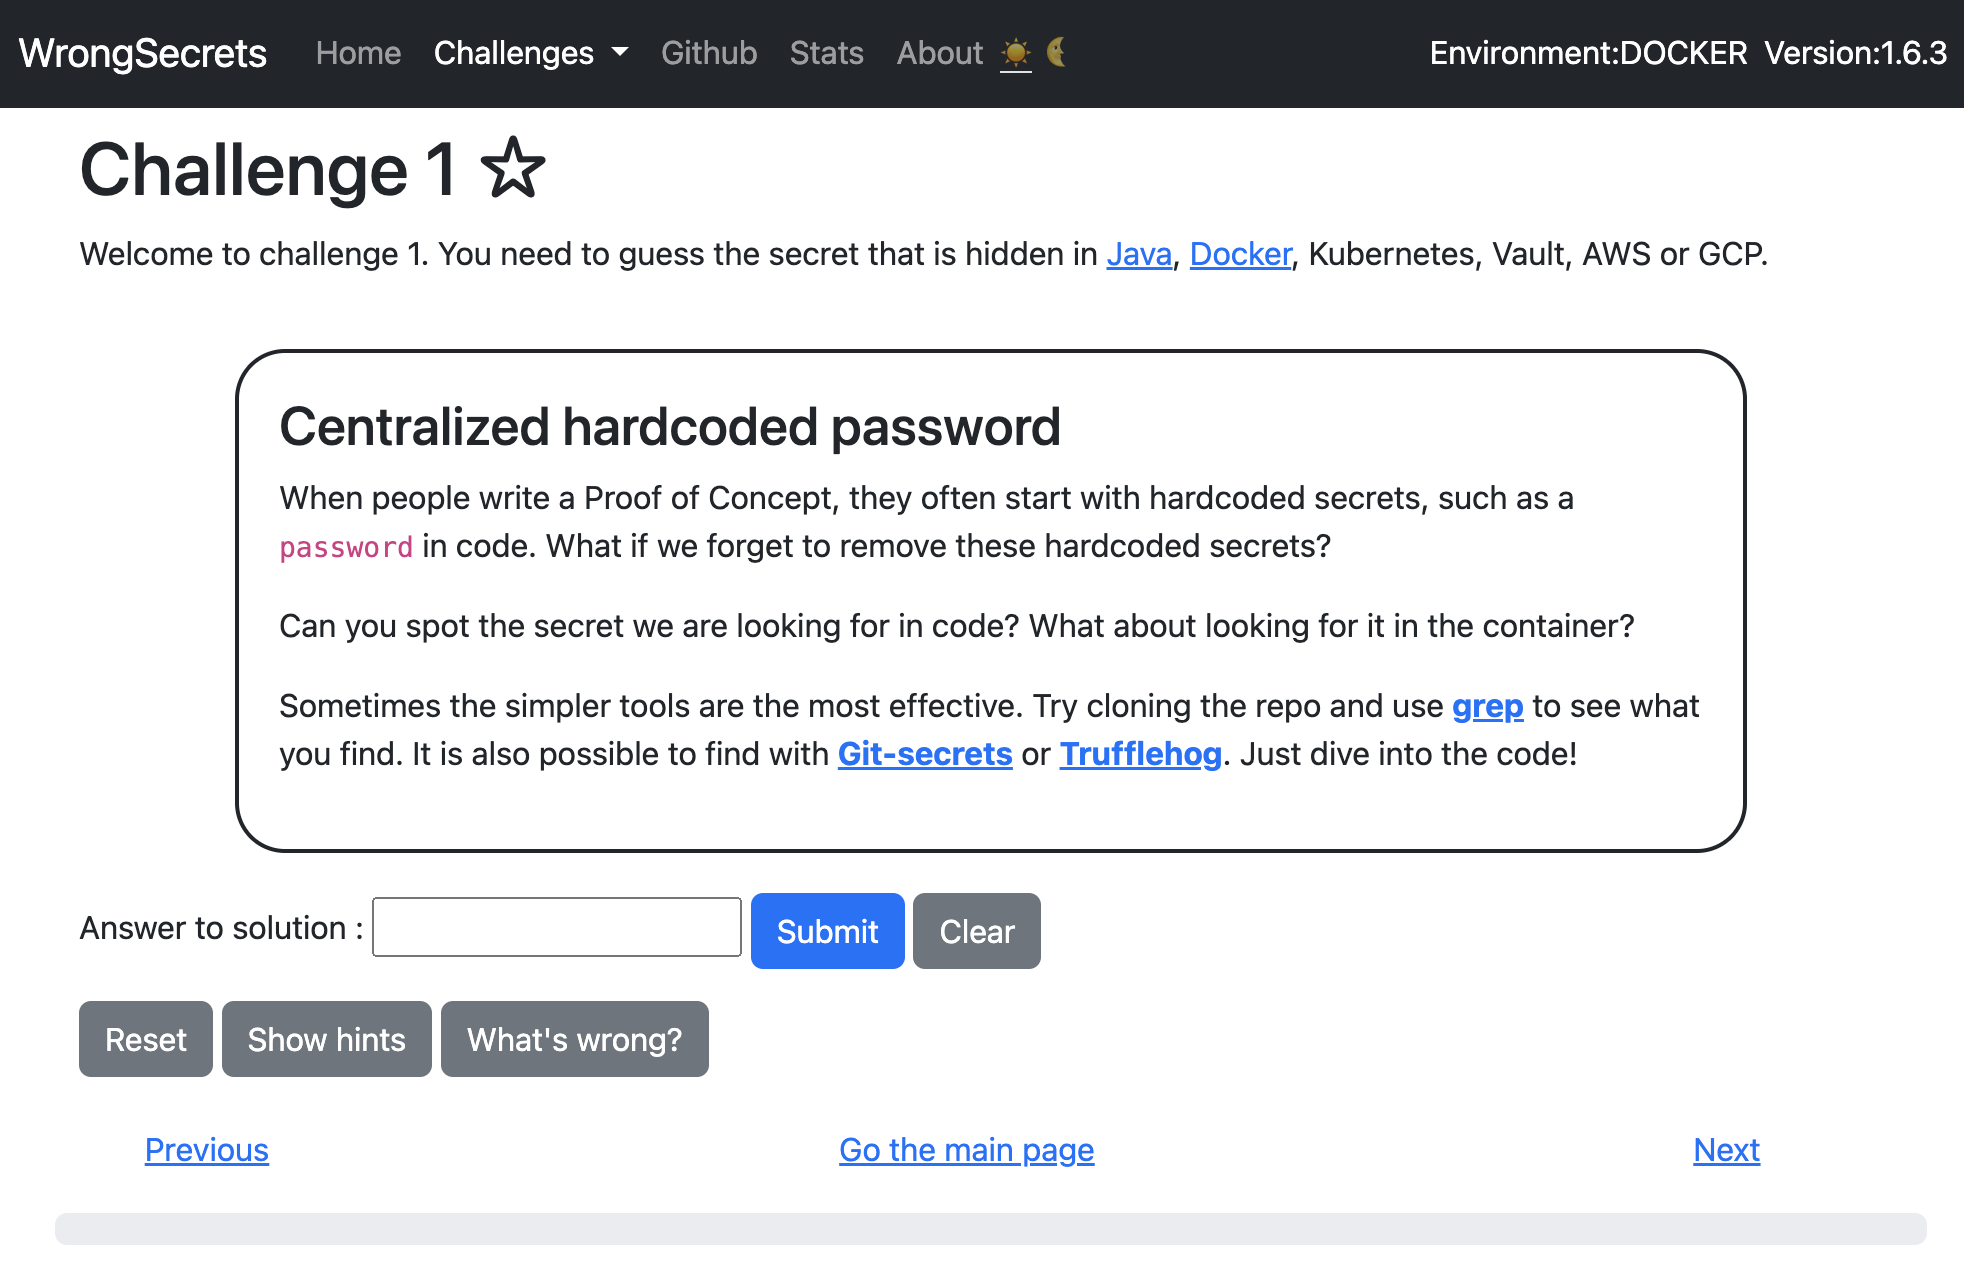
screenshotOfChallenge1

📋 Prerequisites

For basic usage:

  • A web browser
  • Docker (for local setup) - Install here

For advanced setups:

  • Kubernetes/Minikube - Install here
  • Cloud account (AWS/GCP/Azure) for cloud challenges
  • Command line familiarity
Scarica lo strumento

Più Popolari

Vedi tutti →

Scopri gli strumenti più utilizzati dalla nostra community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Il toolkit OSINT definitivo: grafo di indagine, punteggio di affidabilità, famiglie di alias, mappa, timeline e report. 49 moduli, oltre 400 siti, nessuna chiave API richiesta.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # App di esecuzione con un tocco GhostLock (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    Piattaforma di penetration testing autonoma multi-agente basata su LLM con agenti planner/worker, grafi di asset e di esplorazione, registrazione del traffico MITM e retesting delle vulnerabilità.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Toolkit red team lato browser con 102 strumenti offline per ricognizione, generazione di payload, attacchi alle credenziali, crittografia, codifica e reportistica dell'engagement.

    343
  • 5

    antifox

    antifox-ai/antifox

    Piattaforma multi-agente di penetration testing autonoma basata sull'IA che esegue ricognizione, scoperta della superficie d'attacco, validazione dello sfruttamento e consegna di report supportati da evidenze.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Il sistema d'azione per la cybersecurity nativa AI—dove l'intento diventa esecuzione governata, le evidenze diventano memoria operativa, e ogni operazione migliora la successiva.

    258

Esplora tutti gli strumenti

Sfoglia la nostra collezione di strumenti

Vedi tutti gli strumenti →