
 hahwul/xspear
🔱 Potente strumento di scansione XSS e analisi dei parametri &gem
XSpear è uno scanner XSS su rubygems


[!IMPORTANT] Repository XSpear archiviato
Questo repository è stato archiviato ed è ora in sola lettura.
XSpear non viene più mantenuto attivamente.Prova Dalfox invece 🌙🦊
Uno scanner XSS più veloce e potente con funzionalità avanzate.
alert confirm prompt su browser headless (con Selenium)event handler HTML tag Special Char Useful codeCSP HSTS X-frame-options, XSS-protection ecc.)table base cli-report e filtered rule, testing raw query (url)cli json html
Installalo da solo con:
$ gem install XSpear
Oppure installalo da solo (file locale / scarica l'ultima versione):
$ gem install XSpear-{version}.gem
Aggiungi questa riga al tuo Gemfile dell'applicazione:```ruby gem 'XSpear'
Ed poi esegui:

    $ bundle

### Gem di dipendenza
`colorize` `selenium-webdriver` `terminal-table` `progress_bar`<br>
Se l'hai configurato per installarsi automaticamente nella libreria Gem, ma si comporta in modo anomalo, installalo con il seguente comando.```
$ gem install colorize
$ gem install selenium-webdriver
$ gem install terminal-table
$ gem install progress_bar
Usage: xspear -u [target] -[options] [value] [ e.g ] $ xspear -u 'https://www.hahwul.com/?q=123' --cookie='role=admin' -v 1 -a $ xspear -u 'http://testphp.vulnweb.com/listproducts.php?cat=123' -v 2 $ xspear -u 'http://testphp.vulnweb.com/listproducts.php?cat=123' -v 0 -o json
[ Options ] -u, --url=target_URL [required] Target Url -d, --data=POST Body [optional] POST Method Body data -a, --test-all-params [optional] test to all params(include not reflected) --no-xss [optional] no testing xss, only parameters analysis --headers=HEADERS [optional] Add HTTP Headers --cookie=COOKIE [optional] Add Cookie --custom-payload=FILENAME [optional] Load custom payload json file --raw=FILENAME [optional] Load raw file(e.g raw_sample.txt) -p, --param=PARAM [optional] Test paramters -b, --BLIND=URL [optional] Add vector of Blind XSS + with XSS Hunter, ezXSS, HBXSS, etc... + e.g : -b https://hahwul.xss.ht -t, --threads=NUMBER [optional] thread , default: 10 -o, --output=FORMAT [optional] Output format (cli , json) -c, --config=FILENAME [optional] Using config.json -v, --verbose=0~3 [optional] Show log depth + v=0 : quite mode(only result) + v=1 : show scanning status(default) + v=2 : show scanning logs + v=3 : show detail log(req/res) -h, --help Prints this help --version Show XSpear version --update Show how to update
### Tipi di risultato
- (I)NFO: Ottieni informazioni (ad esempio errore SQL, regola filtrata, parametri riflessi, ecc.)
- (V)UNL: XSS vulnerabile, Alert/prompt/confirm controllati con Selenium
- (L)OW: Problema di basso livello
- (M)EDIUM: Problema di livello medio
- (H)IGH: Problema di alto livello

### Modalità verbosa
**[0] modalità silenziosa (mostra solo i risultati)**```
$ xspear -u "http://testphp.vulnweb.com/listproducts.php?cat=123" -v 0
you see report
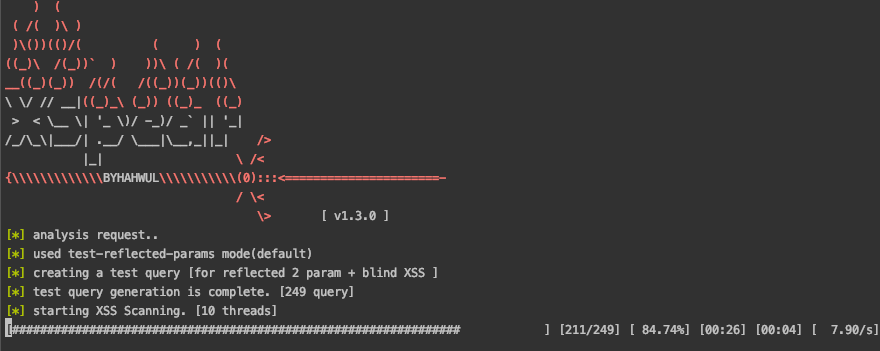
[1] mostra barra di avanzamento (predefinito)``` $ xspear -u "http://testphp.vulnweb.com/listproducts.php?cat=123" -v 1 [] analysis request.. [] used test-reflected-params mode(default) [] creating a test query [for reflected 2 param + blind XSS ] [] test query generation is complete. [249 query] [*] starting XSS Scanning. [10 threads]