
 ashrafzaryouh/cve-2026-20253
Pacchetto di advisory e rilevamento per CVE-2026-20253, una vulnerabilità di creazione arbitraria di file non autenticata in Splunk Enterprise, con analisi tecnica, regole Sigma/YARA, IOC e indicazioni per la patch.

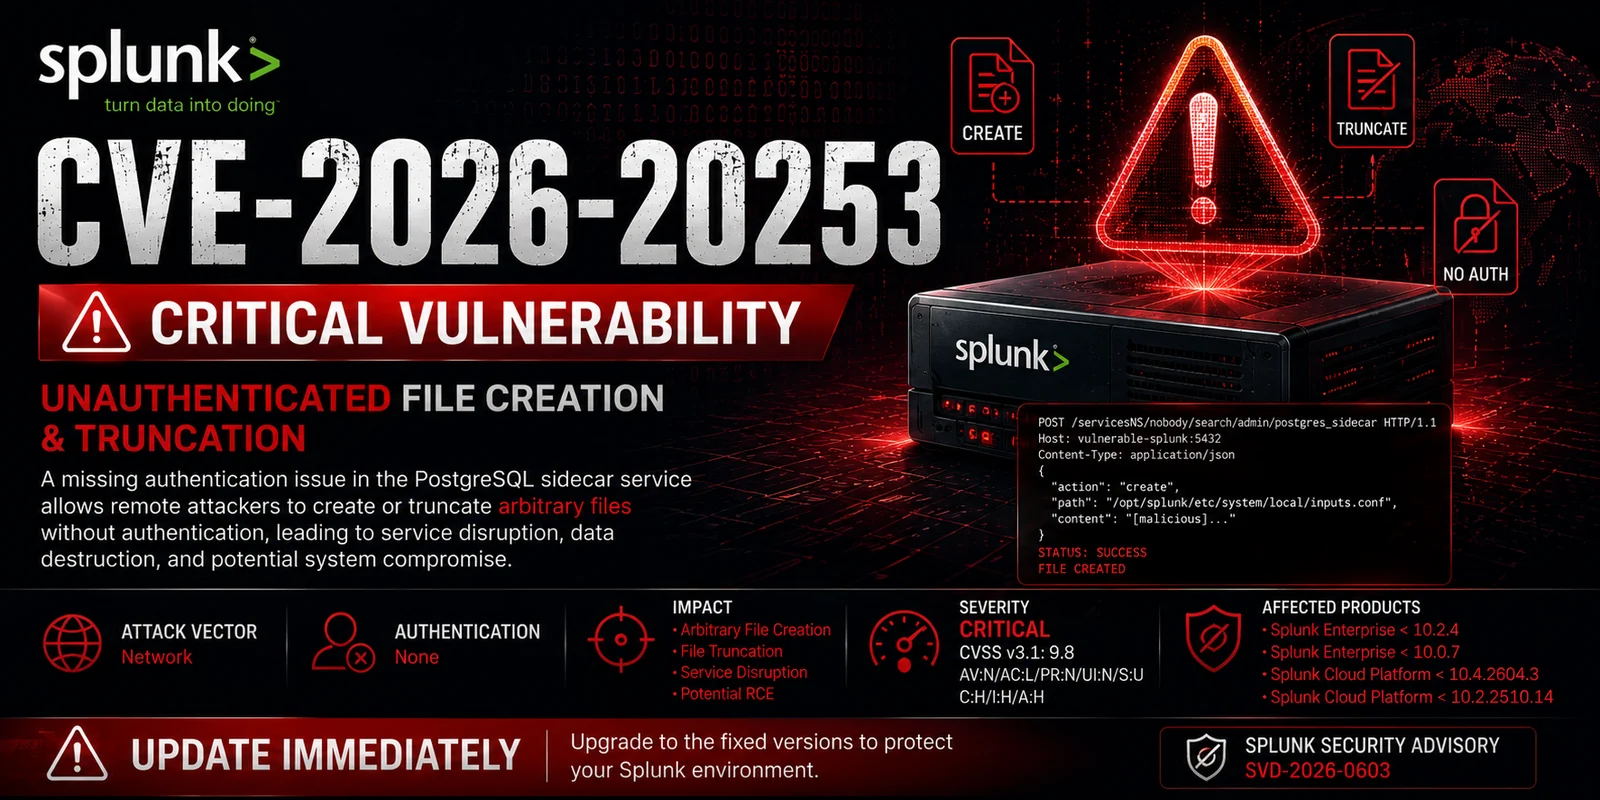


Vulnerabilità di creazione e troncamento arbitrario di file non autenticata che interessa Splunk Enterprise e Splunk Cloud Platform.
CVE-2026-20253 è una vulnerabilità critica in Splunk Enterprise e Splunk Cloud Platform che consente a un attaccante remoto non autenticato di creare o troncare file arbitrari tramite un endpoint esposto del servizio sidecar PostgreSQL.
Poiché la funzionalità vulnerabile manca di controlli di autenticazione, gli attaccanti possono eseguire operazioni sui file senza credenziali valide.
Un'eventuale sfruttamento con successo può comportare:
| Proprietà | Valore |
|---|---|
| CVE | CVE-2026-20253 |
| Fornitore | Splunk |
| Gravità | Critica |
| CVSS v3.1 | 9.8 |
| CWE | CWE-306 |
| Tipo di vulnerabilità | Autenticazione mancante |
| Vettore di attacco | Rete |
| Autenticazione | Nessuna |
| Interazione utente | Nessuna |
| Impatto | Creazione file / Troncamento file |
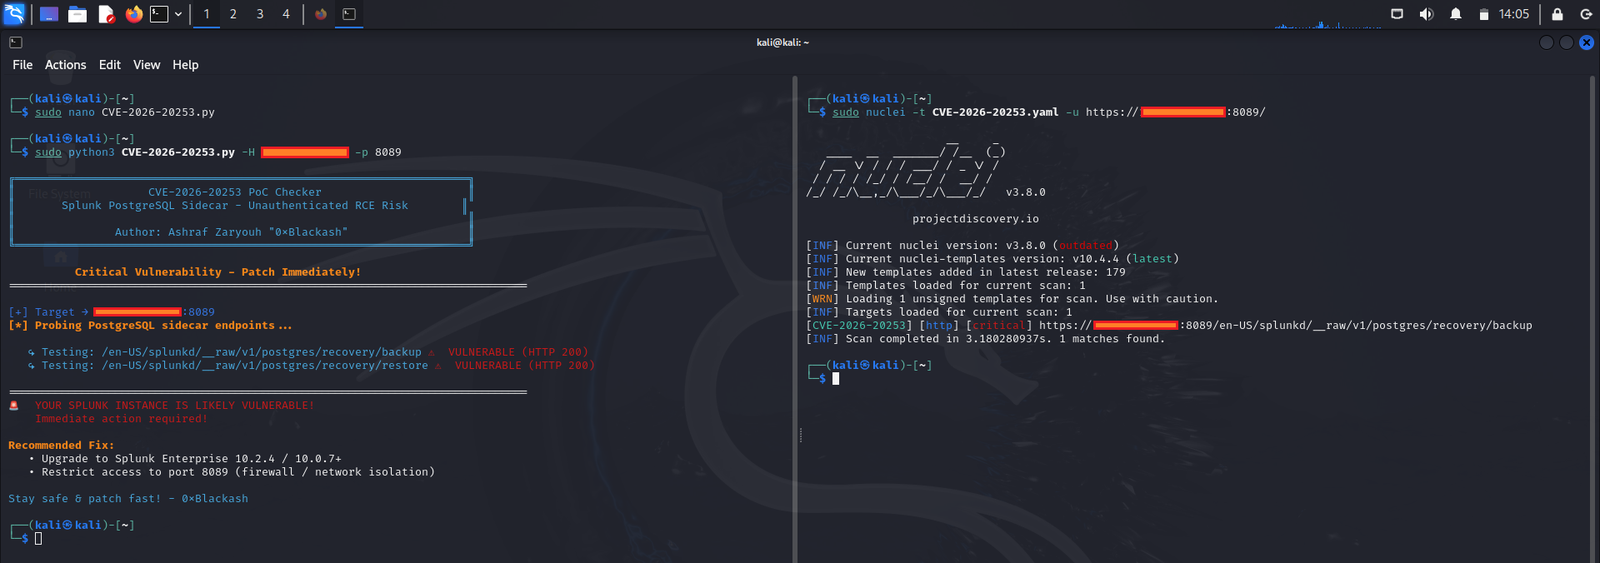
La vulnerabilità risiede in un componente del servizio sidecar PostgreSQL che espone funzionalità sensibili di operazioni sui file.
A causa della mancanza di controlli di autenticazione:
Remote User
        │
        ▼
Accessible Sidecar Endpoint
        │
        ▼
Create Arbitrary Files
        │
        ▼
Truncate Existing Files
        │
        ▼
System Impact
Un attaccante necessita solo dell'accesso di rete al servizio esposto.
Attacker
    │
    ▼
Locate Exposed Splunk Service
    │
    ▼
Connect To PostgreSQL Sidecar
    │
    ▼
Unauthenticated Request
    │
    ▼
Create/Overwrite Files
    │
    ▼
Service Disruption
    │
    ▼
Potential Escalation
Potential exposure of sensitive operational data.
Arbitrary file modification can compromise system integrity.
Critical files may be truncated, causing outages.
SIEM infrastructure may become unreliable or unavailable.
| Versione | Stato |
|---|---|
| < 10.2.4 | Vulnerabile |
| < 10.0.7 | Vulnerabile |
| Versione | Stato |
|---|---|
| < 10.4.2604.3 | Vulnerabile |
| < 10.2.2510.14 | Vulnerabile |
| Prodotto | Versione sicura |
|---|---|
| Splunk Enterprise | 10.2.4+ |
| Splunk Enterprise | 10.0.7+ |
| Splunk Cloud Platform | 10.4.2604.3+ |
| Splunk Cloud Platform | 10.2.2510.14+ |
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
| Metrica | Valore |
|---|---|
| Vettore di attacco | Rete |
| Complessità dell'attacco | Bassa |
| Privilegi richiesti | Nessuno |
| Interazione utente | Nessuna |
| Riservatezza | Alta |
| Integrità | Alta |
| Disponibilità | Alta |
Porte comuni:
8000
8089
8191
5432
http.title:"Splunk"
product:"Splunk"
http.html:"Splunk"
title="Splunk"
body="Splunk"
app="Splunk"
app:"Splunk"
Inatteso:
File creation events
File truncation events
Service failures
Configuration changes
Database sidecar access
find /opt/splunk -mtime -1
find /opt/splunk -size 0
journalctl -xe
grep -Ri "postgres" /opt/splunk/var/log/
Cerca:
Unexpected empty files
Modified configuration files
Splunk restart anomalies
Unauthorized service access
Network connections to sidecar components
Potenziali target:
server.conf
inputs.conf
outputs.conf
authentication.conf
web.conf
1. Discover vulnerable Splunk instance
2. Reach PostgreSQL sidecar endpoint
3. Submit crafted request
4. Create or truncate target file
5. Observe system impact
⚠️ Il codice di exploit weaponizzato è intenzionalmente omesso.
10.2.4+
10.0.7+
VPN-only access
Internal management network
ACL restrictions
Firewall filtering
File creation activity
Configuration modifications
Unexpected service restarts
Management Interfaces
        │
        ├── Internal VLAN
        ├── VPN Access
        └── Zero Trust Controls
Abilita:
Auditd
Sysmon for Linux
EDR telemetry
Network monitoring
Perché questa vulnerabilità è importante:
Compromettere Splunk può influire in modo significativo sulla capacità di un'organizzazione di rilevare attacchi.
CVE-2026-20253/
│
├── README.md
│
├── assets/
│   ├── CVE-2026-20253.png
│   └── screenshots/
│
├── advisory/
│   ├── technical-analysis.md
│   ├── attack-surface.md
│   └── patch-guidance.md
│
├── detection/
│   ├── sigma/
│   ├── yara/
│   ├── splunk-searches/
│   └── hunting-guide.md
│
├── iocs/
│   └── indicators.md
│
└── references/
    └── links.md
Questo repository è destinato esclusivamente a:
Tutte le attività di test devono essere eseguite solo su sistemi di tua proprietà o per i quali sei esplicitamente autorizzato a effettuare valutazioni.
Splunk Enterprise • Critica • CVSS 9.8









