
 #1
Metodologie, framework, reporting e strumenti di automazione per penetration testing.
Raccomandato da Kitploit

 owasp/blt
Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
 wpscanteam/wpscan
Scanner di sicurezza WordPress che rileva vulnerabilità, enumera plugin/temi/utenti e verifica la presenza di password deboli. Si integra con l'API…
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
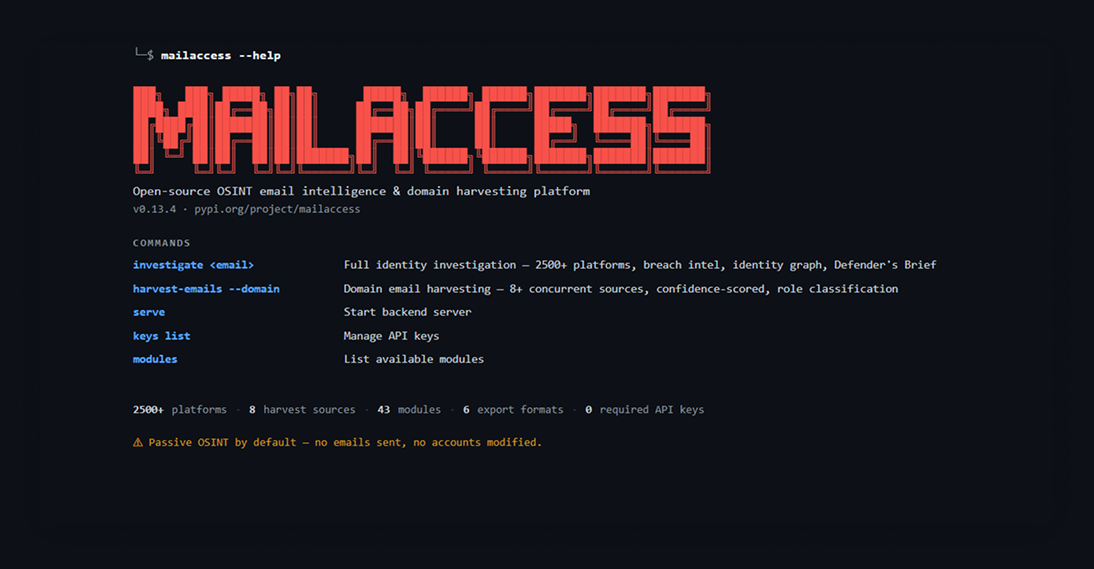 katrielmoses/mailaccess
Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess
 mitmproxy/mitmproxy
Un proxy HTTP interattivo in grado di intercettare e gestire TLS, per penetration tester e sviluppatori di software.
 projectdiscovery/katana
A next-generation crawling and spidering framework.
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 owasp-noir/noir
Dai la caccia a ogni Endpoint nel tuo codice, scopri le Shadow API, mappa la superficie d'attacco.
 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 xalgord/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 hahwul/dalfox
Scanner XSS veloce con analisi dei parametri, fingerprinting WAF e verifica DOM/AST. Supporta il rilevamento di XSS riflessi, memorizzati (stored) e…
 syslifters/sysreptor
Una piattaforma di reporting per penetration testing personalizzabile e potente per professionisti della sicurezza offensiva. Semplifica,…
 1n3/sn1per
Automated penetration testing & attack surface management platform. Recon, scan, exploit, report - 600+ exploits, 90+ integrations, 10K+ detections.
 praetorian-inc/augustus
Framework di test di sicurezza per LLM per rilevare iniezioni di prompt, jailbreak e attacchi avversari — oltre 190 sonde, 28 fornitori, un singolo…
 praetorian-inc/brutus
Strumento veloce per test delle credenziali senza dipendenze in Go. Esegui brute force su SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB e oltre 20…

 rdelasierra-uy/portfolio
Vetrina professionale: writeup di Hack The Box, report, casi di studio GRC (ISO 27001/27002/27005/27035, ISO 31000 + MAGERIT), script di hardening e…








