Skip to content
KitploitKITPLOIT
StrumentiExploitsBlog
Log in
Invia
StrumentiExploitsBlog
Invia

Strumenti di Hacking, PenTest e Cybersecurity per il tuo Arsenale di Sicurezza!

Kitploit è una directory di strumenti di hacking, cybersecurity e pentesting. Scopri gli ultimi aggiornamenti dei progetti per trovare vulnerabilità, analizzare sistemi, automatizzare i test e rafforzare la tua sicurezza.

FeedContattoPrivacy© 2026 Kitploit

Directory degli strumenti

Categorie

Vedi tutte le categorie
Loading categories
Strumenti/GitHubGitHub/katrielmoses/mailaccess
OSINT (Open Source Intelligence)ReconnaissanceVulnerability AnalysisData ExfiltrationForensicsInformation GatheringPenetration TestingSocial EngineeringThreat IntelligenceIdentity & Access Management (IAM)Email Harvesting
319352211 giorno faRevisionato da Kitploit
Condividi
GitHub
katrielmoses/mailaccess

MailAccess

Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess

Vedi Repository
Contenuto non disponibile nella lingua richiesta. Visualizzazione della versione inglese.

Let's connect
X: @delzynkatriel LinkedIn: /in/katriel-moses

MailAccess: email recon that shows its work

License: MIT Python 3.10+ Docker Compose PyPI version PyPI downloads

mailaccess.pro  ·  Docs  ·  PyPI  ·  Changelog

Open-source email OSINT and email scraper. One email in, every account behind it: 82 modules check 5,300+ platforms, and every finding says how it was found and how sure we are. One domain in, every public email at the company. Run it on your own machine, or use it hosted at mailaccess.pro.


Powered by Netlas: see what runs on every host behind a domain Powered by ipgeolocation.io: IP geolocation and threat intel for every IP Powered by WhoisFreaks: who owned a domain, and what else they registered Partnered with IPBurger: dedicated ISP IPs that stay yours, built for recon Partnered with Mango Proxy: residential IPs that keep big harvests clean

Built for security researchers, OSINT analysts and penetration testers working under authorization. Read DISCLAIMER.md before use.
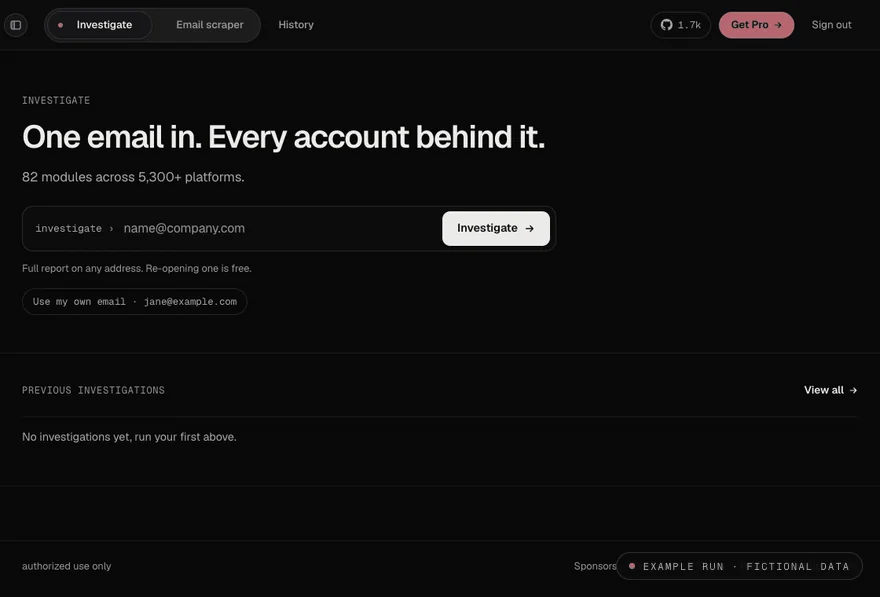
See it run

Example run on the web app: jane@example.com is investigated live, accounts appear as each check returns, then the report opens

Example run with fictional data ([email protected]). The live view, then the report it opens into.

Install

pip install mailaccess
mailaccess investigate [email protected]

Python 3.10+. The CLI starts and stops its backend for each run. Use mailaccess serve for a persistent server, mailaccess[ml] for spaCy name classification, and mailaccess[browser] (then playwright install chromium) for the optional headless-browser checks. Docker and self-hosting: docs/self-hosting.md.

Quick start

mailaccess investigate [email protected]                  # every account behind an email
mailaccess investigate [email protected] -o report.html   # save the report (also .pdf, .md, .json)
mailaccess harvest-emails --domain example.com           # every public email at a domain
mailaccess find-email --name "Jane Doe" --domain example.com
mailaccess login                                         # sign in for your free key
mailaccess doctor                                        # check your setup
mailaccess keys set HIBP_API_KEY your-key                # optional providers
mailaccess upgrade

Pipelines, stdin, JSONL and CI: docs/integrations.md.

What it does

Scarica lo strumento

Più Popolari

Vedi tutti →

Scopri gli strumenti più utilizzati dalla nostra community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Il toolkit OSINT definitivo: grafo di indagine, punteggio di affidabilità, famiglie di alias, mappa, timeline e report. 49 moduli, oltre 400 siti, nessuna chiave API richiesta.

    717
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # App di esecuzione con un tocco GhostLock (CVE-2026-43499)

    504
  • 3

    ARTEX

    baarai/artex

    Piattaforma di penetration testing autonoma multi-agente basata su LLM con agenti planner/worker, grafi di asset e di esplorazione, registrazione del traffico MITM e retesting delle vulnerabilità.

    402
  • 4

    redforge

    cybersecurity91/redforge

    Toolkit red team lato browser con 102 strumenti offline per ricognizione, generazione di payload, attacchi alle credenziali, crittografia, codifica e reportistica dell'engagement.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Il sistema d'azione per la cybersecurity nativa AI—dove l'intento diventa esecuzione governata, le evidenze diventano memoria operativa, e ogni operazione migliora la successiva.

    260
  • 6

    antifox

    antifox-ai/antifox

    Piattaforma multi-agente di penetration testing autonoma basata sull'IA che esegue ricognizione, scoperta della superficie d'attacco, validazione dello sfruttamento e consegna di report supportati da evidenze.

    259

Esplora tutti gli strumenti

Sfoglia la nostra collezione di strumenti

Vedi tutti gli strumenti →