Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
Outils/GitHubGitHub/msaad00/agent-bom
Vulnerability ScannersContainer SecurityCloud SecurityDevSecOpsSecret DetectionThreat IntelligenceSupply Chain SecurityMisconfigurationAI Security
GitHubmsaad00/agent-bom

agent-bom

AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code, containers, cloud and AI. Self-host free; local scans need no account.

29788il y a 16h 14mVérifié par Kitploit
Voir le dépôtSite web
Partager
Contenu non disponible dans la langue demandée. Affichage de la version anglaise.

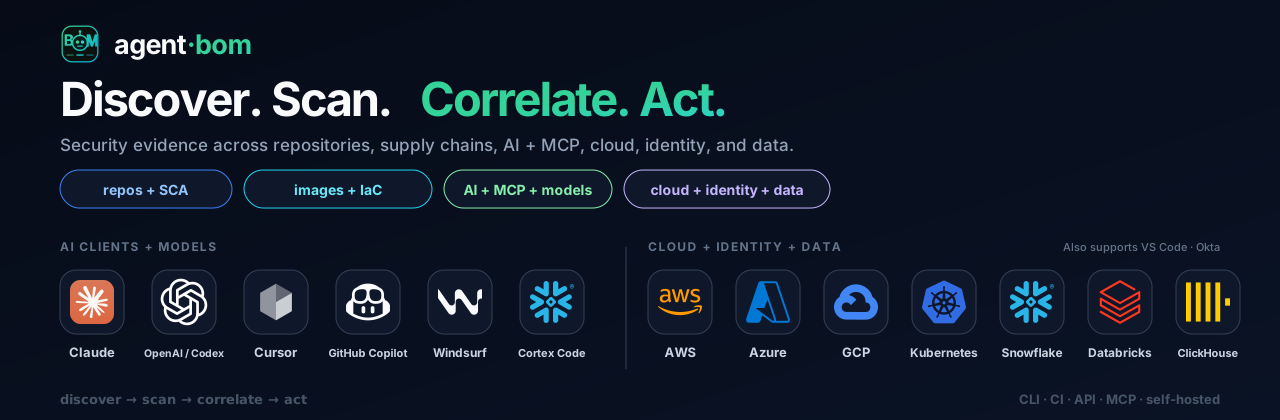
agent-bom — AI supply-chain BOM: supported agents, MCP servers and AI packages, and what each one can reach.

Build PyPI Python 3.11 through 3.14

Apache-2.0 license OpenSSF Scorecard

AI supply-chain BOM: supported agents, MCP servers and AI packages, and what each one can reach.

For AppSec teams and developers who run Claude Code, Cursor, Codex or any MCP client: see which agents, MCP servers, tools and packages are installed, which are vulnerable, and what each one can reach. Local scans need no account.

Quick start · Try in browser · Laptop → team → org · Product tour · Docs

Quick start

From the repository you want to inspect, with uv installed:

uvx agent-bom scan . -f html -o agent-bom-report.html

Open agent-bom-report.html for inventory, findings and fix guidance. Run it again later to see what changed. No MCP configuration in the project? Package findings still apply.

No project handy? uvx agent-bom scan --demo --offline scans a bundled sample. Exit 1 is expected there: the sample trips the security gate. Elsewhere, a non-zero exit can mean a security gate or incomplete assessment; inspect the report and coverage (exit codes, first-run guide).
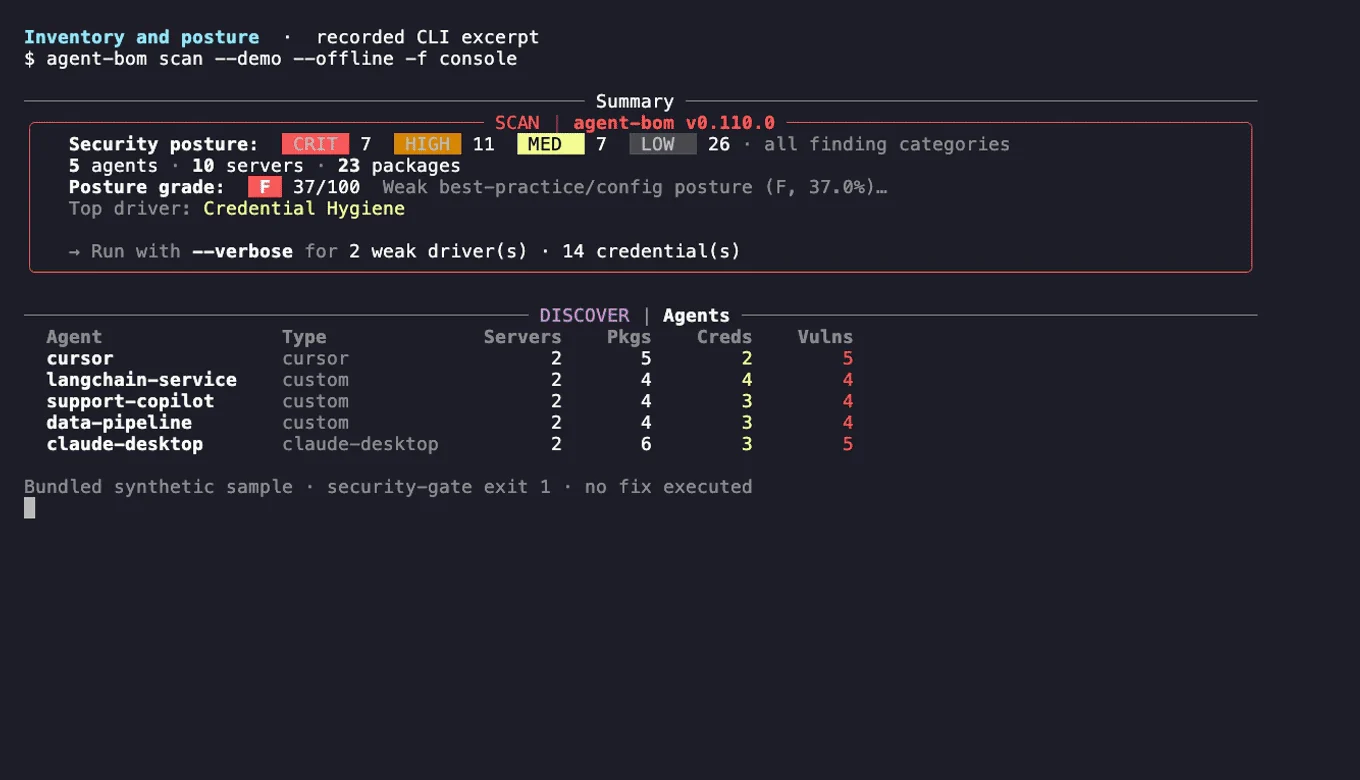
Recorded agent-bom CLI showing sample findings and remediation guidance; no fix executed

What the scan reads and what it does not establish

The scan stays inside this repository: packages, MCP configuration, secrets and personal data, skills and IaC. It does not read agent configuration elsewhere on the machine. Missing evidence is reported as partial, not clean. See what a scan does and does not establish.

From laptop to team to org

  • On your laptop: uvx agent-bom scan . for findings with fixes and a delta on every rescan; claude mcp add agent-bom -- uvx agent-bom mcp server to use agent-bom as a tool inside your coding agent (MCP server, plugins).
  • In your team: uses: koda-ai-studio/agent-bom@v0 on pull requests and a weekly schedule: for a PR gate with a findings comment, SARIF in code scanning and a weekly rescan that catches new CVEs in unchanged code (GitHub Action).
  • Across your org: agent-bom up locally, then Docker Compose or the Helm chart from oci://ghcr.io/koda-ai-studio/charts/agent-bom for retained scans, one graph of agents, MCP servers, packages and credentials, SSO and audit in your own infrastructure (self-host).

All three are free under Apache-2.0 and are adoption paths, not editions. There is no managed cloud offering today; community support runs on GitHub (deployment chooser, support model).

Why an AI supply-chain BOM

A CVE in an AI package, a poisoned tool description or an over-scoped credential matters by what the agent that loads it can reach. A package SBOM stops at packages; agent-bom records the chain, agent → MCP server → tool → package → credential → data, and keeps the evidence for every edge.

Sample production AI environment: Document Intake Agent uses a document-tools MCP server that depends on pillow 9.0.0, linked to KEV-listed CVE-2023-4863; Support Triage Agent uses a ticketing MCP server that references TICKETING_API_KEY, which can access a customer ticket archive

Sample data. What the sample shows

What it covers

Agents and MCP servers, models and AI platforms, dependencies, code, containers and IaC, cloud and data platforms, and a runtime MCP proxy and gateway. Exports are SARIF, CycloneDX, SPDX, JSON and HTML.


Coverage by area
Télécharger l’outil

Populaires

Voir tout →

Découvrez les outils les plus utilisés par notre communauté.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 La boîte à outils OSINT ultime : graphe d'enquête, notation de confiance, familles d'alias, carte, chronologie et rapports. 49 modules, plus de 400 sites, aucune clé API requise.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Application d'exécution en un clic GhostLock (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    Plateforme autonome de tests d'intrusion multi-agents basée sur des LLM, avec agents planificateur/ouvrier, graphes d'actifs et d'exploration, enregistrement du trafic MITM et retest des vulnérabilités.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Boîte à outils red team côté navigateur avec 102 outils hors ligne pour la reconnaissance, la génération de payloads, les attaques par identifiants, la cryptographie, l'encodage et le reporting d'engagement.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    Plateforme CSIRT qui ingère les rapports Shadowserver dans MongoDB et les rejoue sous forme de cartes interactives, d'analyses, de constats, d'avis et de tableaux de bord exécutifs.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Le système d'action pour la cybersécurité native IA—où l'intention devient une exécution gouvernée, les preuves deviennent une mémoire opérationnelle, et chaque opération améliore la suivante.

    264

Explorer tous les outils

Parcourez notre collection d'outils

Voir tous les outils →