
 #1
Outils de rétro-ingénierie binaire, désassemblage, décompilation et patching.
Recommandé par Kitploit

 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 frida/frida-gum
Bibliothèque d'instrumentation et d'introspection multiplateforme écrite en C
 onekey-sec/unblob
Extraire des fichiers de tout type de format conteneur
 rovellipaolo/ninjadroid
Ninja Reverse Engineering sur les paquets APK Android
 google/silifuzz
Fuzz les implémentations de CPU en générant des entrées de test à partir de proxies logiciels, puis les exécute sur du matériel réel pour détecter…
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 skylot/jadx
Outil en ligne de commande et avec interface graphique pour décompiler les fichiers Android Dex et APK en code source Java lisible, avec décodage des…
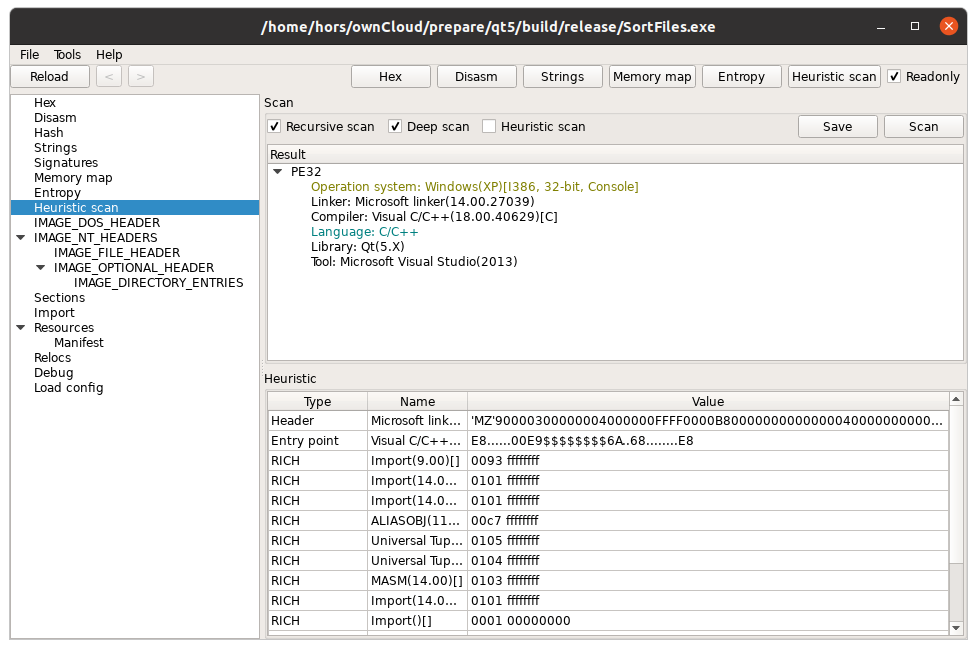 horsicq/xpeviewer
Visionneuse/éditeur de fichiers PE pour Windows, Linux et MacOS.
 icsharpcode/ilspy
Décompilateur .NET avec prise en charge de la génération PDB, ReadyToRun, Metadata (&plus) - multiplateforme !
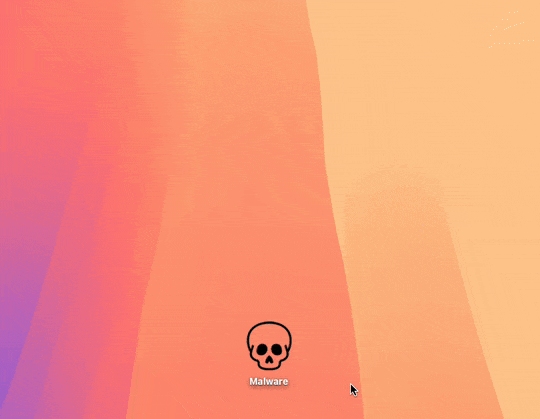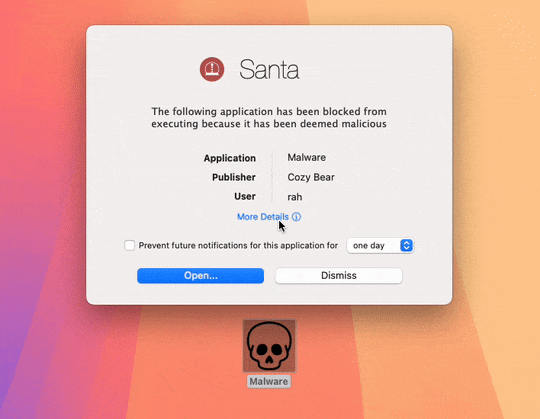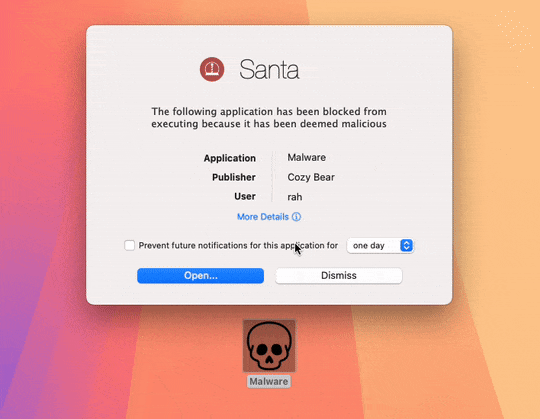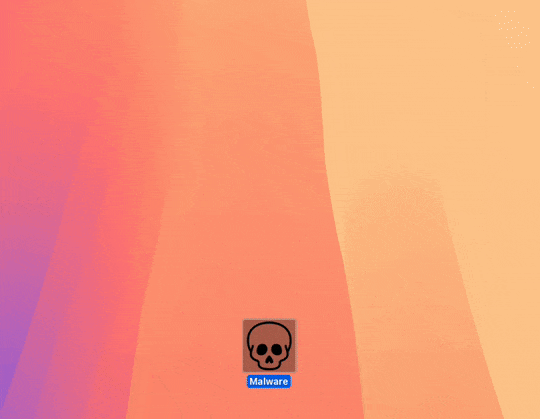 northpolesec/santa
Un système d'autorisation d'accès aux binaires et aux fichiers pour macOS.
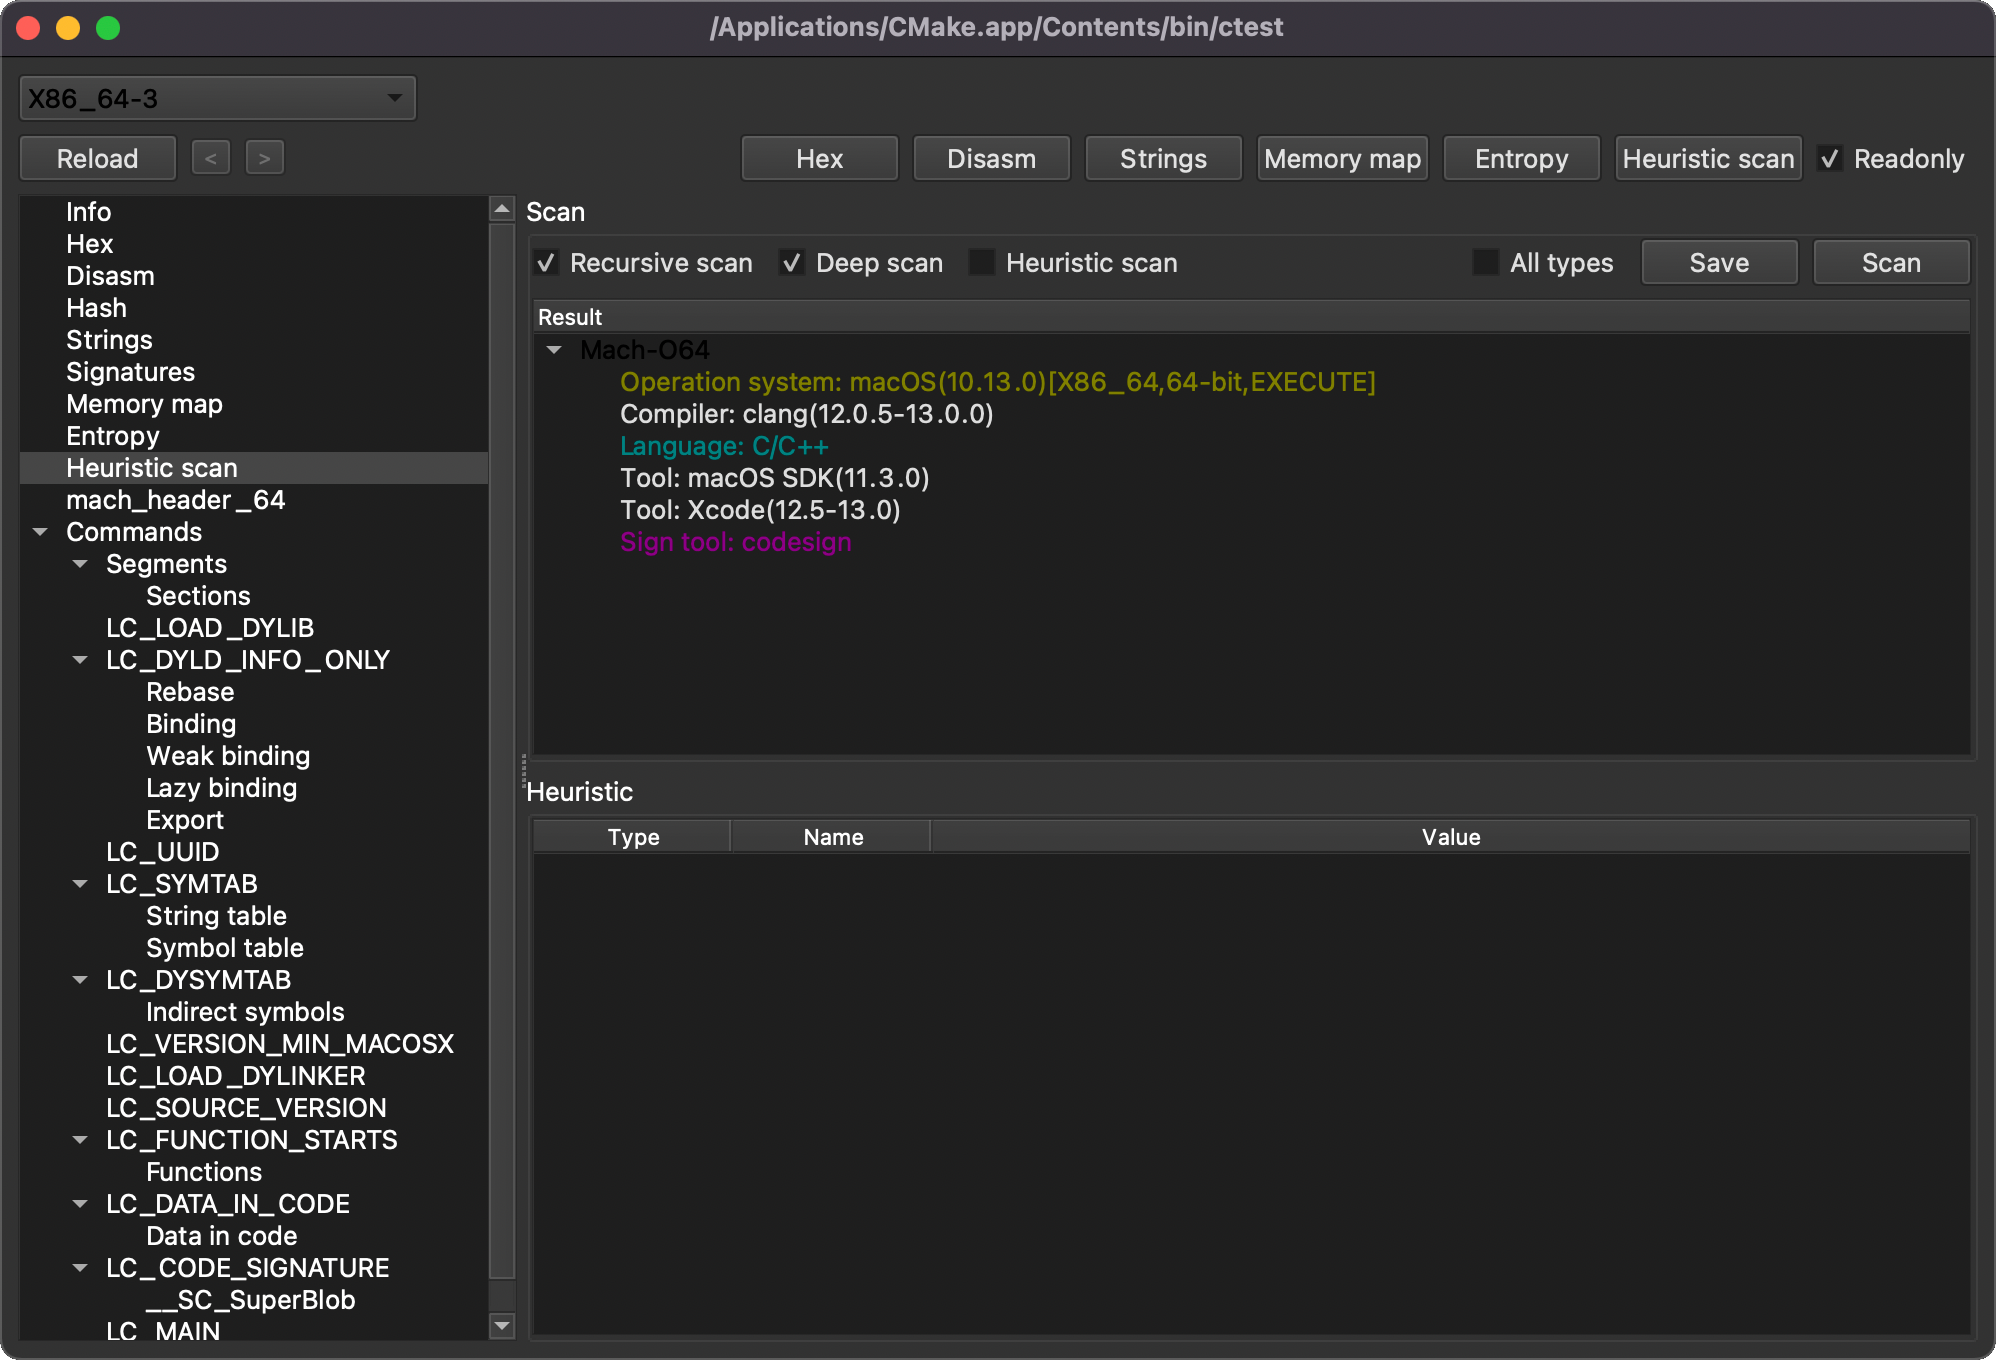 horsicq/xmachoviewer
XMachOViewer est un visualiseur de fichiers Mach-O pour Windows, Linux et MacOS.
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 mfthomps/resim
Logiciel de rétro-ingénierie utilisant un simulateur système complet
 upx/upx
UPX - l'emballeur ultime pour exécutables
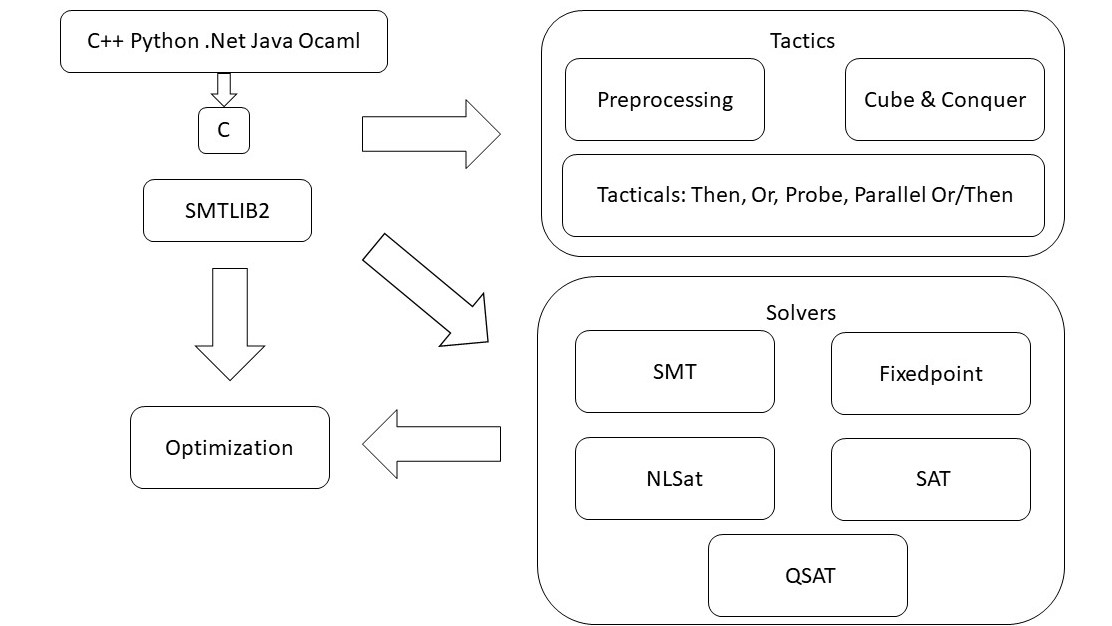 z3prover/z3
High-performance SMT solver for automated theorem proving, constraint solving, and program verification. Supports multiple theories and language…
 morluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.








