morluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.

English · 简体中文 · 繁體中文 · 日本語 · 한국어 · Türkçe · Русский · Tiếng Việt · ไทย · Deutsch · Español · Français · Українська · Polski · Português (Brasil) · العربية · فارسی · Bahasa Indonesia · Italiano · Ελληνικά · മലയാളം · Roman Urdu · Română · Български
See a feature you like. Understand how it works, down to the binary level.



Quick start · How REA works · What you can analyze · Showcases · Build RL environments · FAQ · Documentation
npx rea-agents setup
[!IMPORTANT] Get REA from morluto/rea, rea.tools, or the rea-agents npm package. Follow the installation and release links from these official sources. A similar repository name or copied README does not establish that a download is official.
See a feature in an app that you want in your own product? Ask your agent to investigate it with REA. It can inspect the app without its source code, explain how the feature works, show the evidence, and build a version for your project.
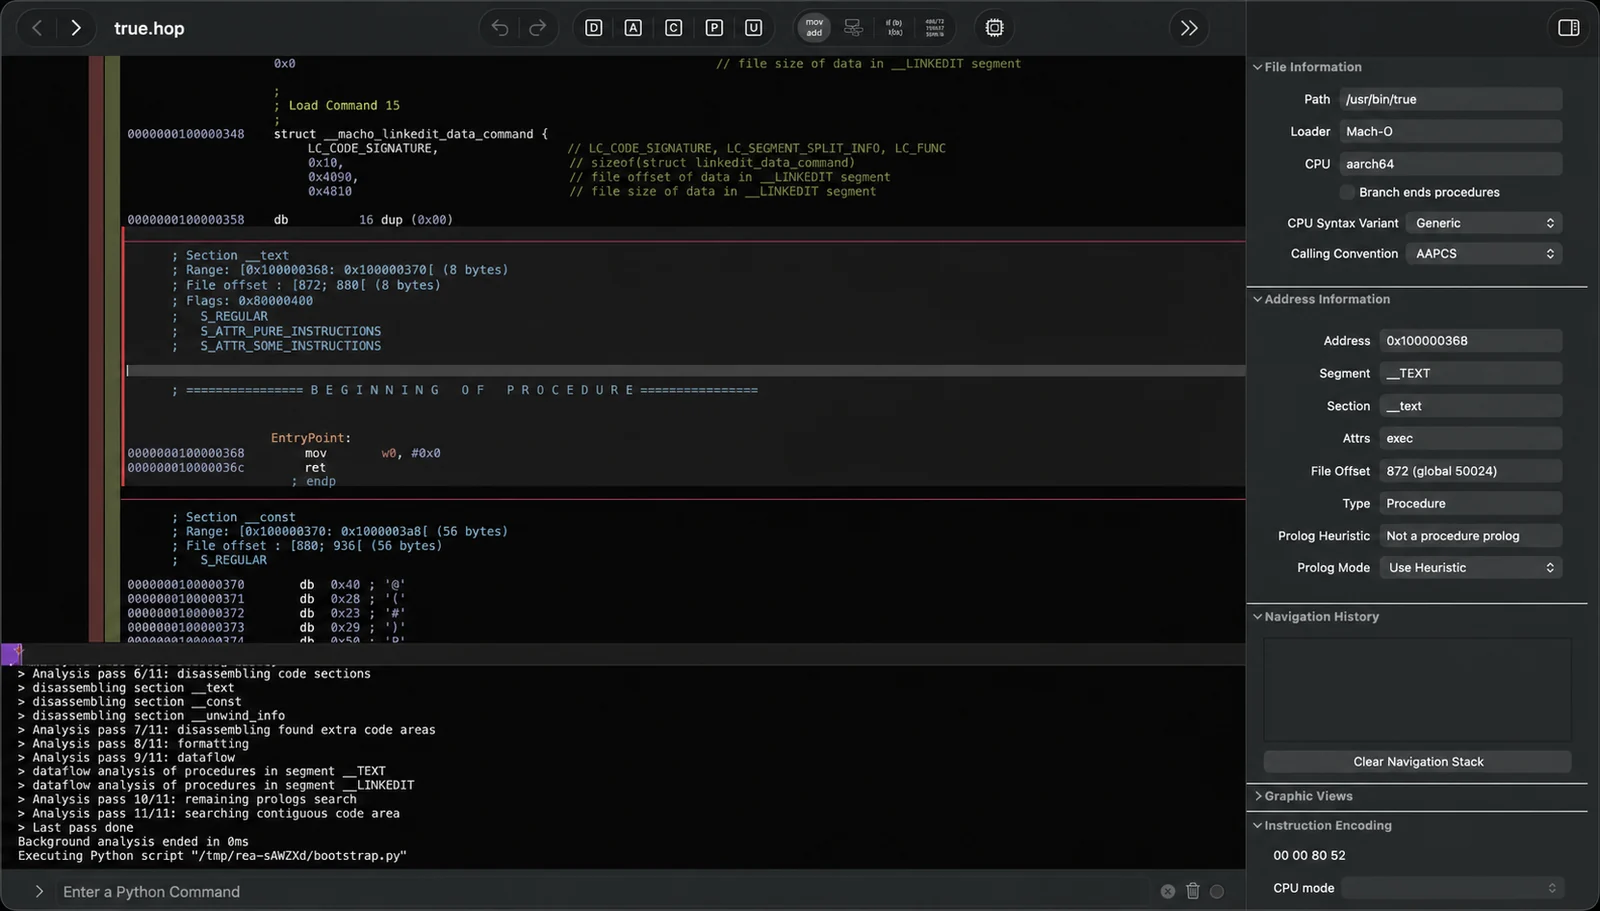
REA connects your agent to tools for inspecting native binaries, JavaScript and Electron apps, .NET assemblies, and websites. You can also use the same tools from your terminal. Analysis runs locally, and results include the evidence and limitations behind each conclusion.
Setup registers REA with your agent and installs matching workflow instructions. Native analysis can use an existing Hopper, Ghidra, IDA or Kuna installation; setup can optionally install Hopper with approval. Static JavaScript analysis needs no native analysis engine.
Visit the REA website for setup instructions, illustrated guides, and real case studies.
On Linux, Ghidra, JADX, firmware tool launches and static JavaScript/Electron
analysis require a procps-compatible system ps for process ownership
checks. Recovery steps are in docs/getting-started/installation.md under
"Linux owned-process prerequisite".
With Node.js and npm installed, run:
npx rea-agents setup
Choose your agents, review the proposed changes, and approve them. Setup adds REA's MCP server and matching workflow instructions, with backups of existing configuration. Restart your agent afterward. Setup records the selected runtime and REA entry script directly. If acquired through a package runner, keep its cache entry available. Run package acquisition from a trusted directory outside the target project. Installation and recovery details are in the setup guide below.
Setup supports Claude Code, Codex, Cursor, Gemini CLI, Grok Build and other agents. See installation and setup for provider configuration, manual MCP registration, Claude Code/Codex plugins, and the Cursor Marketplace plugin.
MCP advertises compact input schemas to reduce context overhead; guidance a compact schema omits follows the tool description. The full tool set and canonical server validation are unchanged. See "Compact input schema profile" in the MCP contracts guide.
Output schemas are omitted from tools/list by default: no model API reads
them, and REA validates every result itself. Set
REA_MCP_OUTPUT_SCHEMA_PROFILE=compact to advertise each output schema within
a 4,096-byte budget. Both settings keep canonical server-side validation and
complete structured results. See "Output schemas" in the MCP contracts guide.
Understand how search works in the Notes app, show me the evidence, and build a
similar feature for my project.
Replace Notes with your target app and the feature you want to understand.