

Skip to content
KitploitKITPLOIT
HerramientasExploitsBlog
Log in
Enviar
HerramientasExploitsBlog
Enviar

¡Herramientas de Hacking, PenTest y Ciberseguridad para tu Arsenal de Seguridad!

Kitploit es un directorio de herramientas de hacking, ciberseguridad y pentesting. Descubre las últimas actualizaciones de proyectos para encontrar vulnerabilidades, analizar sistemas, automatizar pruebas y fortalecer tu seguridad.

FeedsContactoPrivacidad© 2026 Kitploit

Directorio de Herramientas

Categorías

Ver todas las categorías
Loading categories
NtStrace — Rastreador de llamadas al sistema basado en frida-stalker en Windows (x64). | Kitploit
Herramientas/GitHubGitHub/gmh5225/ntstrace
Análisis Dinámico (Sandboxing)Ingeniería InversaDepuradoresAnálisis de MalwareAnálisis de Binarios
GitHubgmh5225/ntstrace

NtStrace

Rastreador de llamadas al sistema basado en frida-stalker en Windows (x64).

Ver Repositorio
1114hace 2 añosAún no revisado

Más Populares

Ver todos →

Descubre las herramientas más usadas por nuestra comunidad.

Explora todas las herramientas

Explora nuestra colección de herramientas

Ver todas las herramientas →
Compartir

NtStrace

Rastreador de llamadas al sistema basado en frida-stalker en Windows (x64).

[483]NtWaitForWorkViaWorkerFactory
test.exe!0x7ff91fbaf262
[35]NtQueryVirtualMemory
test.exe!0x7ff91fbaf262
[35]NtQueryVirtualMemory
test.exe!0x7ff91fbaf262
[35]NtQueryVirtualMemory
test.exe!0x7ff91fbb06d2
[199]NtCreateThreadEx
[+] Following thread 17876
test.exe!0x7ff91fbb06d2
[7]NtDeviceIoControlFile
[+] Unfollowing thread 17876
test.exe!0x7ff91fbaeee2
[7]NtDeviceIoControlFile
test.exe!0x7ff91fbaeee2
[7]NtDeviceIoControlFile
[+] Unfollowing thread 6344
[+] Unfollowing thread 6124

También puede identificar con precisión los tipos que encubren llamadas al sistema, como el proyecto siguiente.
https://github.com/passthehashbrowns/hiding-your-syscalls
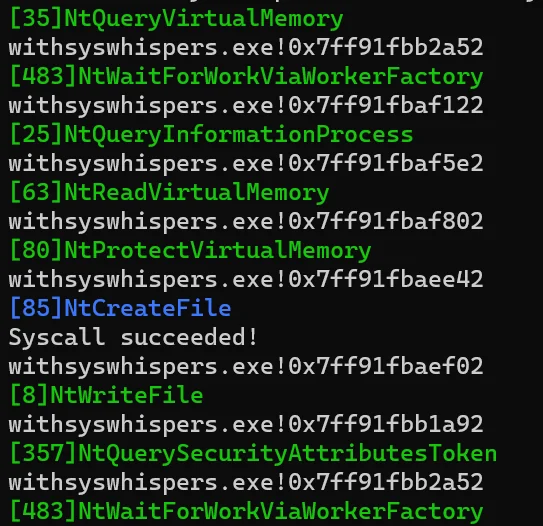
img

Uso

frida -l tracer.js app.exe

Licencia

iostrace

El software original está disponible en
https://github.com/sh1ma/iostrace.

Descargar herramienta