SentinelThread-Forensics

High-speed Windows forensic triage platform that orchestrates the Hayabusa engine to transform raw EVTX logs into prioritized threat timelines with…

High-speed Windows forensic triage platform that orchestrates the Hayabusa engine to transform raw EVTX logs into prioritized threat timelines with…

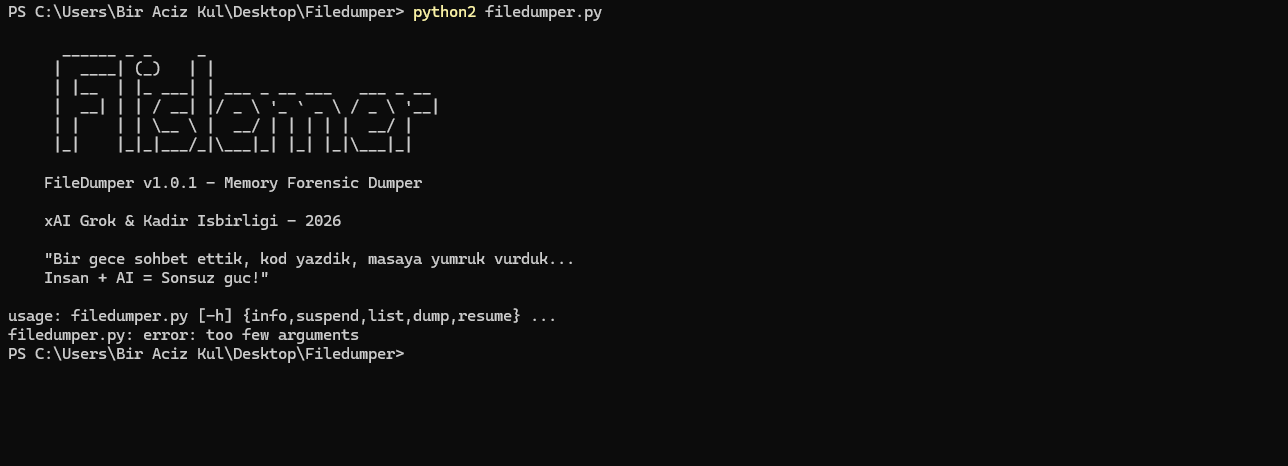
Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…

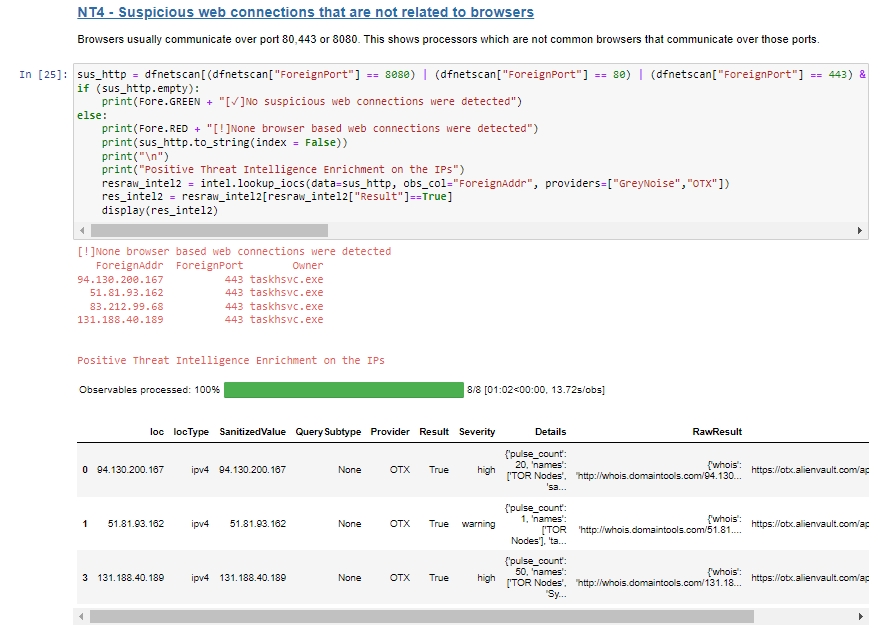
Security sensor for realtime threat detection and protection

Android Logs Events And Protobuf Parser

A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs

PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.

Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)

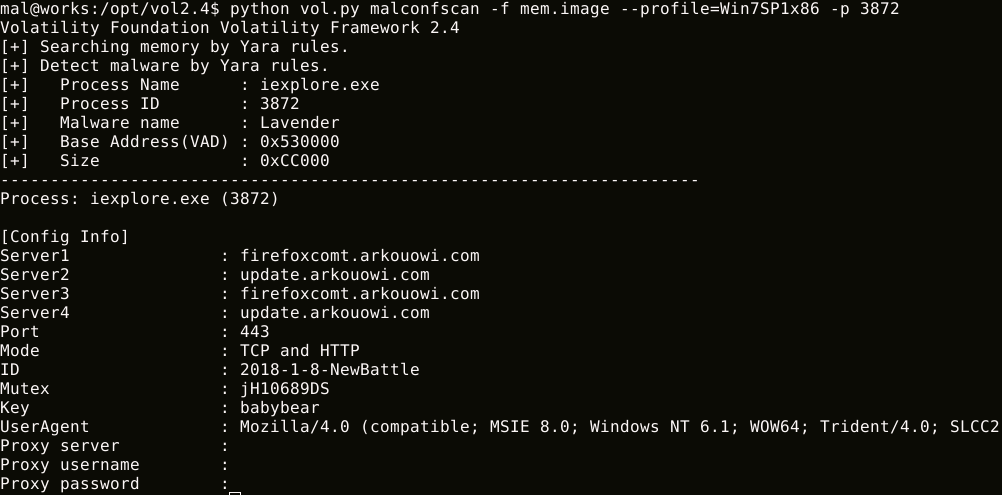
Volatility plugin for extracts configuration data of known malware

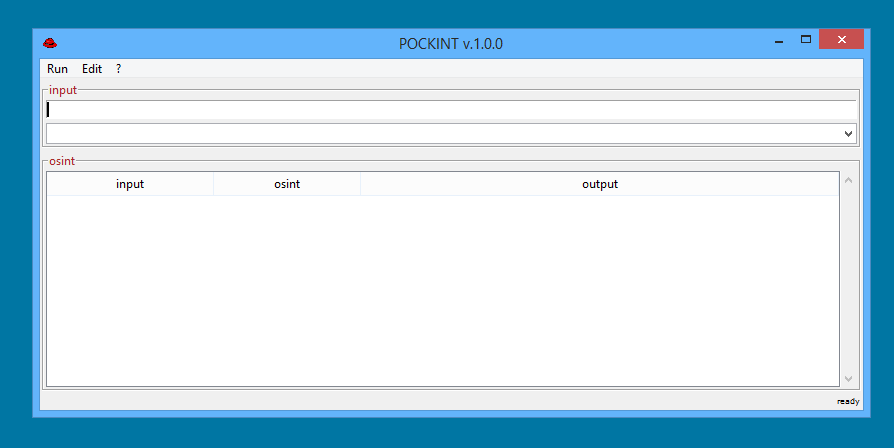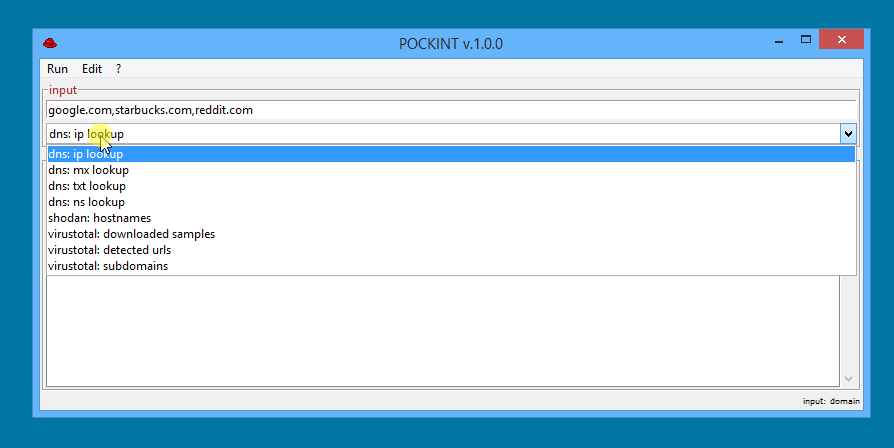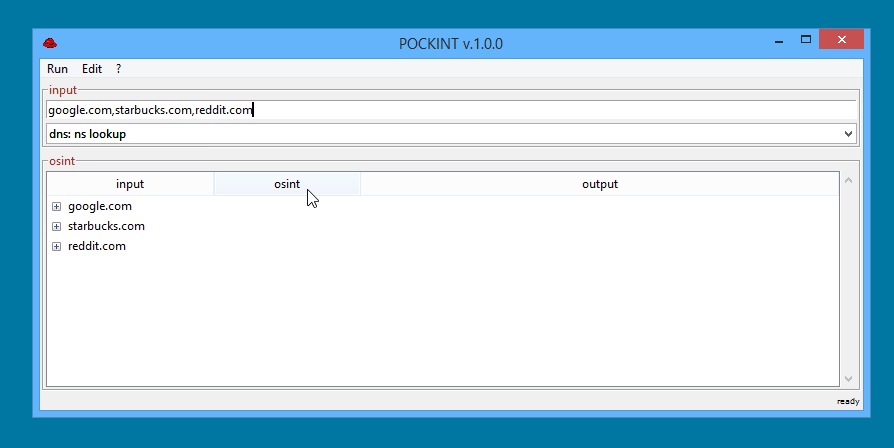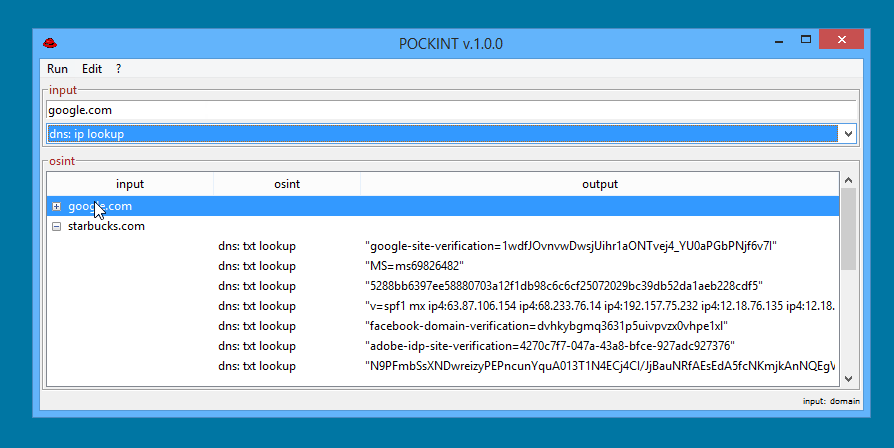
A portable OSINT Swiss Army Knife for DFIR/OSINT professionals 🕵️ 🕵️ 🕵️

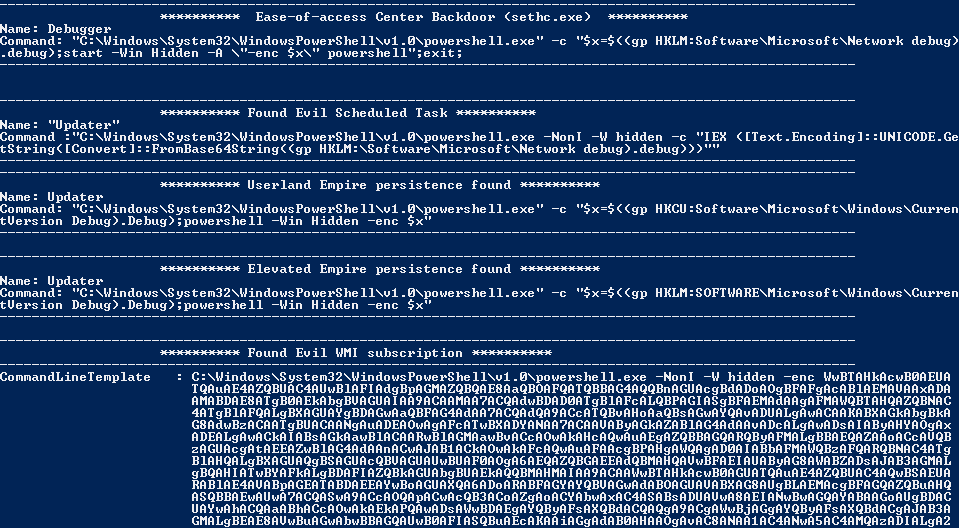
Powershell Empire Persistence finder

Automagically extract forensic timeline from volatile memory dump

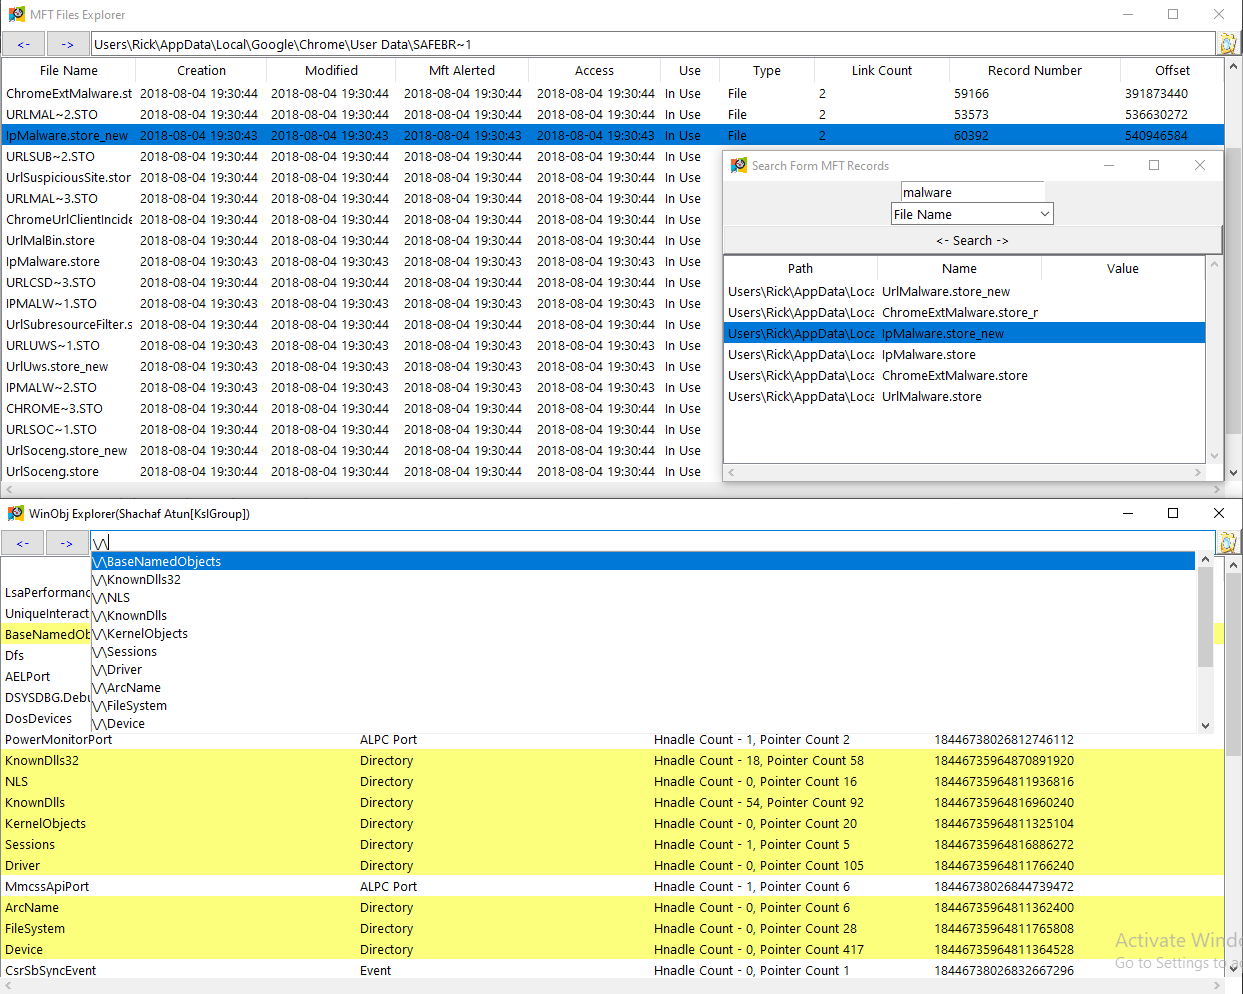
volatility explorer (volatility 2)

A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.

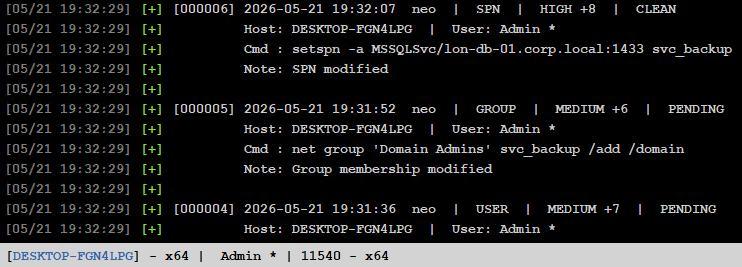
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…

Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…

Filesystem scanner for Log4Shell (CVE-2021-44228) and related CVEs. Detects vulnerable JAR files via hash matching and class presence. Runs…

An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…