
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
52 results
dfirtriage preview

dfirtriage

GitHubtravisfoley/dfirtriage

Digital forensic acquisition tool for Windows based incident response.
digital-forensicsforensicsincident-response+1
3482 years ago
Pegasus-Malware-Scan preview

Pegasus-Malware-Scan

GitHubsobri3195/pegasus-malware-scan

Multi-layered malware scanner combining hash-based verification, behavioral analysis, and sandbox execution for threat detection, incident response,…

educationforensicsincident-response+3
61 year ago
ir-rescue preview

ir-rescue

GitHubdiogo-fernan/ir-rescue

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
digital-forensicsdisk-forensicsforensics+6
4885 years ago
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
digital-forensicsdisk-forensicsforensics+3
5165 years ago
tscopy preview

tscopy

GitHubtrustedsec/tscopy

Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…

data-recoverydigital-forensicsdisk-forensics+2
1034 years ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
digital-forensicsforensicsincident-response+2
4.5k17 days ago
pywintrace preview

pywintrace

GitHubfireeye/pywintrace

Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…

defensive-toolsdigital-forensicsincident-response+2
3053 years ago
Kage-DFIR-toolkit preview

Kage-DFIR-toolkit

GitHubkarim852/kage-dfir-toolkit

Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
defensive-toolsdigital-forensicsforensics+8
3920 days ago
fingerprint preview

fingerprint

GitHubbitranox/fingerprint

Monitoring Registry and File Changes in Windows
digital-forensicsforensicsincident-response
726 months ago
LogonTracer preview

LogonTracer

GitHubjpcertcc/logontracer

Investigate malicious Windows logon by visualizing and analyzing Windows event log

ai-securitydigital-forensicsincident-response+2
3.3k2 months ago
VMkatz preview

VMkatz

GitHubnikaiw/vmkatz

Extract Windows credentials directly from VM memory snapshots and virtual disks
digital-forensicsexploitationforensics+7
1.6k2 days ago
evtx preview

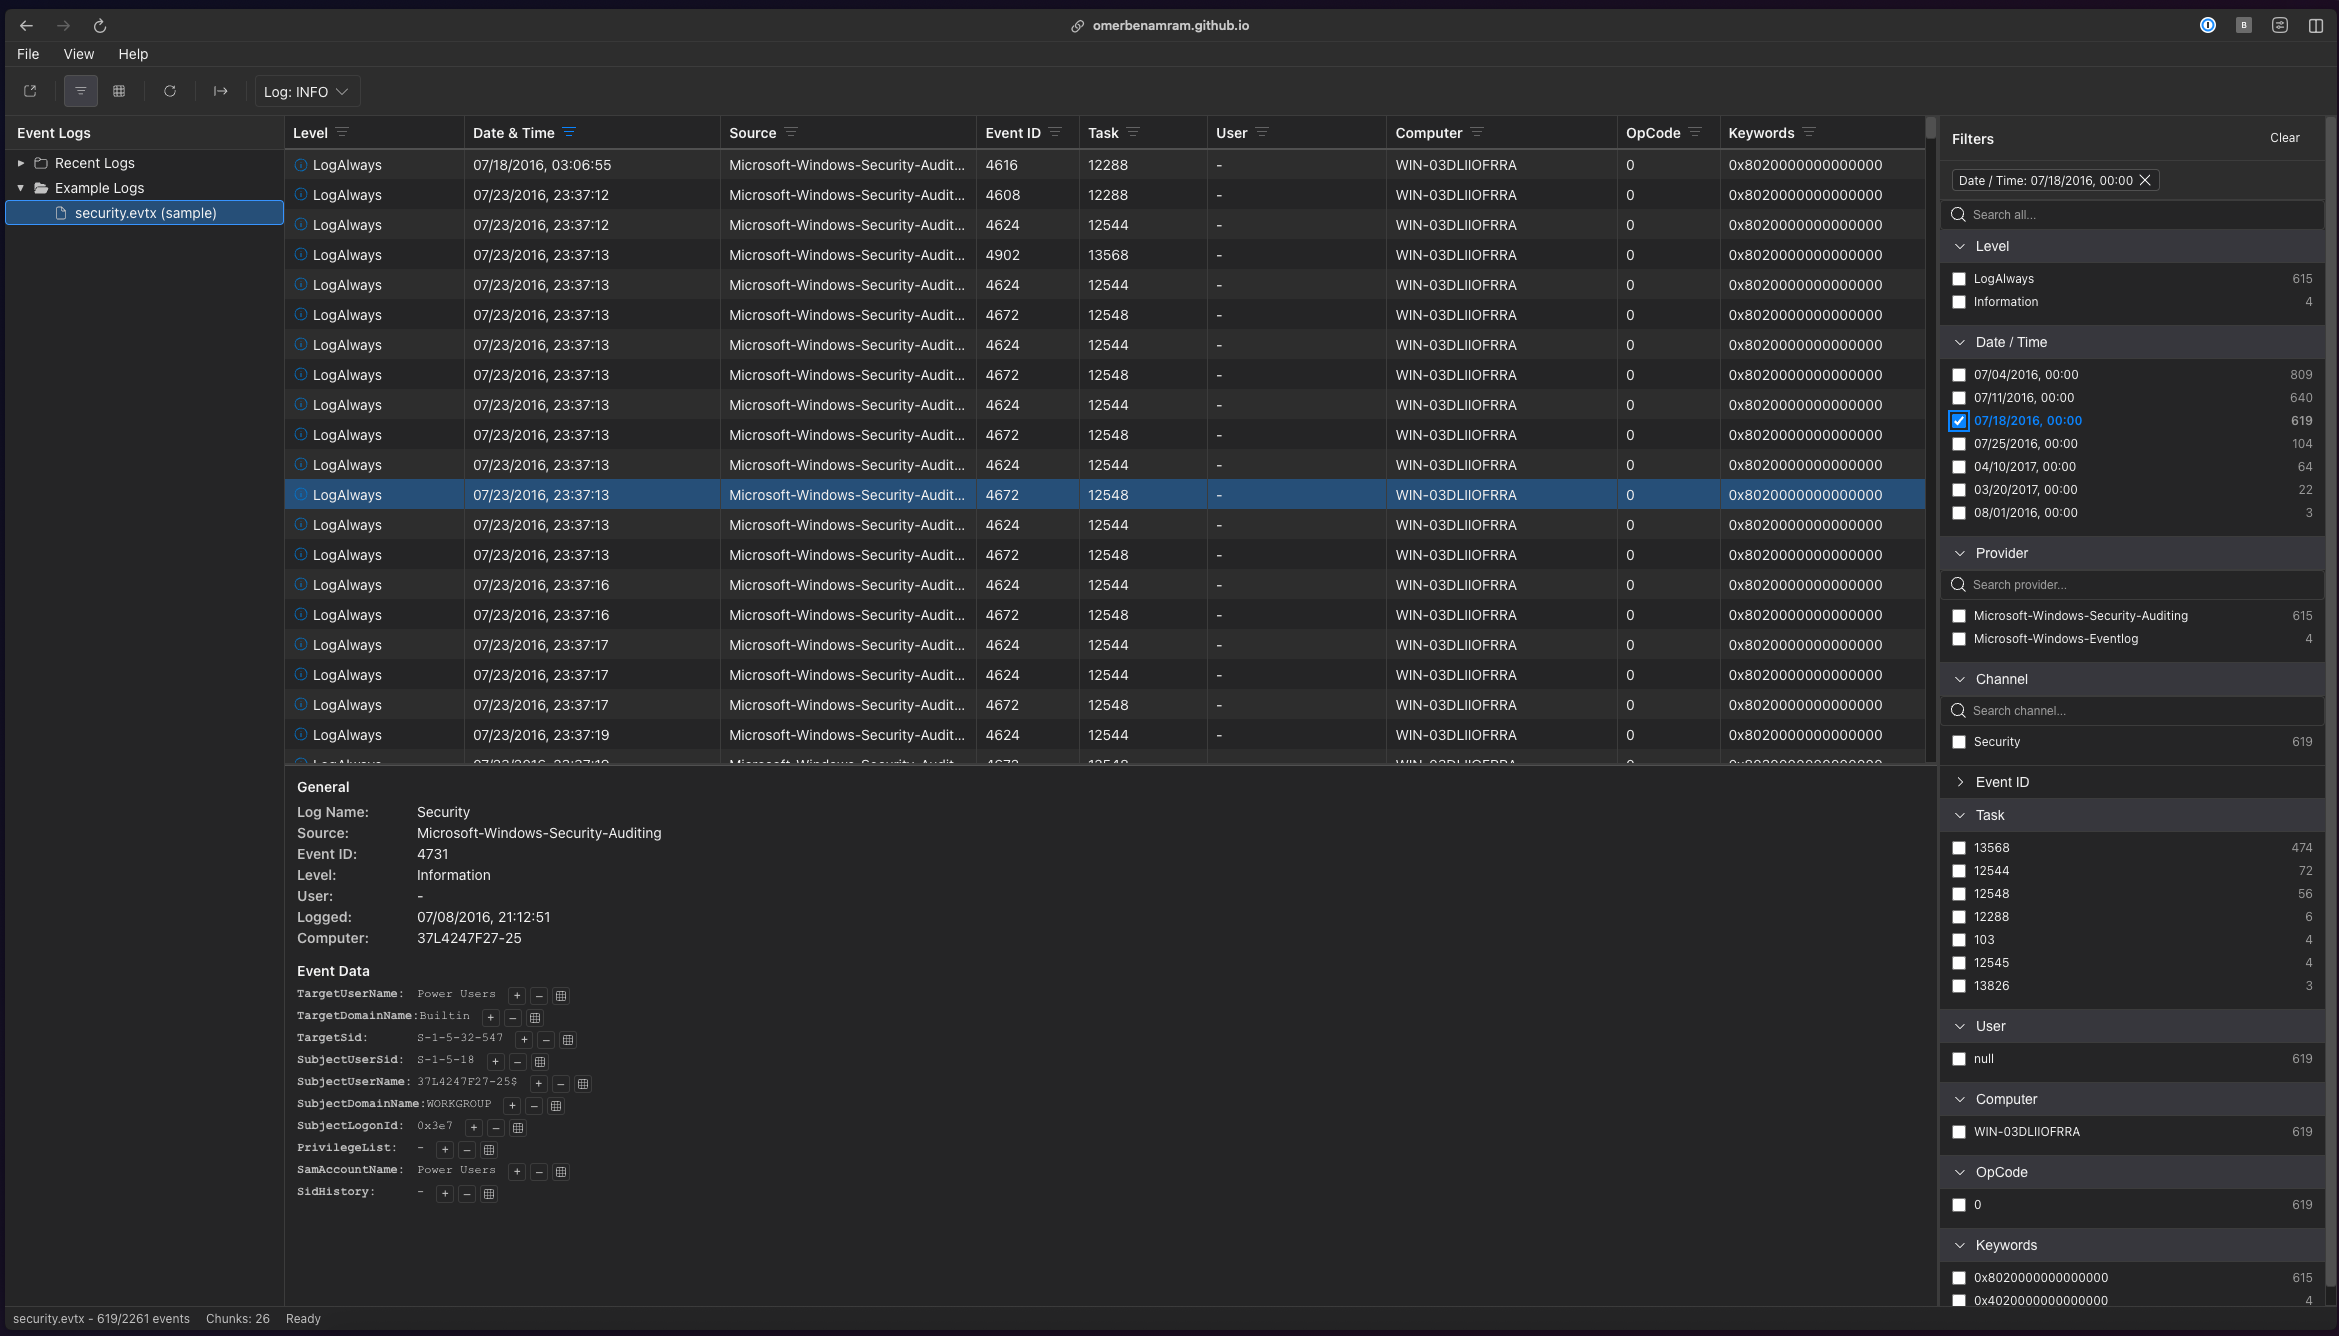
evtx

GitHubomerbenamram/evtx

A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
digital-forensicsforensicsincident-response+1
9678h 3m ago
beagle preview

beagle

GitHubyampelo/beagle

Beagle is an incident response and digital forensics tool which transforms security logs and data into graphs.
digital-forensicsforensicsincident-response+2
1.4k6 years ago
MemProcFS-Analyzer preview

MemProcFS-Analyzer

GitHublethal-forensics/memprocfs-analyzer

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
anomaly-detectiondigital-forensicsincident-response+5
7421 month ago
SuperMem preview

SuperMem

GitHubcrowdstrike/supermem

A python script developed to process Windows memory images based on triage type.
digital-forensicsforensicsincident-response+2
2684 years ago
kdmp-parser preview

kdmp-parser

GitHub0vercl0k/kdmp-parser

A Windows kernel dump C++ parser library with Python 3 bindings.
digital-forensicsforensicsincident-response+1
2171 year ago
larac2shell preview

larac2shell

GitHubakefallonitis/larac2shell

Cross-platform interactive shell for Microsoft Defender for Endpoint Live Response
authenticationcommand-and-controlincident-response+6
166 months ago
mini-shai-hulud-scanner preview

mini-shai-hulud-scanner

GitHubintrudify/mini-shai-hulud-scanner

Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…

forensicsincident-responseioc-management+6
35 months ago
Previous123Next