

 stuub/cve-2024-28995
CVE-2024-28955 Exploitation PoC
 stuub/rcity-cve-2024-27198
CVE-2024-27198 & CVE-2024-27199 PoC - RCE, Admin Account Creation, Enum Users, Server Information
 maverickaayush/onus
Locally-hosted, air-gapped VAPT platform that runs 8 parallel scanning modules, deterministically scores findings with CVSS v3.1, and generates PDF…
 stuub/cve-2024-29895-cactirce-poc
CVE-2024-29895 PoC - Exploiting remote command execution in Cacti servers using the 1.3.X DEV branch builds
 cyberexpert111/blind-ssrf-to-remote-code-execution-shellshock-professional-bug-bounty-report
Professional bug bounty report detailing the exploitation of a Blind SSRF vulnerability leading to Shellshock (CVE-2014-6271) remote code execution,…
 debajyoti0-0/cve-2026-60206
Technical analysis and Proof-of-Concept for CVE-2026-60206, a critical Oracle WebLogic Server SAML authentication bypass vulnerability.
 fevra-dev/claimjumper
Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
 purpleteam-labs/purpleteam-tls-checker
TLS checking component of purpleteam
 purpleteam-labs/purpleteam-orchestrator
Orchestration component of purpleteam
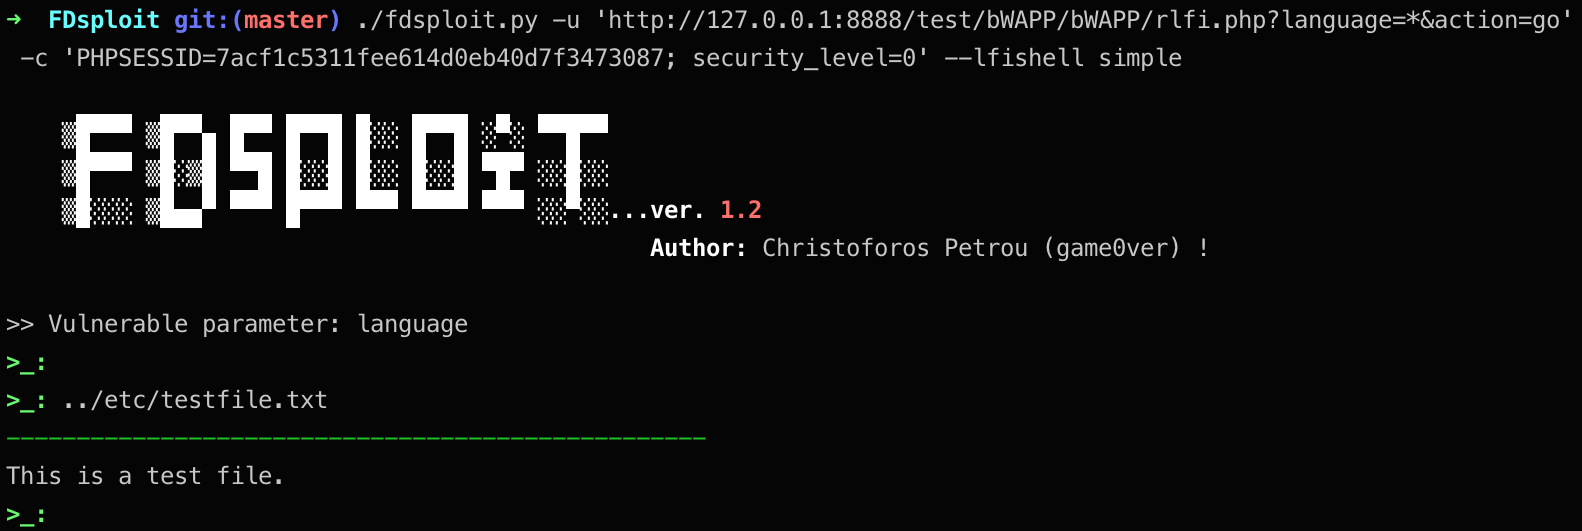 chrispetrou/fdsploit
File Inclusion & Directory Traversal fuzzing, enumeration & exploitation tool.
 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
 digeex/raider
DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…