
die-in-browser
 xoreaxlmbdx/die-in-browser
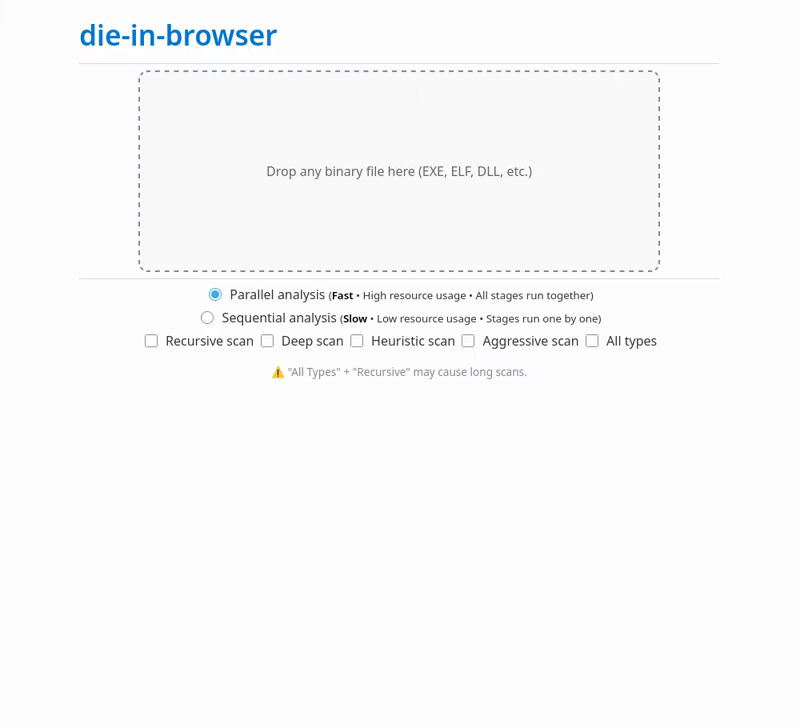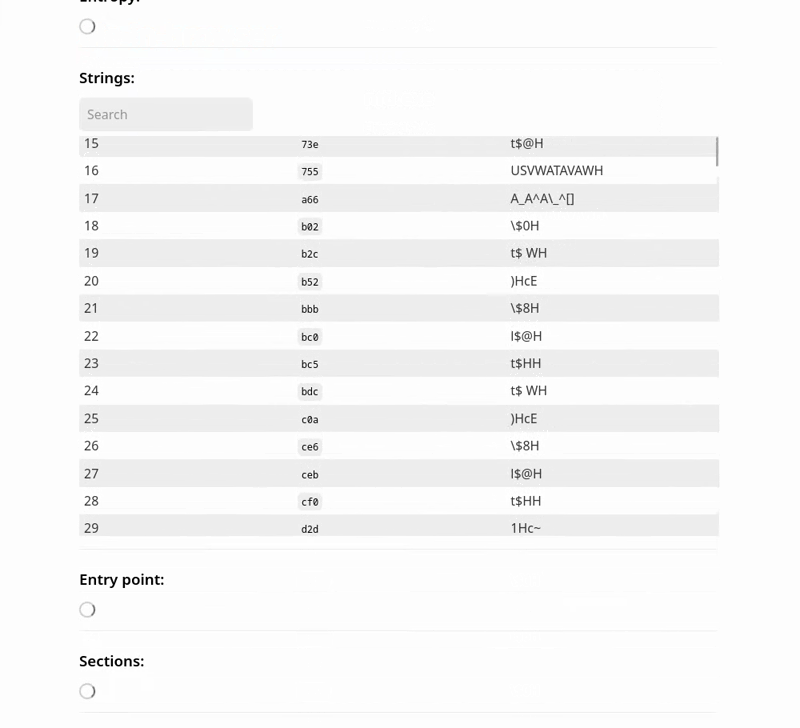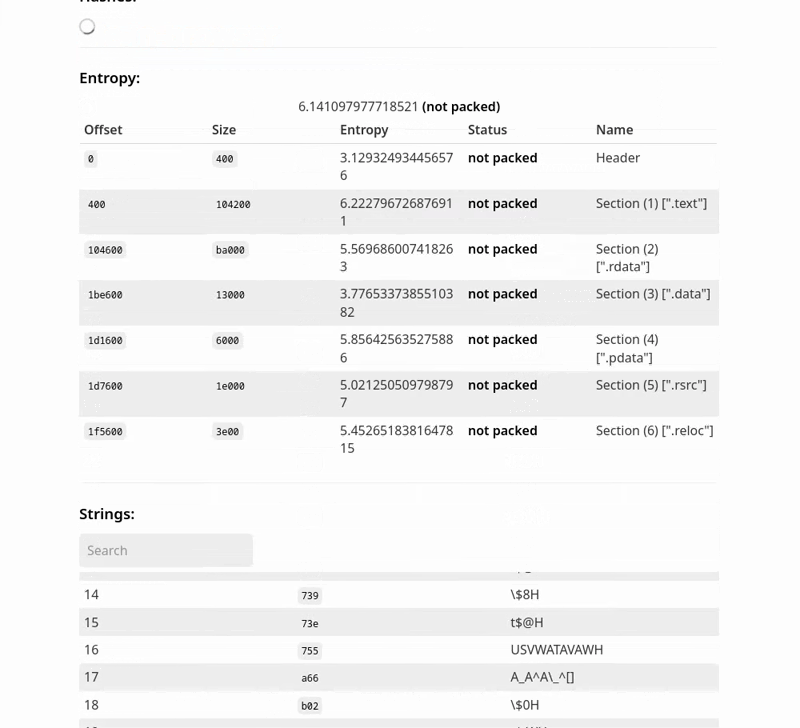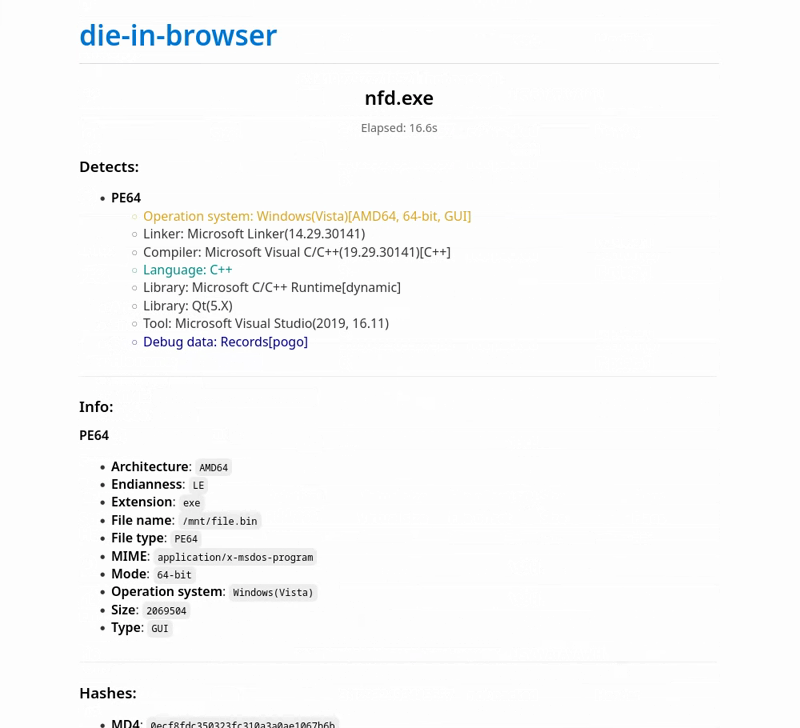
Static binary analysis with Detect It Easy — 100% in your browser, no uploads.
binary-analysisfirmware-analysishash-analysis+3
70
xoreaxlmbdx/die-in-browserStatic binary analysis with Detect It Easy — 100% in your browser, no uploads.
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 hashview/hashview
A web front-end for password cracking and analytics
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
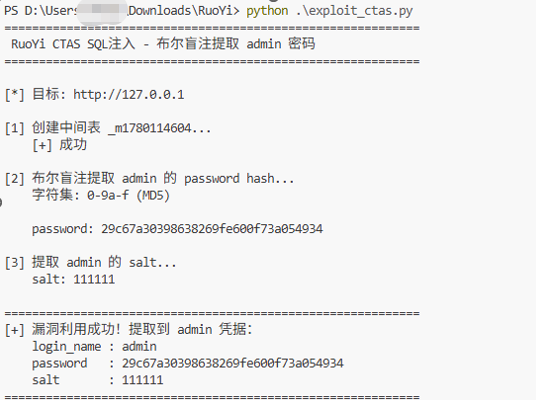 chinesespeople/cve-2026-52614
There is a SQL injection vulnerability in the backend of Ruoyi v4.8.3
 ge0rg3/requests-ip-rotator
A Python library to utilize AWS API Gateway's large IP pool as a proxy to generate pseudo-infinite IPs for web scraping and brute forcing.
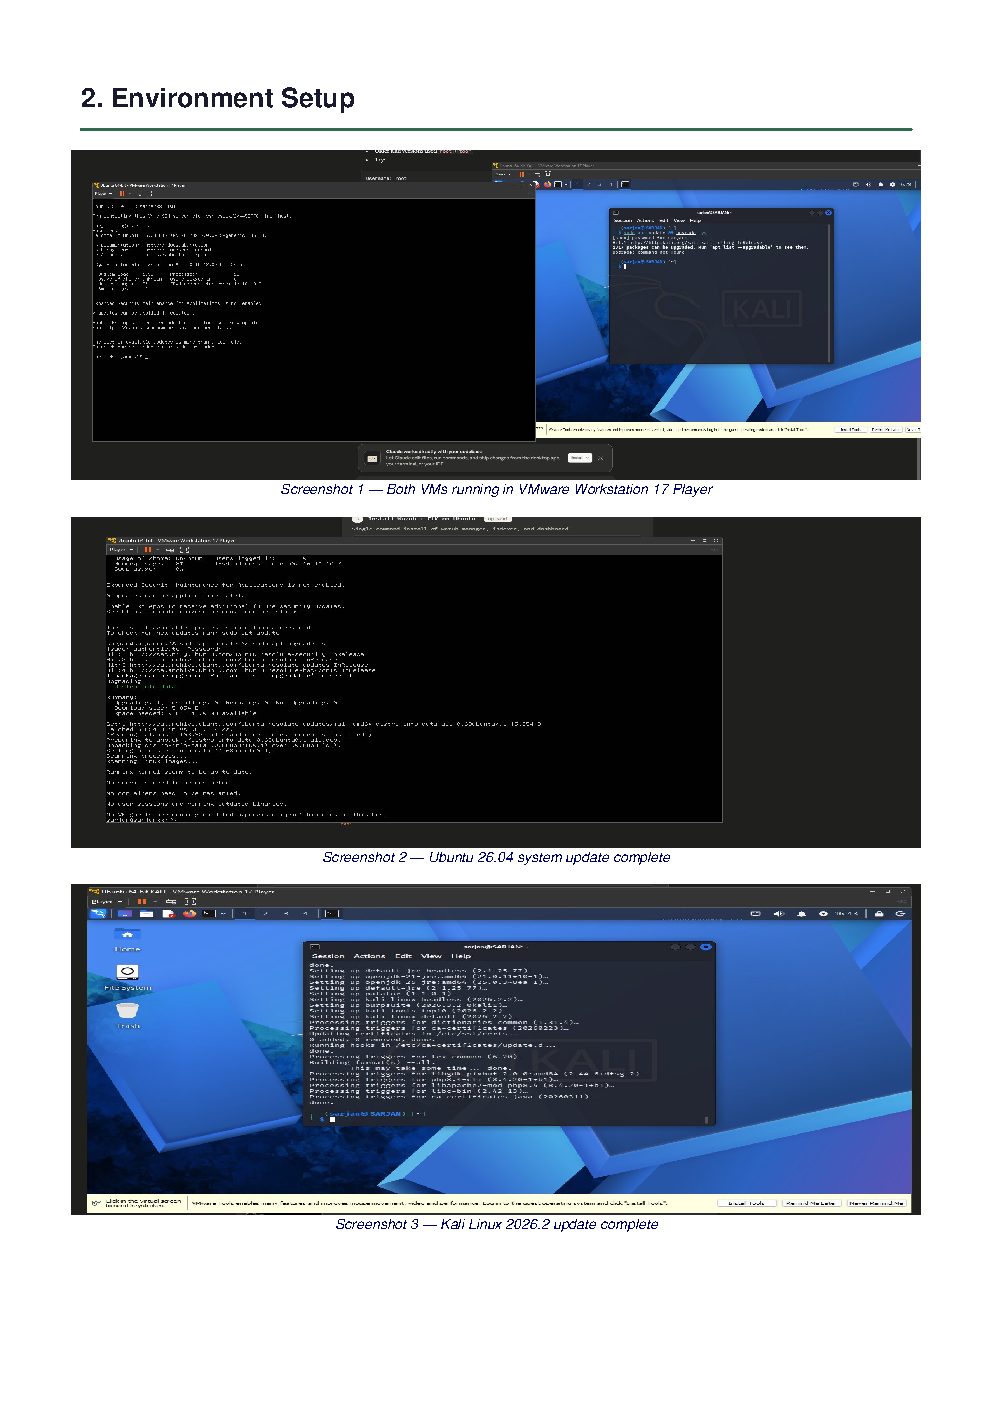 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
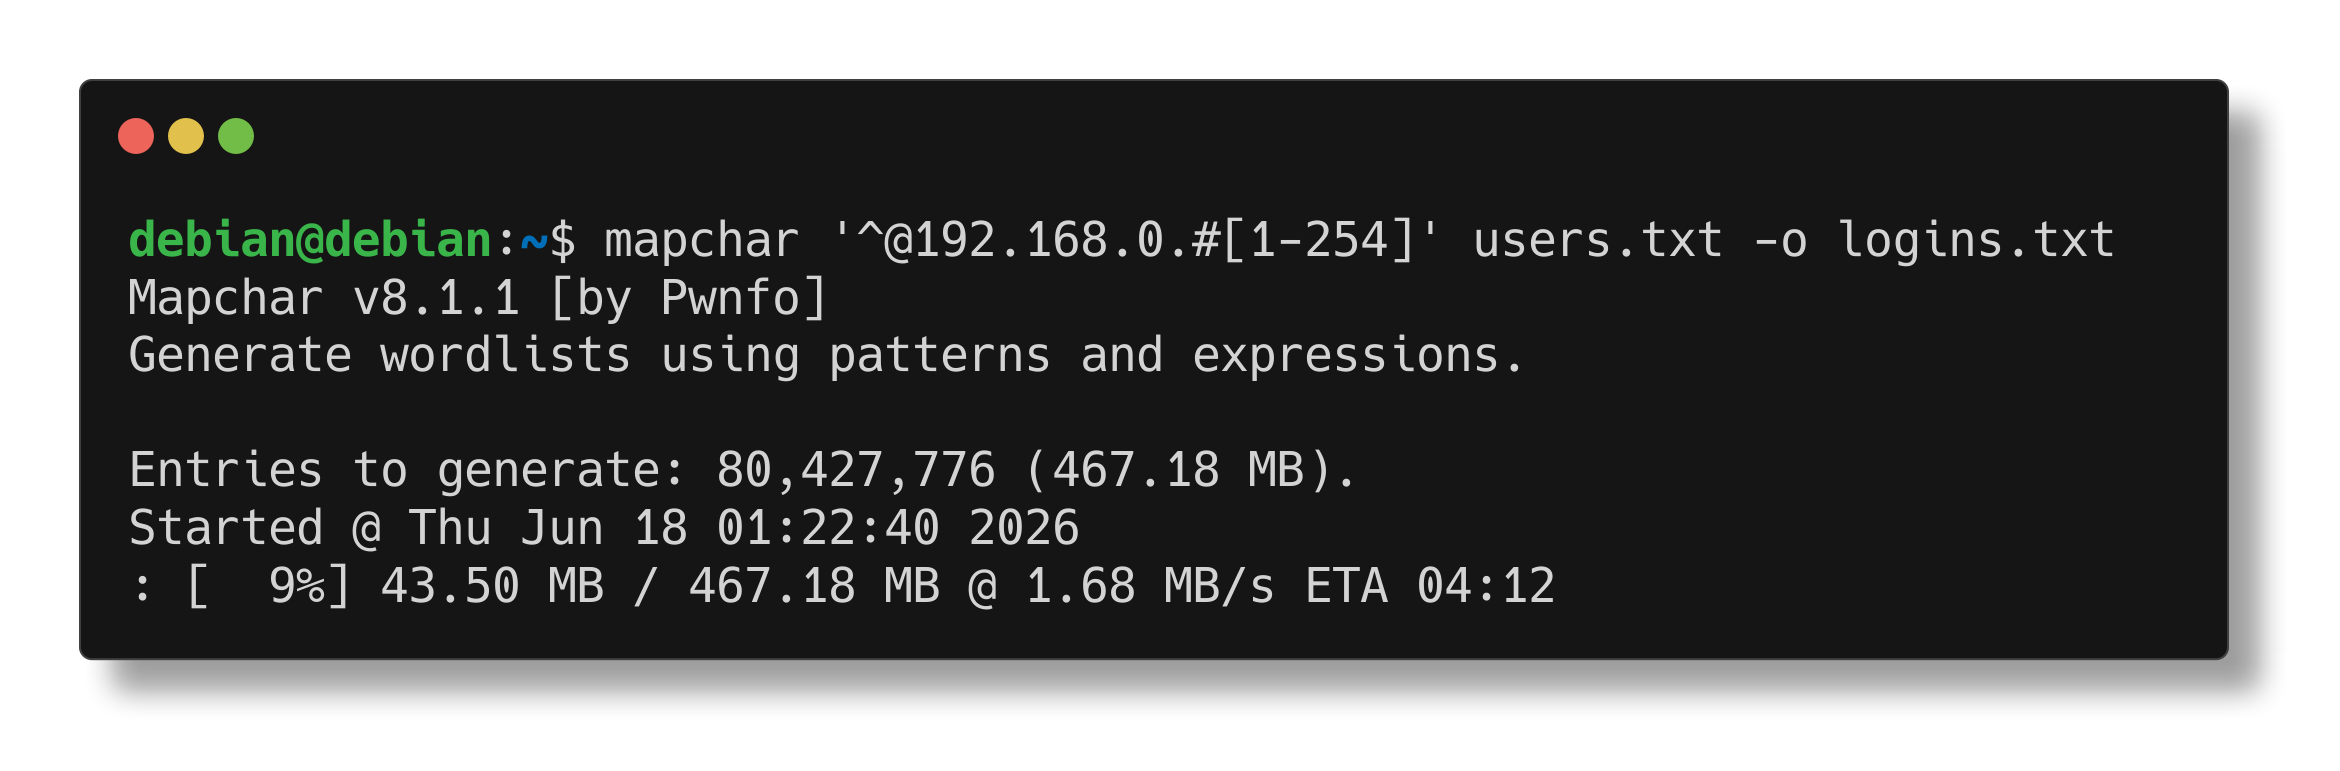 pwnfo/mapchar
Generate wordlists using pattern logic and expressions.
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
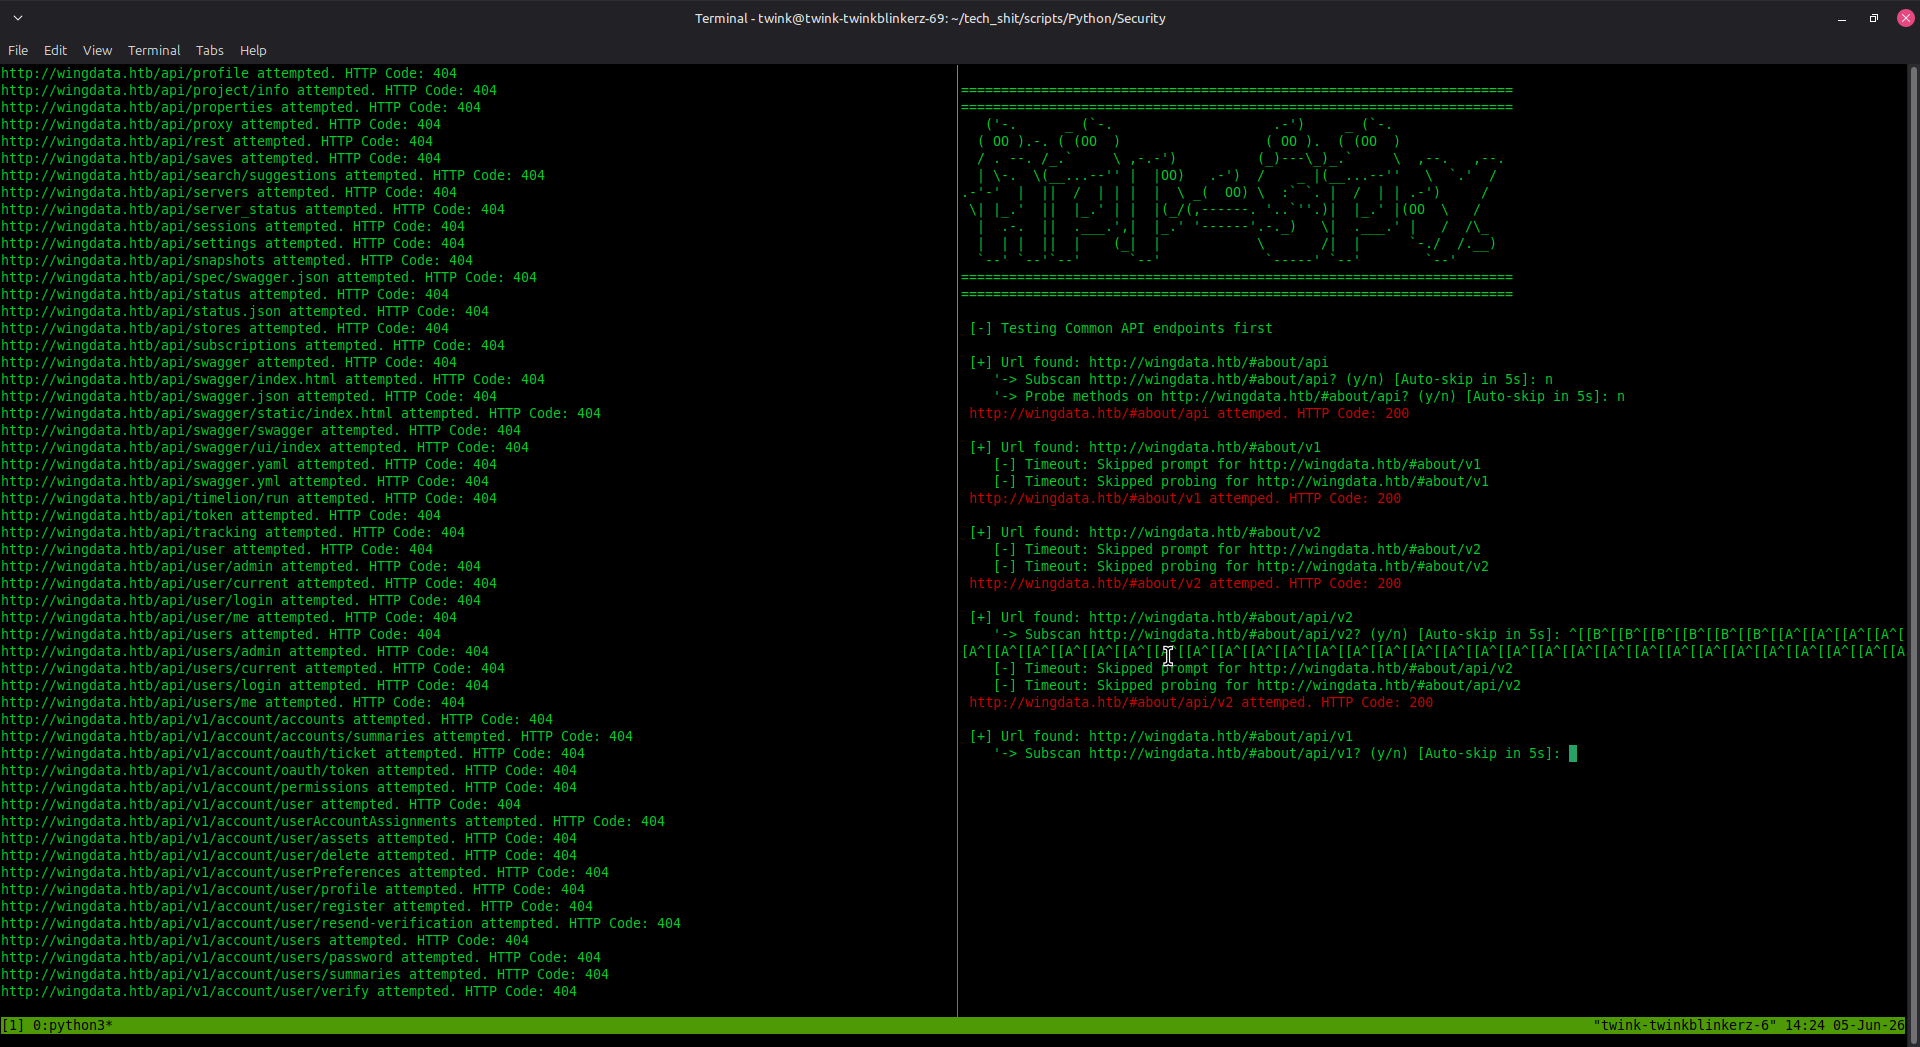 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
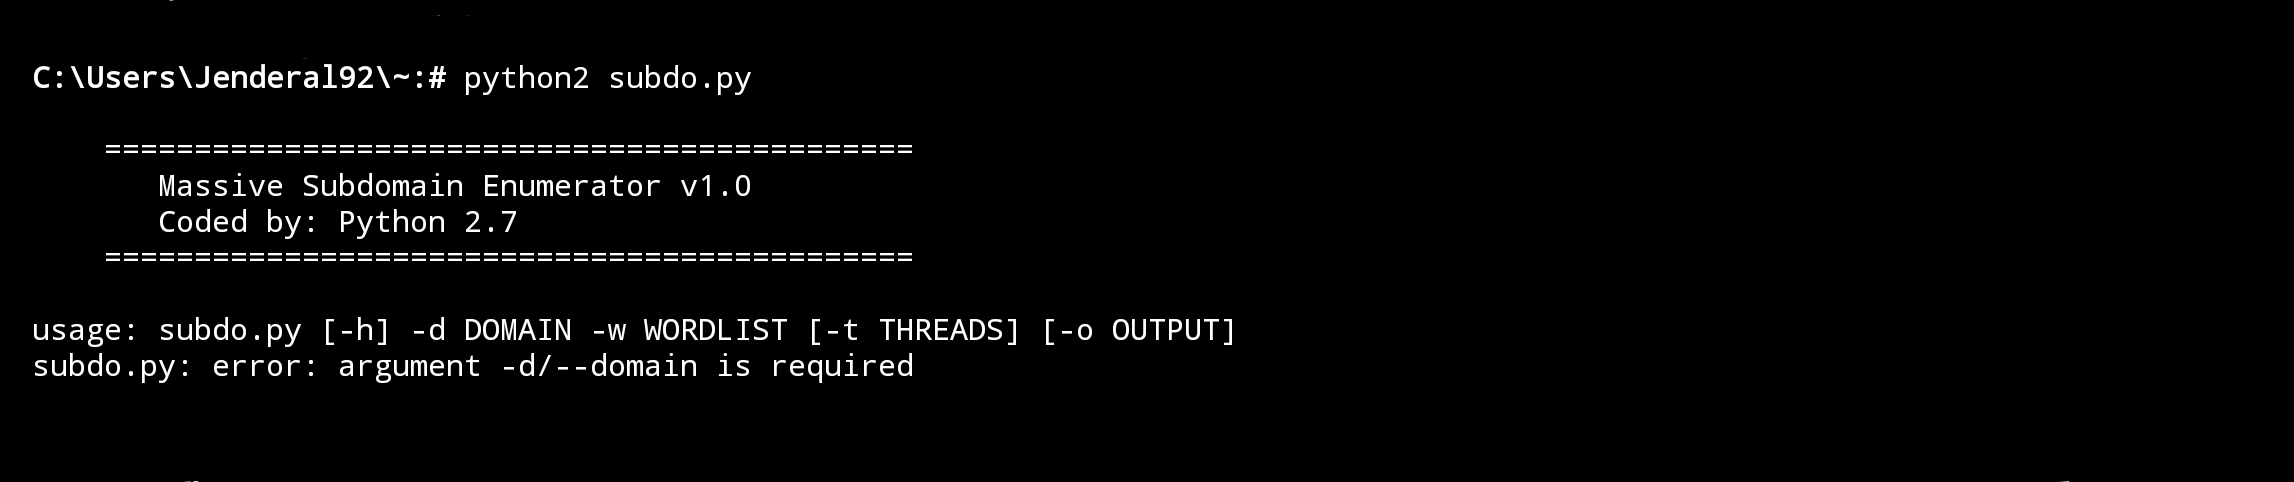 jenderal92/massive-subdomain-enumerator
This tool uses a combination of dictionary-based wordlists (brute-force) and DNS resolution checks to verify the existence of subdomains.
 itzmetanjim/cve-2026-8697
Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 kaihaochen04/monikerlinktest
cve-2024-21413
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
 pedrofbrm/apache-web-log-analysis-lab
Blue Team lab focused on analyzing Apache web access logs to detect directory brute forcing and web scanning activity.
 oalabs/hashdb-ida
HashDB API hash lookup plugin for IDA Pro
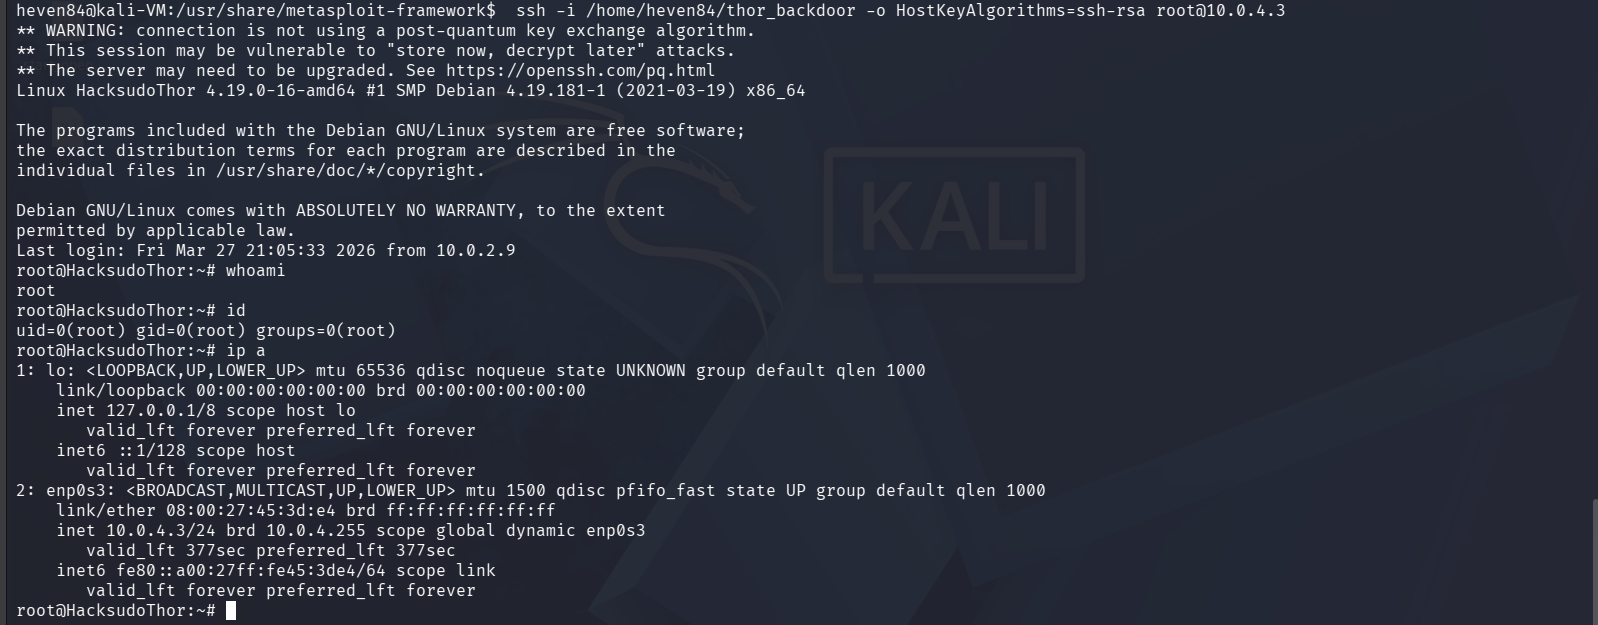 heventafese/penetration-testing-walkthrough-hacksudo-thor
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…