

waf-bypass
 nemesida-waf/waf-bypass
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…
api-security-testingpenetration-testingvulnerability-scanners+2
1.5k
nemesida-waf/waf-bypassAutomated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…
 owasp/opencre
Interactive platform linking security standards and guidelines for designing, developing, testing, and procuring secure software. Provides a unified…
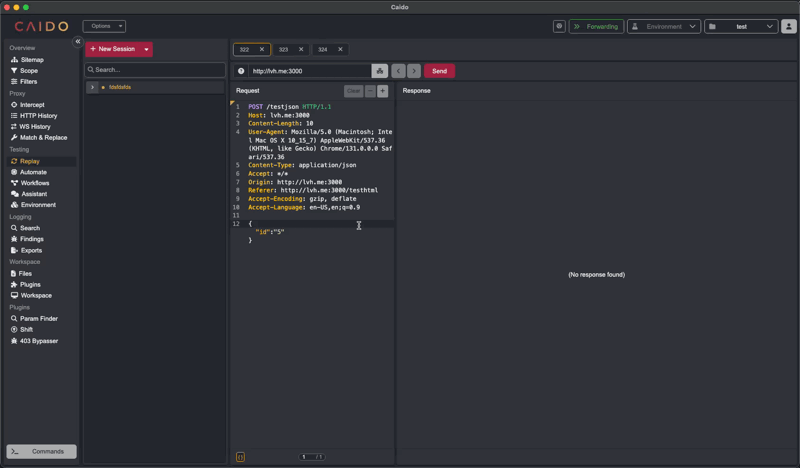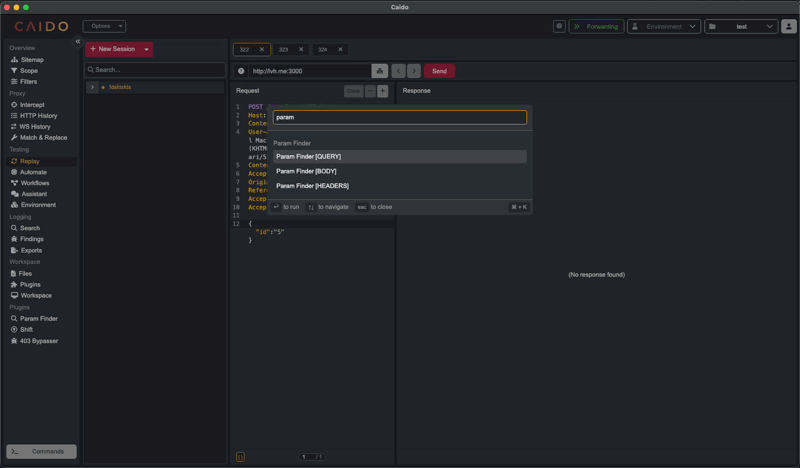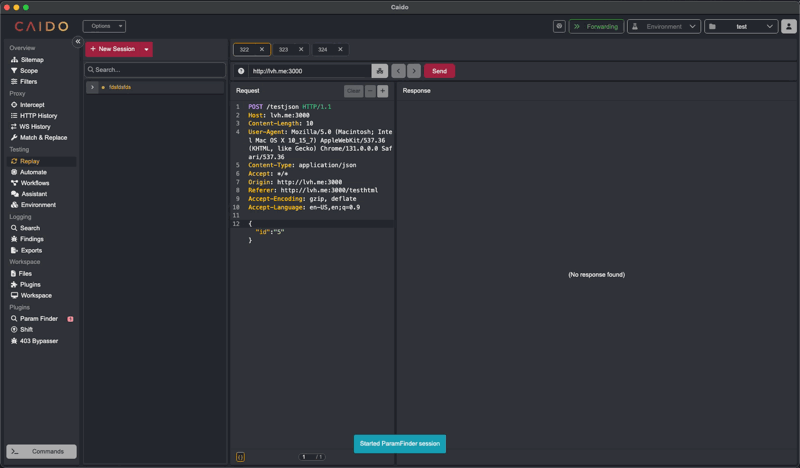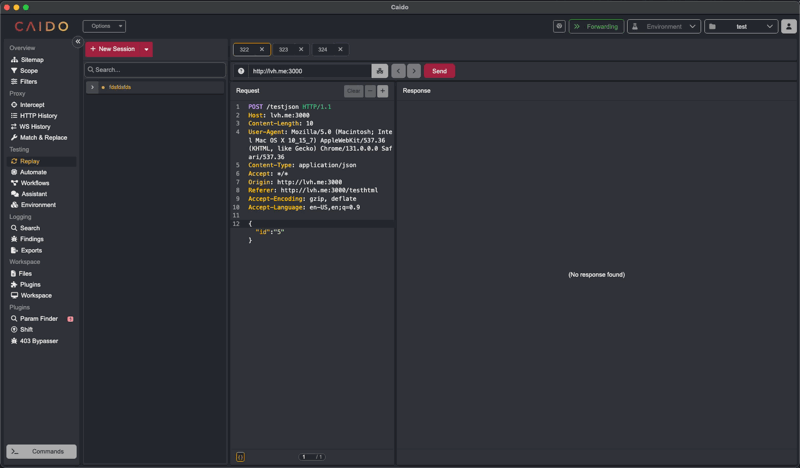 caido-community/paramfinder
Discover hidden parameters in Caido
 oscerd/cve-2026-46588
Reproducer for CVE-2026-46588: Apache Camel camel-couchdb CouchDb* header injection (operation confusion) subverting a write-only endpoint into read…
 oscerd/cve-2026-46587
Reproducer for CVE-2026-46587: Apache Camel camel-couchbase CCB_* header injection enabling document disclosure, tampering, and TTL-forced data…
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.
 moscvv/thm-cybersec-portfolio
Write-ups from completed TryHackMe rooms — Linux privilege escalation, sudo buffer overflow (CVE-2019-18634), and OWASP Top 10 (2025).
 bishopfox/snowpick
find sensitive data leaking from ServiceNow instances.
 oscerd/cve-2026-46453
Reproducer for CVE-2026-46453 — Apache Camel camel-elasticsearch-rest-client unprefixed-header injection (operation/query override via inbound HTTP…
 mehedi-hasan-sami98/dvwa-zap-pentest
Web application security assessment of DVWA using OWASP ZAP — vulnerability scanning, RCE (CVE-2012-1823) analysis, and remediation report.
 0x00phantom-hat/cve-2026-12400-exploit
Authenticated WordPress IDOR exploit for CVE-2026-12400; enumerates FlowForms REST form IDs and modifies form content or hijacks email notifications.
 jacobideji/aiiroverlay
AI IR Overlay™ — practical incident response framework for AI agents in production. Built on NIST SP 800-61 r3, mapped to NIST AI RMF, NIST CSF 2.0,…
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 cyberexpert111/blind-ssrf-to-remote-code-execution-shellshock-professional-bug-bounty-report
Professional bug bounty report detailing the exploitation of a Blind SSRF vulnerability leading to Shellshock (CVE-2014-6271) remote code execution,…
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 cyber-note/cve-2026-34835-black-box-analysis
A black-box (DAST) security analysis of CVE-2026-34835 focusing on external validation methodology, observable behavior, security impact, and…
 rootdirective-sec/cve-2026-55255-lab
Local Docker lab for reproducing CVE-2026-55255, an IDOR vulnerability in Langflow's Responses API. Validates cross-user flow execution in vulnerable…
 owasp/iot-security-verification-standard-isvs
OWASP IoT Security Verification Standard (ISVS)