Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
177 results
WP-Contest-Gallery-28.1.4-Exploit preview

WP-Contest-Gallery-28.1.4-Exploit

GitHubcerberusmrxi/wp-contest-gallery-28.1.4-exploit

Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…

exploitationpassword-crackingpayload-development+4
1
2 months ago
Burp_CVE-2025-31324 preview

Burp_CVE-2025-31324

GitHubblueowl-overlord/burp_cve-2025-31324

Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324

api-security-testingexploitationpenetration-testing+3
1 year ago
Log4J-Scanner preview

Log4J-Scanner

GitHub0xdexter0us/log4j-scanner

Burp extension to scan Log4Shell (CVE-2021-44228) vulnerability pre and post auth.

exploitationpenetration-testingvulnerability-scanners+3
1014 years ago
Python-exploit-CVE-2020-25213 preview

Python-exploit-CVE-2020-25213

GitHubbly-coder/python-exploit-cve-2020-25213

Python exploit for RCE in Wordpress

exploitationpayload-generationpenetration-testing+3
63 years ago
CVE-2026-48909-Joomla-SP-Exploit preview

CVE-2026-48909-Joomla-SP-Exploit

GitHubcerberusmrxi/cve-2026-48909-joomla-sp-exploit

CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…

code-analysiscommand-and-controleducation+8
22 months ago
neo preview

neo

GitHub4ier/neo

Turn any web app into an API. Chrome extension captures browser traffic, auto-generates schemas, lets AI replay APIs directly. No official API needed.

ai-securityapi-securitycrawler+8
7565 months ago
titus preview

titus

GitHubpraetorian-inc/titus

High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.

code-analysiscontainer-securitydevsecops+6
7053 days ago
burp-ai-agent preview

burp-ai-agent

GitHubsix2dez/burp-ai-agent

Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more

ai-securityapi-security-testingexploit-frameworks+4
1.5k25 days ago
Airachnid-Burp-Extension preview

Airachnid-Burp-Extension

GitHubspiderlabs/airachnid-burp-extension

A Burp Extension to test applications for vulnerability to the Web Cache Deception attack

penetration-testingvulnerability-scannersweb-application-exploitation+1
1418 years ago
reflector preview

reflector

GitHubelkokc/reflector

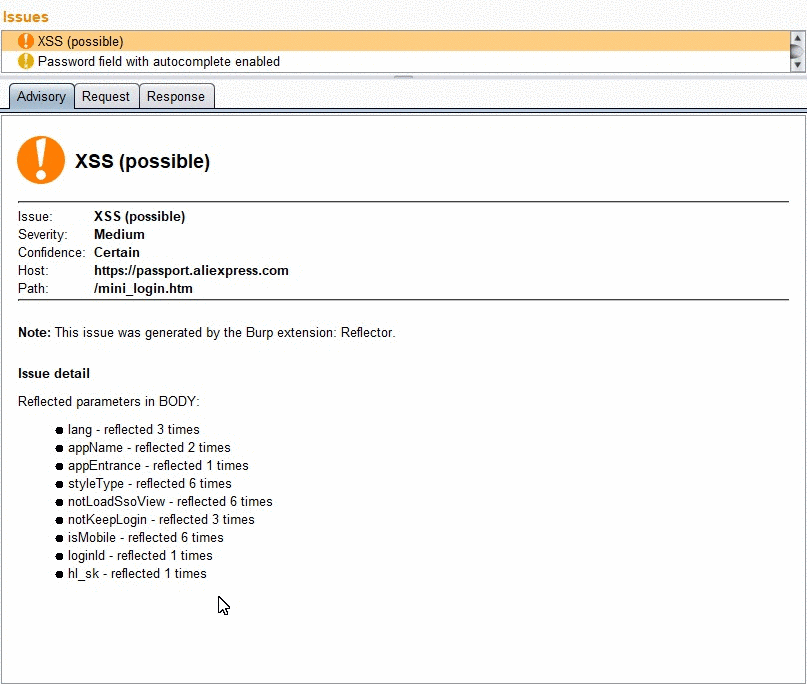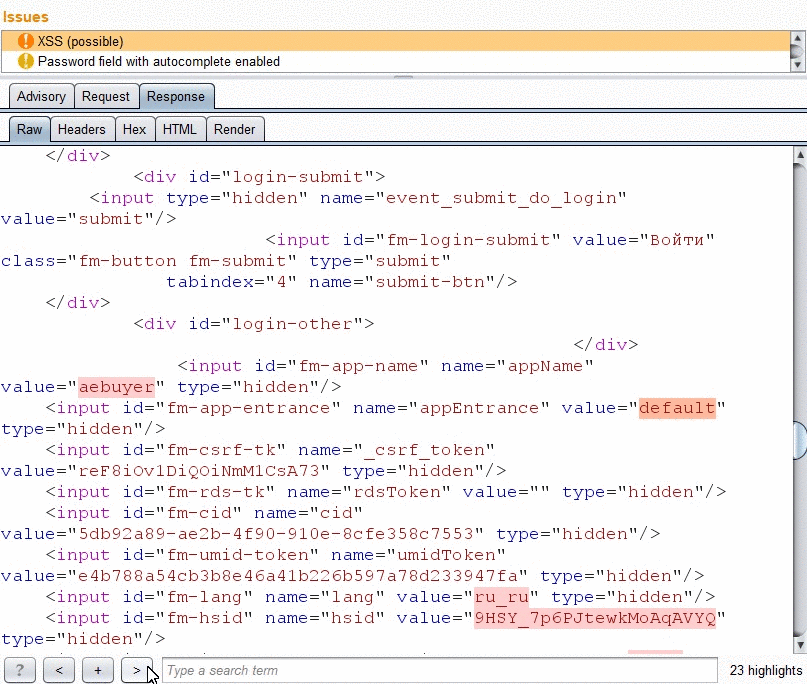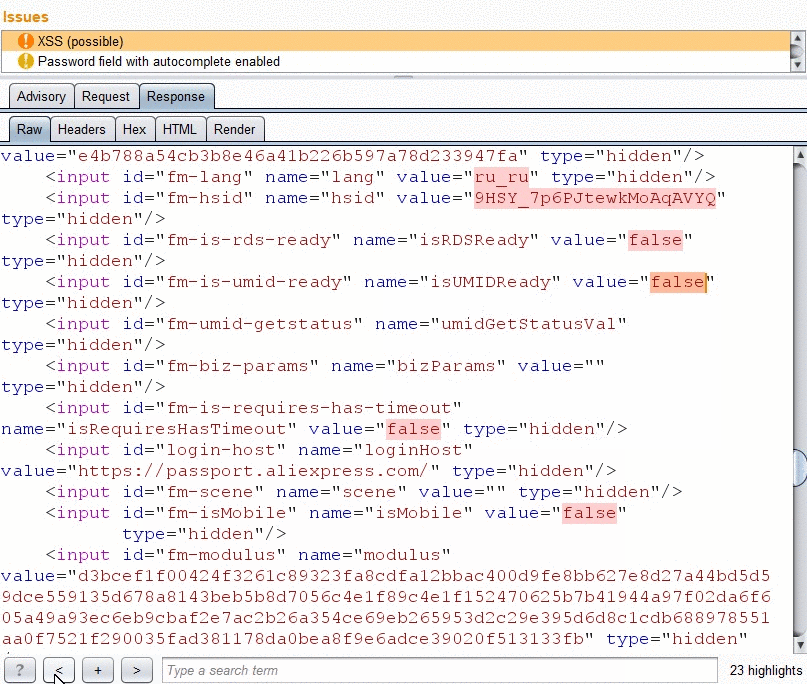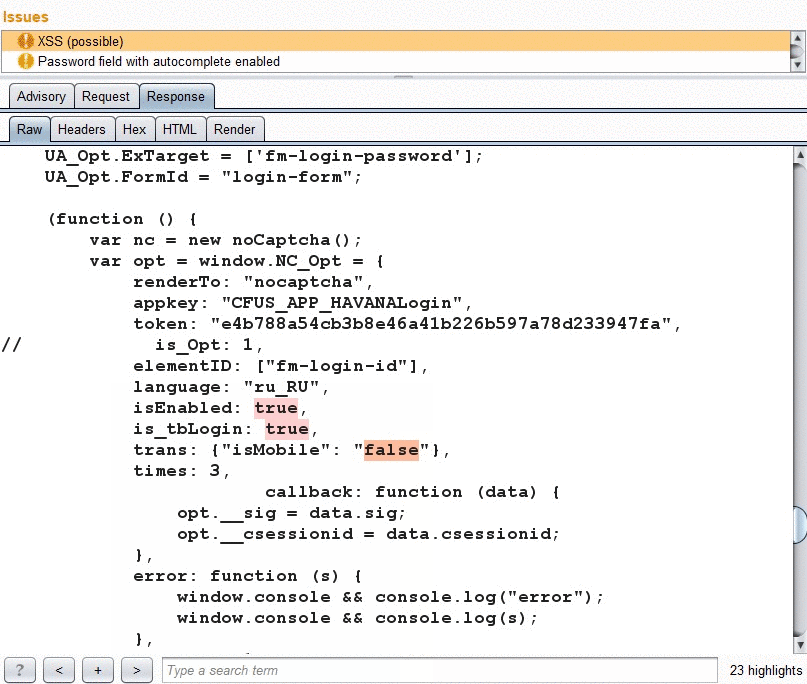
Burp plugin able to find reflected XSS on page in real-time while browsing on site

penetration-testingvulnerability-scannersweb-application-exploitation+1
1.2k5 years ago
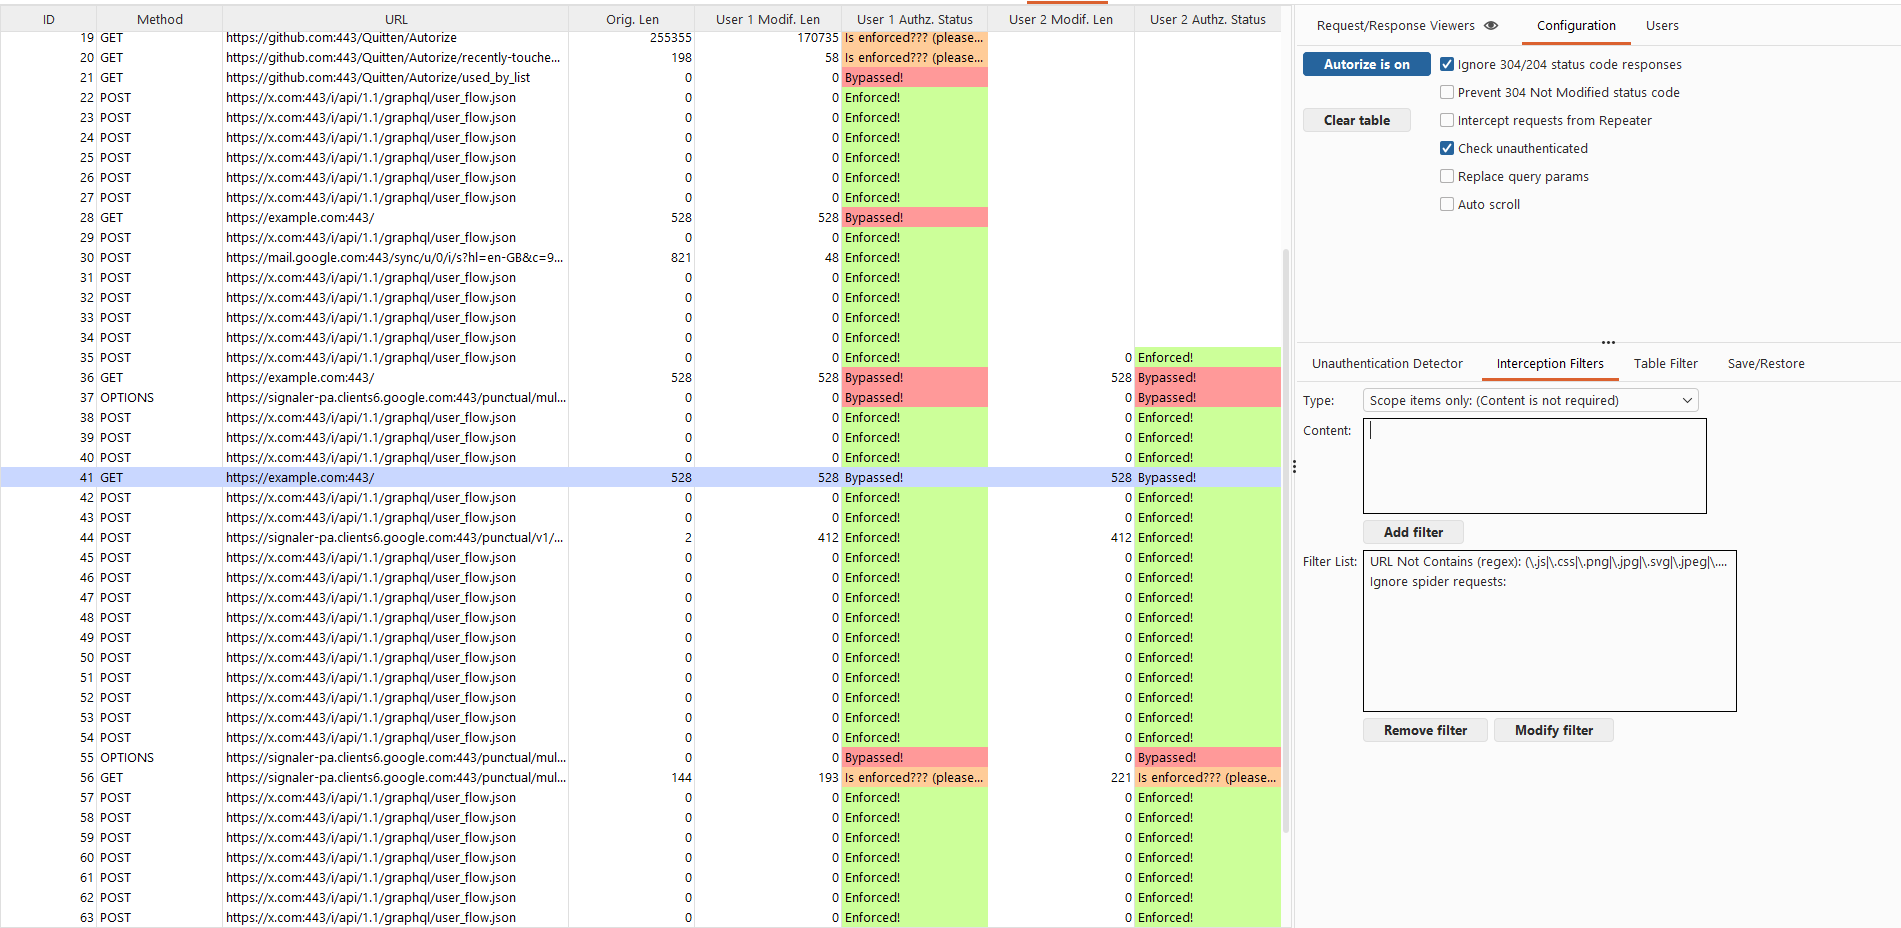
Autorize preview

Autorize

GitHubquitten/autorize

Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…

api-security-testingauthentication-authorizationpenetration-testing+2
1.2k6 months ago
BurpBounty preview

BurpBounty

GitHubwagiro/burpbounty

Burp Bounty (Scan Check Builder in BApp Store) is a extension of Burp Suite that allows you, in a quick and simple way, to improve the active and…

penetration-testingvulnerability-scannersweb-security
1.8k3 years ago
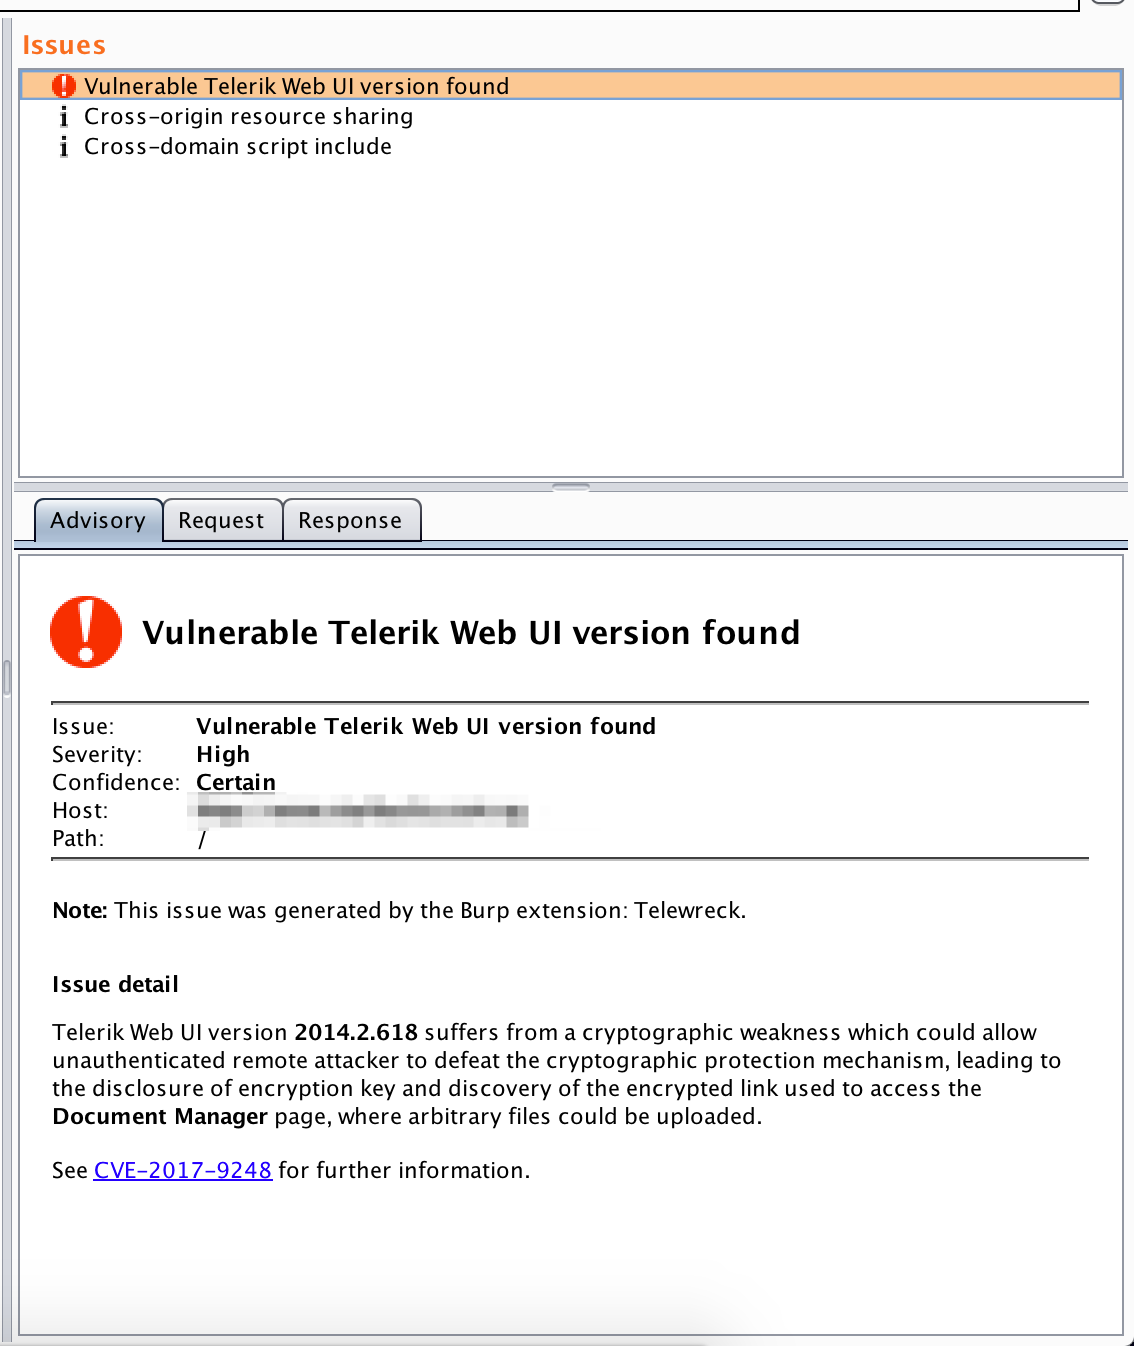
Telewreck preview

Telewreck

GitHubcapt-meelo/telewreck

A Burp extension to detect and exploit versions of Telerik Web UI vulnerable to CVE-2017-9248.

exploitationpenetration-testingvulnerability-scanners+1
968 years ago
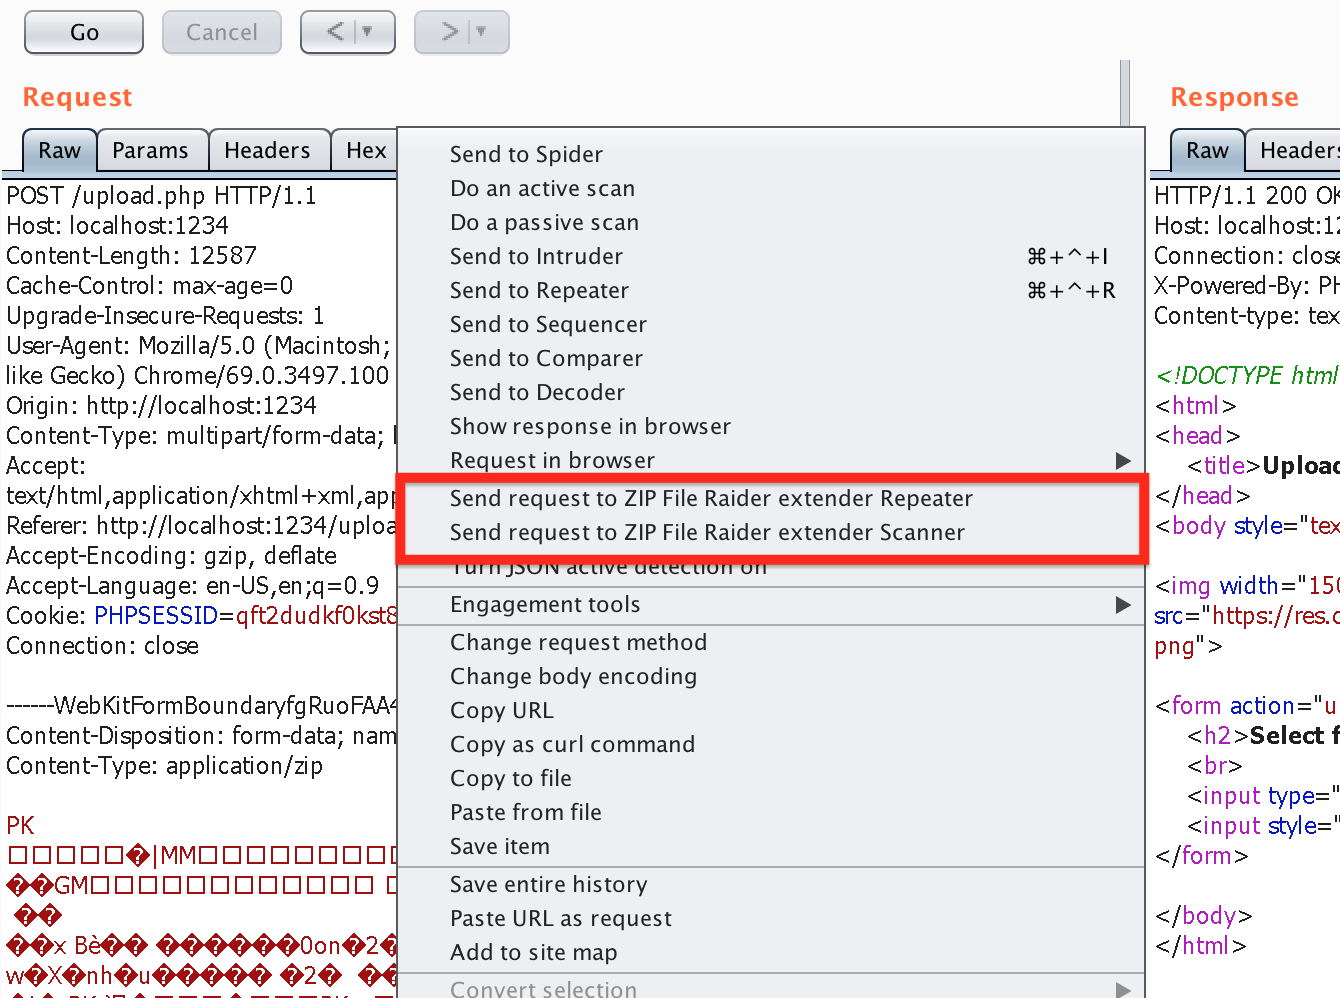
ZIPFileRaider preview

ZIPFileRaider

GitHubdestine21/zipfileraider

ZIP File Raider - Burp Extension for ZIP File Payload Testing

fuzzingpayload-generationpenetration-testing+2
716 years ago
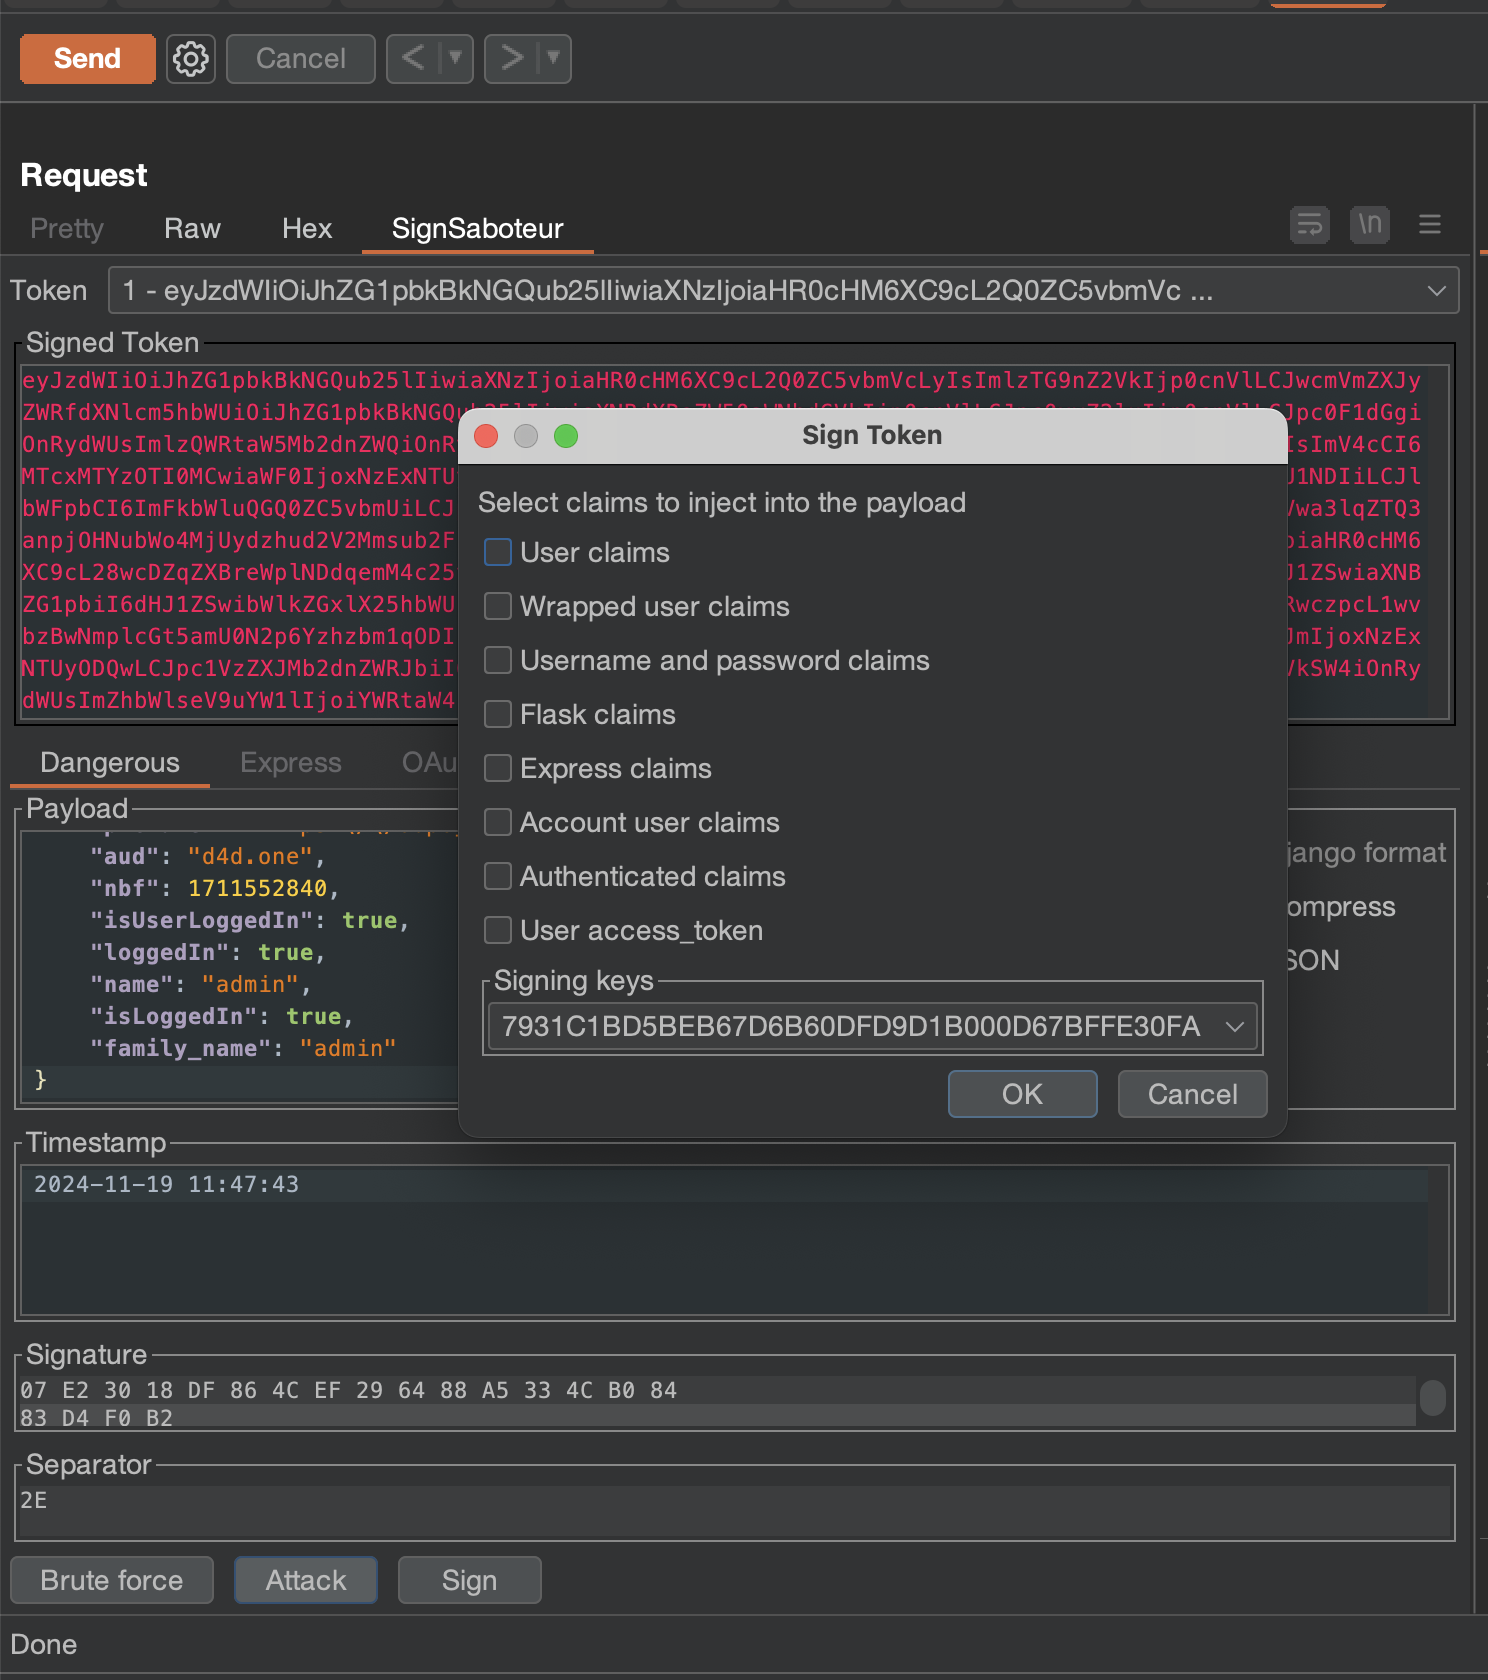
sign-saboteur preview

sign-saboteur

GitHubd0ge/sign-saboteur

SignSaboteur is a Burp Suite extension for editing, signing, verifying various signed web tokens

authentication-authorizationcryptographyfuzzing+7
1721 year ago
JS-Tap preview

JS-Tap

GitHubhoodoer/js-tap

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…

command-and-controldata-exfiltrationinformation-gathering+8
4772 months ago
IPRotate_Burp_Extension preview

IPRotate_Burp_Extension

GitHubrhinosecuritylabs/iprotate_burp_extension

Extension for Burp Suite which uses AWS API Gateway to rotate your IP on every request.

cloud-securityids-ips-evasionpenetration-testing+2
8957 months ago
http-request-smuggler preview

http-request-smuggler

GitHubportswigger/http-request-smuggler

Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…

dynamic-analysis-sandboxingpenetration-testingvulnerability-scanners+3
1.2k1 month ago
Previous1…78910Next