

Tiredful-API
 payatu/tiredful-api
An intentionally designed broken web application based on REST API.
api-security-testingeducationlabs-practice+2
payatu/tiredful-apiAn intentionally designed broken web application based on REST API.
 codewatchorg/sqlipy
SQLiPy is a Python plugin for Burp Suite that integrates SQLMap using the SQLMap API.
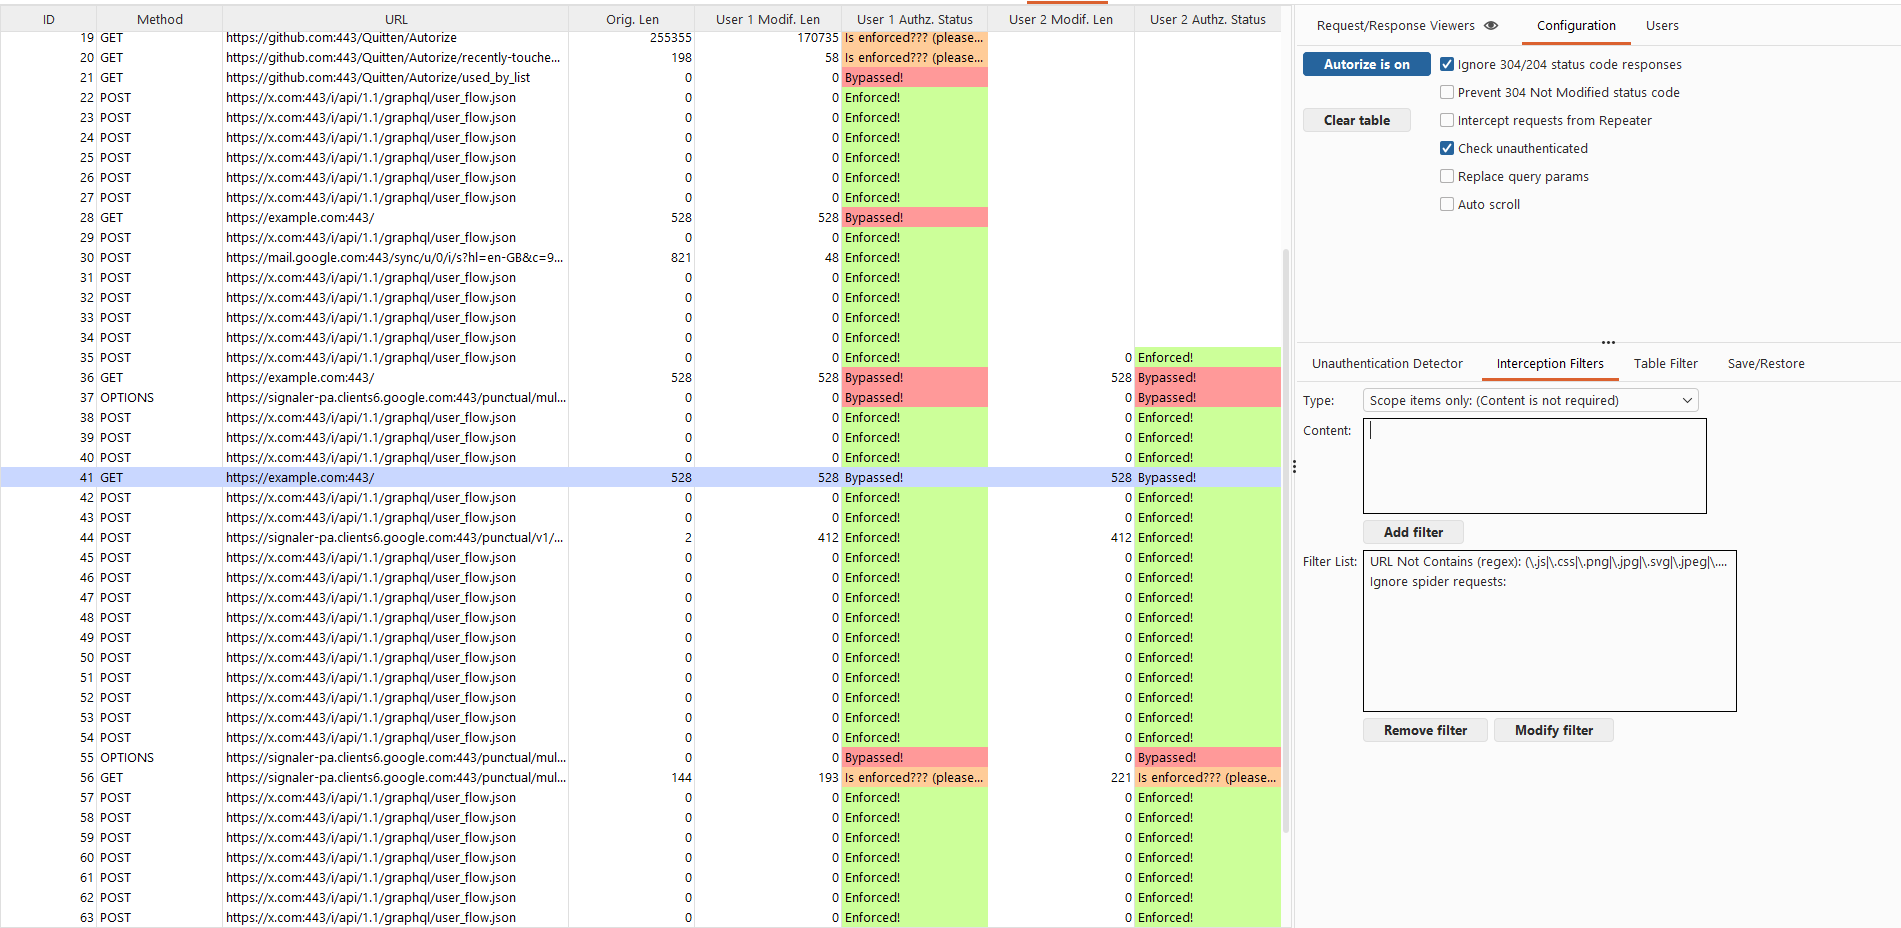 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
 owasp/mastg-hacking-playground
Collection of intentionally insecure iOS and Android apps for learning mobile security testing, reverse engineering, and vulnerability analysis,…
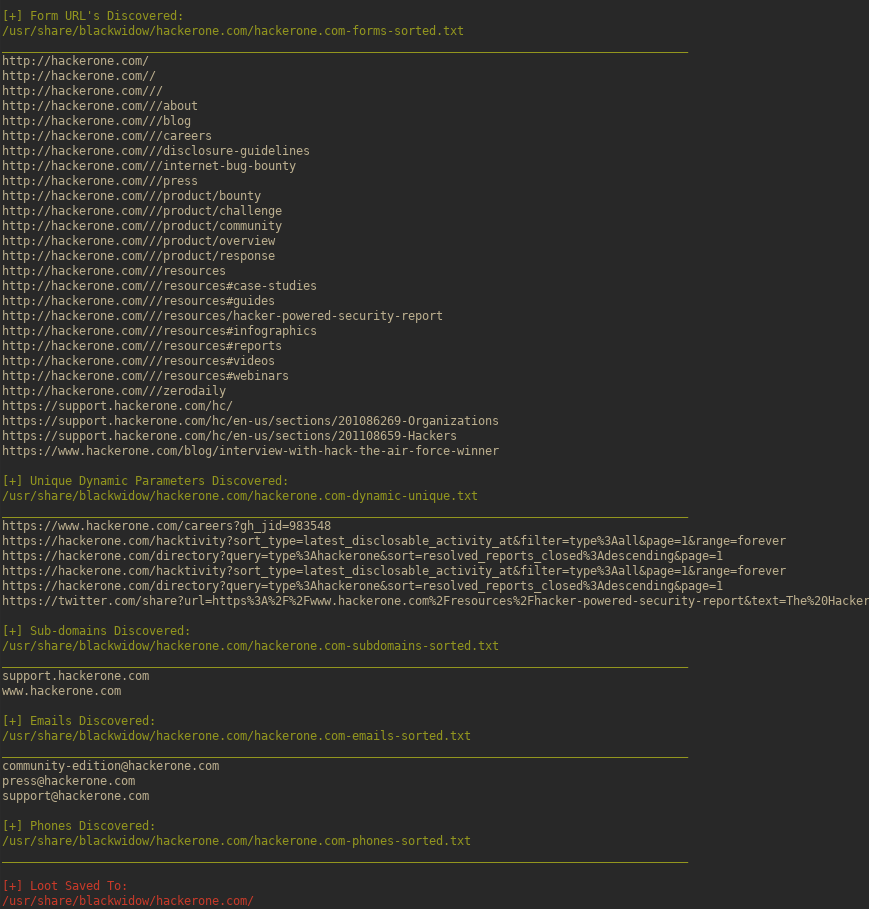 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
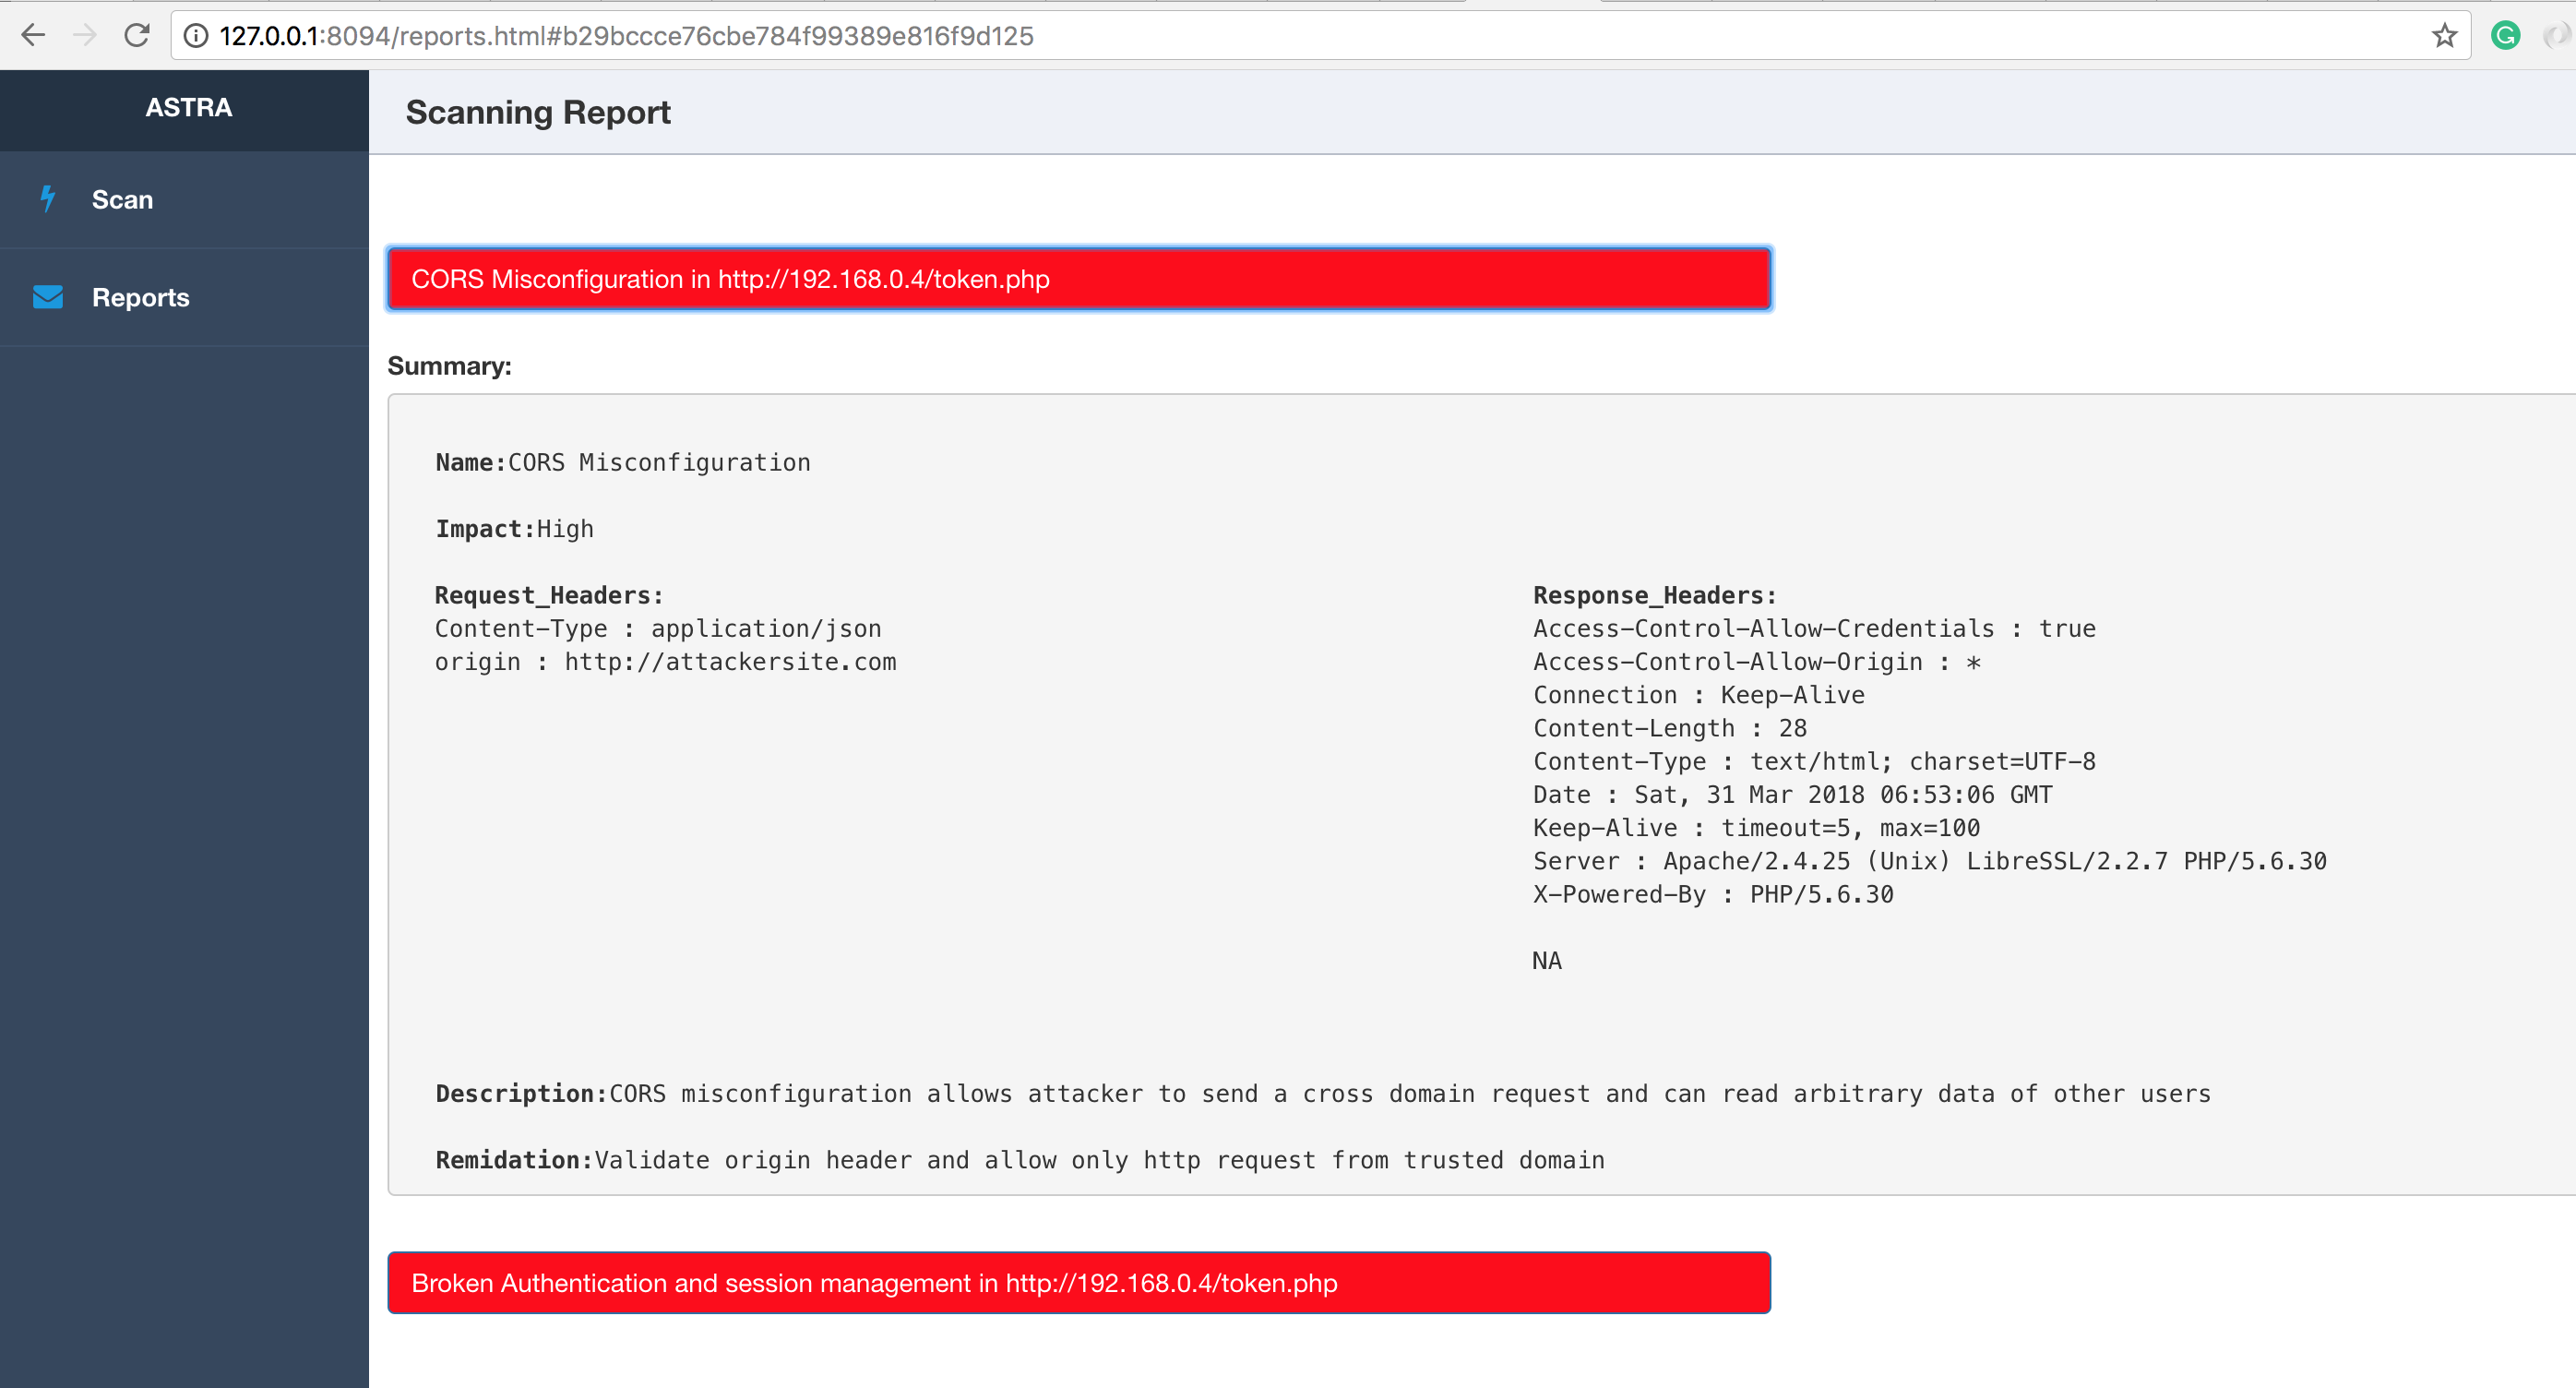 flipkart-incubator/astra
Automated Security Testing For REST API's
 0x4d31/burpa
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…
 owasp/igoat-swift
OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
 owtf/owtf
Modular penetration testing framework integrating multiple tools for automated web application security assessment, aligned with OWASP Testing Guide,…
 pentestgeek/burpcommander
Ruby command-line interface to Burp Suite's REST API
 owasp/igoat
OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar
 joanbono/gurp
Burp Commander written in Go
 ebryx/aes-killer
Burp Plugin to decrypt AES encrypted traffic on the fly
 security-code-scan/security-code-scan
Vulnerability Patterns Detector for C# and VB.NET
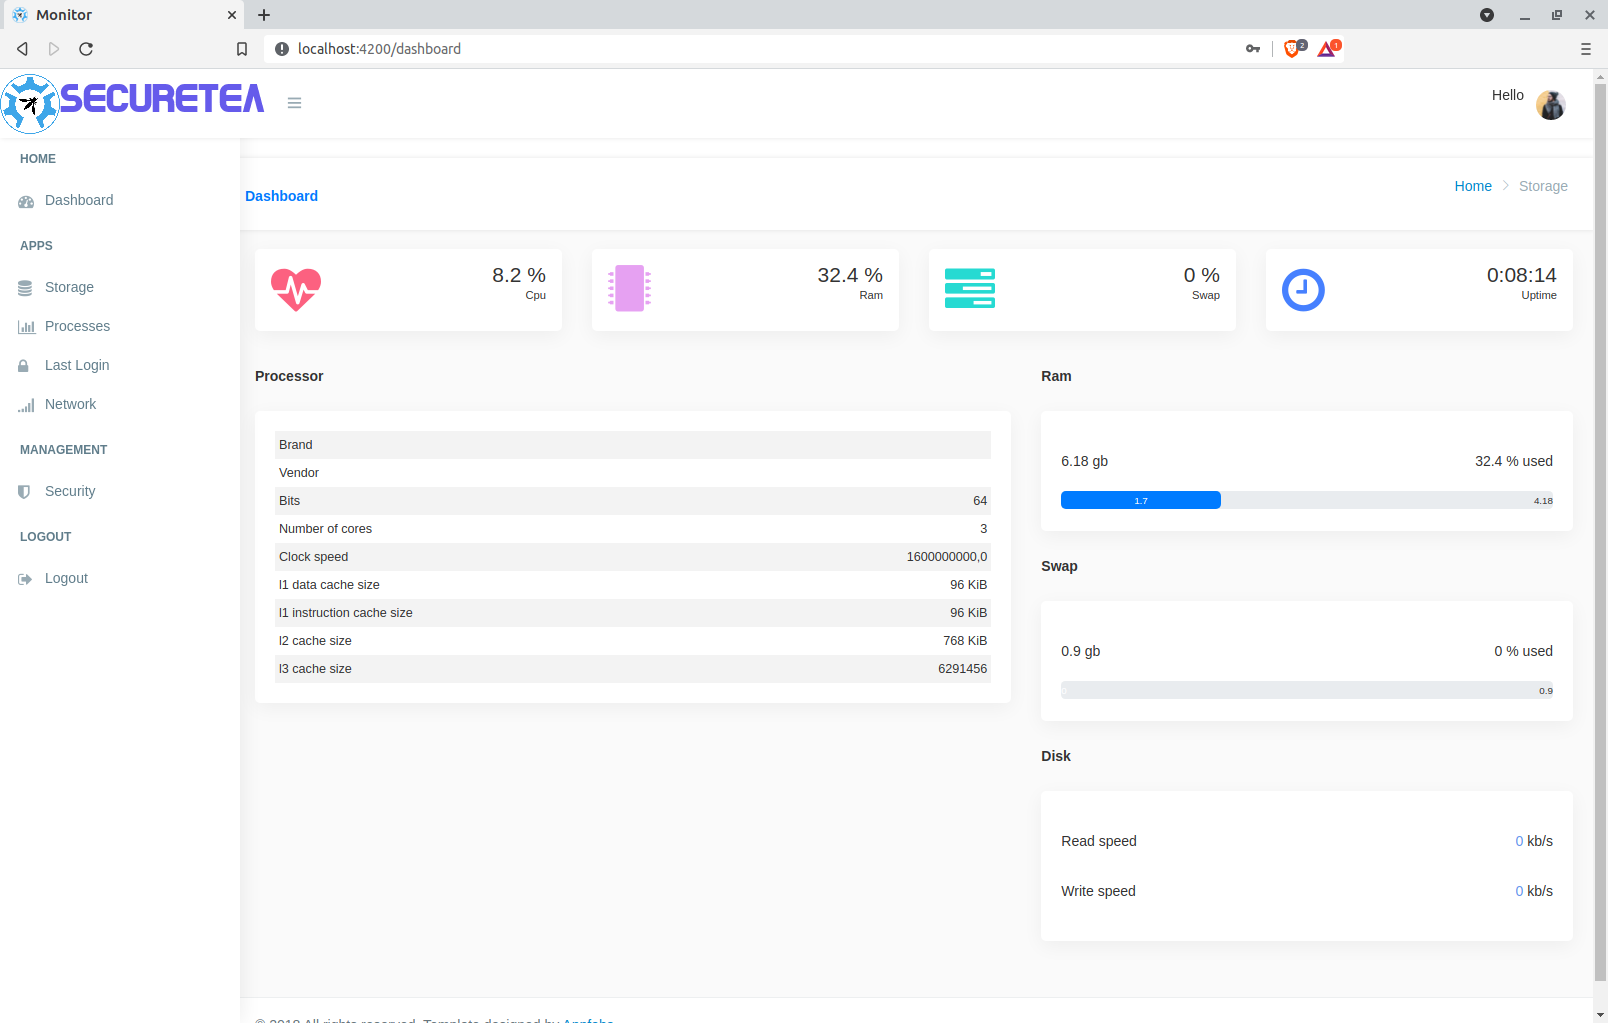 owasp/securetea-project
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
 securityrat/securityrat
OWASP SecurityRAT (version 1.x) - Tool for handling security requirements in development
 moopinger/smugglefuzz
A rapid HTTP downgrade smuggling scanner written in Go.
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/