
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
BlackWidow — A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website. | Kitploit
Tools/GitHubGitHub/1n3/blackwidow
OSINT (Open Source Intelligence)Web Vulnerability ScannersVulnerability AnalysisInformation GatheringWeb SecurityFuzzing
GitHub1n3/blackwidow

BlackWidow

A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.

View Repository
1.8k390627 months agoReviewed by Kitploit
Share
Website

alt tag

ABOUT:

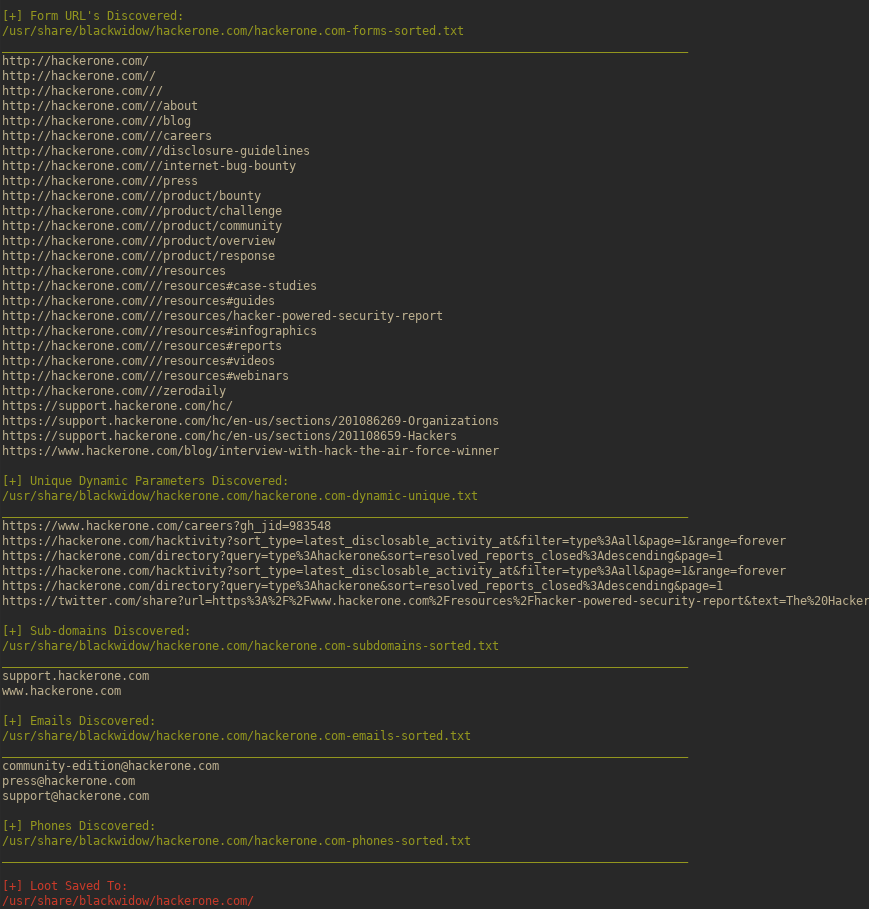
BlackWidow is a python based web application spider to gather subdomains, URL's, dynamic parameters, email addresses and phone numbers from a target website. This project also includes Inject-X fuzzer to scan dynamic URL's for common OWASP vulnerabilities.

DEMO VIDEO:

BlackWidow Demo

FEATURES:

  • Automatically collect all URL's from a target website
  • Automatically collect all dynamic URL's and parameters from a target website
  • Automatically collect all subdomains from a target website
  • Automatically collect all phone numbers from a target website
  • Automatically collect all email addresses from a target website
  • Automatically collect all form URL's from a target website
  • Automatically scan/fuzz for common OWASP TOP vulnerabilities
  • Automatically saves all data into sorted text files

LINUX INSTALL:

sudo bash install.sh

USAGE:

blackwidow -u https://target.com - crawl target.com with 3 levels of depth.
blackwidow -d target.com -l 5 -v y - crawl the domain: target.com with 5 levels of depth with verbose logging enabled.
blackwidow -d target.com -l 5 -c 'test=test' - crawl the domain: target.com with 5 levels of depth using the cookie 'test=test'
blackwidow -d target.com -l 5 -s y -v y - crawl the domain: target.com with 5 levels of depth and fuzz all unique parameters for OWASP vulnerabilities with verbose logging on.
injectx.py -u https://test.com/uers.php?user=1&admin=true -v y - Fuzz all GET parameters for common OWASP vulnerabilities with verbose logging enabled.

SAMPLE REPORT:

alt tag

DOCKER:

git clone https://github.com/1N3/BlackWidow.git
cd BlackWidow
docker build -t blackwidow .
docker run -it blackwidow # Defaults to --help

LICENSE:

You may modify and re-distribute this software as long as the project name "BlackWidow", credit to the author "xer0dayz" and website URL "https://sn1persecurity.com" are NOT mofified. Doing so will break the license agreement and a takedown notice will be issued.

DISCLAIMER:

This program is used for educational and ethical purposes only. I take no responsibility for any damages caused from using this program. By downloading and using this software, you agree that you take full responsibility for any damages and liability.


LINKS:

  • Twitter
  • Twitter
  • Website
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →




