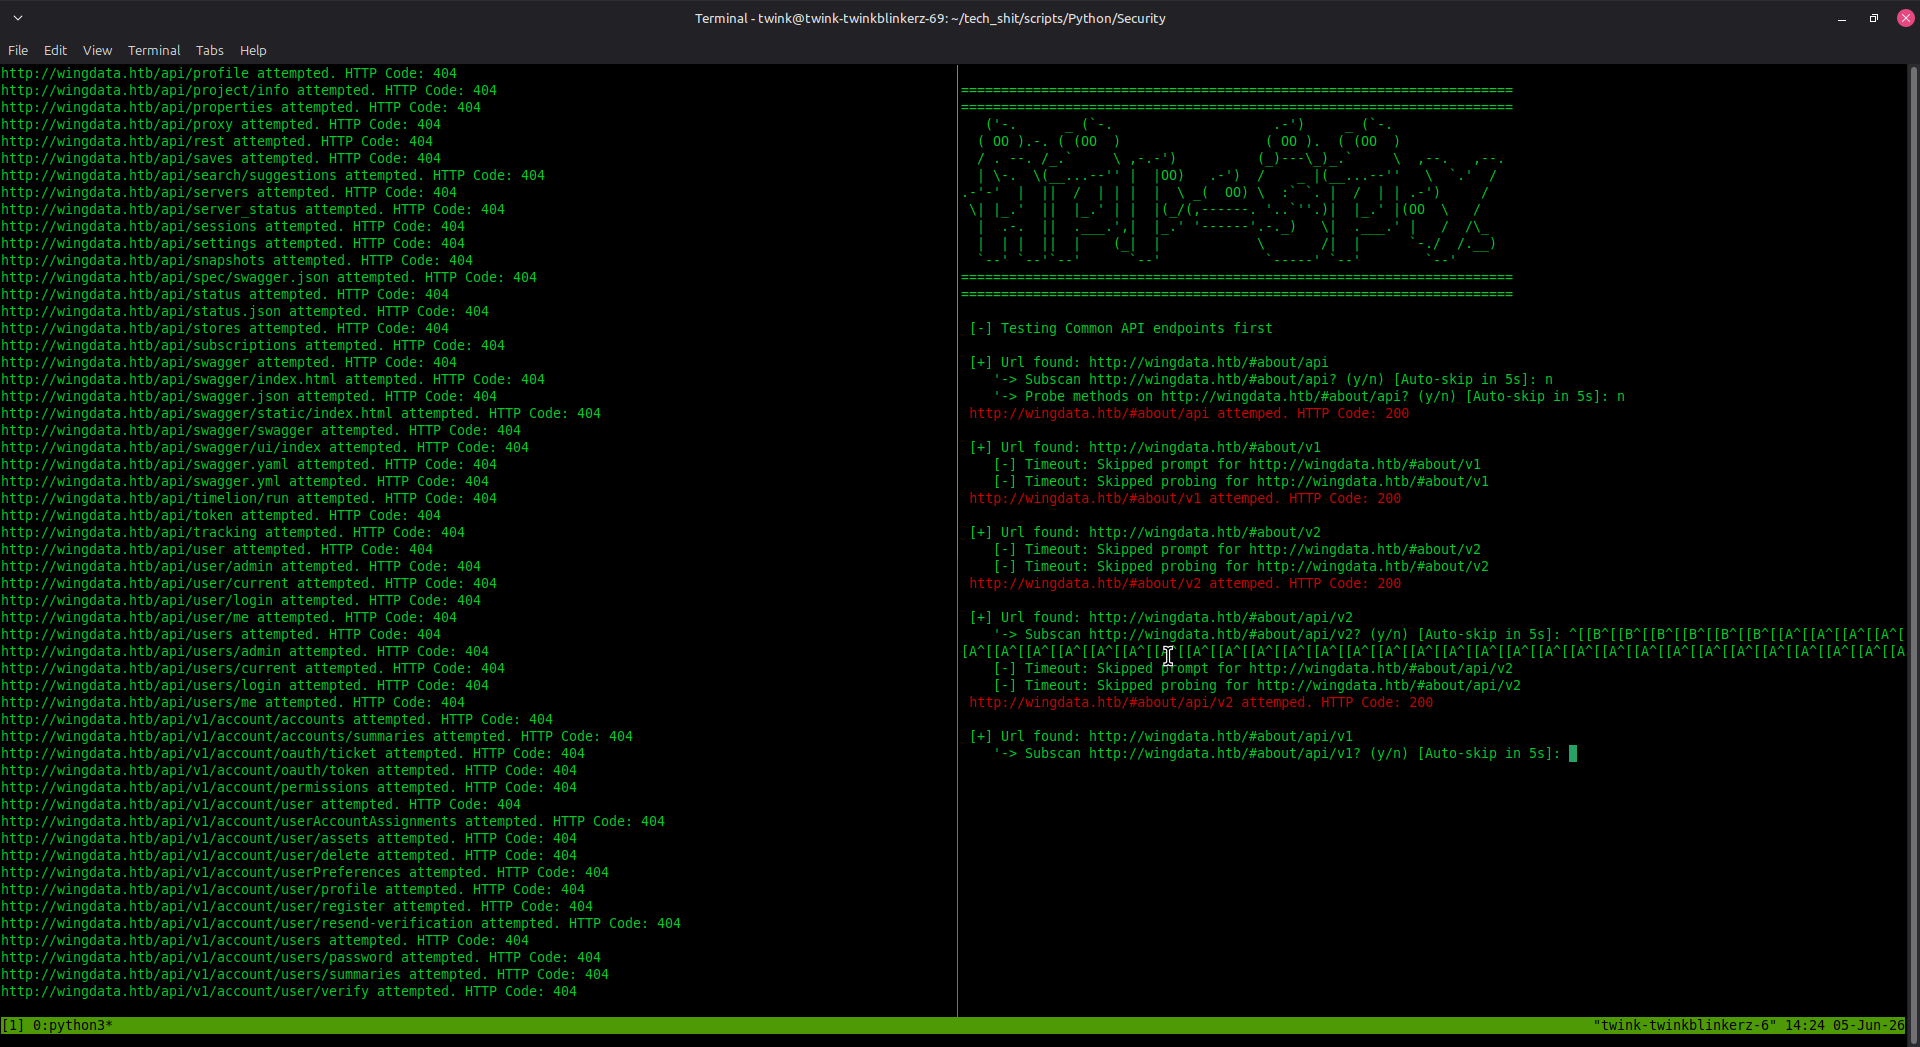

API-SPY-API-PROBE
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…

A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…

Open-source MITM proxy to intercept, inspect, and mock network traffic.

An API hooking framework for intercepting and monitoring Windows applications

An OWASP-aligned intentionally vulnerable platform for learning and testing AI, LLM, RAG, MCP, and Agentic AI security.

Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…

Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…

Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!

Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…

API Scraper Agent for Web API's

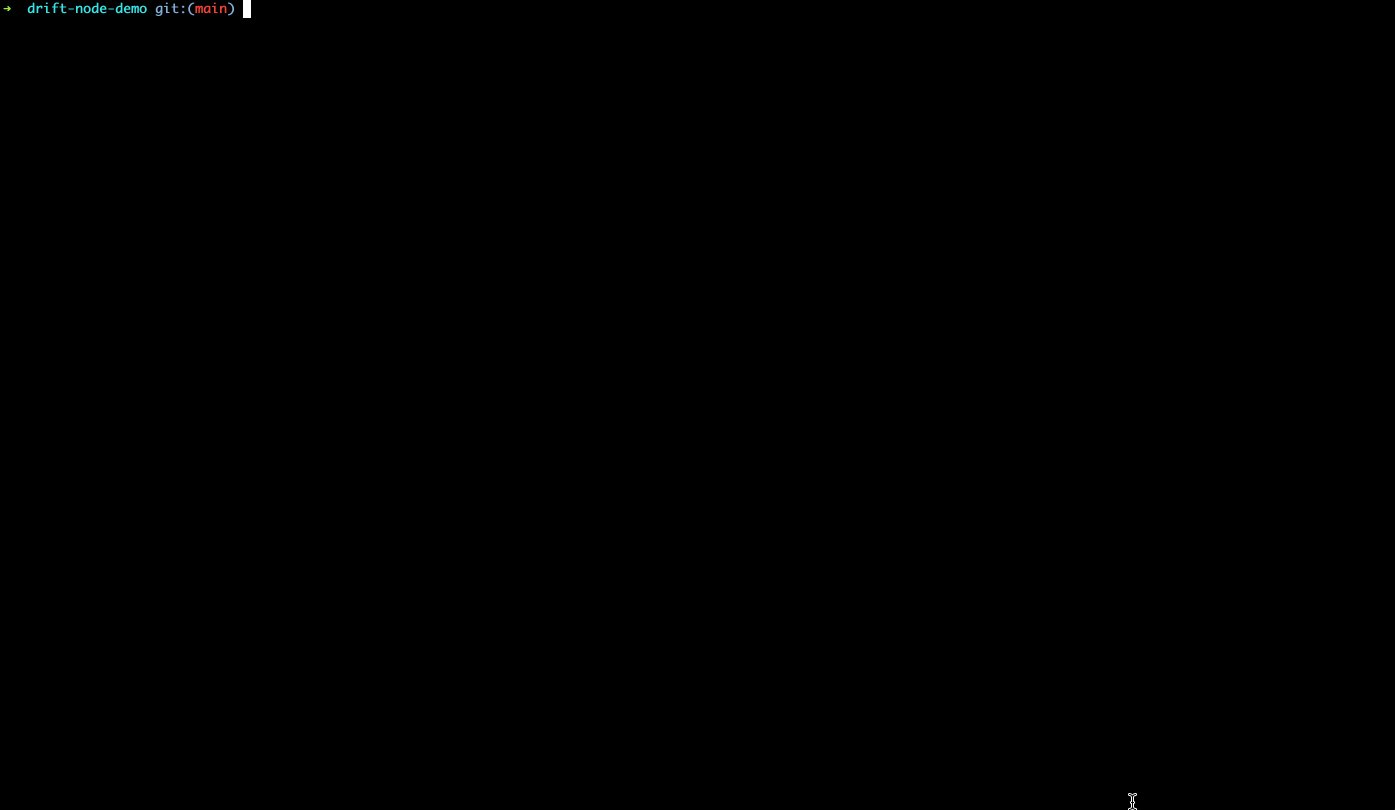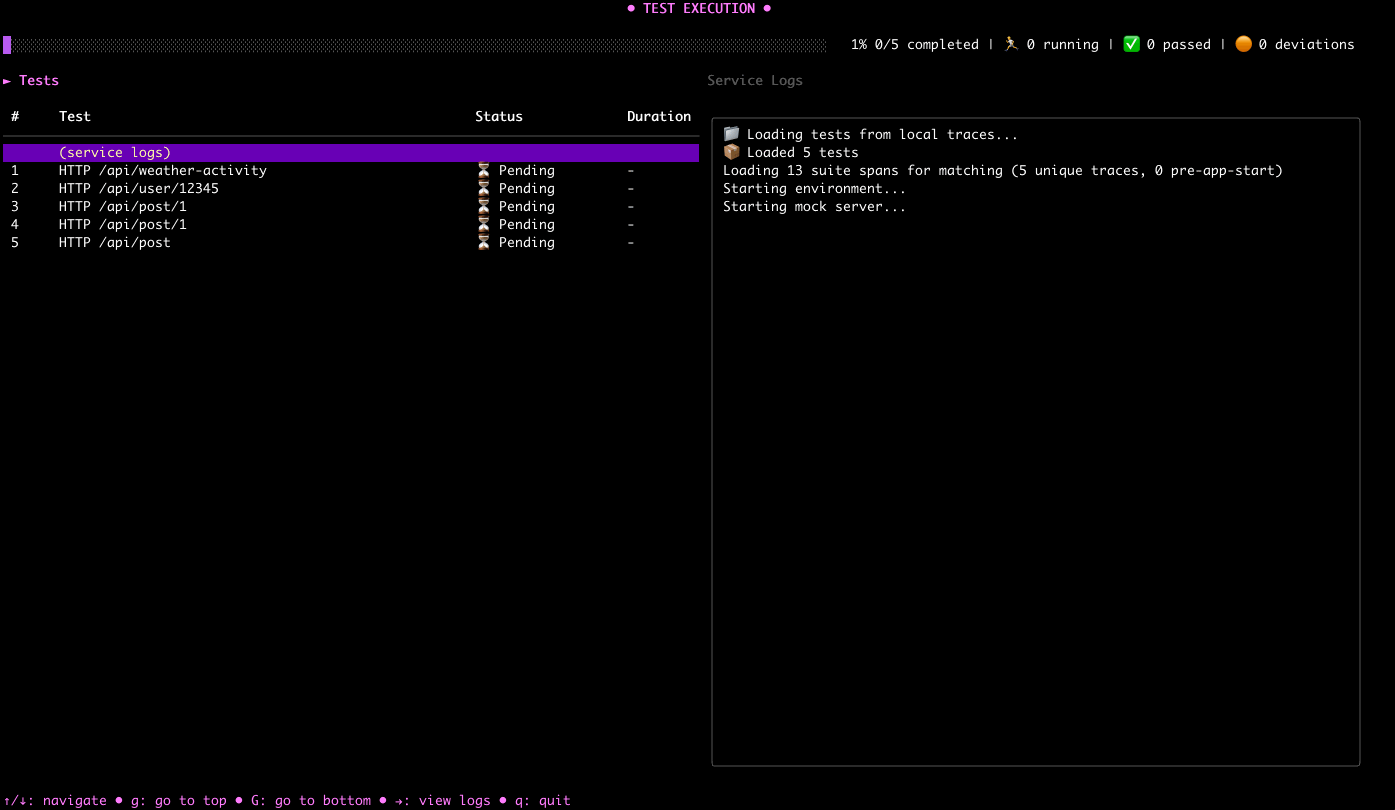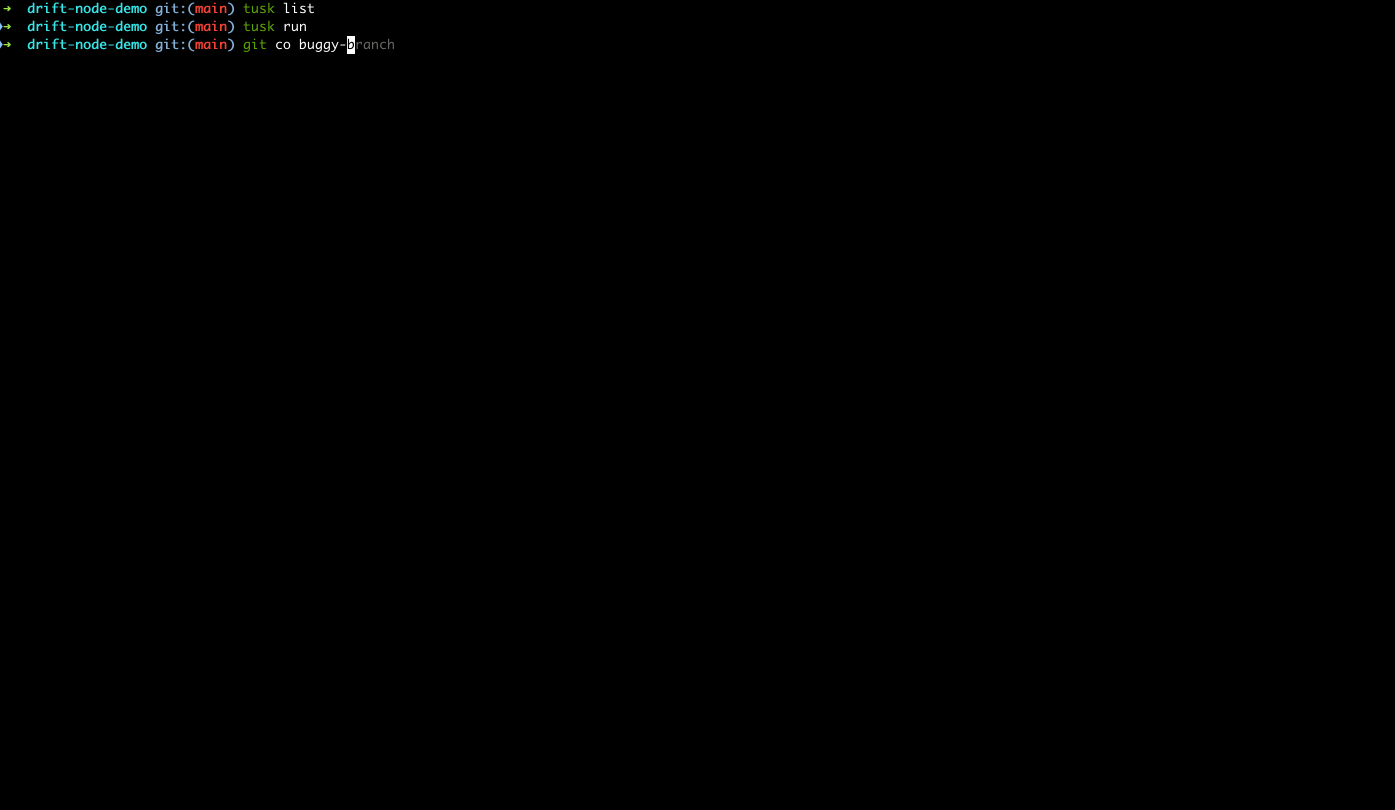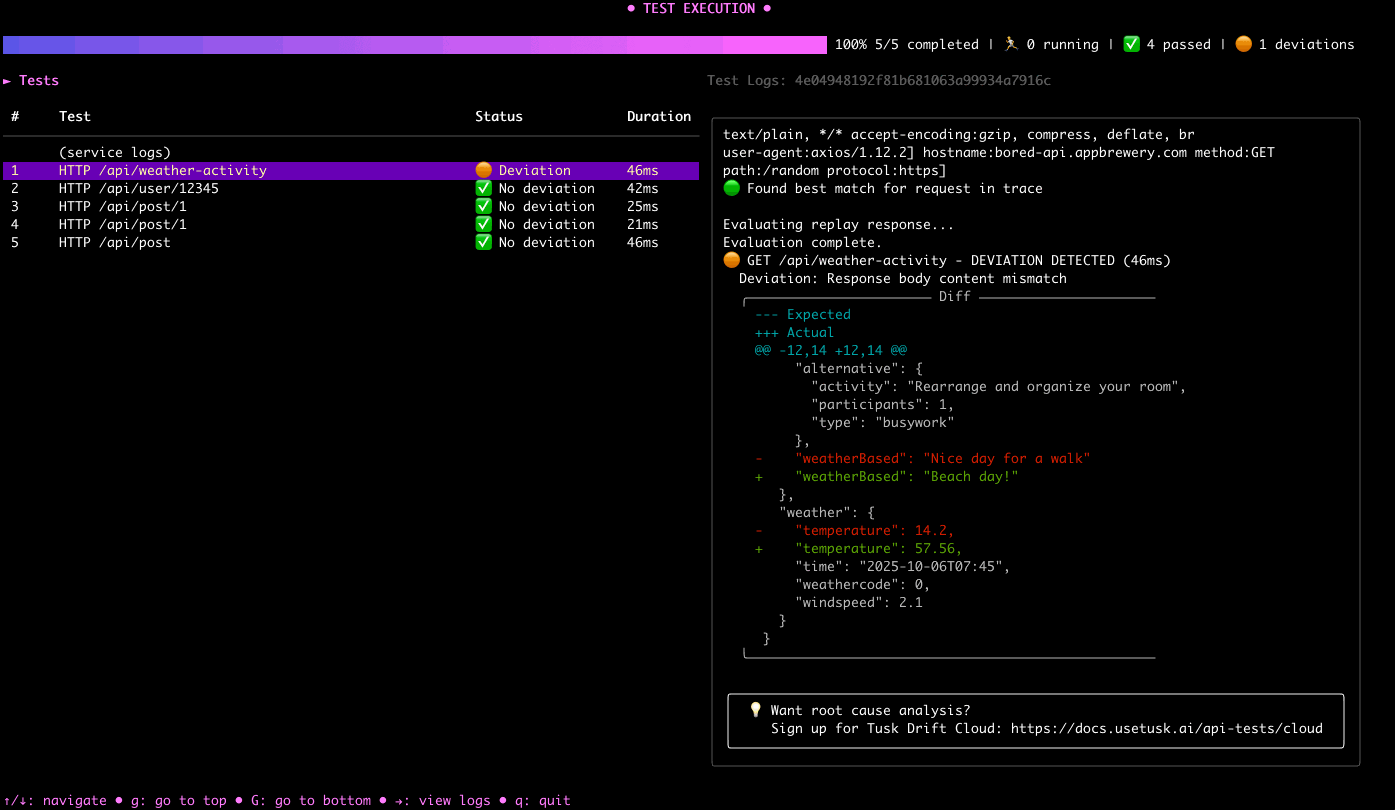
Node.js SDK for capturing and replaying API calls made to/from your service

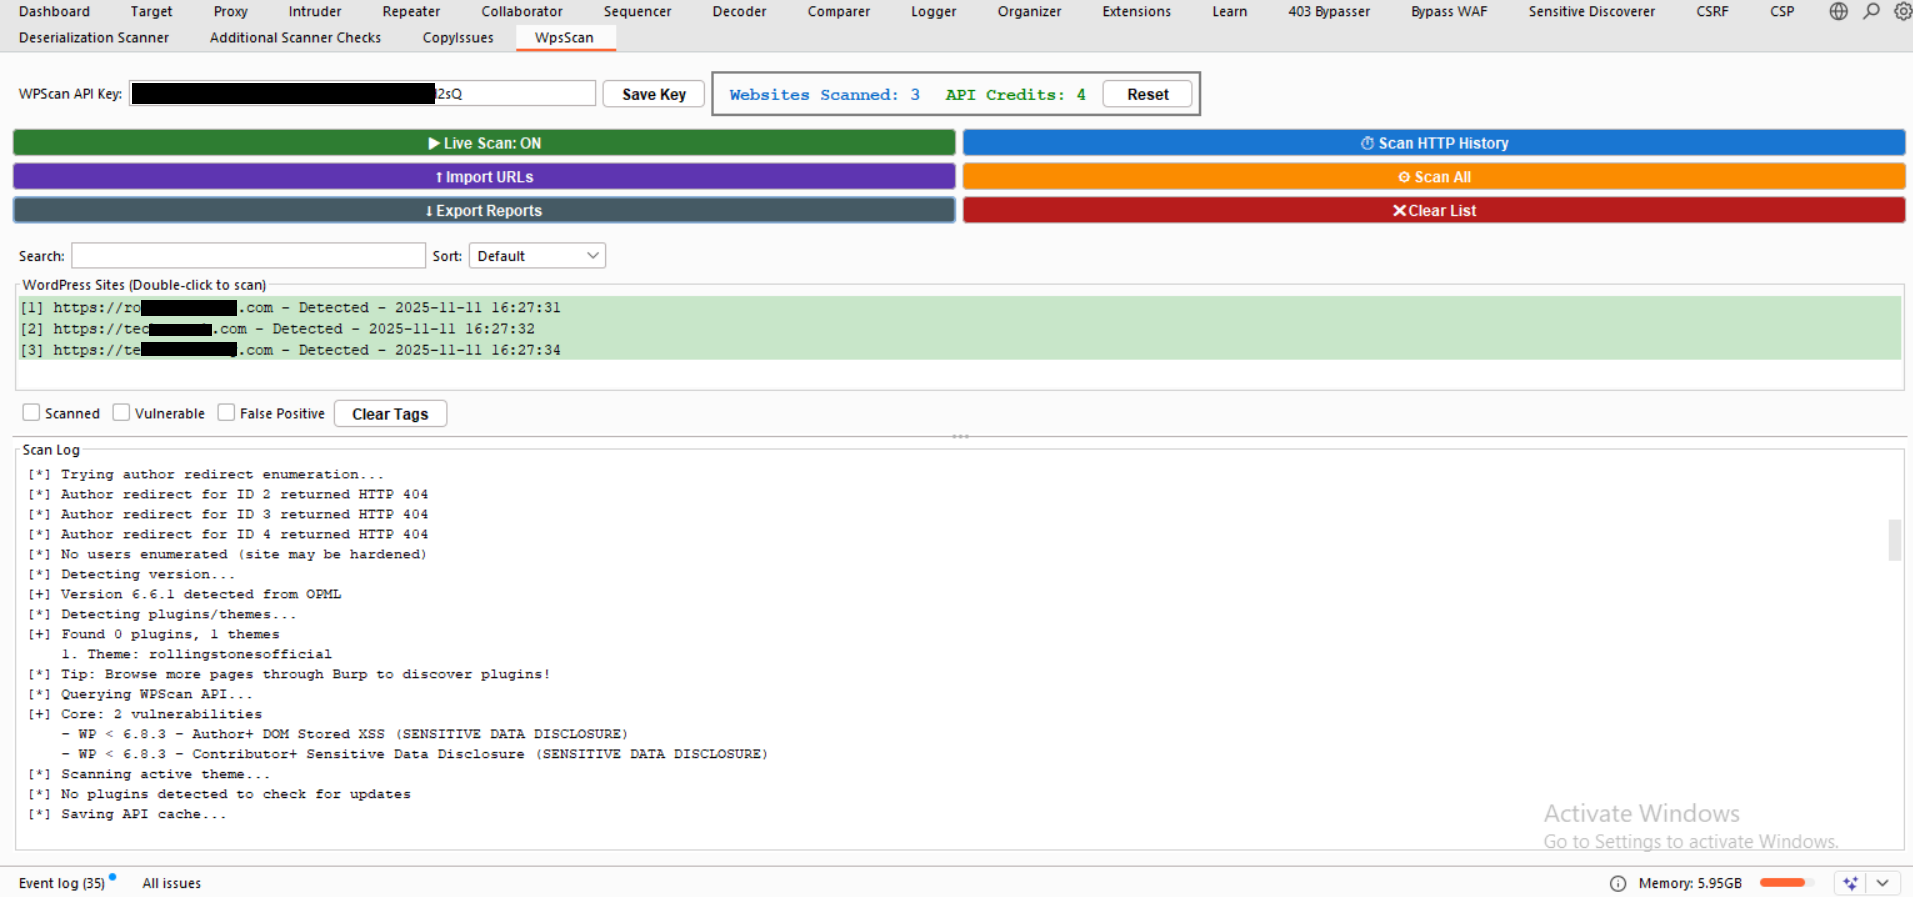
Burp extension for wordpress security scanning

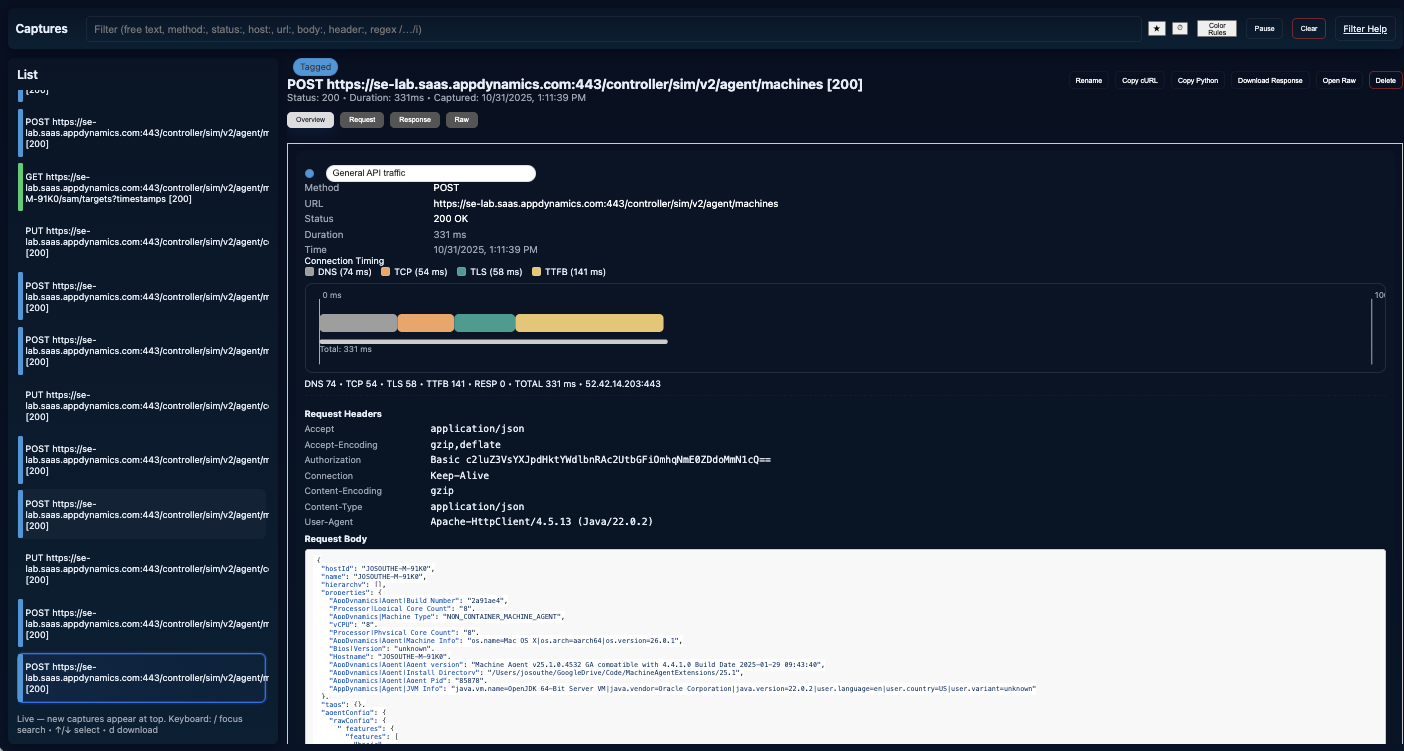
HTTP Proxy Analysis for reverse engineering protocol communication

Proof-of-concept for CVE-2024-48415: stored XSS vulnerability in itsourcecode Loan Management System v1.0 via borrower profile fields. Includes…

Apache APISIX 2.12.1 Remote Code Execution by IP restriction bypass and using default admin AIP token

批量url检测Spring-Cloud-Gateway-CVE-2022-22947

This script exploits the CVE-2024-40094 vulnerability in graphql-java

Proof-of-concept exploit for CVE-2023-27532 in Veeam Backup and Replication that abuses an unsecured API endpoint to extract credentials from the…

Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…