

ASST
 owasp/asst
OWASP ASST (Automated Software Security Toolkit) | A Novel Open Source Web Security Scanner.
code-analysiseducationstatic-code-analysis+2
1905 days ago
owasp/asstOWASP ASST (Automated Software Security Toolkit) | A Novel Open Source Web Security Scanner.
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
 bwasp/bwasp
BoB Web Application Security Project
 pentagridsec/pentagridresponseoverview
Response Overview Extension for BurpSuite - Find exotic responses by grouping response bodies
 cyber-note/cve-2026-34835-black-box-analysis
A black-box (DAST) security analysis of CVE-2026-34835 focusing on external validation methodology, observable behavior, security impact, and…
 theauditortool/benchproctor
Open SAST benchmark corpus: 2,938,418 balanced cases, 11 languages, 21 framework targets, 242 emitted categories, and 231 distinct CWE IDs. Score…
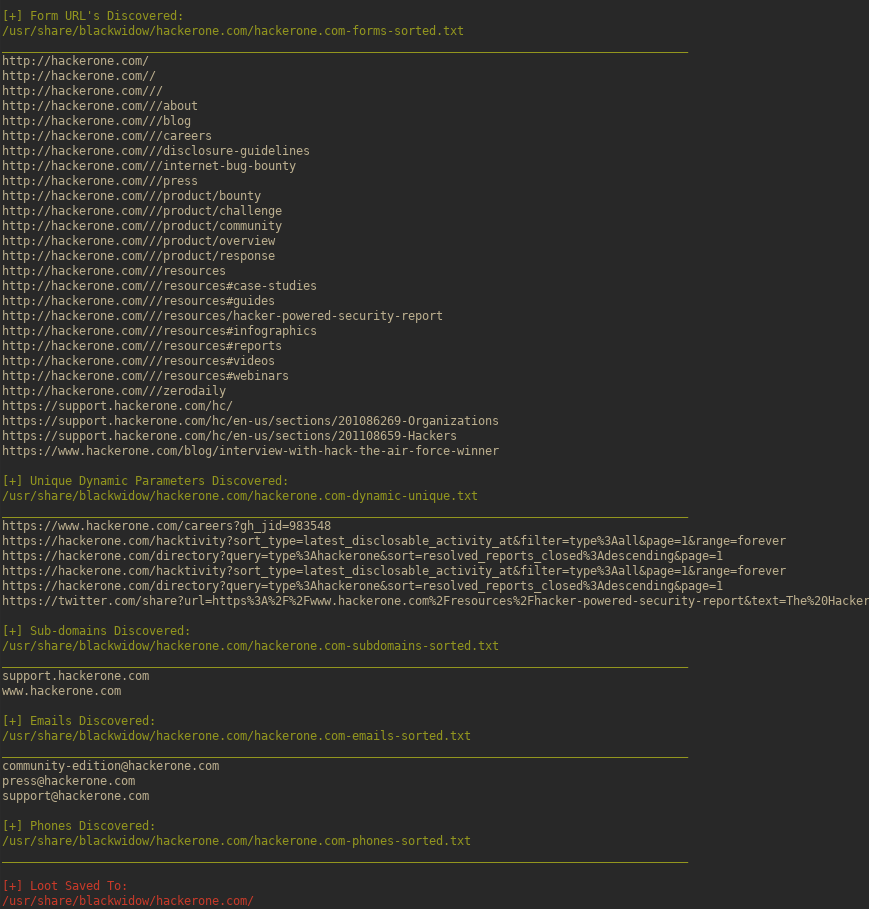 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 kavin-jain/verified-pentest
Self-service pentest platform that only scans domains whose ownership is proven, and re-checks that proof at scan time. OWASP, TLS, DNS and port…
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 urbanadventurer/whatweb
Next generation web scanner
 xalgorix/xalgorix
Open-source AI penetration testing agent that exploit-verifies every finding. Autonomous 22-phase pentests of web apps & APIs with CVSS-scored PDF…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 danoszz/penthera
Offline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
 curiotrace/paramtrace
Fast HTTP parameter discovery for authorized security testing
 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
 stanislav-web/opendoor
OWASP Web Recon & Directory Discovery Platform